

ghost-hoock
 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
android-securitybinary-exploitationexploitation+6
genksome/ghost-hoockGhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 sonyxperiadev/apkanalyser
Static analysis tool for Android APKs that inspects Dalvik bytecode, decodes XML resources, and detects potential issues. Supports binary…
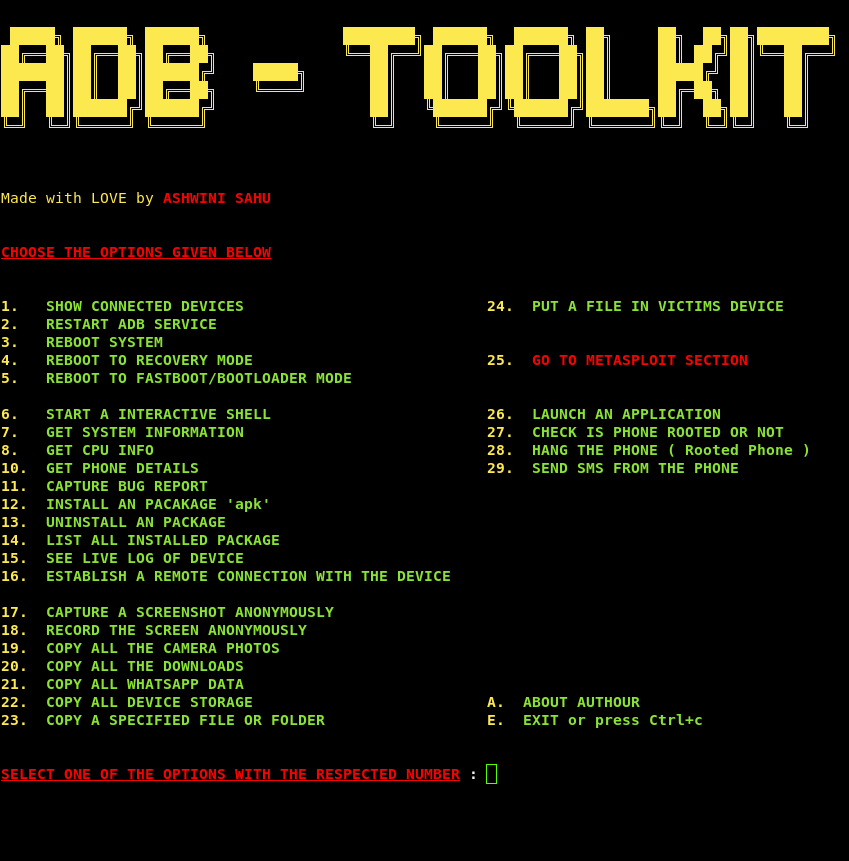 ashwin990/adb-toolkit
ADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!
 tamirzb/cve-2018-9539
PoC code for CVE-2018-9539
 may215/awesome-termux-hacking
⚡️An awesome list of the best Termux hacking tools
 donctl/sandy
Release of the sandy framework.
 owasp/mas-crackmes
The MAS Crackmes aka. UnCrackable Apps, a collection of mobile reverse engineering challenges part of the OWASP MAS project.
 spiralbl0ck/remote-buffer-overflow-over-wifi_stack-in-wpa_supplicant-binary-in-android-11-platform-samsung-a20e
Remote buffer overflow over wifi_stack in wpa_supplicant binary in android 11, platform:samsung a20e, stock options so like works out of the box
 yogehi/cve-2024-4406-xiaomi13pro-exploit-files
Files related to the Pwn2Own Toronto 2023 exploit against the Xiaomi 13 Pro.
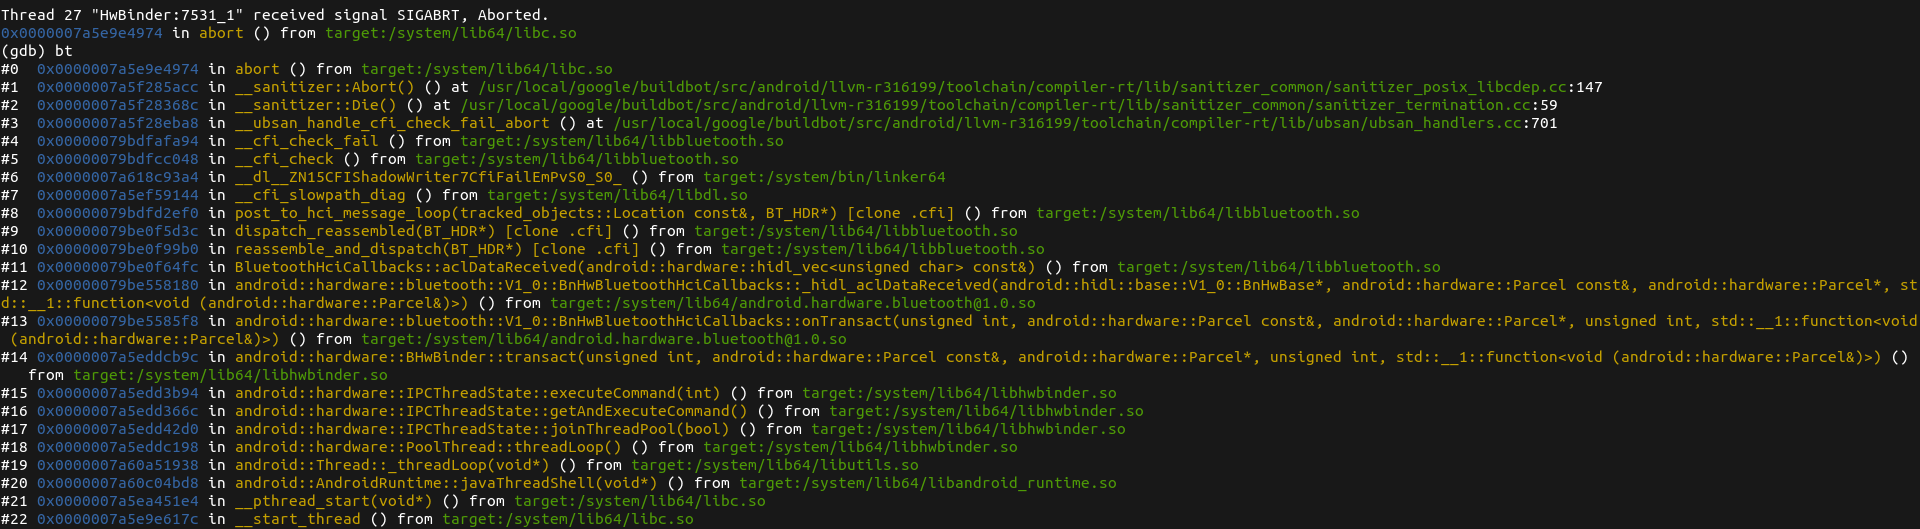 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 camsshaft/selinux-permissive-only-cve-2025-21479
This is an SELinux permissive version of the Cheese exploit also known as CVE-2025-21479 which affected the adreno kgsl on many devices including…
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
 r3n3r0/cve-2026-0049
PoC and analysis of a zero-click DoS in Android's DNG SDK, with crafted DNG samples, an NDK crash harness, and UBSan/IntSan reproduction of the…
 shaikusaf/external_wpa_supplicant_8_aosp10_r33cve-2021-0326
Android Wi-Fi vulnerability research repository containing patched wpa_supplicant source for CVE-2021-0326, enabling analysis and testing of the…
 user1342/awesome-android-reverse-engineering
A curated list of awesome Android Reverse Engineering training, resources, and tools.
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
 lntrx/cve-2021-28663
Proof-of-concept exploit for CVE-2021-28663, a design flaw in the Mali GPU Android kernel driver enabling arbitrary read via memory alias and…