
CVE-2024-0044
 0xbinder/cve-2024-0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
android-securitydata-exfiltrationexploitation+6
331
0xbinder/cve-2024-0044CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
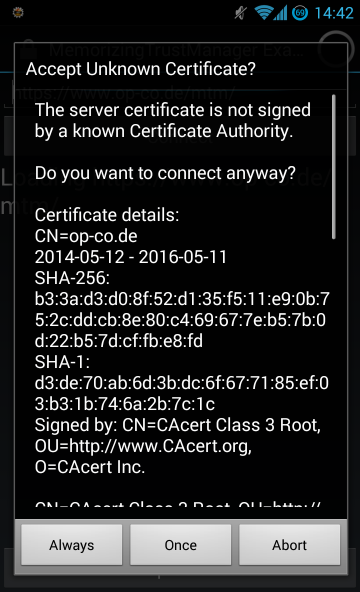 ge0rg/memorizingtrustmanager
A "plugin" for Android Java to allow asking the user about SSL certificates
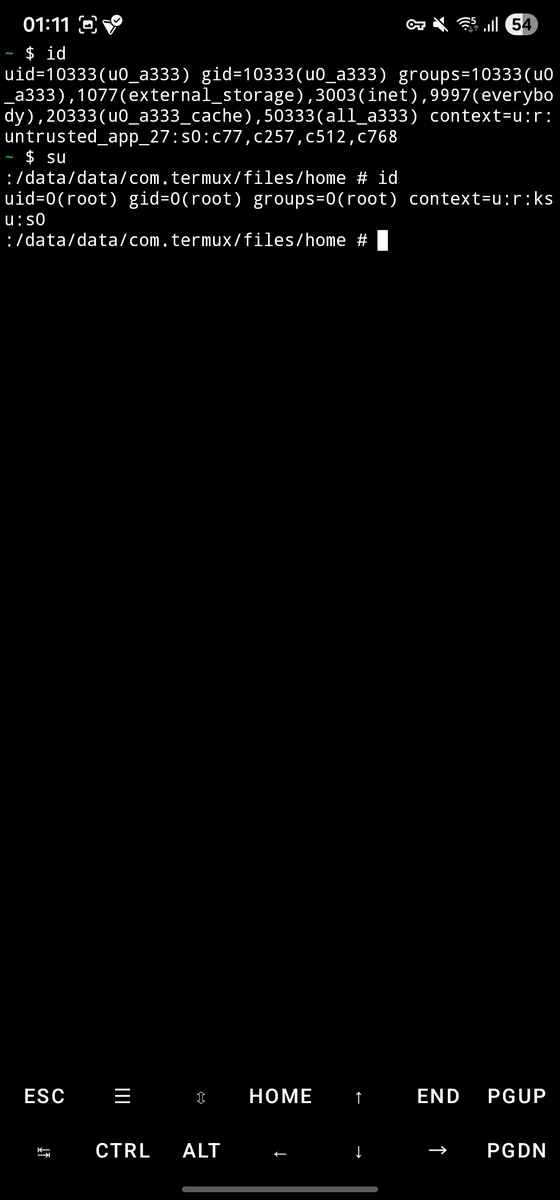 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 jakev/pyxamstore
Python utility for parsing Xamarin AssemblyStore blob files
 markakd/bad_io_uring
Android kernel exploitation for CVE-2022-20409
 kangtastic/cve-2019-2215
Temproot for Pixel 2 and Pixel 2 XL via CVE-2019-2215
 ojasookert/cve-2017-0781
Blueborne CVE-2017-0781 Android heap overflow vulnerability
 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 aau-network-security/hostage
Low Interaction Mobile Honeypot
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
 lntrx/cve-2021-28663
Proof-of-concept exploit for CVE-2021-28663, a design flaw in the Mali GPU Android kernel driver enabling arbitrary read via memory alias and…
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
 adityatelange/poc-cve-2026-0073
CVE-2026-0073 - ADB Wireless Mutual Authentication Bypass PoC
 scs-labrat/android_autorooter
Exfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely
 cybersecsi/robodroid
Manage Android machines with pre-defined behaviors for Cyber Range environments.
 colorful-glassblock/duchamp-root
Xiaomi K70e (duchamp) one-click root via CVE-2026-43499 (IonStack) + KernelSU integration
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.