
drozer
 reverseclabs/drozer
The Leading Security Assessment Framework for Android.
android-securityexploit-frameworksvulnerability-analysis+3
reverseclabs/drozerThe Leading Security Assessment Framework for Android.
 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 designativedave/androrat
Remote Administration Tool for Android devices
 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
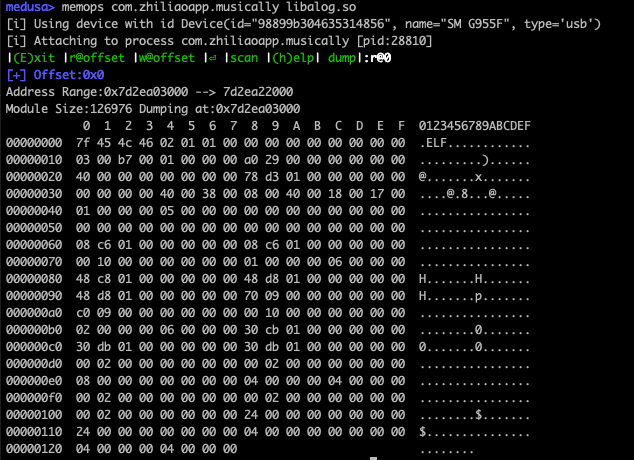 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
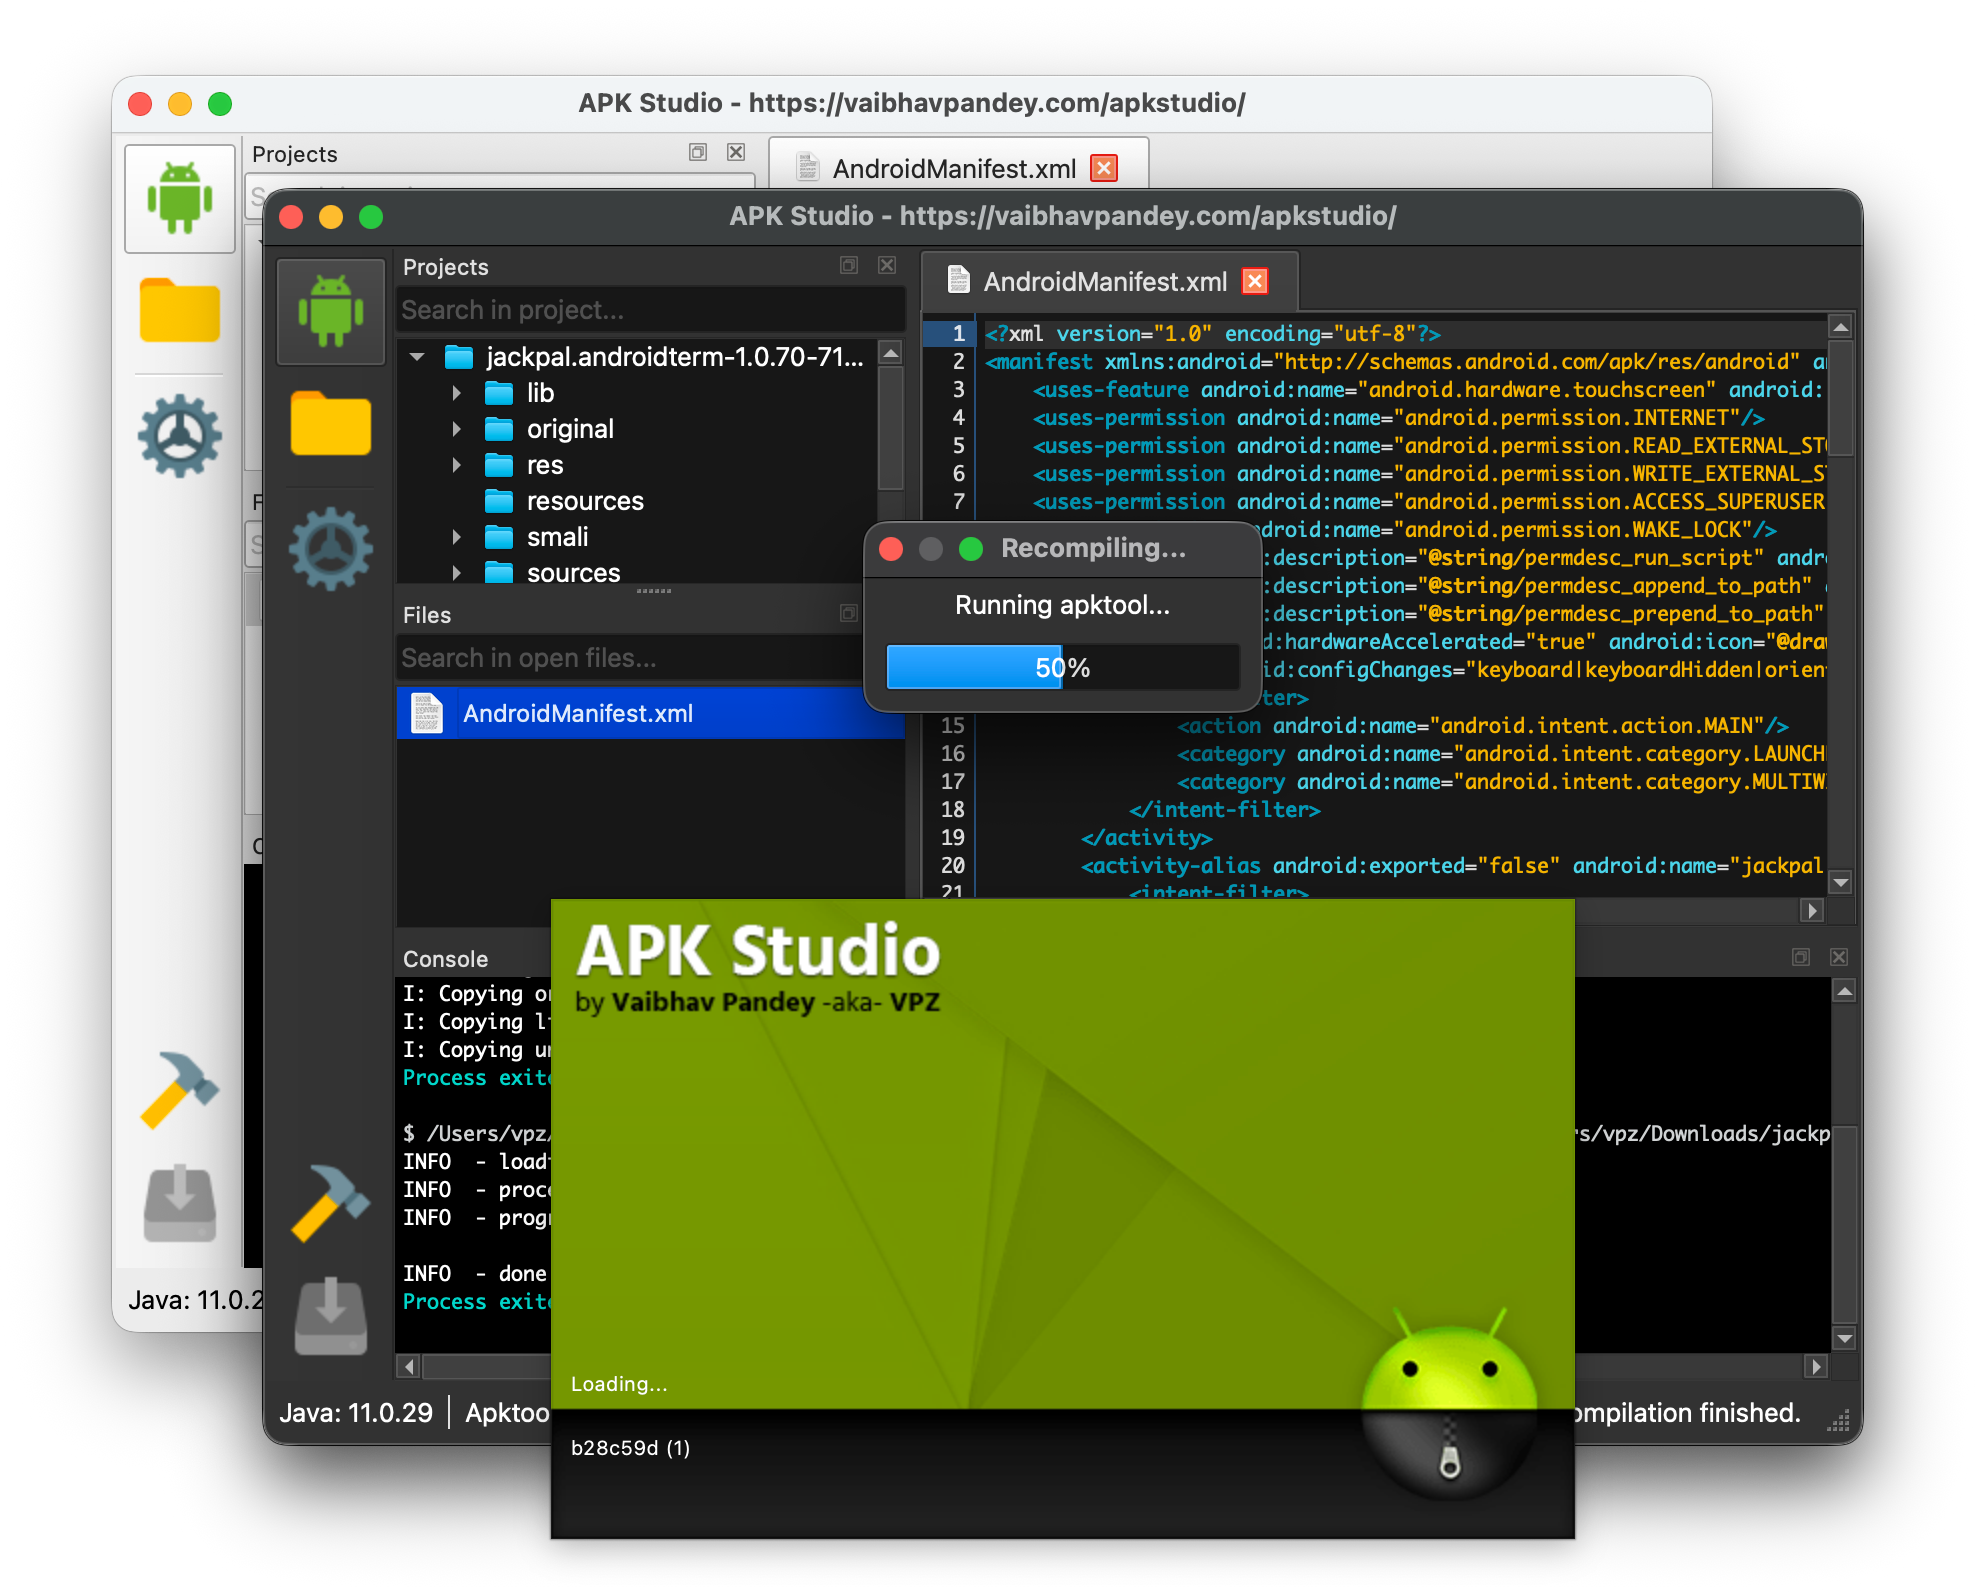 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 auroraoss/aurorastore
Open-source Android client for browsing and downloading apps from Google Play with anonymous login, device/locale spoofing, and tracker detection.
 iddoeldor/frida-snippets
Hand-crafted Frida examples
 niklashigi/apk-mitm
🤖 A CLI application that automatically prepares Android APK files for HTTPS inspection
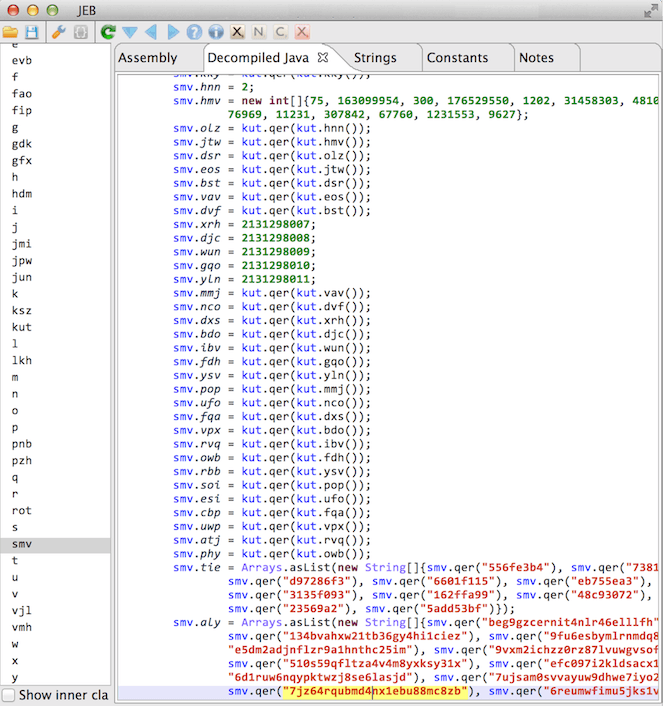 calebfenton/simplify
Android virtual machine and deobfuscator
 grapheneos/vanadium
Privacy and security hardened Chromium build providing the WebView and default browser for GrapheneOS, with OS-level hardening and compatibility…
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
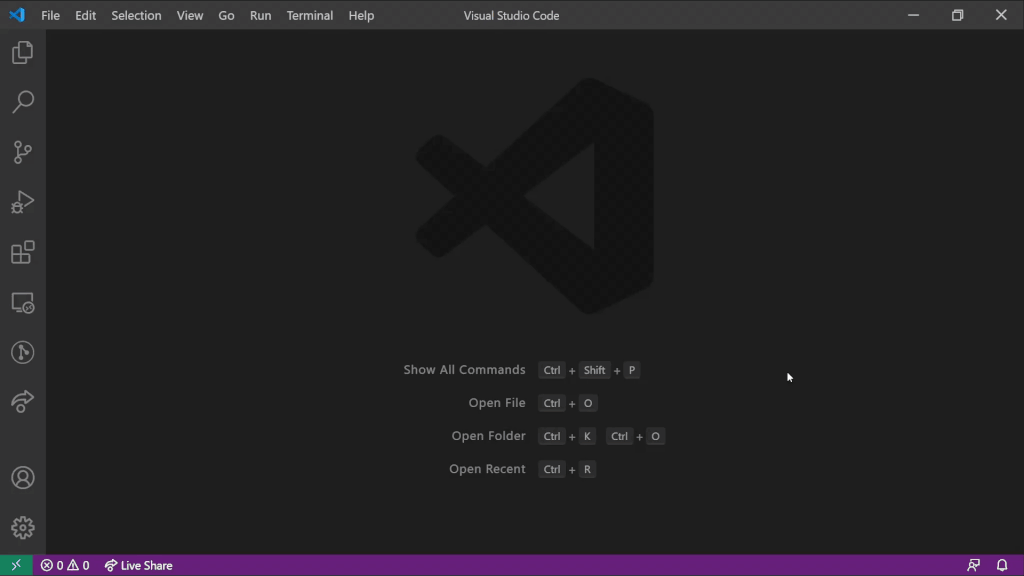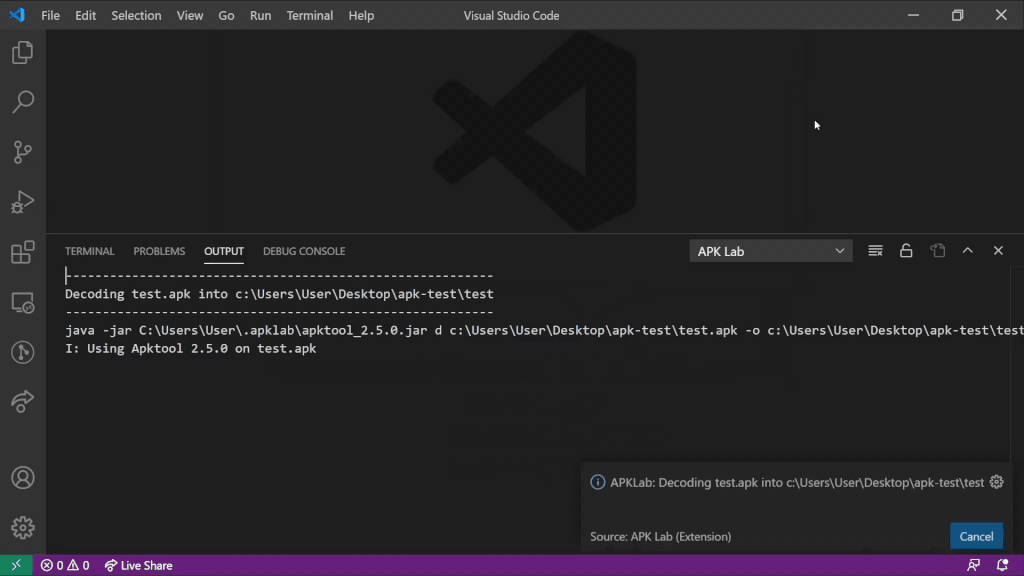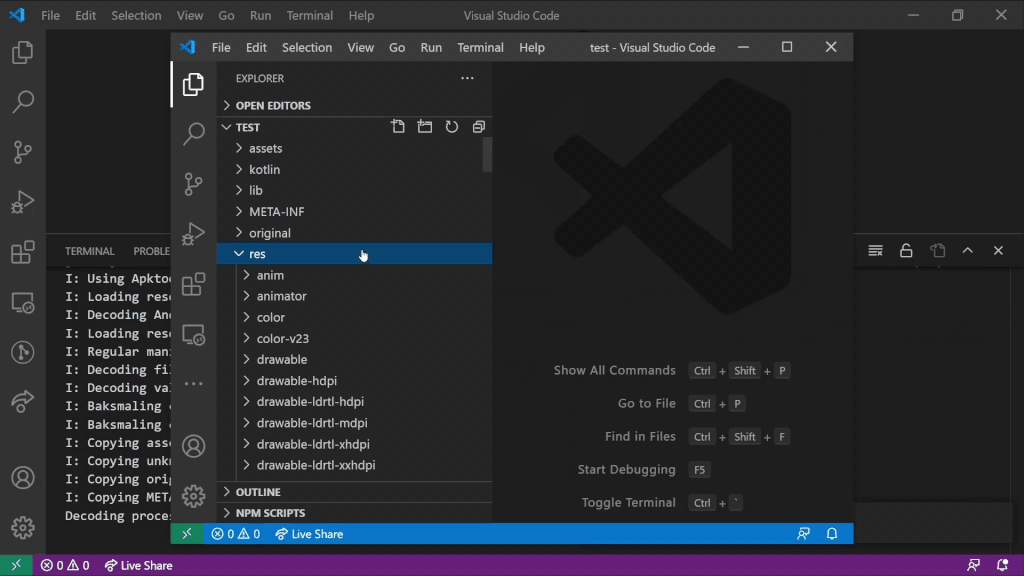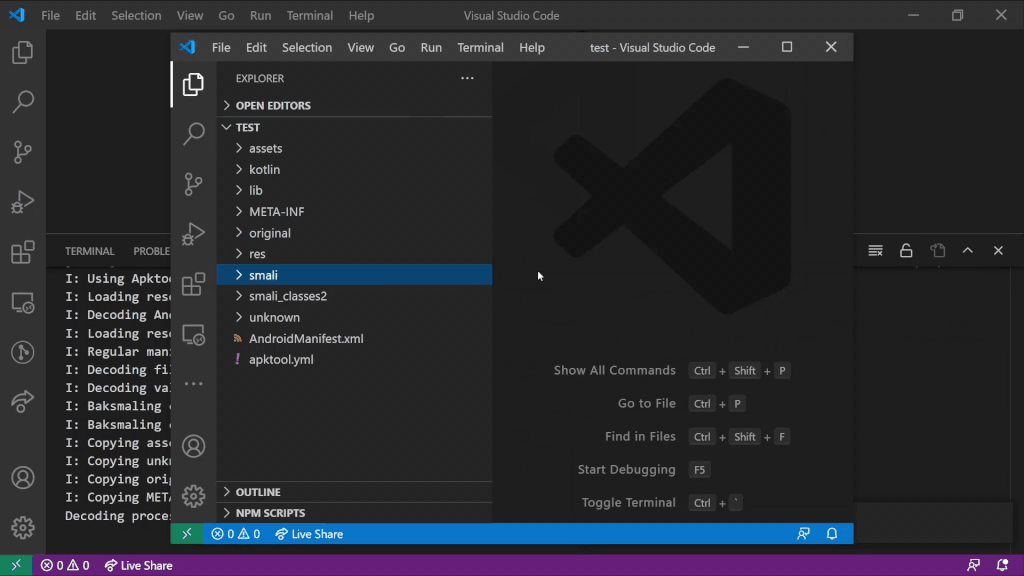 apklab/apklab
Android Reverse-Engineering Workbench for VS Code
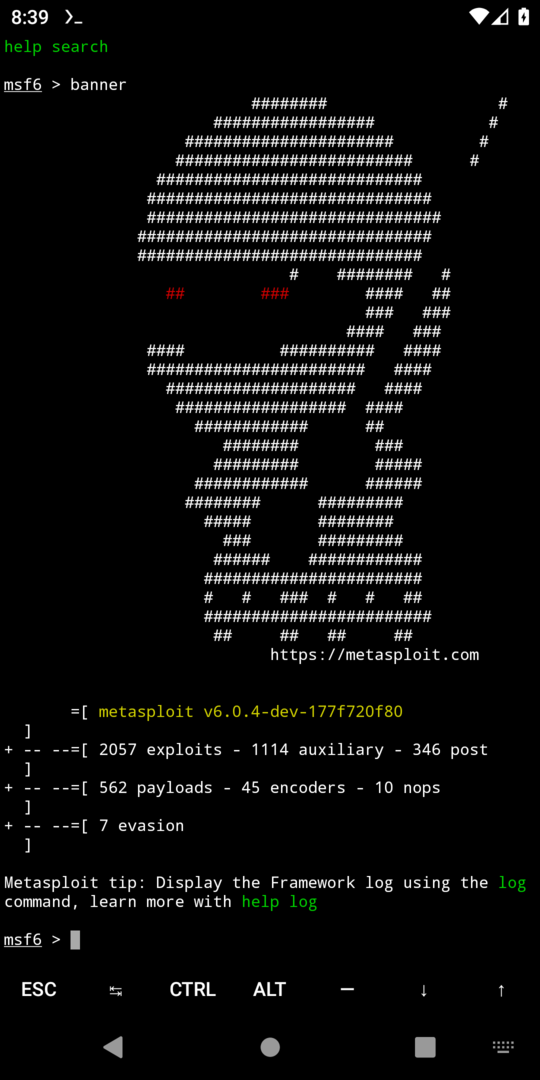 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
 ev-flow/quark-engine
Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…