
Tai-e
 pascal-lab/tai-e
An easy-to-learn/use static analysis framework for Java and Android
android-securitycode-analysiseducation+2
pascal-lab/tai-eAn easy-to-learn/use static analysis framework for Java and Android
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
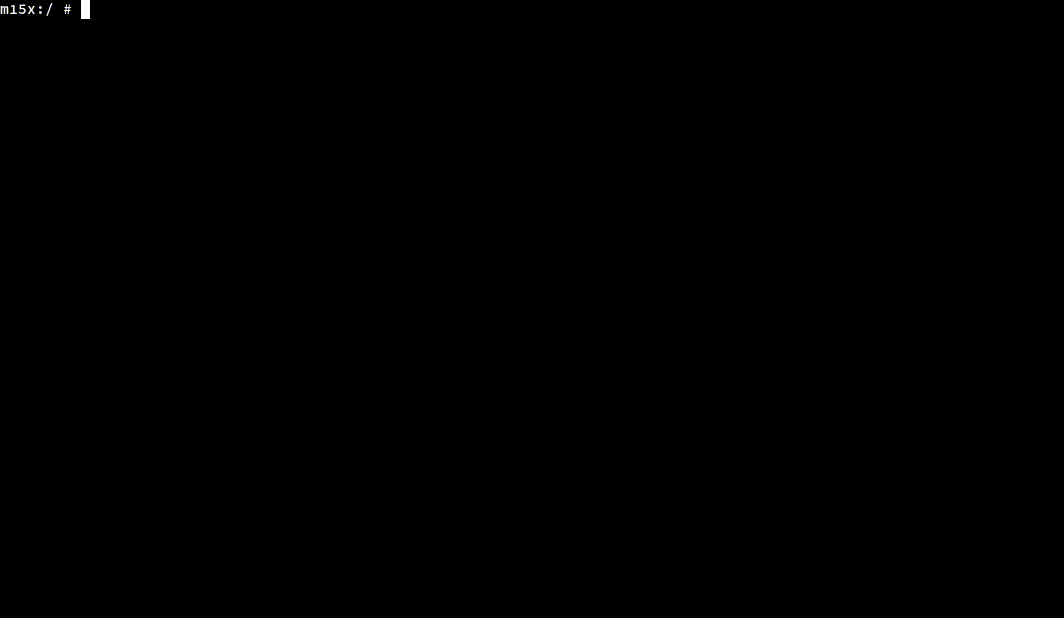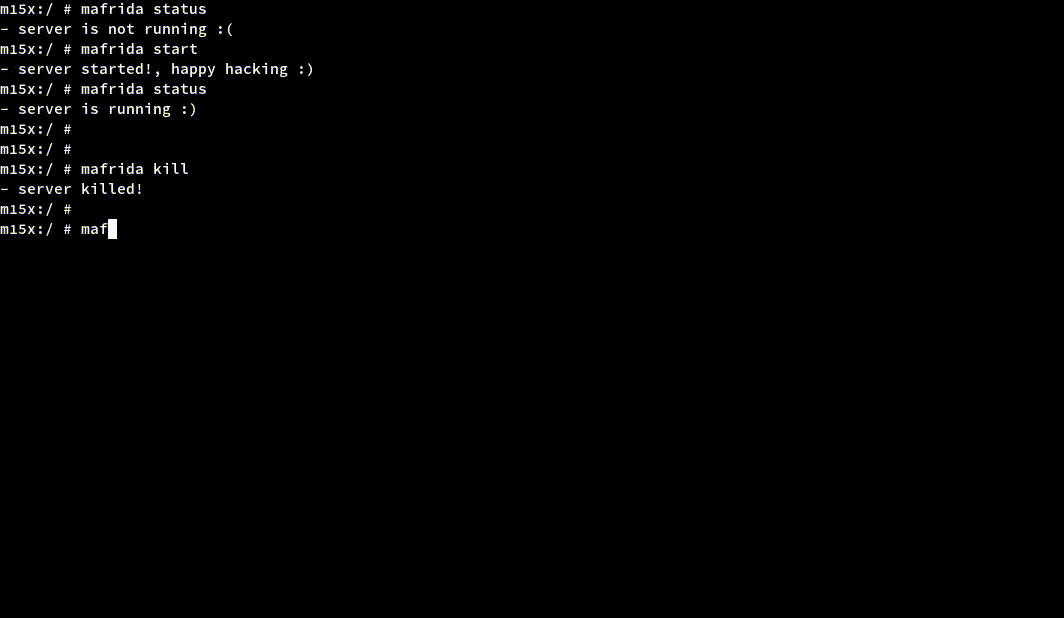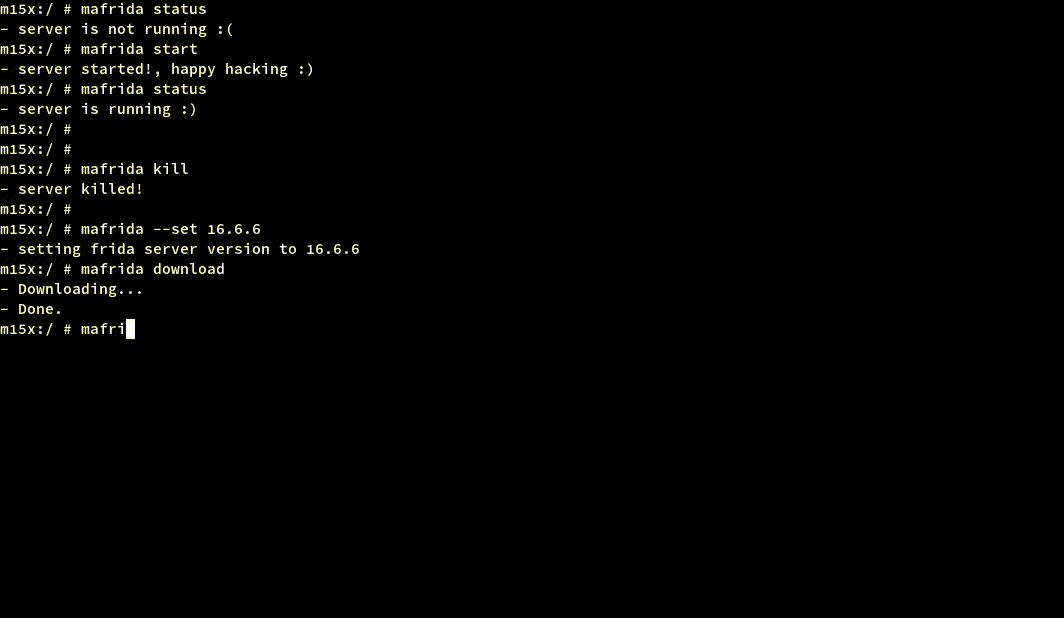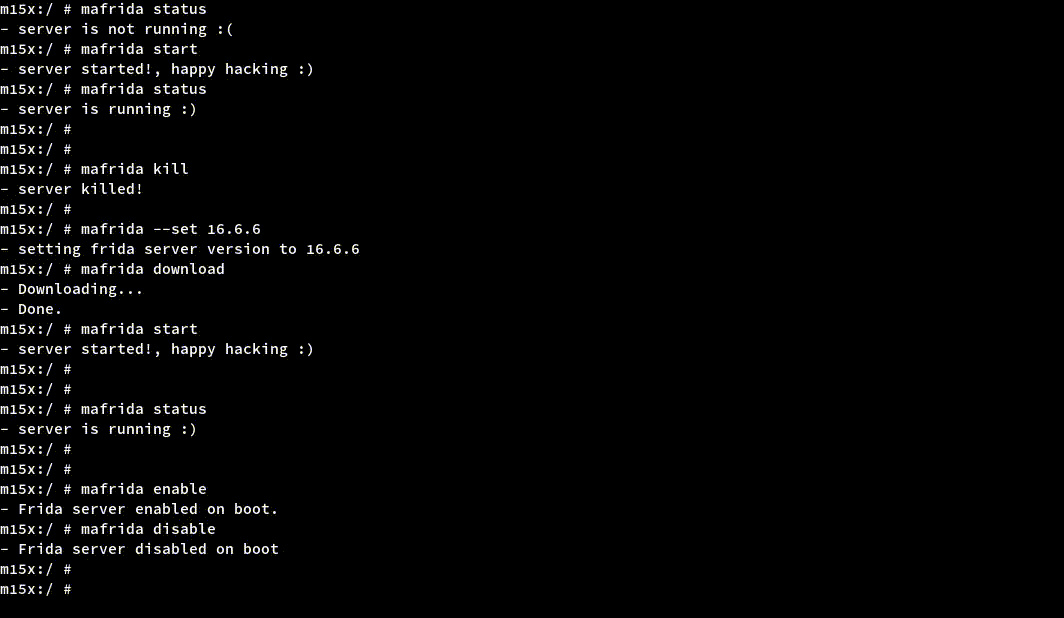 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 yakidango-official/ghostlock-h80gt
Honor 80 GT privilege escalation PoC: GhostLock (CVE-2026-43499) + custom KernelSU module loading
 hunt-benito/two-dots-and-a-slash-cve-2026-18907-tecno-hi-browser-download-path-traversal
Python PoC for CVE-2026-18907 path traversal in TECNO Hi Browser's download handler. Includes malicious HTTP server and naive downloader to…
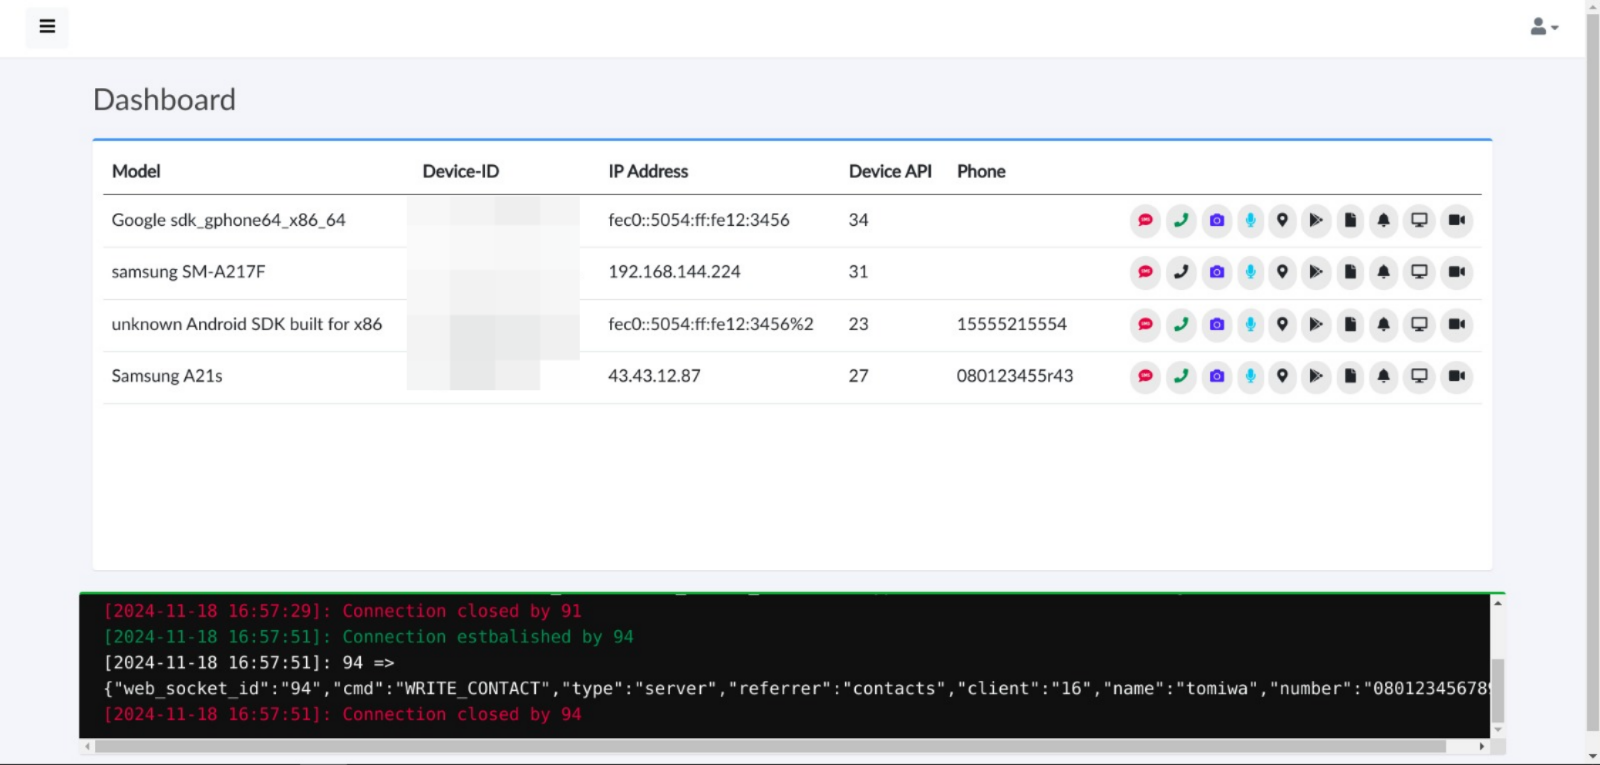 tomiwa-ot/moukthar
Android remote administration tool
 tinopreter/docviewerexploitapp
This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…
 supersonic/cve-2022-20494
Exploit app for CVE-2022-20494, a high severity permanent denial-of-service vulnerability that leverages Android's DND (Do not disturb) feature
 supersonic/wallbreak
Exploit app for CVE-2021-39670 and CVE-2021-39690, two permanent denial-of-service vulnerabilities in Android's wallpaper system
 vino-theva/cve-2019-6447
This paper is about manual exploitation of android open port vulnerability found in ES file manager. This open TCP 59777 port allows the attacker to…
 julio-cfa/poc-es-file-explorer-cve-2019-6447
Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.
 indiandragon/shellshock-vulnerability-scan
Android app to scan for bash Vulnerability - CVE-2014-6271 also known as Shellshock
 mjancek/bluebornedetection
Simple detection tool for Blueborne vulnerability found on Android devices --- CVE-2017-0781.
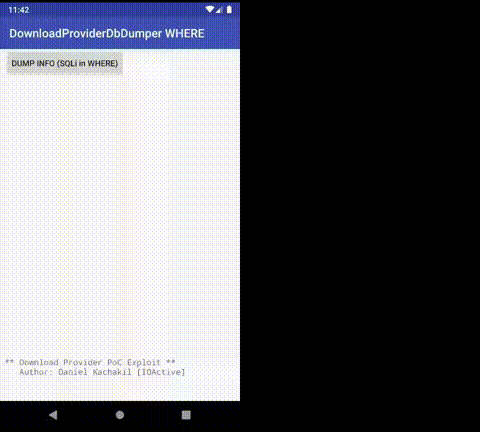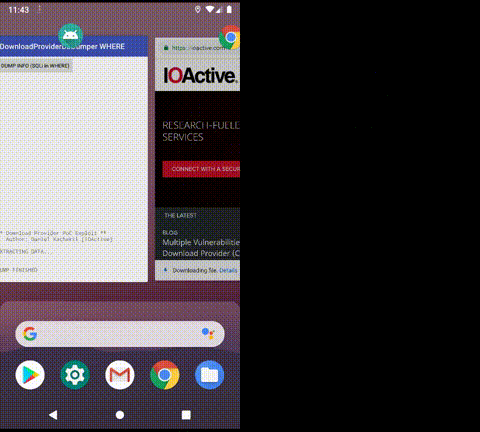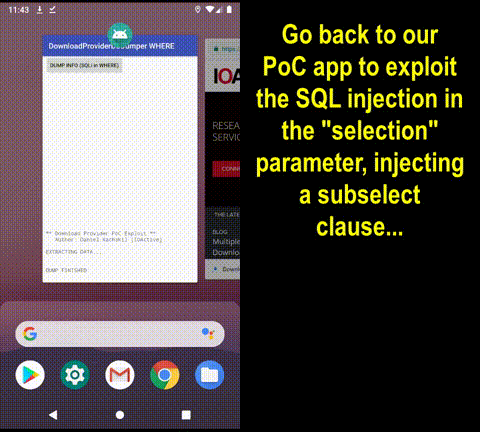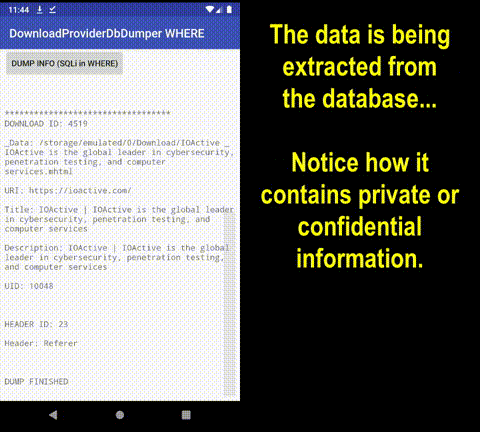 ioactive/aosp-downloadproviderdbdumpersqliwhere
PoC Exploiting SQL Injection in Android's Download Provider in Selection Parameter (CVE-2019-2198)
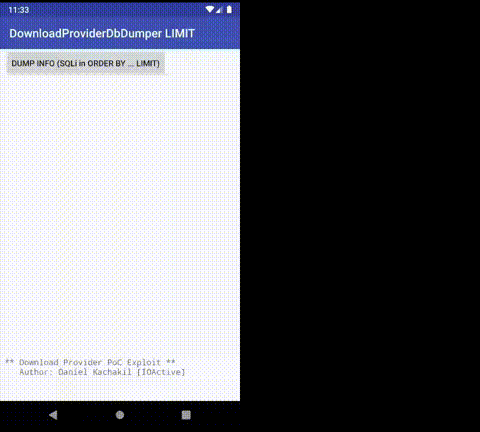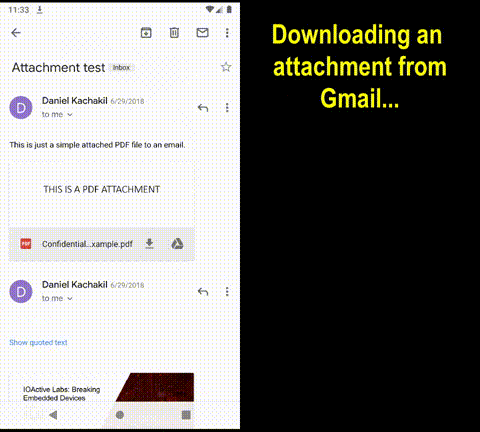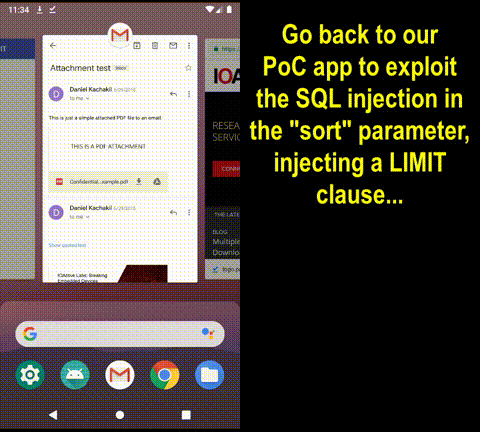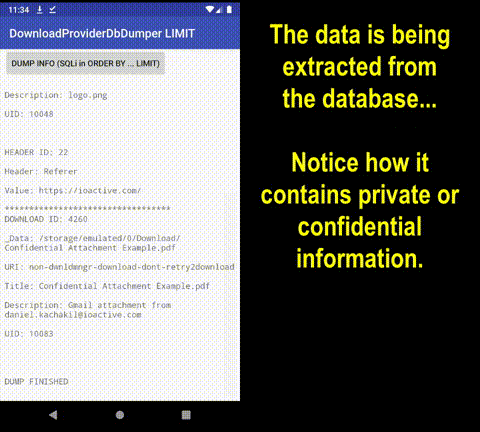 ioactive/aosp-downloadproviderdbdumpersqlilimit
PoC Exploiting SQL Injection in Android's Download Provider in Sort Parameter (CVE-2019-2196)
 ioactive/aosp-downloadproviderhijacker
PoC Exploiting Permission Bypass in Android's Download Provider (CVE-2018-9468)
 ioactive/aosp-downloadproviderheadersdumper
PoC Exploiting Headers Disclosure in Android's Download Provider (CVE-2018-9546)
 ioactive/aosp-downloadproviderdbdumper
PoC Exploiting SQL Injection in Android's Download Provider (CVE-2018-9493)