

FolkPatch
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
android-securitymobile-securitypayload-development+3
1.3k
lyravoid/folkpatchRoot access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 loukious/android_kernel_xiaomi_sm8150
Nethunter kernel for the POCO X3 Pro (vayu) based on crDroid's kernel.
 0xdsm/apepe
Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
 mesquidar/adbsploit
A python based tool for exploiting and managing Android devices via ADB
 neternels/android_kernel_xiaomi_sunny
CAFest nethunter kernel based on LA.UM.9.1.r1-11900-SMXXX0.0 with latest upstream-f2fs-stable-linux-4.14.y merged, bb and perf focused. | Force push…
 chethine/esfileexplorer-cve-2019-6447
Exploiting Android Vulnerability in ES File Explorer
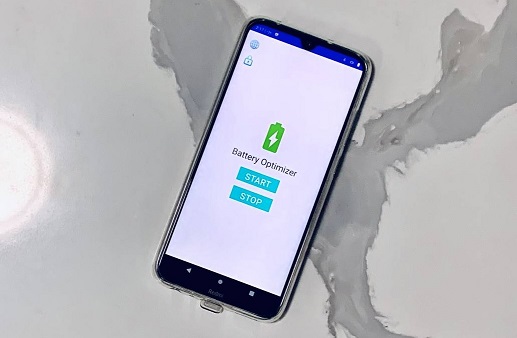 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 xploitwizer-community/xploitspy
Cloud-based Android monitoring tool with GPS tracking, microphone recording, SMS/call logging, live notification capture, file explorer, and built-in…
 c3r34lk1ll3r/cve-2019-2215
PoC for old Binder vulnerability (based on P0 exploit)
 sh4hin/androl4b
A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis
 advancedhacker101/android-c-sharp-rat-server
This is a plugin for the c# R.A.T server providing extension to android based phone systems
 aymankhalfatni/cve-2017-0785
CVE-2017-0785: BlueBorne PoC
 ojasookert/cve-2017-0785
Blueborne CVE-2017-0785 Android information leak vulnerability