
reFlutter
 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
android-securitydynamic-analysis-sandboxingios-security+3
2.8k
impact-i/reflutterPatches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
 topjohnwu/magisk
Android customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 ymh001/meizu21-ghostlock-root
MEIZU 21 locked-bootloader runtime root via CVE-2026-43499 and KernelSU late-load
 worawit/blutter
Flutter Mobile Application Reverse Engineering Tool
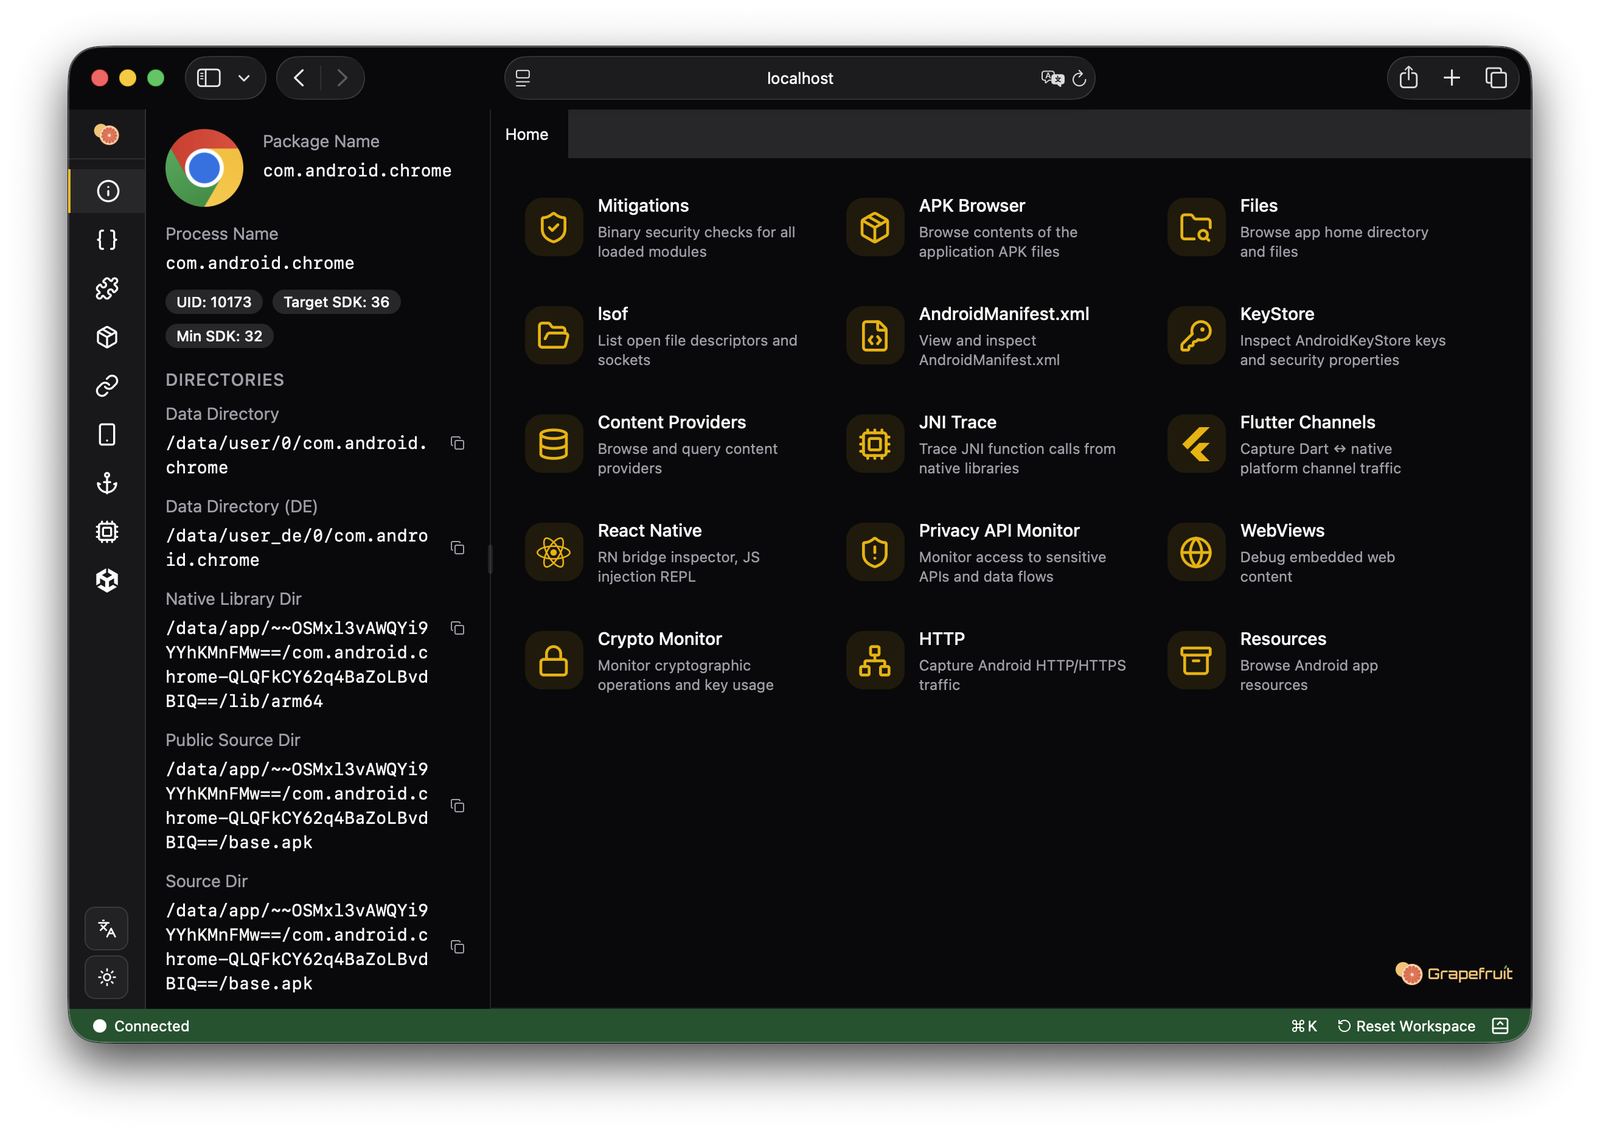 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.

 guardianproject/tormobile/arti-mobile
Rust-based Tor library for Android and iOS, providing a standard API to integrate the Arti Tor runtime into mobile apps for private,…
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 taptap/cve-2025-59489
Automated scanner that detects Unity runtime injection vulnerability CVE-2025-59489 in Android APKs by extracting Unity version and checking against…
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 trinadh465/frameworks_native_aosp-10_r33_cve-2023-21094
Exploit or patch for CVE-2023-21094 in Android 10 frameworks/native, targeting a specific vulnerability in the Android runtime.
 trinadh465/platform_art_cve-2021-0394
Analyzes and demonstrates the Android Runtime vulnerability CVE-2021-0394, providing code-level insights for security researchers and developers.
 gmh5225/frida-vmprotect-bypass
Frida script that bypasses VMProtect runtime protections on mobile platforms, enabling dynamic instrumentation and analysis of protected binaries.
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 shaikusaf/shaikusaf-frameworks_base_aosp10_r33_cve-2022-20138
Proof-of-concept exploit for CVE-2022-20138 targeting Android 10 (AOSP r33) framework base, demonstrating a privilege escalation vulnerability in the…