
GhostLock
 r0rt1z2/ghostlock
Kernel root exploit (CVE-2026-43499) for some Amazon devices
android-securityexploitationexploit-frameworks+4
r0rt1z2/ghostlockKernel root exploit (CVE-2026-43499) for some Amazon devices
 xjoker/lenovo_y700_tb320fc_on_cve-2025-21479
In-memory kernel privilege escalation for Lenovo Legion Y700 2023 (TB320FC) exploiting CVE-2025-21479, a Qualcomm Adreno GPU SMMU flaw, with ReSukiSU…
 cyberbalsa/ghostlock-nvidia-shield-9.2.4
Validated GhostLock CVE-2026-43499 port for NVIDIA Shield TV Pro mdarcy 9.2.4
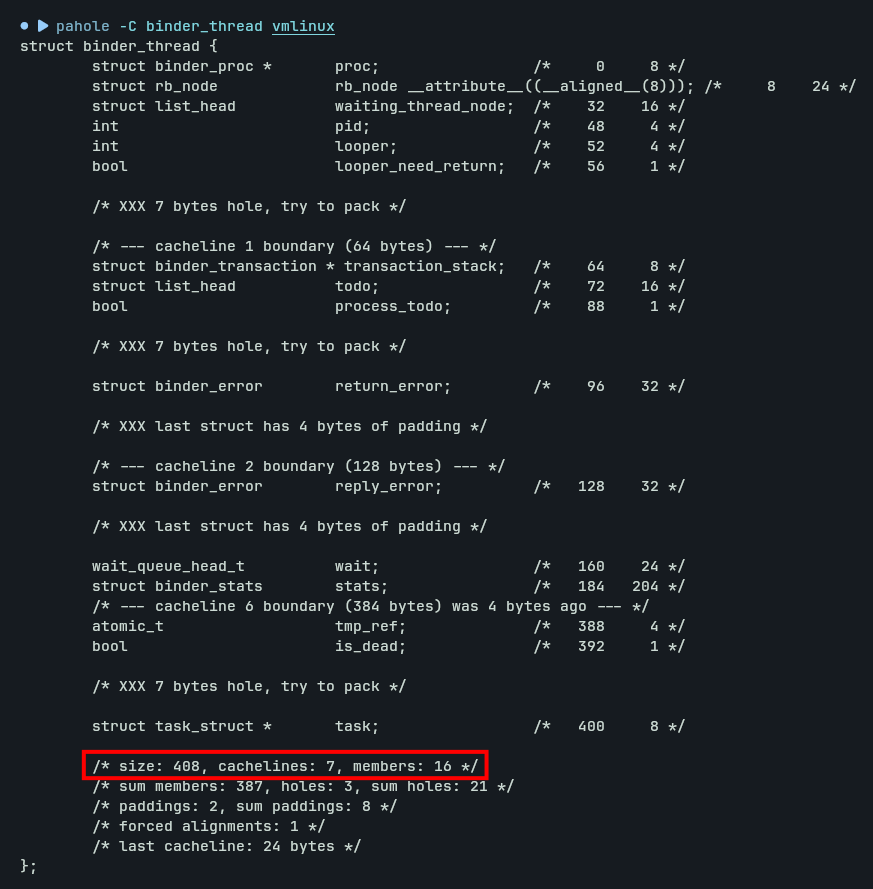 0xbinder/cve_2019_2215
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.
 xiaobailovesstirring/cve-2026-0013-poc
CVE-2026-0013 Android EoP PoC - Compiled artifacts for security research (Derivative of inforcqb/cve-2026-0013-exploit)
 valentineus/hp-slate7-root-kit
HP Slate 7 2800 Android 4.1.1 rooting kit using CVE-2015-1805.
 lazybear8372/cve-2023-41898_lab
Walk through CVE-2023-41898: exploit an unvalidated deep link in Home Assistant Android to load arbitrary URLs in a privileged WebView and leak a…
 lazybear8372/cve-2023-31014_lab
Educational Android lab for CVE-2023-31014 implicit intent hijacking
 murf-xd/cve-2023-20768
Android kernel CVE analysis and PoC for a MediaTek ION allocator type confusion, covering root-cause diffing, unprivileged trigger, and…
 sweatyrocket/huawei-p10-cve-2017-8890-unlock
Huawei P10 VTR-L29C432B151 CVE-2017-8890 exploit research and bootloader-unlock journey
 kasnria001/pwnage24mtk
Cert exploit for MTK devices.There is a logic flaw in MTK cert verification process.Similar to CVE-2023-20696.
 nestle19/cve-2019-2215
Android kernel exploit for CVE-2019-2215, a use-after-free in the Binder driver, enabling privilege escalation to root via memory corruption and cred…
 flipphoneguy/root-sonim-xp3800
app that ports CVE-2019-2215 to arm32 and mounts a su binary to /sbin with denylist + root app installer. firehose/Magisk guide included
 acloudinthebluesky/cve-2019-6447-es-file-explorer
Technical analysis and safety-conscious research harness for CVE-2019-6447 in ES File Explorer for Android
 mythicaltree/cve-2019-2215
Proof-of-concept exploit for CVE-2019-2215 (Bad Binder) targeting Android 10 x86_64 emulator. Designed for isolated kernel exploitation research and…
 byt3quester/cve-2023-20938-poc
Local privilege escalation proof-of-concept for CVE-2023-20938, a use-after-free in Android binder, achieving root and disabling SELinux on…
 0xatharv/cve-2023-20938-public
A bug trigger for CVE-2023-20938 for Android Binder.
 i-redbyte/android-badbinder-demo
demo CVE-2019-2215 (Bad Binder) for Android Q