

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
24.8k
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
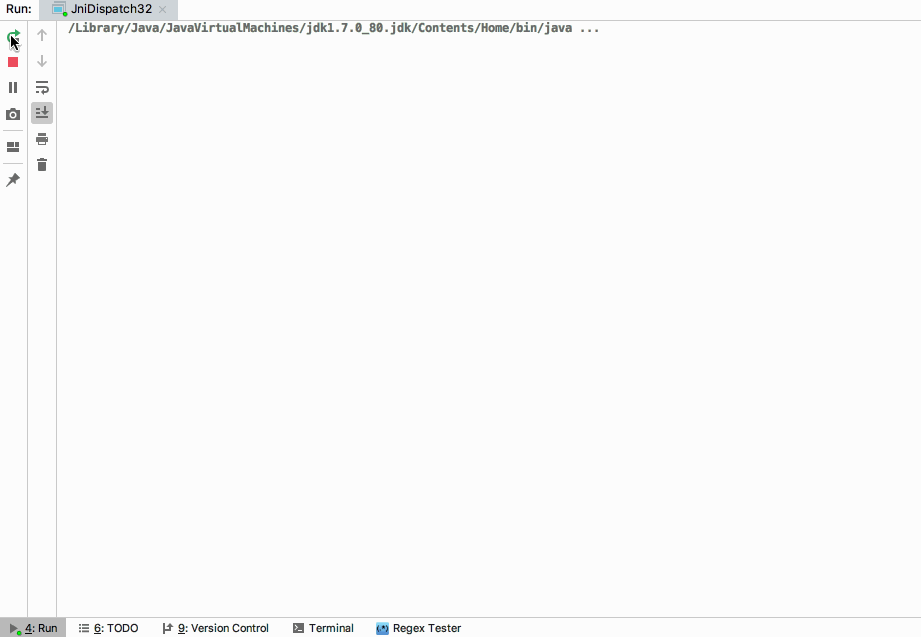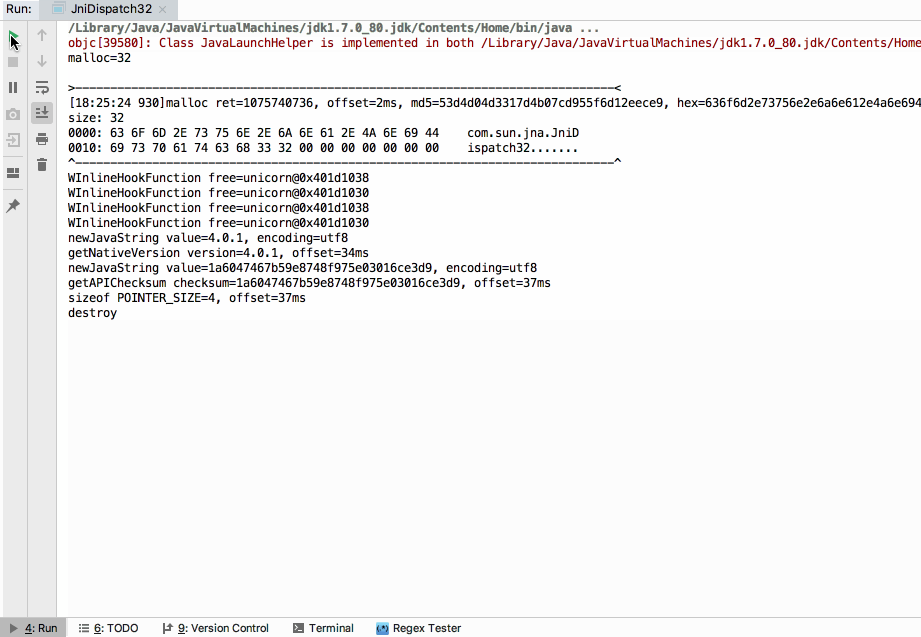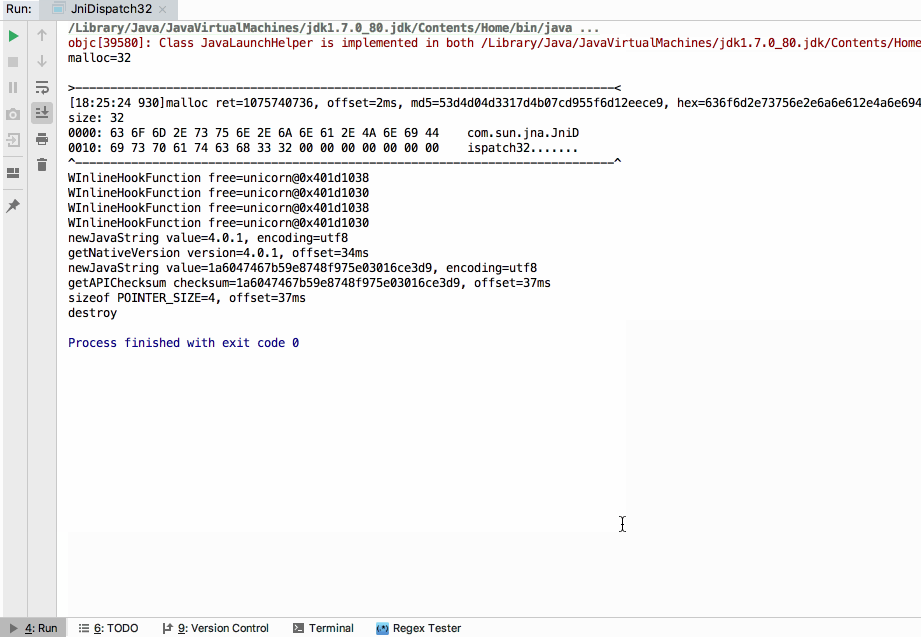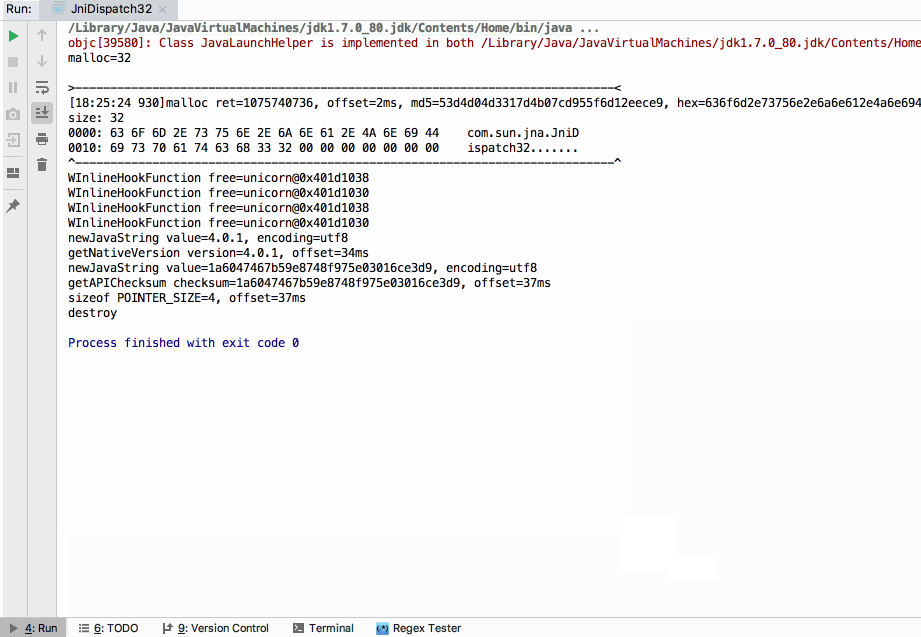 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 ultrasina/androidreverse
Android reverse engineering entirely on-device. Radare2 binary analysis, 8 Java decompilers, Flutter & Unity il2cpp support.
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 flipphoneguy/root-sonim-xp3800
app that ports CVE-2019-2215 to arm32 and mounts a su binary to /sbin with denylist + root app installer. firehose/Magisk guide included
 pealeap/cve-2026-21045_and_cve-2026-21048
Generates crafted TIFF/DNG files to trigger out-of-bounds writes in Samsung's libimagecodec.quram.so, including binary analysis and reproduction…
 ma4the/omae-wa-cheese-da
CVE-2025-21479 PoC for ZFlip5 with Knox in the way!(˶˃ ᵕ ˂˶)
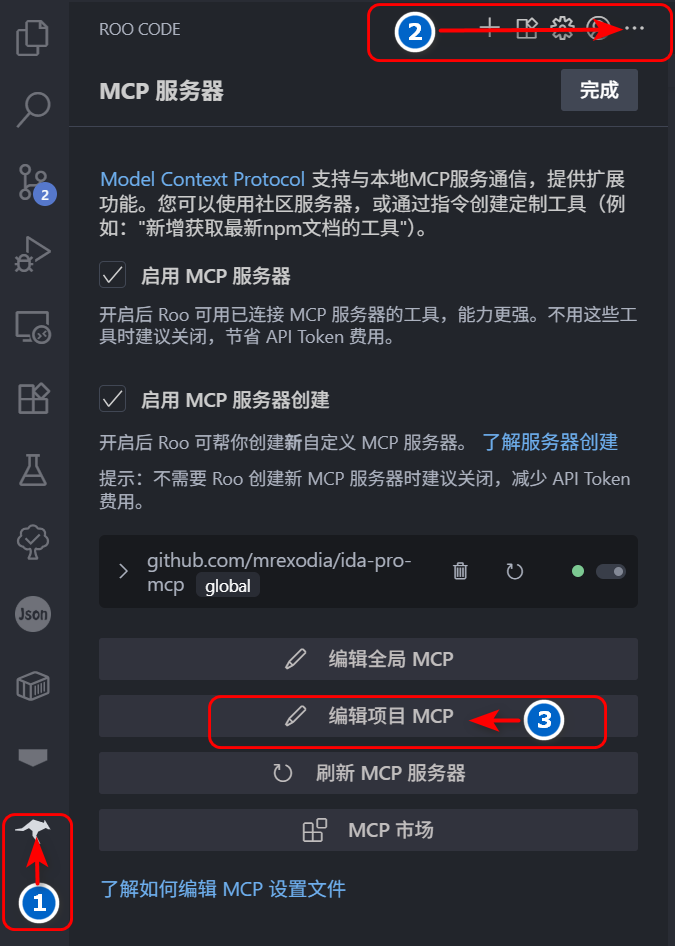 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
 k0mraid3/k0mraid3s-system-shell-prebuilt
Exploit I discovered in October of 2022 with androids Package manager binary (pm) and the way it handled debugging flags, patched out by march 2023.…
 spiralbl0ck/remote-buffer-overflow-over-wifi_stack-in-wpa_supplicant-binary-in-android-11-platform-samsung-a20e
Remote buffer overflow over wifi_stack in wpa_supplicant binary in android 11, platform:samsung a20e, stock options so like works out of the box
 sonyxperiadev/apkanalyser
Static analysis tool for Android APKs that inspects Dalvik bytecode, decodes XML resources, and detects potential issues. Supports binary…