
Insular
 secure-system/insular
Isolate your big brother apps https://secure-system.gitlab.io/Insular/
android-securitycontainer-escapedynamic-analysis-sandboxing+3
secure-system/insularIsolate your big brother apps https://secure-system.gitlab.io/Insular/
 aye468448-eng/cve-2026-0073-android-adbd-authentication-bypass
PoC for CVE-2026-0073, an Android ADB authentication bypass enabling network attackers to connect to previously paired devices over wireless…
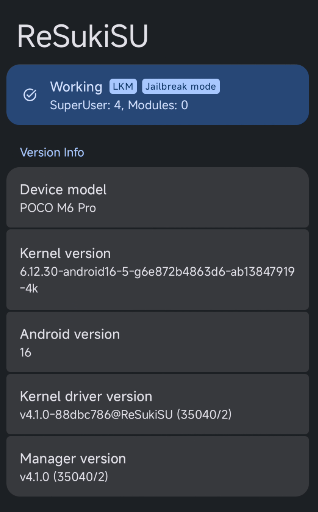 datfooldive/ghostlock-emerald
GhostLock (CVE-2026-43499) kernel exploit for Poco M6 Pro (emerald) with locked bootloader
 tinnci/cve-2024-31317
Detailed discussion of Zygote vulnerability CVE-2024-31317
 m00ddy/cve-2026-0073-android-client-tls-auth-bypass
translating original python exploit to C
 iodn/tap-ducky
Turns any rooted phone into the legendary USB Rubber Ducky. Android USB HID Keystroke Injector
 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 unnaim/adbhijacker
A PoC tool for the CVE-2026-0073 on android 11+ devices which allows instant zero click RCE on any unpatched device with adb over tcp enabled
 sectestannaquinn/cve-2026-0073-android-adbd-authentication-bypass-poc
Proof-of-concept exploit for CVE-2026-0073, an Android ADB authentication bypass allowing network attackers to connect to devices with ADB over TCP…
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
 agg23/cve-2024-31317
Detailed discussion of Zygote vulnerability CVE-2024-31317
 cyb3r-w0lf/dirty_stream-android-poc
Android - Dirty Stream exploit for MI-File Explorer V1-210567 version. CVE-2024-35205
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 thebl4ckph4nt0m/cve-2024-0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13. This repo demonstrates how to exploit…
 0xbinder/cve-2024-0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 k4ran909/cve_2024_0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 hunter24x24/cve_2024_0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 kai2er/cve-2024-0044-exp
利用CVE-2024-0044 在Android12、13 没有root'下进行数据备份 用法./CVE-2024-0044-EXP.sh <package_name>