

byd-dolphin-hacking
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
android-securitybinary-analysisembedded-systems-security+7
59
wheregoes/byd-dolphin-hackingReverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 hydradragonantivirus/hydradragonav-mobile
Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware
 ge0rg/memorizingtrustmanager
A "plugin" for Android Java to allow asking the user about SSL certificates
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 soralis0912/cve-2026-43499-warhol-root
Local privilege escalation exploit targeting CVE-2026-43499 for the Xiaomi 17T Pro (warhol) on Android 16 with MediaTek MT6993 SoC.
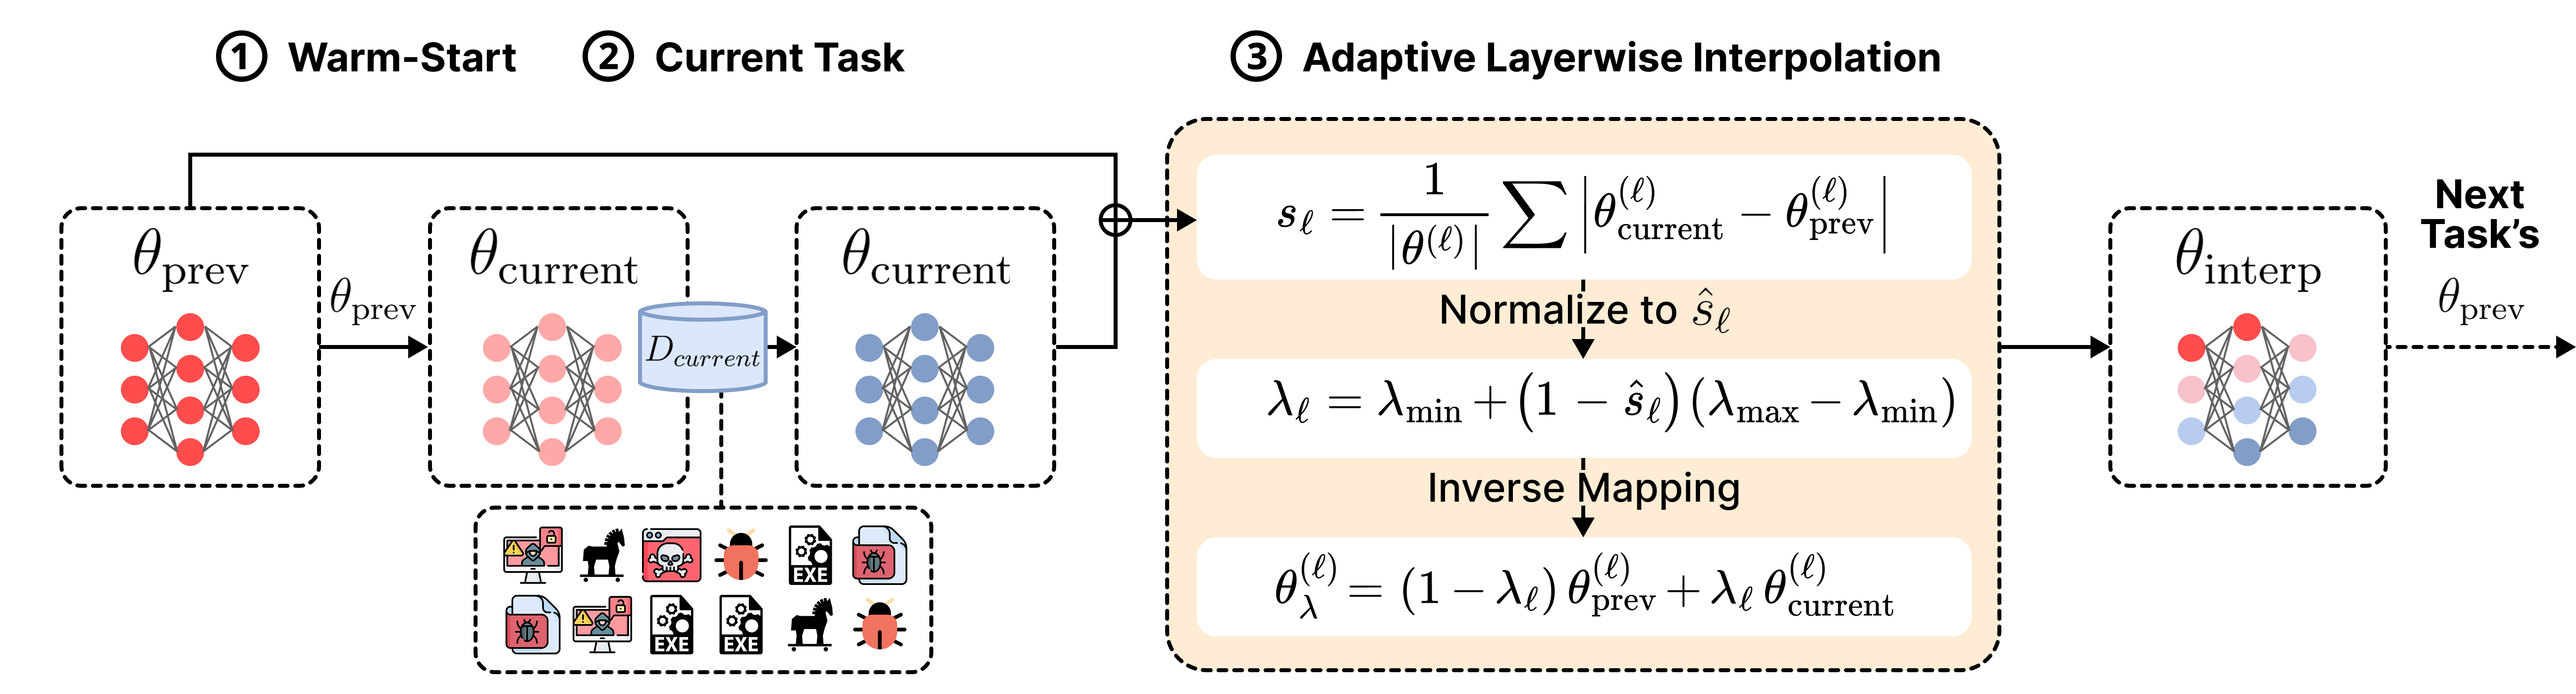 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 scs-labrat/android_autorooter
Exfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely
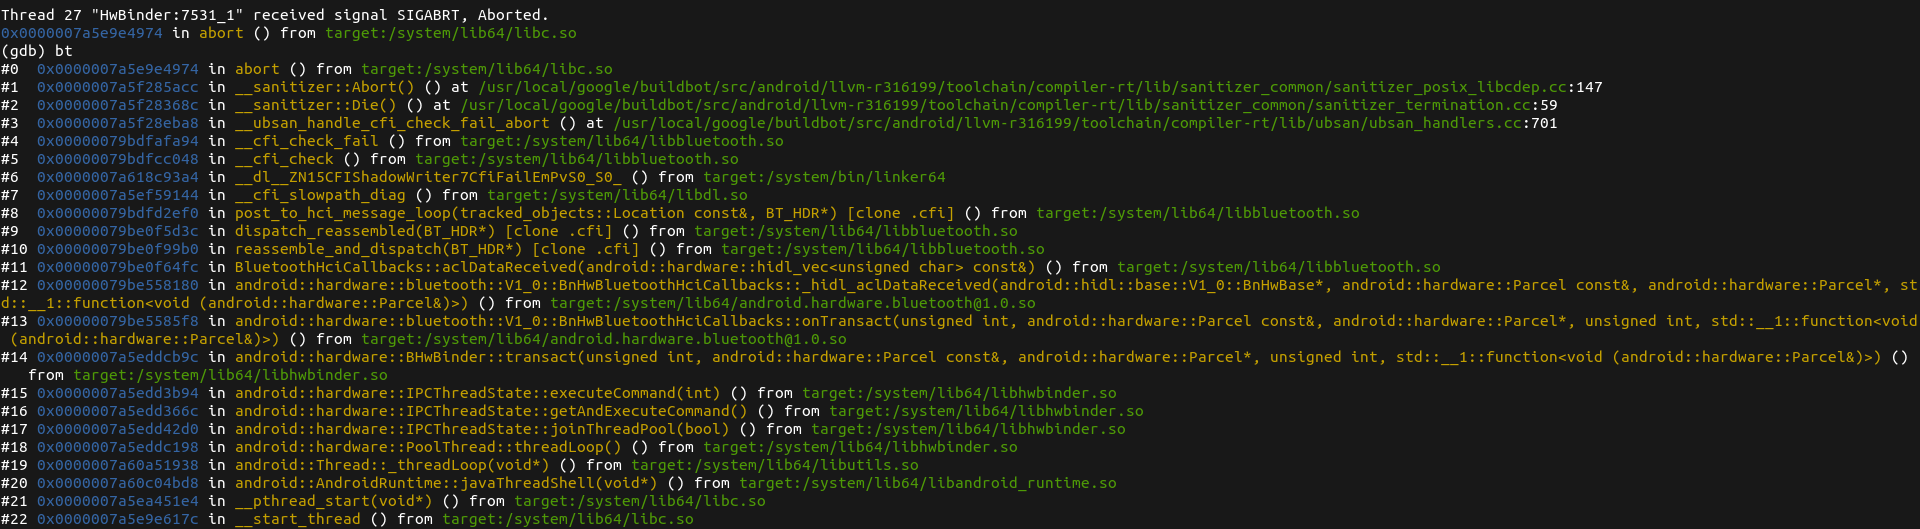 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 leosol/initroot
Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
 naonymous101/cve-2022-46638
Blog Pribadi
 tamirzb/cve-2019-14040
PoC code for CVE-2019-14040
 tamirzb/cve-2019-14041
PoC code for CVE-2019-14041
 mranonymoustz/cve-2019-11932-whatsapp-exploit
Double-free vulnerability in DDGifSlurp in decoding.c in libpl_droidsonroids_gif can read more…
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 vikramaditya015/samsung-android-lpe
Poc for CVE-2026-20980, CVE-2026-20981, CVE-2026-20982
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
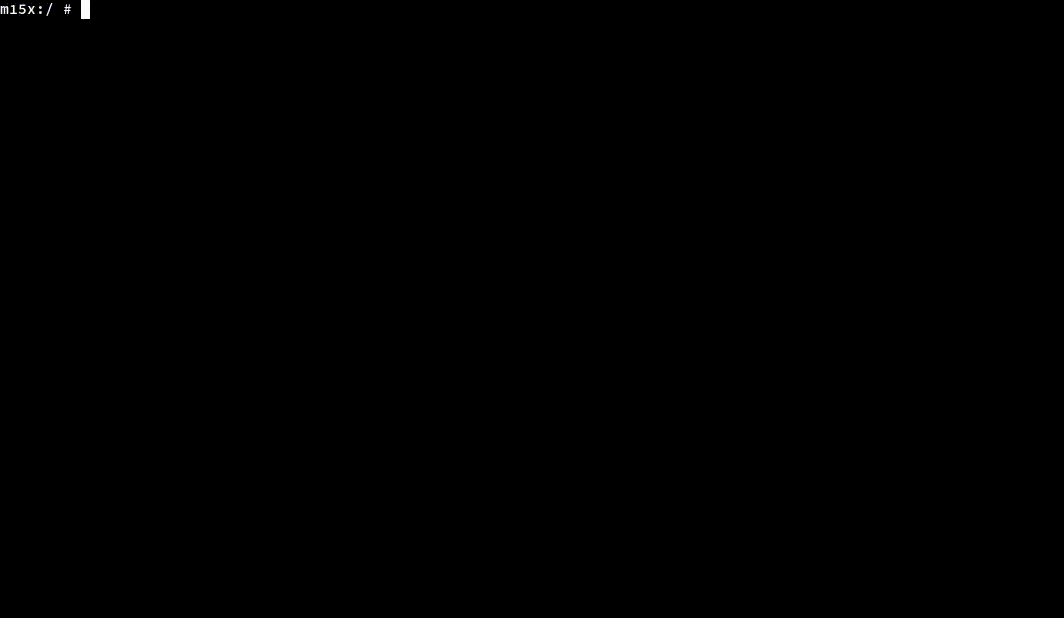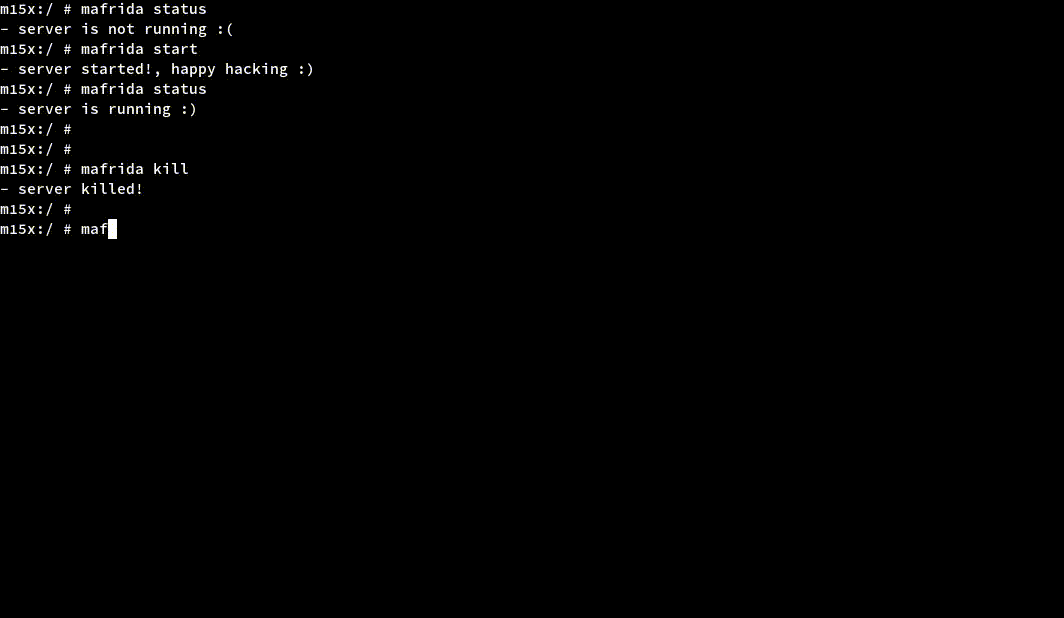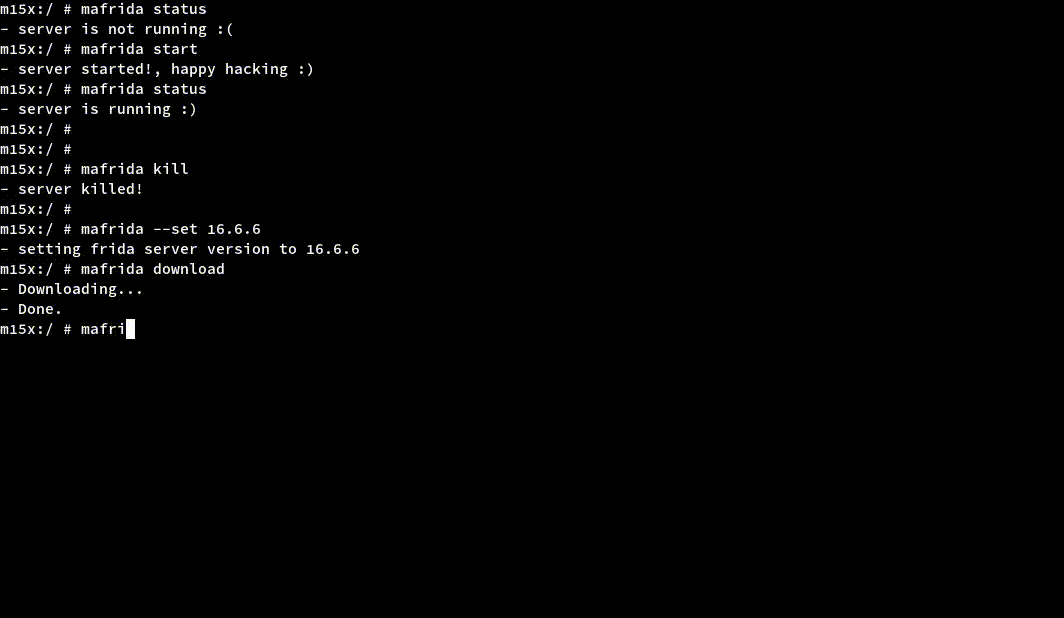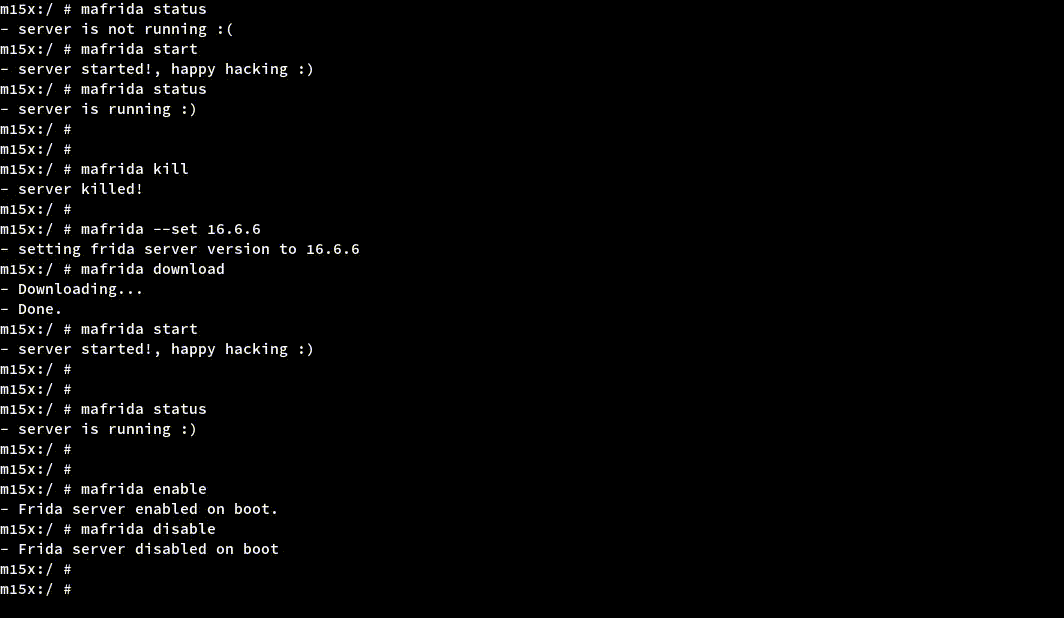 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…