
cve-2019-2215-markw
 begitdj/cve-2019-2215-markw
Exploit for CVE-2019-2215 to gain temporary root on Xiaomi MIUI devices, enabling bootloader unlock and system modifications.
android-securitybinary-exploitationexploitation+4
1
begitdj/cve-2019-2215-markwExploit for CVE-2019-2215 to gain temporary root on Xiaomi MIUI devices, enabling bootloader unlock and system modifications.
 nanoturtle1145/root-my-s24
Using CVE-2026-43499 to root your Galaxy S24 Series(SM-S92X0 ,(China / Hong Kong SAR / Taiwan))
 wxxsfxyzm/ghostlock-galaxy
Root your Galaxy using CVE-2026-43499
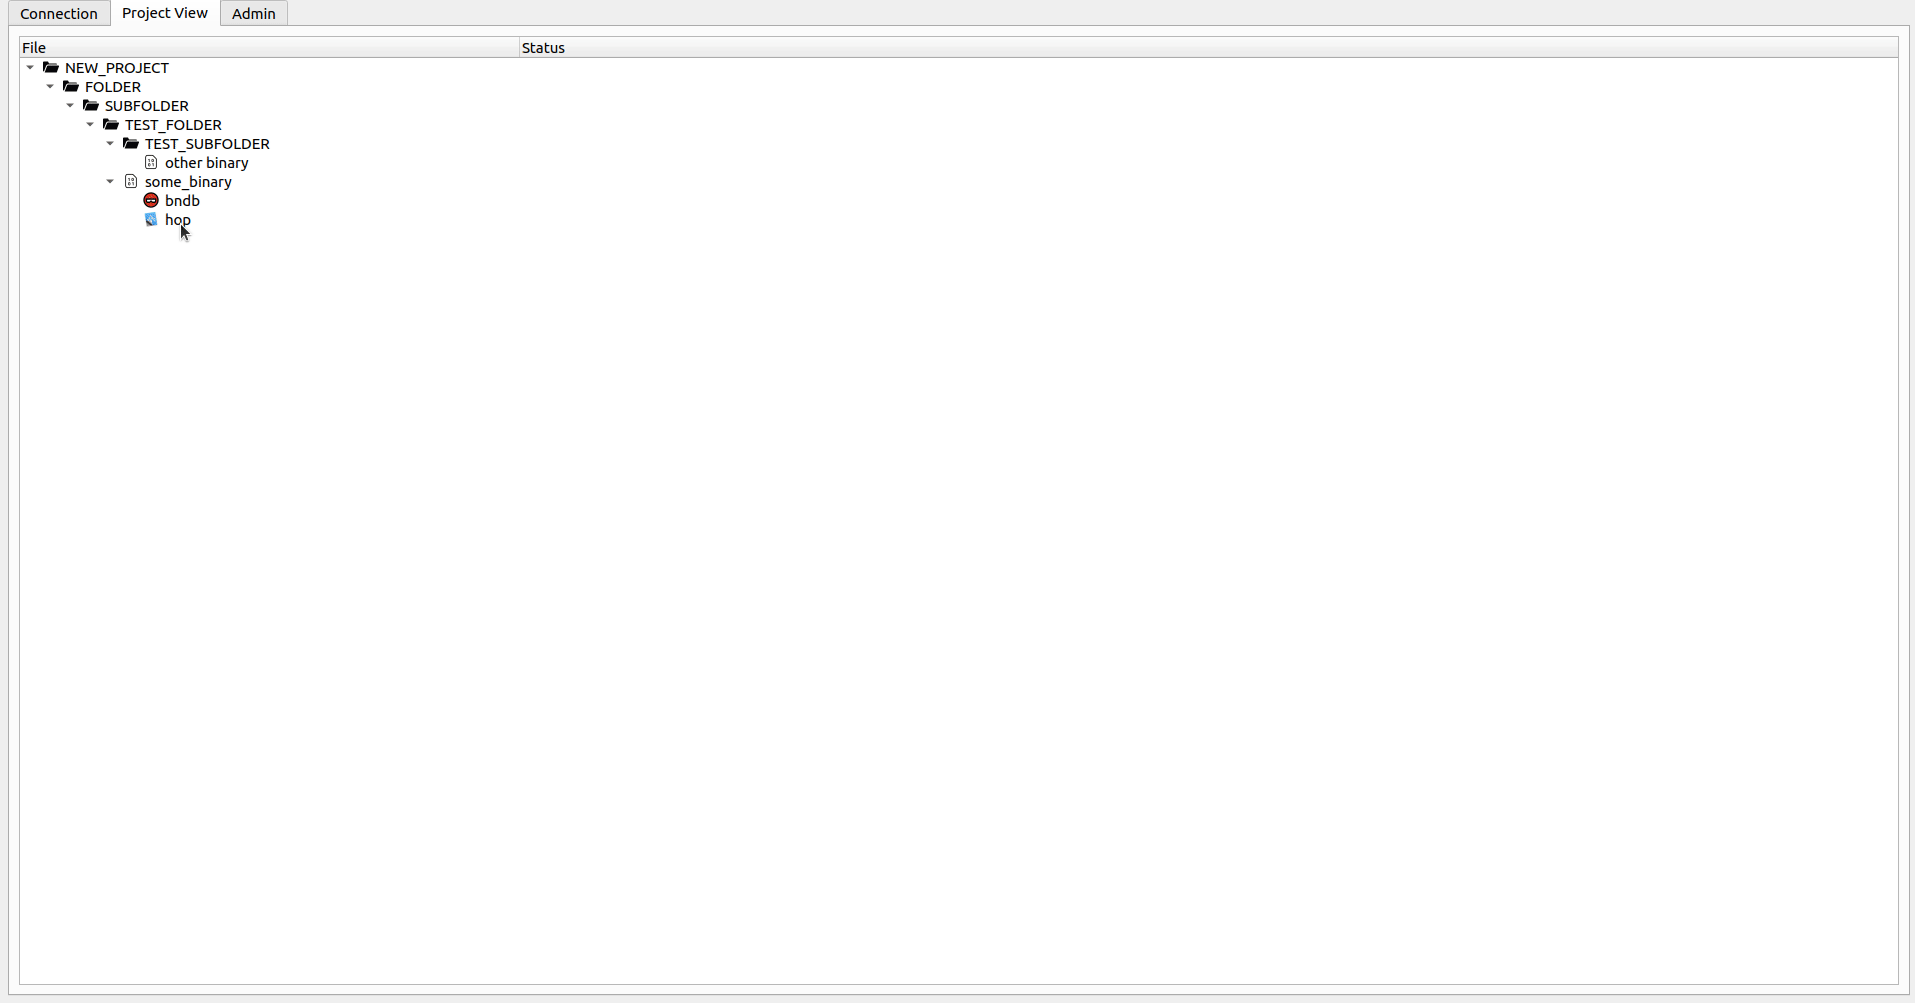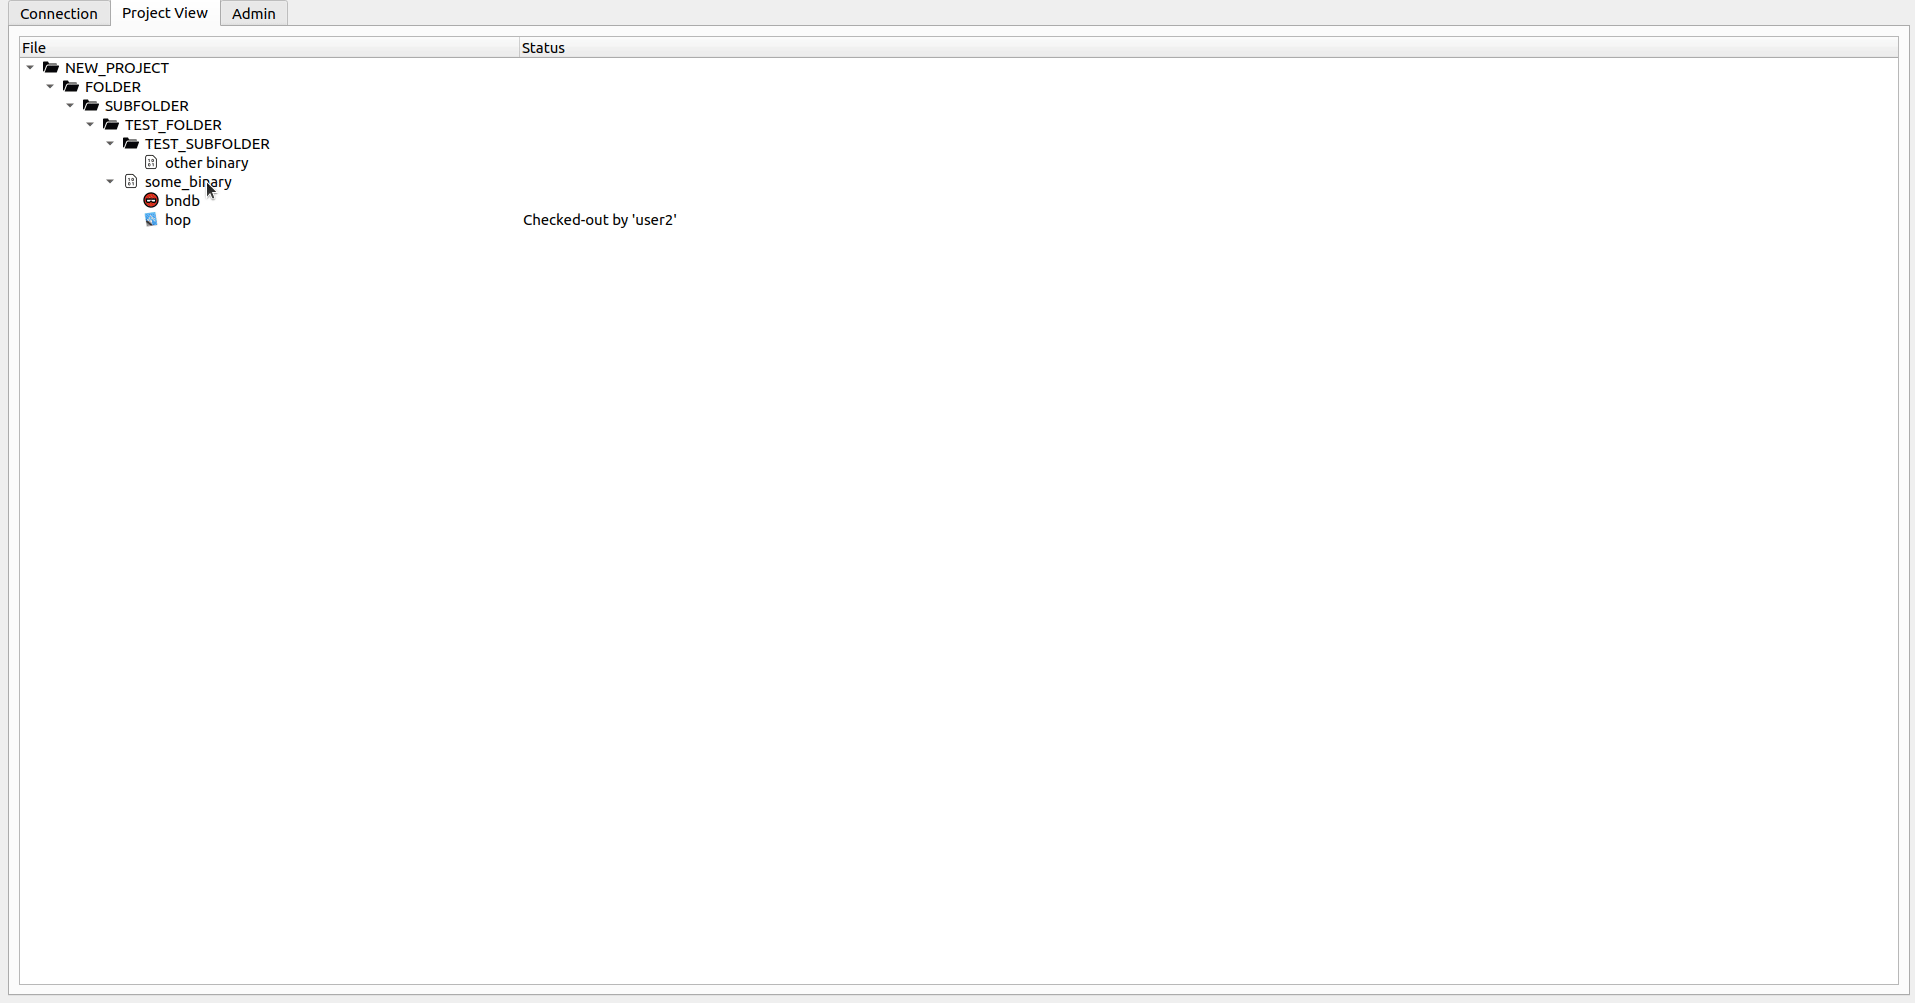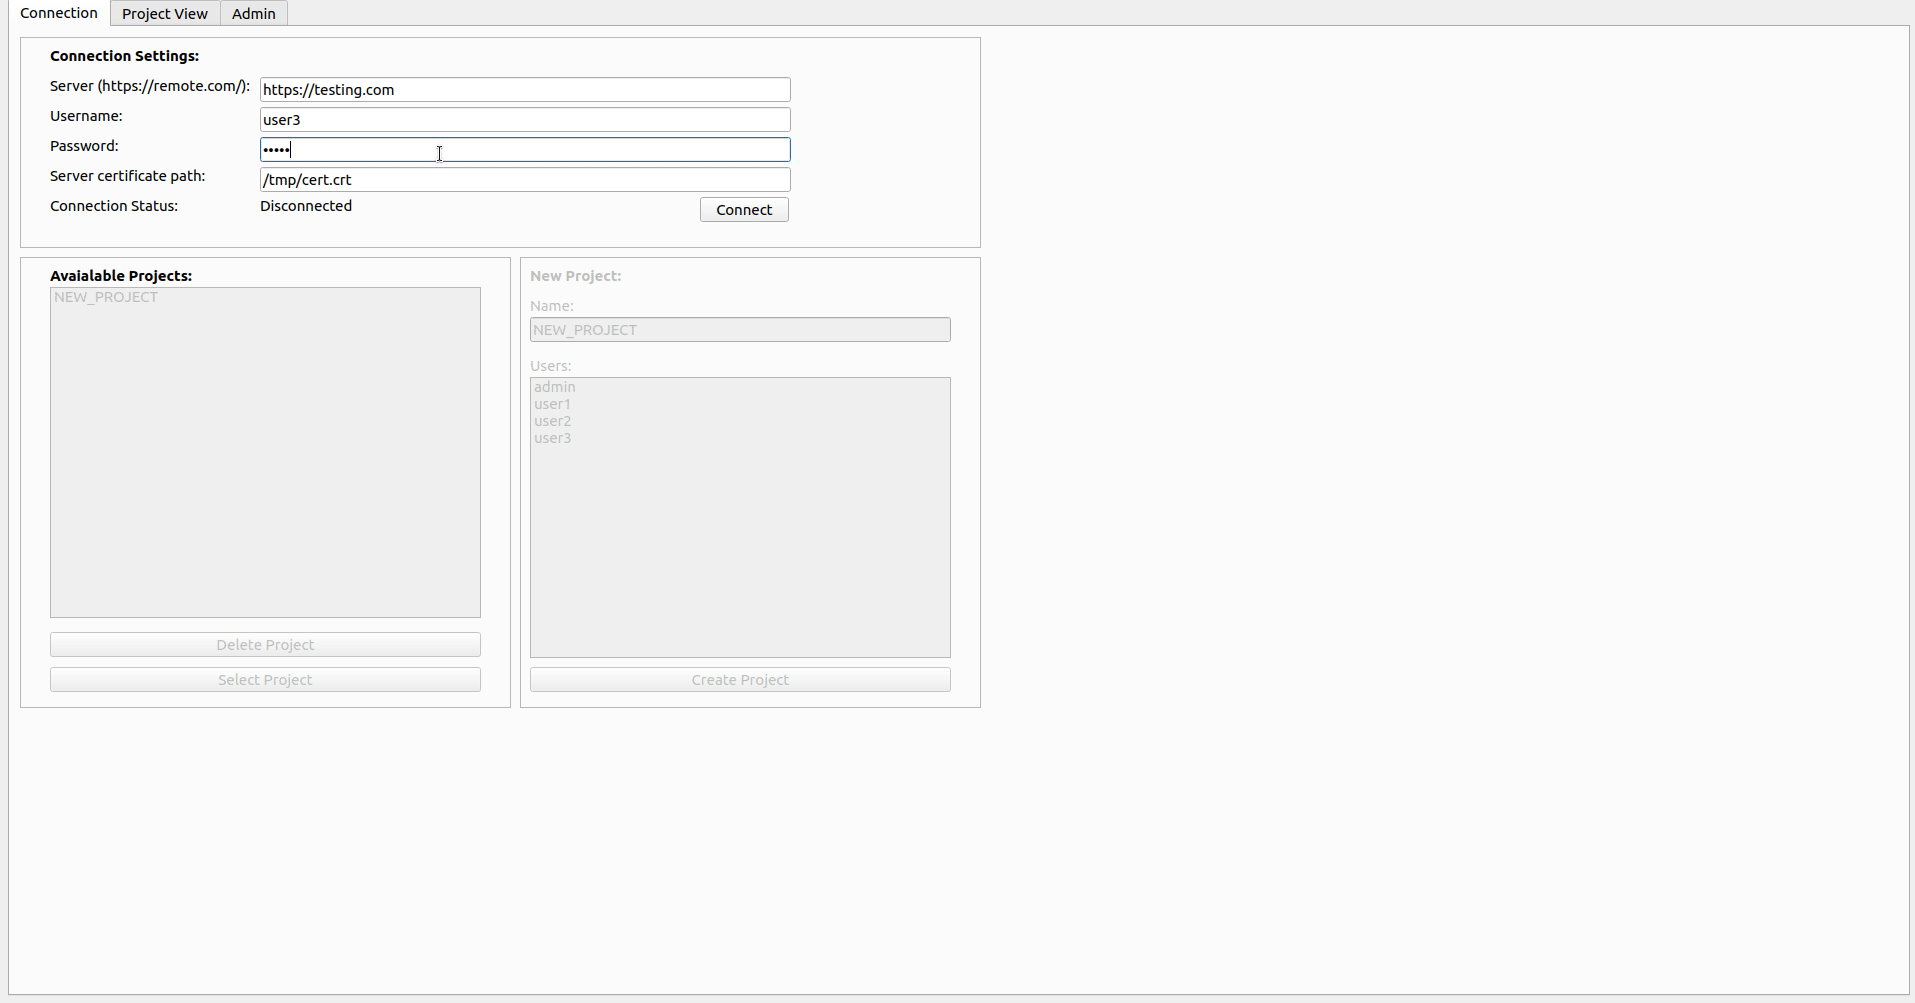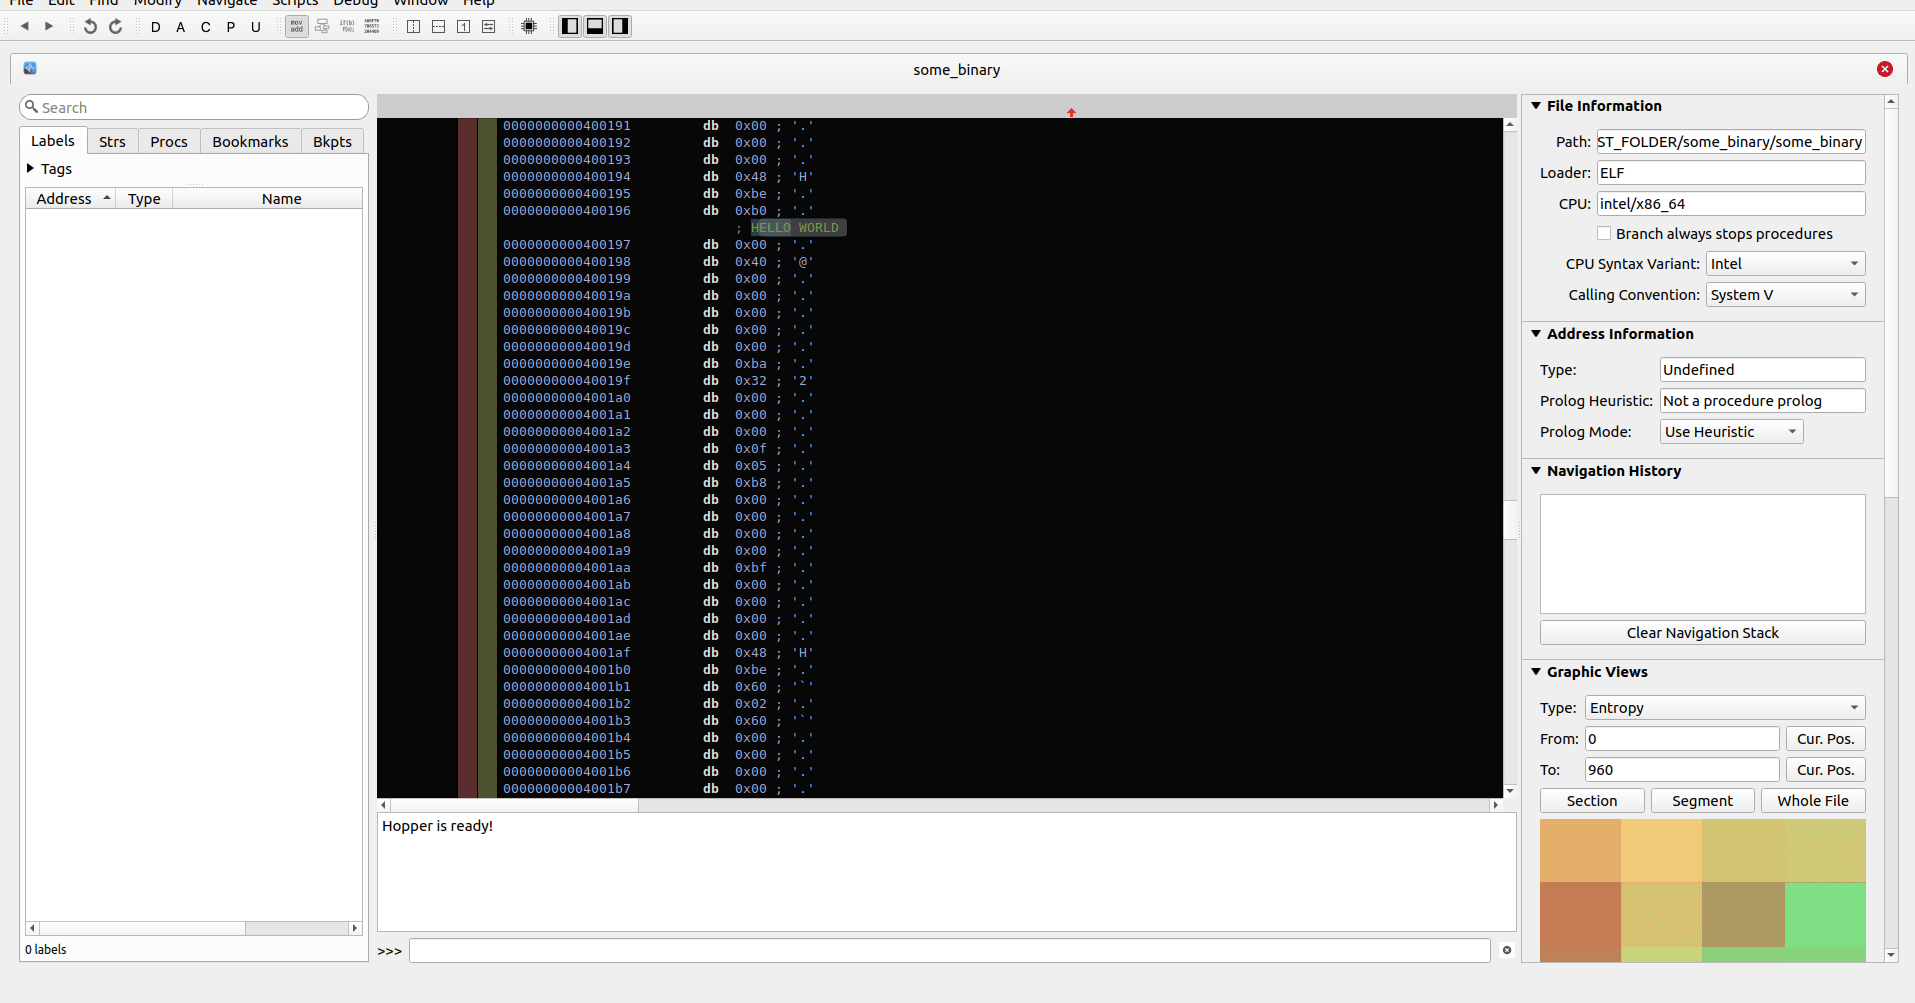 martyx00/collare
Multi-tool reverse engineering collaboration solution.
 universal-debloater-alliance/universal-android-debloater-next-generation
Cross-platform GUI written in Rust using ADB to debloat non-rooted Android devices. Improve your privacy, the security and battery life of your…
 viliuskraujutis/androidbroadcastsmonitor
A tool to subscribe to receive all standard Android broadcasts on your Android device.
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
 huntoai/rdroid
[Android RAT] Remotely manage your android phone using PHP Interface
 android1500/androidfaker
Android Faker a Simple Xposed Module Which Spoof Your Device IDs Values. Supporting Android 8.1+
 roeeh/bootmodechecker
This app checks if you're vulnerable to CVE-2016-8467 and/or if your bootmode property has been tampered with.
 tinopreter/docviewerexploitapp
This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…
 pwnaccelerator/stagefright-cve-2015-3864
PoC - Binary patches for CVE-2015-3864 (NOT for production, use at your own risk)
 sunnyjiang/shellshocker-android
This is an Android Application that helps you detect if your machine that run bash is vulnerable by CVE-2014-6271
 gopartner/realme-c53-unlock-root
Bootloader unlock (CVE-2022-38694) & root guide for Realme C53 / RMX3760 (Unisoc T612)
 leosol/initroot
Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 timwr/cve-2013-6282
CVE-2013-6282 proof of concept for Android
 roeeh/conscryptchecker
This app verifies if your device is still vulnerable to CVE-2015-3825 / CVE-2015-3837, aka "One Class to Rule Them All", by checking if it contains…