
CVE-2026-27280
 r3n3r0/cve-2026-27280
In-depth analysis and proof-of-concept for CVE-2026-27280, an out-of-bounds write in Adobe DNG SDK's dng_render_task::ProcessArea, reachable via…
android-securitybinary-exploitationexploitation+5
1
r3n3r0/cve-2026-27280In-depth analysis and proof-of-concept for CVE-2026-27280, an out-of-bounds write in Adobe DNG SDK's dng_render_task::ProcessArea, reachable via…
 alphabugx/cve-2025-54957
Proof-of-concept exploit for CVE-2025-54957, an out-of-bounds write in Dolby's DDPlus Unified Decoder, demonstrating a 0-click crash on Android via…
 hunt-benito/two-dots-and-a-slash-cve-2026-18907-tecno-hi-browser-download-path-traversal
Python PoC for CVE-2026-18907 path traversal in TECNO Hi Browser's download handler. Includes malicious HTTP server and naive downloader to…
 kalilinux/nethunter/build-scripts/kali-nethunter-installer
Builds flashable installer ZIPs that deploy a mobile penetration-testing environment on Android, including kernel boot patching, rootfs integration,…
 neternels/android_kernel_xiaomi_sunny
CAFest nethunter kernel based on LA.UM.9.1.r1-11900-SMXXX0.0 with latest upstream-f2fs-stable-linux-4.14.y merged, bb and perf focused. | Force push…
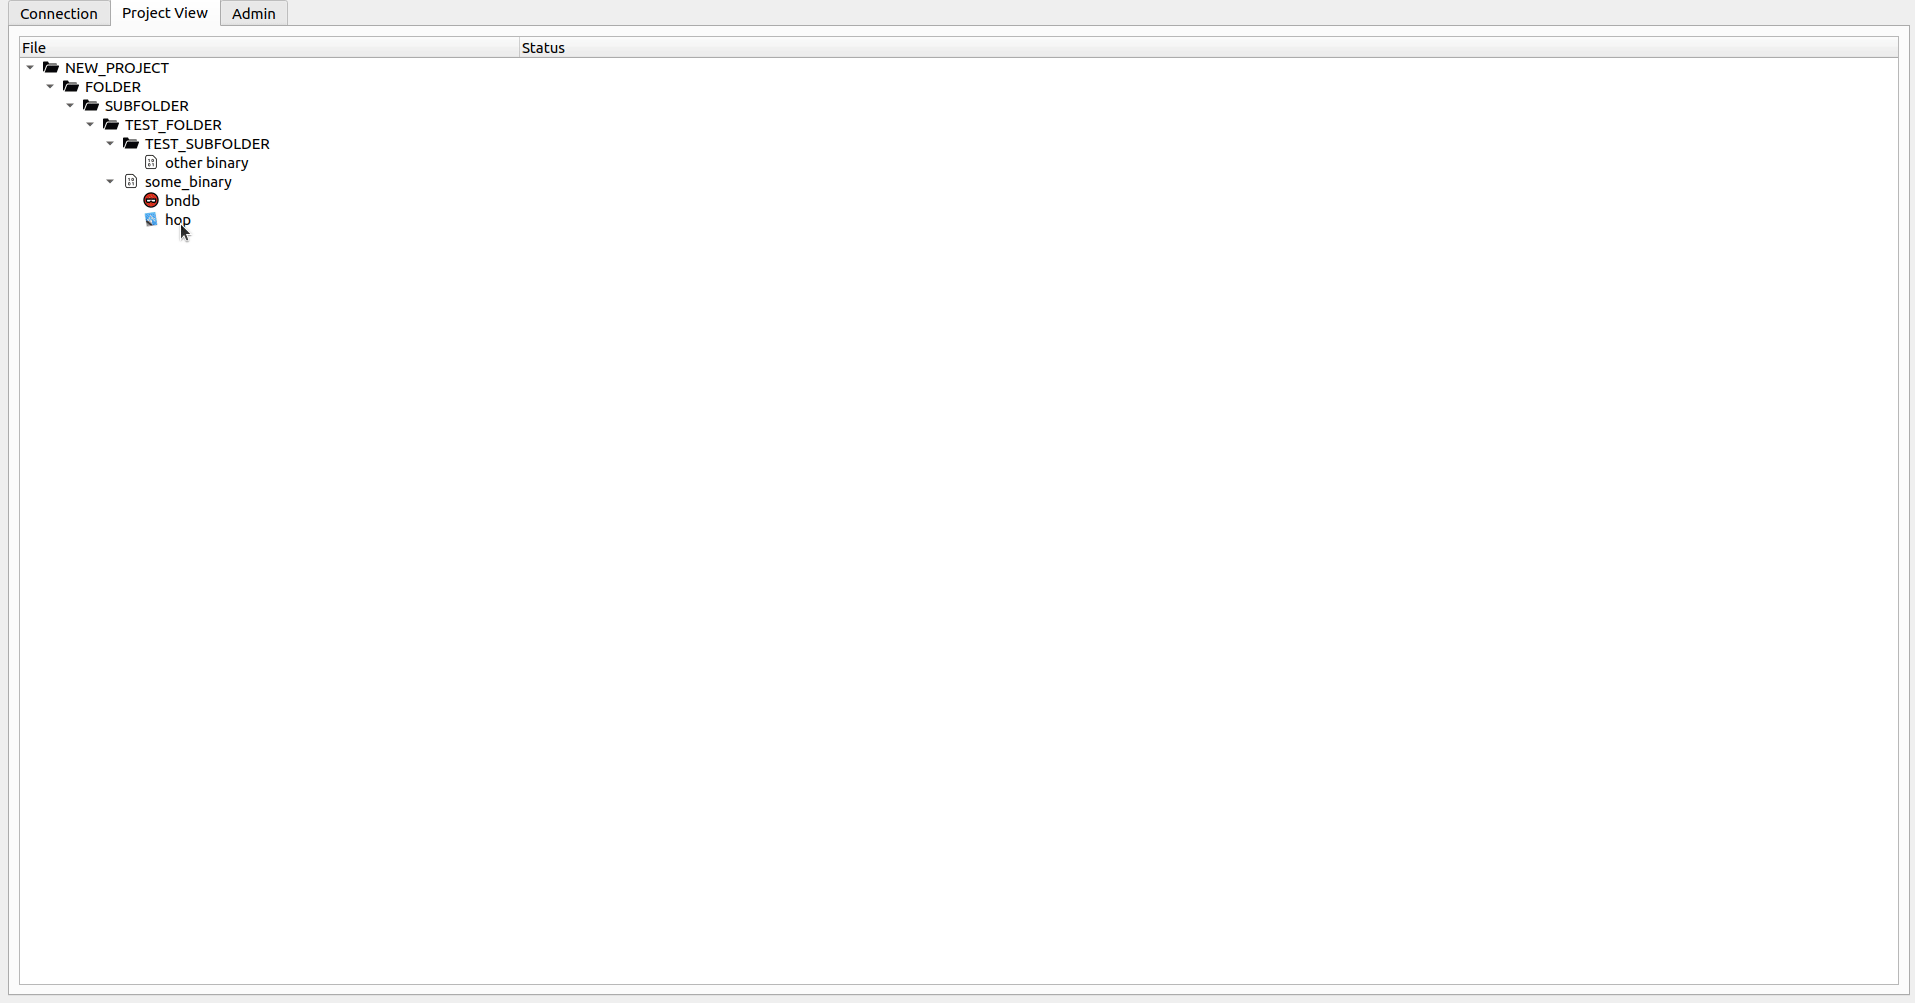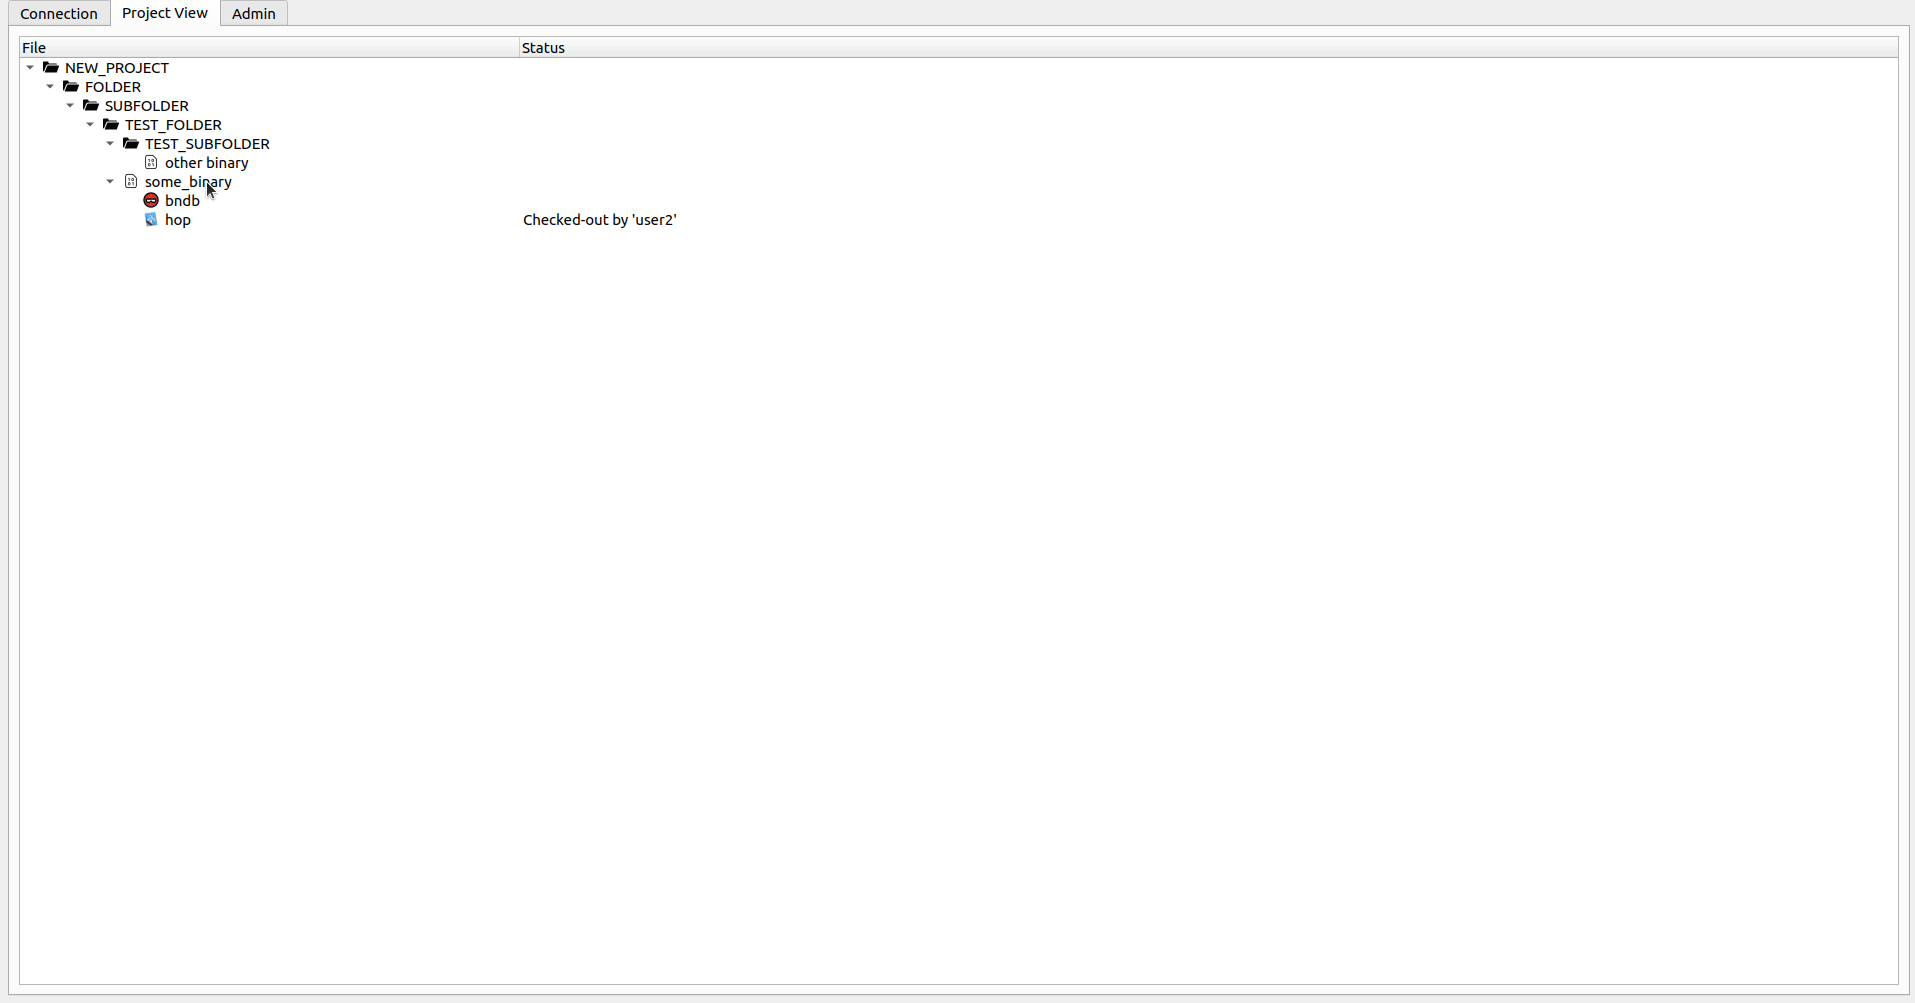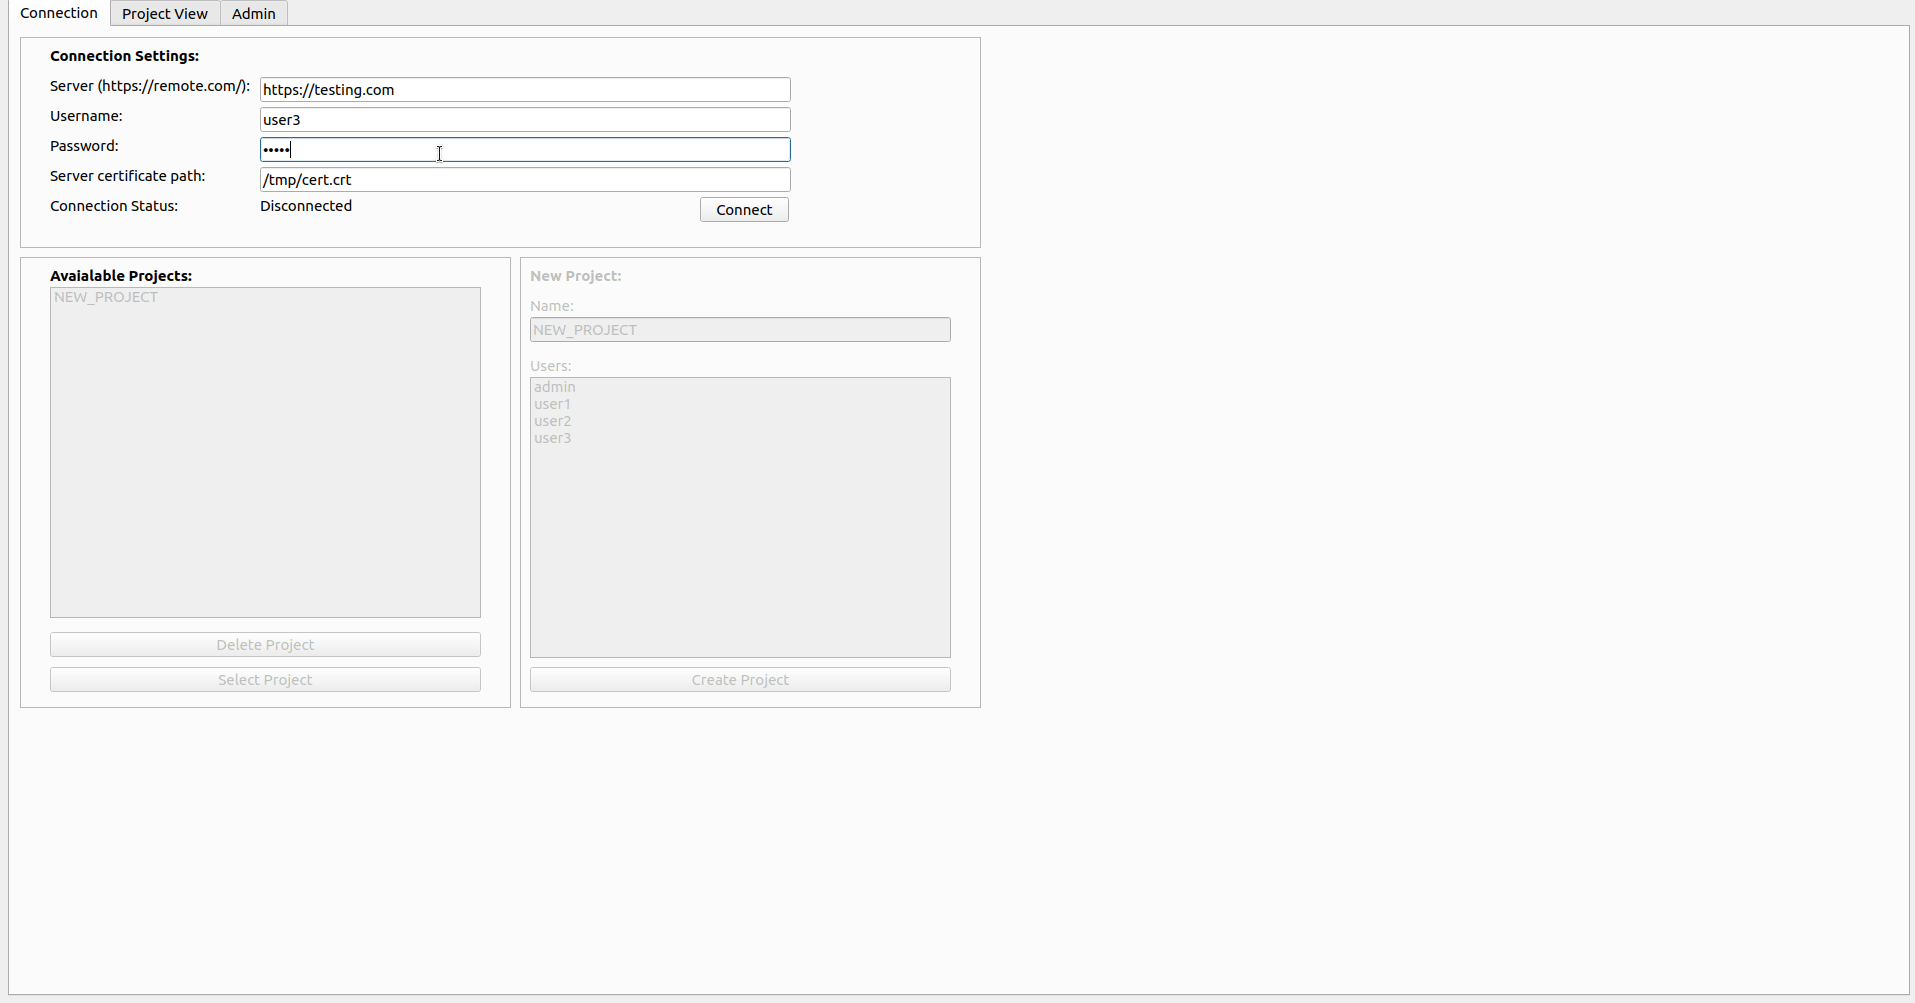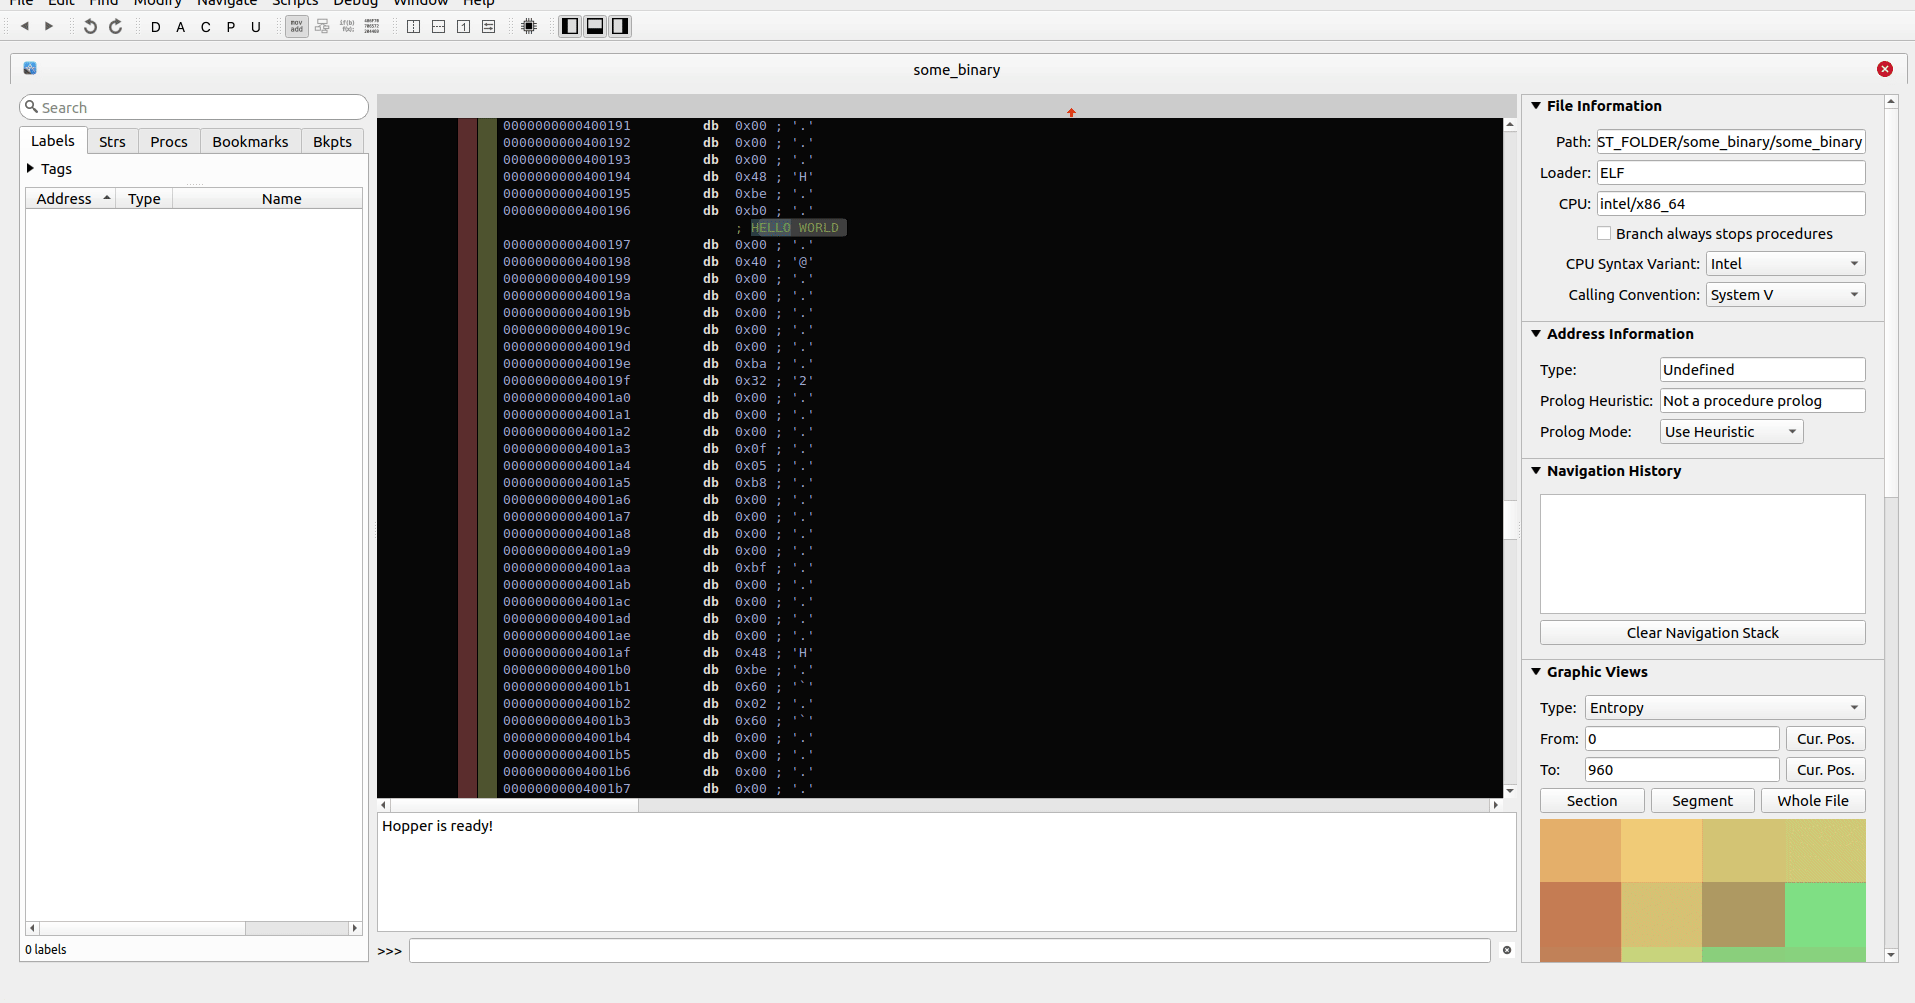 martyx00/collare
Multi-tool reverse engineering collaboration solution.
 skorpion96/cve-2026-40000
A poc for a vulnerability in ZTE File Manager (zte.com.cn.filer) which allows to read arbitrary files from other apps as the privileges of this file…
 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
 mwsrc/betterandrorat
Android Remote Access Trojan
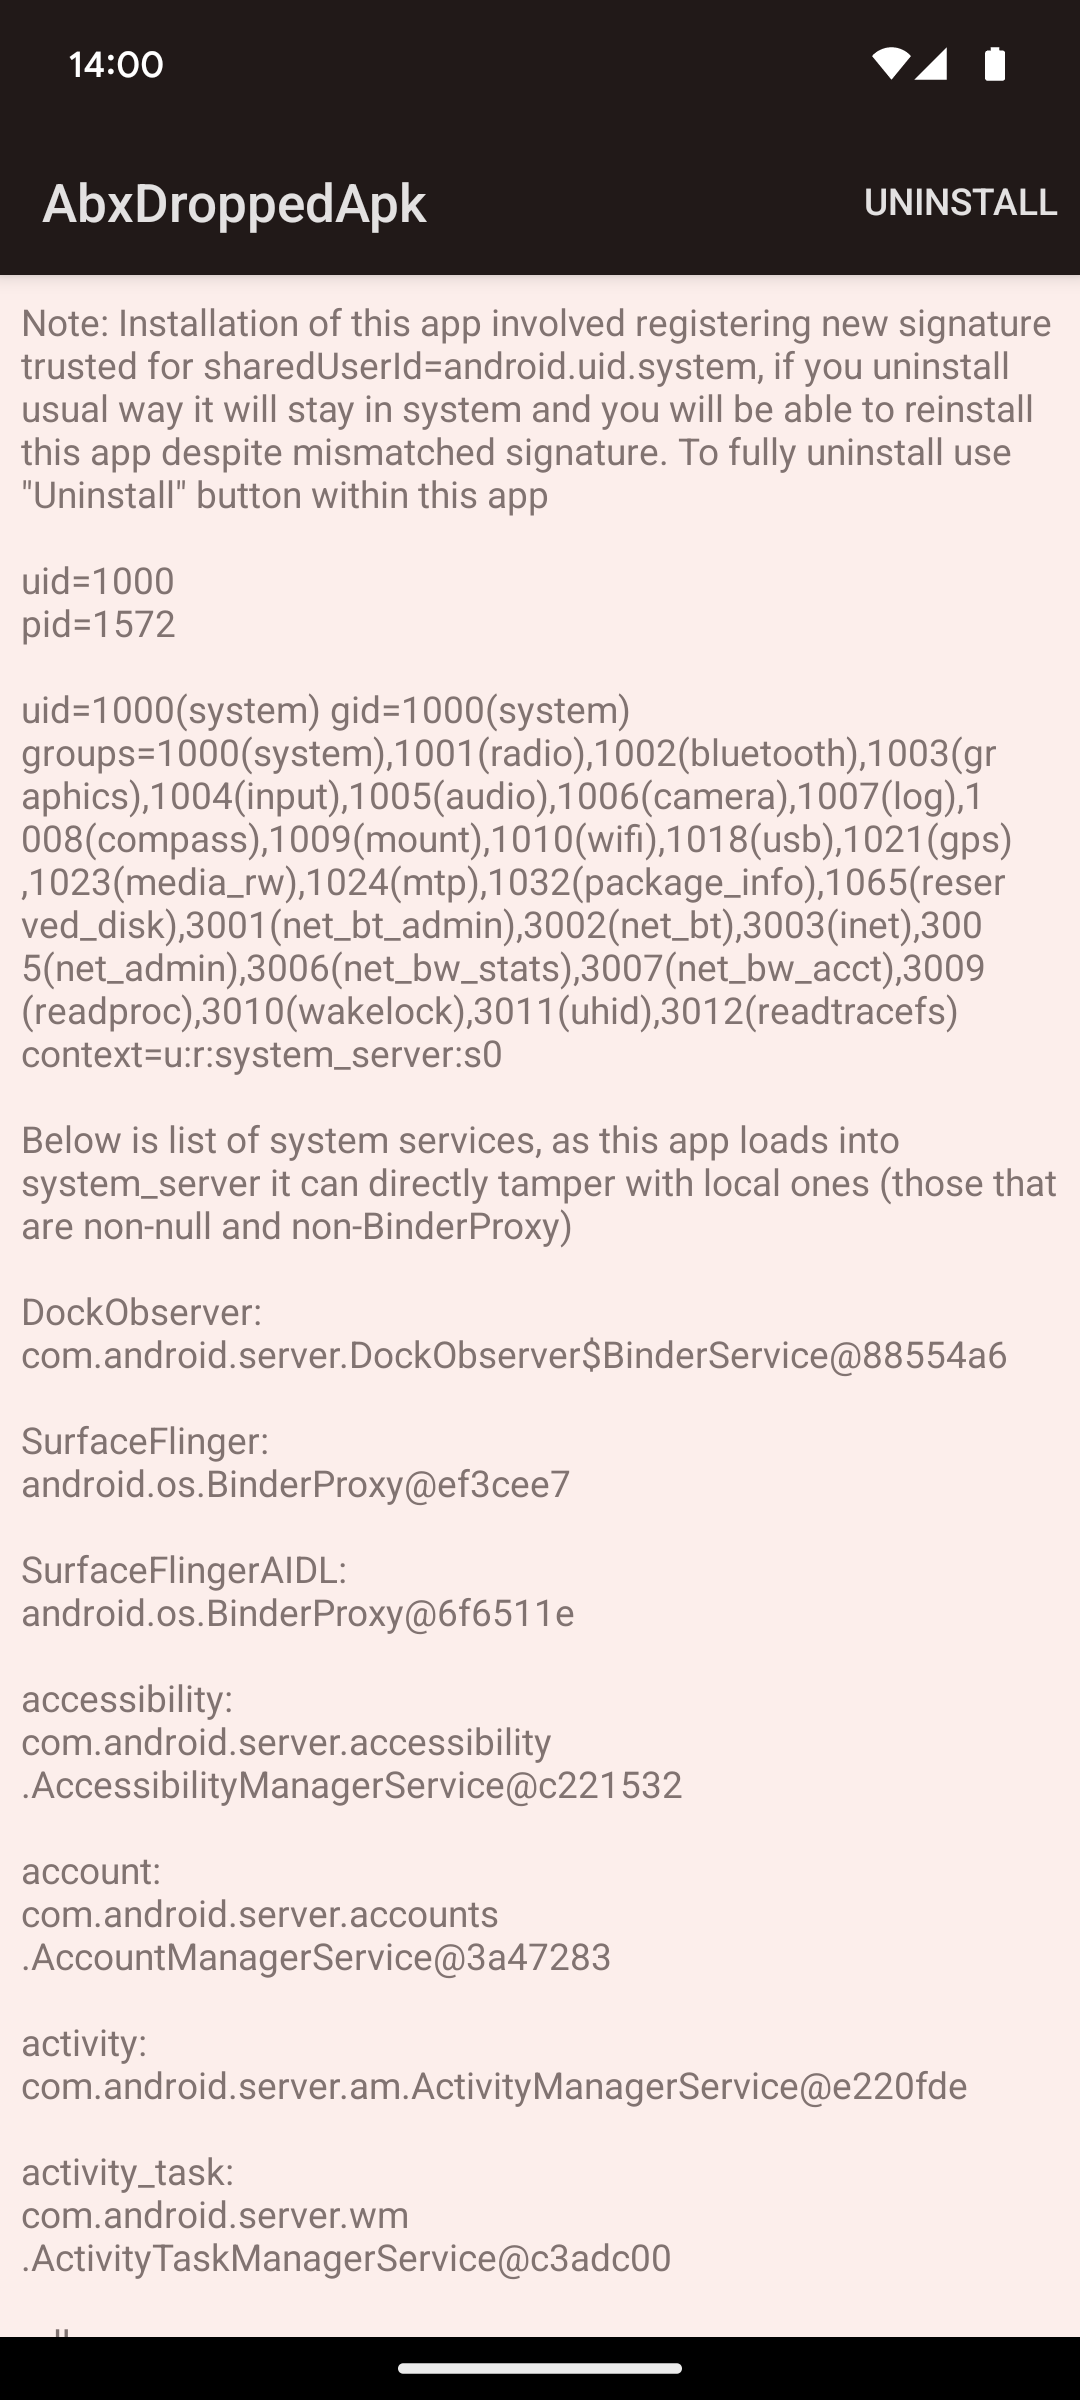 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used
 xyzasian/janus-cve-2017-13156
Java-based exploit tool for CVE-2017-13156 that bypasses Android APK signature verification by appending a DEX file to an existing APK, enabling code…
 purseclab/cve-2023-33768
DoS against Belkin smart plugs via crafted firmware injection
 haxatron/cve-2022-0219
Proof-of-concept exploit for CVE-2022-0219, an XXE vulnerability in Jadx that allows local file disclosure when exporting malicious APK files via the…
 vino-theva/cve-2019-6447
This paper is about manual exploitation of android open port vulnerability found in ES file manager. This open TCP 59777 port allows the attacker to…
 osuni-99/cve-2019-6447
The above investigation of the ES file browser security weakness allows us to see the issue in its entirety
 seqred-s-a/cve-2019-14220
Arbitrary file read in BlueStacks
 valbrux/cve-2019-11932-supportapp
This native code file aims to be complementary to the published Whatsapp GIF RCE exploit by Awakened , by calculating the system() function address…