
CVE-2026-98260
 woshigenm/cve-2026-98260
Android kernel LPE research for CVE-2026-98260 (posix-cpu-timers UAF): trigger PoC, fake-cred and real-cred uid-0 shell chains, plus a…
android-securitybinary-exploitationexploitation+5
4
woshigenm/cve-2026-98260Android kernel LPE research for CVE-2026-98260 (posix-cpu-timers UAF): trigger PoC, fake-cred and real-cred uid-0 shell chains, plus a…
 kpgc10kai/timerroot
Android front end for CVE-2026-98260: root shell + KernelSU late-load through Shizuku
 interplains/zero-breach-toolkit
Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.
 wonjj6768/lenovo-tb365fc-ghostlock-cve-2026-43499
GhostLock (CVE-2026-43499) root + KernelSU LKM for the Lenovo TB365FC (ZUXOS / Android 16, kernel 5.15.170)
 k-o-n-t-o-r/ghostlock-sabrina
CVE-2026-43499 GhostLock root exploit for Chromecast with Google TV (sabrina)
 woaphone/cve-2021-28664-poc
PoC skeleton for CVE-2021-28664, a Mali kbase GPU driver use-after-free, demonstrating a kernel arbitrary physical memory read/write primitive on…
 cyberbalsa/ghostlock-nvidia-shield-9.2.4
Validated GhostLock CVE-2026-43499 port for NVIDIA Shield TV Pro mdarcy 9.2.4
 cxyofficial/k50g-pocof4gt-cve-2026-43499-poc
Local privilege escalation exploit for Redmi K50G/POCO F4 GT using CVE-2026-43499 (futex UAF) to gain temporary root and load KernelSU without…
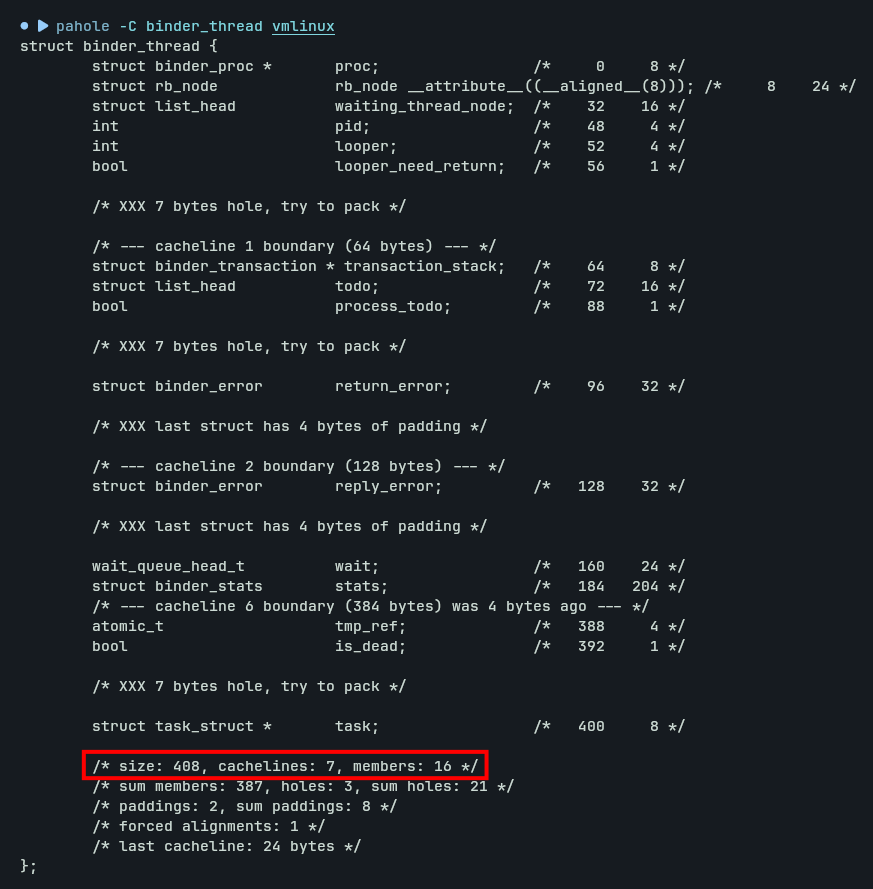 0xbinder/cve_2019_2215
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.
 yijiacloud/ghostlock-oppo-pckm00
CVE-2026-43499 GhostLock futex UAF LPE PoC for OPPO PCKM00 (SM6150) / Linux 4.14.180
 kuzeyardabulut/cve-2025-8045
Dirty Pagetable Exploit for CVE-2025-8045
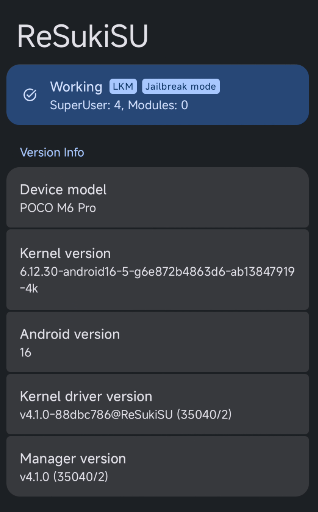 datfooldive/ghostlock-emerald
GhostLock (CVE-2026-43499) kernel exploit for Poco M6 Pro (emerald) with locked bootloader
 soralis0912/cve-2026-43499-pmg110-root
Android LPE exploit for CVE-2026-43499 targeting OPPO PMG110 (kernel 6.6). Uses futex PI UAF to gain root and install a su daemon via LD_PRELOAD.
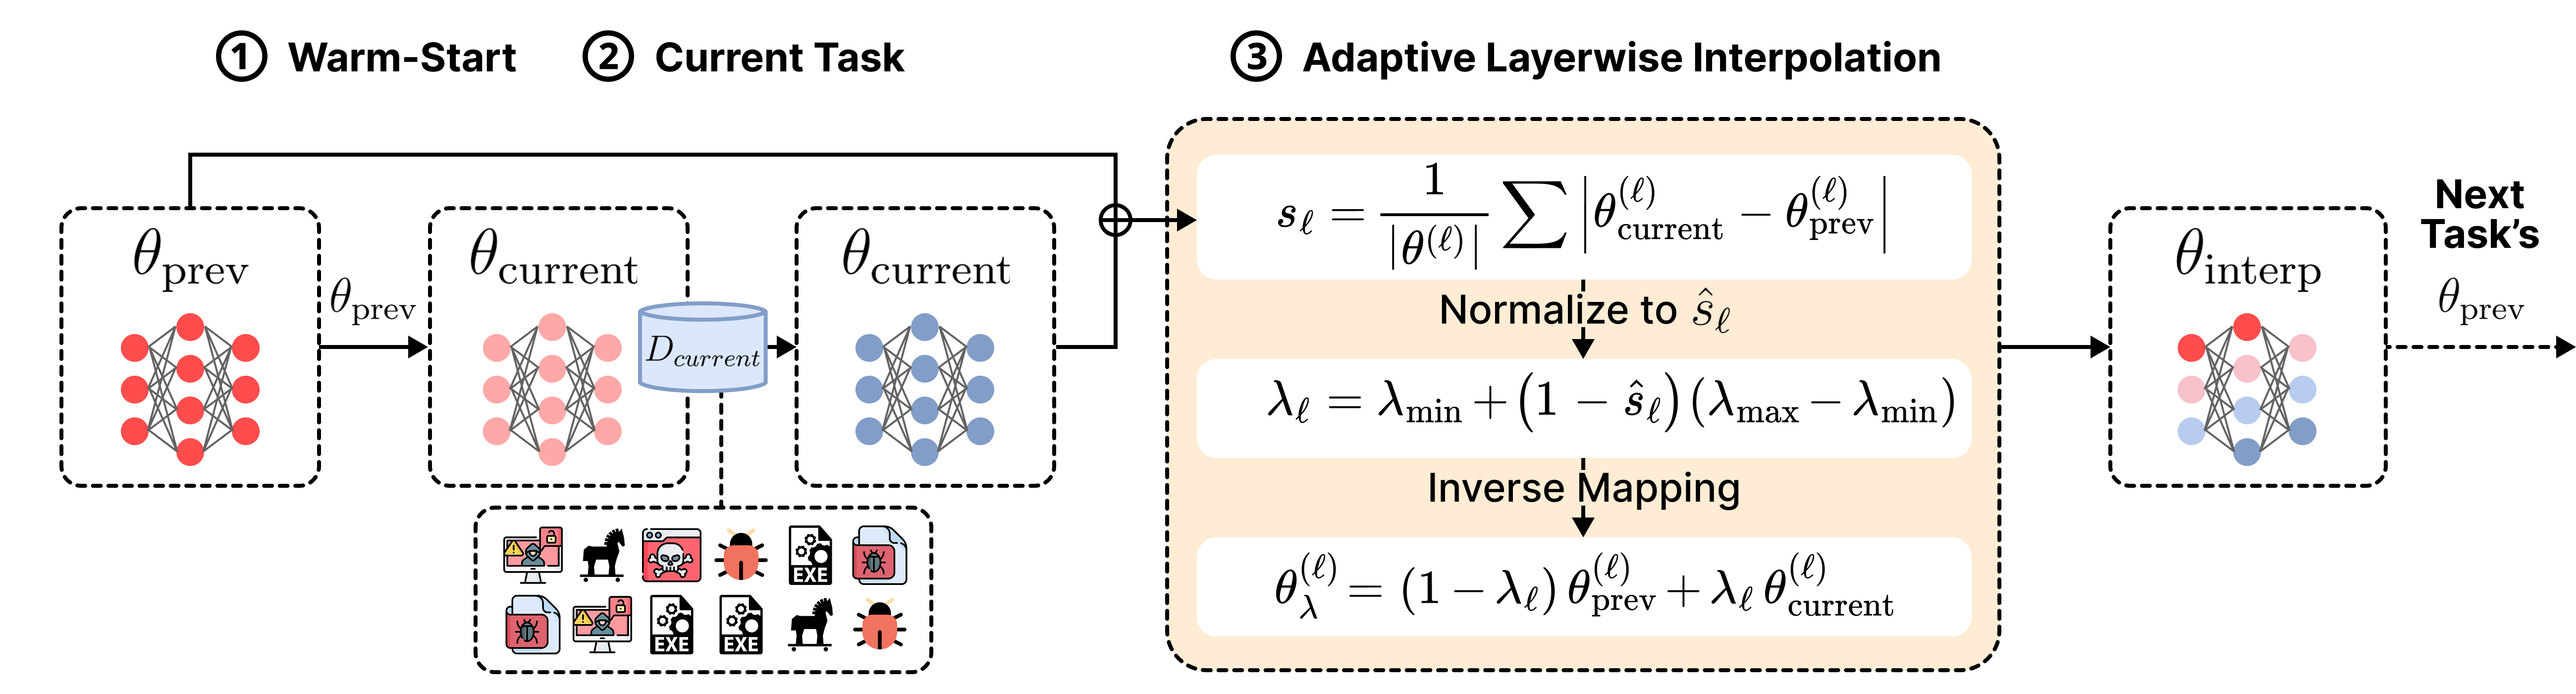 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 nestle19/cve-2019-2215
Android kernel exploit for CVE-2019-2215, a use-after-free in the Binder driver, enabling privilege escalation to root via memory corruption and cred…
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
 alirezaparsi/copg
Advanced per-app device / CPU / GPU spoofer for rooted Android — device profiles, per-app CPU models, prop & Android-ID spoofing, all driven by a…
 infiniteloopers/cve-2019-11932
Technical write-up and exploit code for CVE-2019-11932, a double-free vulnerability in WhatsApp for Android that leads to remote code execution via a…