

Gu3ssWeak
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
android-securityctfeducation+7
121 month ago
b4sith-sec/gu3ssweakDeliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 techupdate24/capacitor-flaw-cve-2026-103922
A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 georgiev-martin/nofrak
Proof Of Concept for Android. NoFrak is designed to prevent fracking attacks, as described in "Breaking and Fixing Origin-Based Access Control in…
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 grant-h/qu1ckr00t
A PoC application demonstrating the power of an Android kernel arbitrary R/W.
 l0lsec/cve-2026-12960
CVE-2026-12960 - Improper Export of Android Application Components in the ASUS Router app (com.asus.aihome). PoC, exploit APK, video, and vendor…
 commando-x/vuln-bank-mobile
A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…
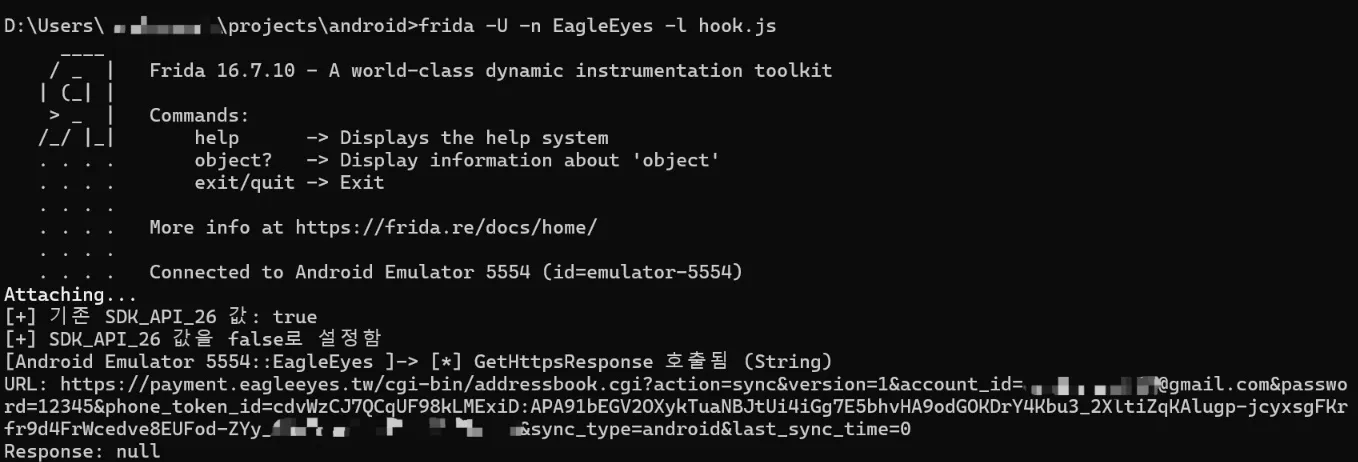 shinycolumn/cve-2025-46408
Improper Hostname Verification in EagleEyes Lite Android Application
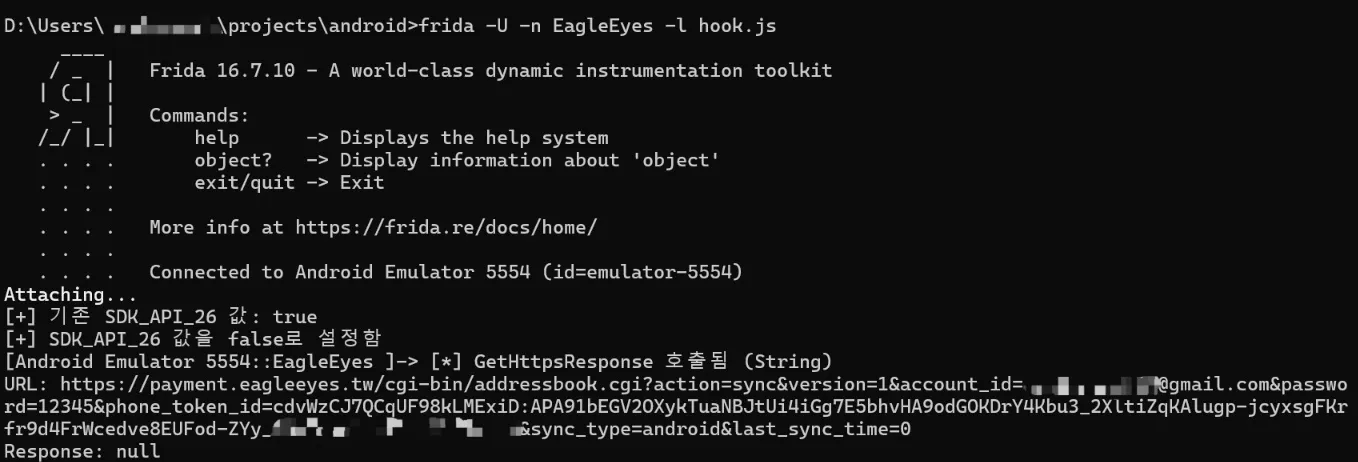 shinycolumn/cve-2025-50110
Cleartext Transmission of Sensitive Information in EagleEyes Lite Android Application
 secmob/pocforcve-2015-1528
I'll submit the poc after blackhat
 shinycolumn/cve-2025-50944
Improper Certificate Chain Validation in EagleEyes Lite Android Application
 ratiros01/cve-2014-8609-exploit
Proof-of-concept exploit for CVE-2014-8609, demonstrating Android pending intent vulnerability exploitation for security research and mobile…
 sterrasec/apk-interceptor
Android deeplink, Intent, and WebView bridge assessment helper for ethical hacking