

Lab-RATS-v1.6
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
android-securitycommand-and-controldata-exfiltration+8
80
k4n3co/lab-rats-v1.6Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
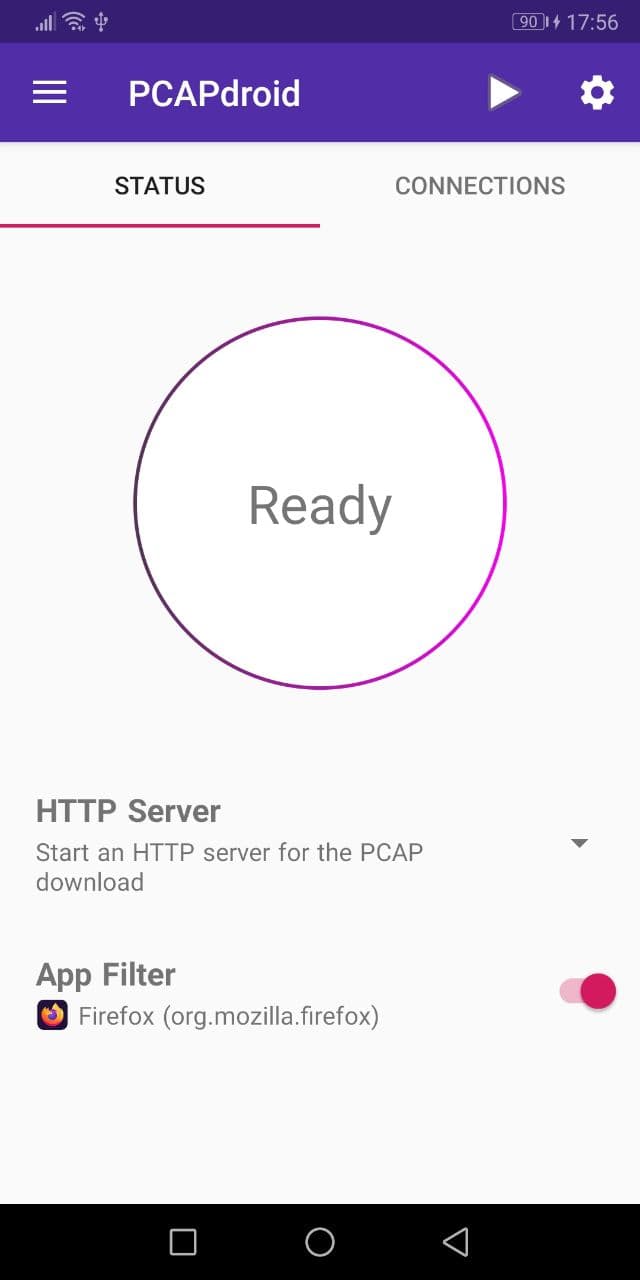 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 maximilianfeix/hexvero
Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
 ironfox-oss/ironfox
Hardened Android web browser forked from Mull/Firefox with privacy-focused patches, anti-fingerprinting, telemetry removal, and secure defaults for…
 user1342/awesome-android-reverse-engineering
A curated list of awesome Android Reverse Engineering training, resources, and tools.
 gvcoder09/nodpi4android
Android proxy app that circumvents Deep Packet Inspection censorship by fragmenting TLS ClientHello packets and rewriting the TLS version to restore…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 may215/awesome-termux-hacking
⚡️An awesome list of the best Termux hacking tools
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
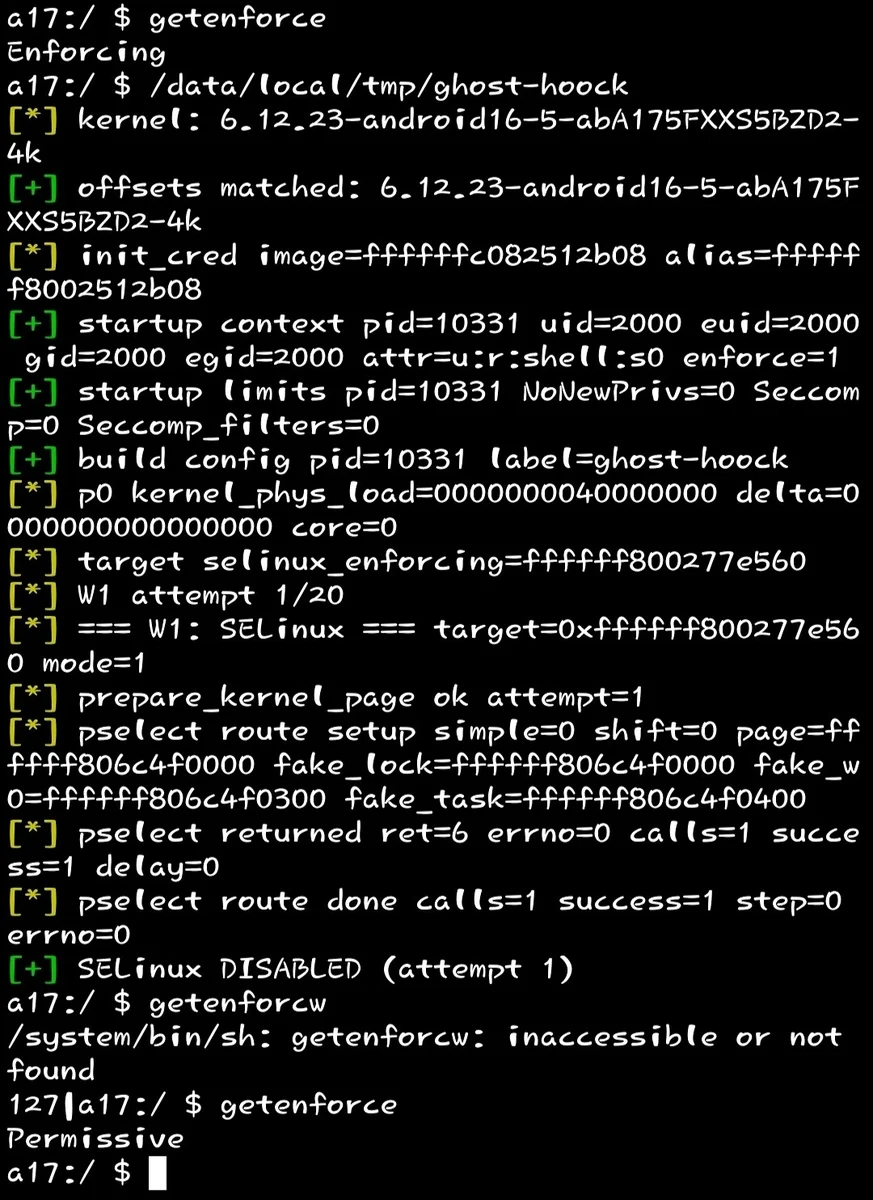 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.