

zaproxy
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
android-securityapi-securityapi-security-testing+15
15.6k
zaproxy/zaproxyOpen-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 trinadh465/packages_apps_nfc_aosp10_r33_cve-2020-0453
Android NFC package patched for CVE-2020-0453, addressing a security vulnerability in the NFC component.
 fs0c131y/esfileexploreropenportvuln
ES File Explorer Open Port Vulnerability - CVE-2019-6447
 unnaim/adbhijacker
A PoC tool for the CVE-2026-0073 on android 11+ devices which allows instant zero click RCE on any unpatched device with adb over tcp enabled
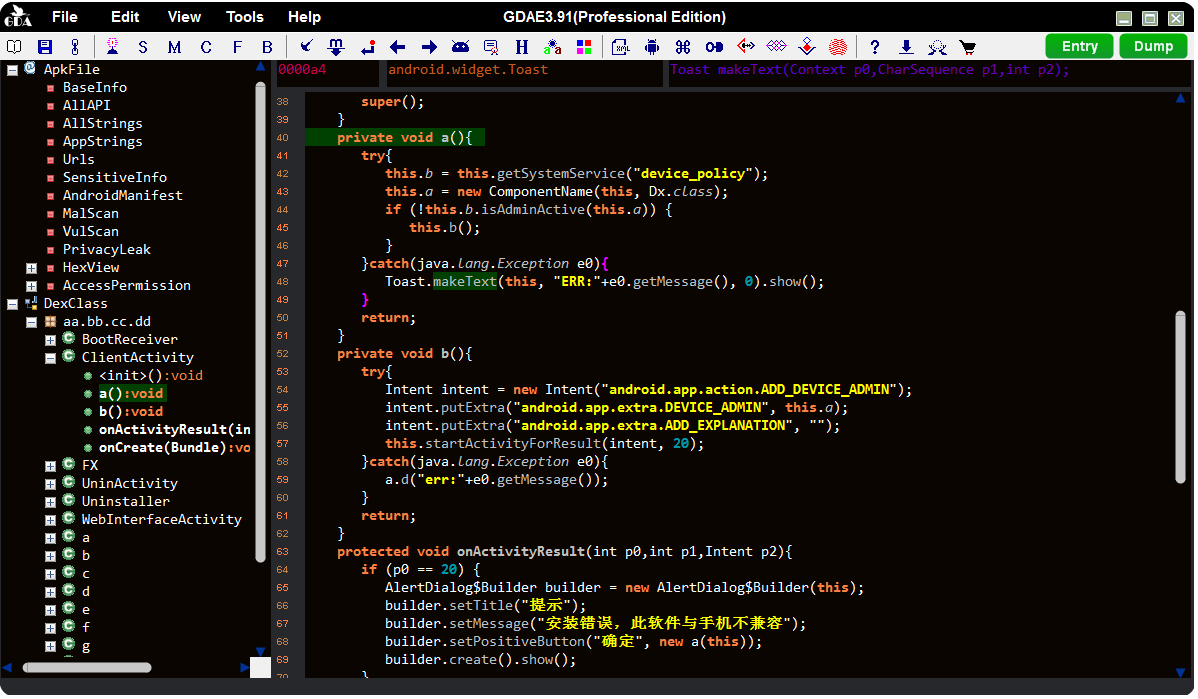 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 alexandreborges/malwoverview
Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia,…
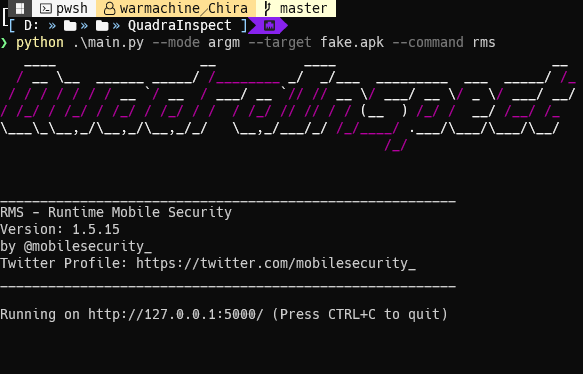 morpheuslord/quadrainspect
Modular Android APK security analysis framework integrating static, dynamic, and reverse engineering tools for comprehensive vulnerability assessment…
 bytedance/appshark
Static taint analysis platform for Android apps that detects vulnerabilities and compliance issues using customizable rule-based scanning and…
 indiandragon/shellshock-vulnerability-scan
Android app to scan for bash Vulnerability - CVE-2014-6271 also known as Shellshock
 idanshechter/cve-2017-13208-scanner
Python script using r2pipe to detect CVE-2017-13208 in Android libnetutils.so by checking for missing dhcp_size validation via static binary analysis.
 metaredteam/rtx-cve-2023-45779
Proof-of-concept code for Android APEX key reuse vulnerability
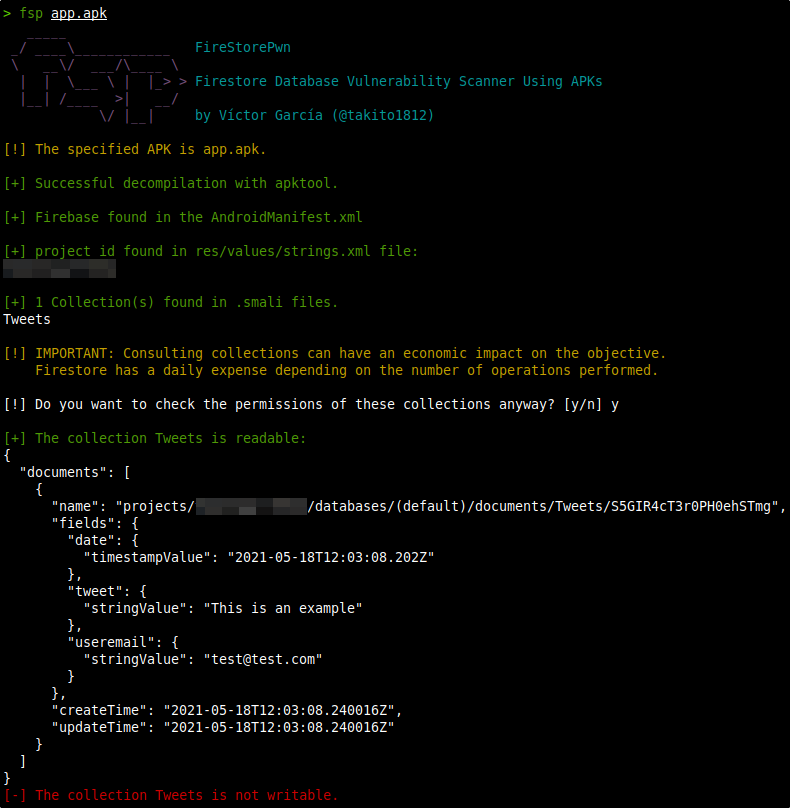 takito1812/firestorepwn
fsp - Firestore Database Vulnerability Scanner Using APKs
 mjancek/bluebornedetection
Simple detection tool for Blueborne vulnerability found on Android devices --- CVE-2017-0781.
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 darkz2012/qualcomm-vulnerability-scanner
A tool to scan Android devices for the recently exploited Qualcomm flaw CVE-2026-21385, providing a simple and efficient way to identify vulnerable…
 alterakey/trueseeing
Non-decompiling iOS/Android app vulnerability scanner (DC25 demo lab, CB17)
 haxatron/cve-2022-0219
Proof-of-concept exploit for CVE-2022-0219, an XXE vulnerability in Jadx that allows local file disclosure when exporting malicious APK files via the…
 hadesscs/artemis
Extracts and investigates infrastructure (IPs, domains) from APK files, with manifest parsing and WHOIS lookup for mobile application reconnaissance.