
truegaze
 nightwatchcybersecurity/truegaze
Static analysis tool for Android/iOS apps focusing on security issues outside the source code
android-securityios-securitymisconfiguration+3
132
nightwatchcybersecurity/truegazeStatic analysis tool for Android/iOS apps focusing on security issues outside the source code
 osuni-99/cve-2019-6447
The above investigation of the ES file browser security weakness allows us to see the issue in its entirety
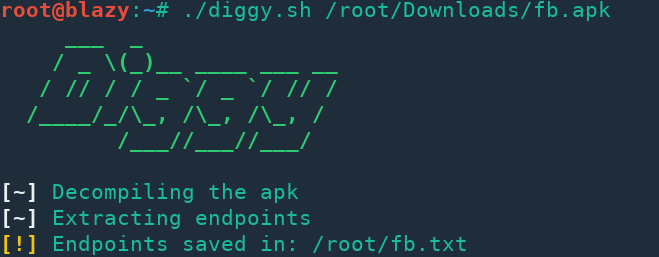 s0md3v/diggy
Extract endpoints from apk files.
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 k4ran909/cve_2024_0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 h3x0v3rl0rd/cve-2019-6447
Python exploit for CVE-2019-6447 enabling arbitrary file read on ES File Explorer 4.1.9.7.4 for Android. Demonstrates mobile vulnerability…
 chethine/esfileexplorer-cve-2019-6447
Exploiting Android Vulnerability in ES File Explorer
 dana-at-cp/backdoor-apk
backdoor-apk is a shell script that simplifies the process of adding a backdoor to any Android APK file. Users of this shell script should have…
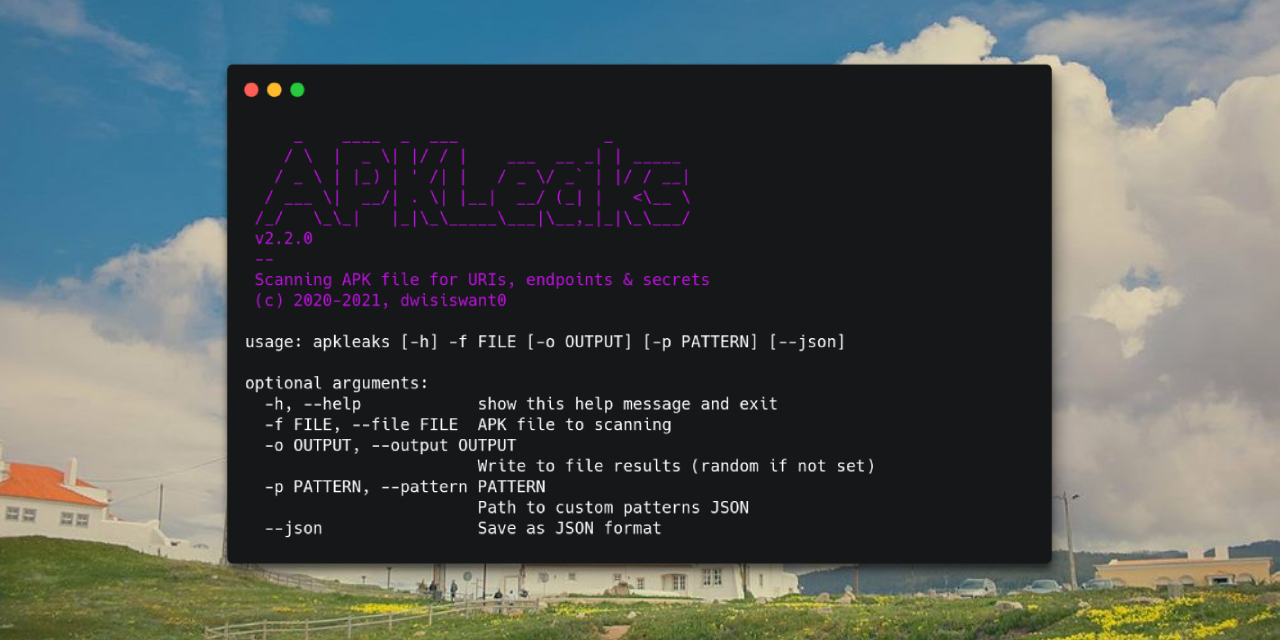 dwisiswant0/apkleaks
Scanning APK file for URIs, endpoints & secrets.
 kalilinux/nethunter/build-scripts/kali-nethunter-installer
Builds flashable installer ZIPs that deploy a mobile penetration-testing environment on Android, including kernel boot patching, rootfs integration,…
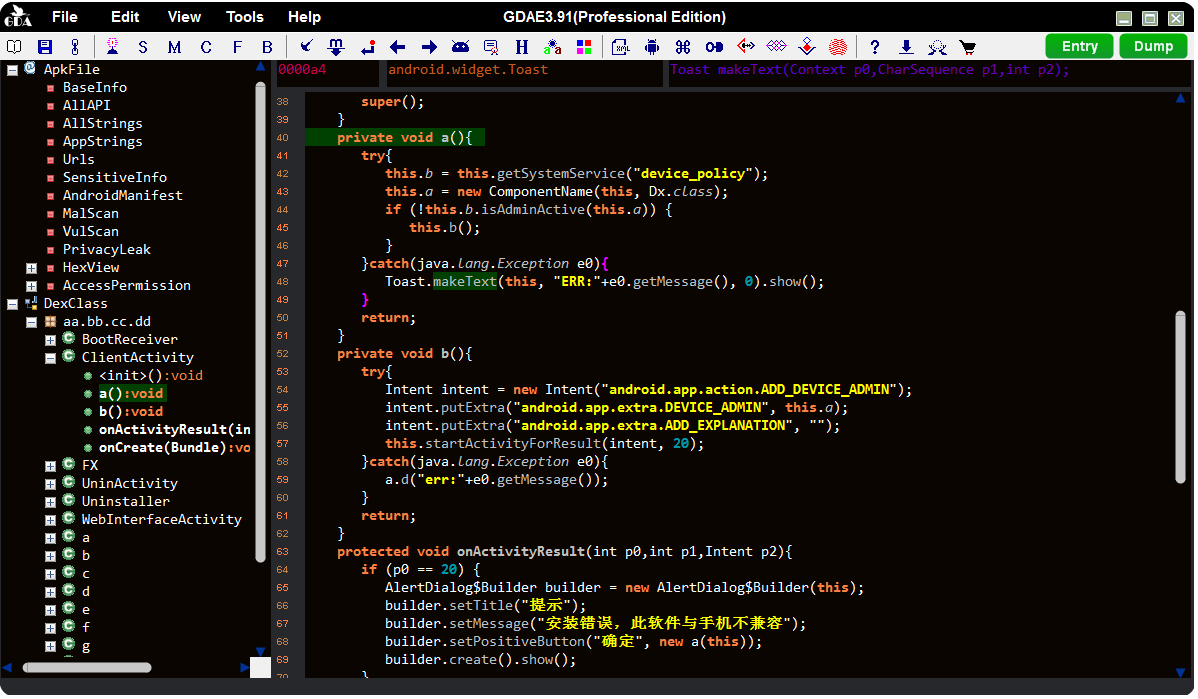 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 eudemonics/scaredycat
Python script to generate a malicious MP4 file and start a CherryPy web server hosting a simple HTML page with the embedded file. Exploits another…
 mwsrc/betterandrorat
Android Remote Access Trojan
 0xdsm/apepe
Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
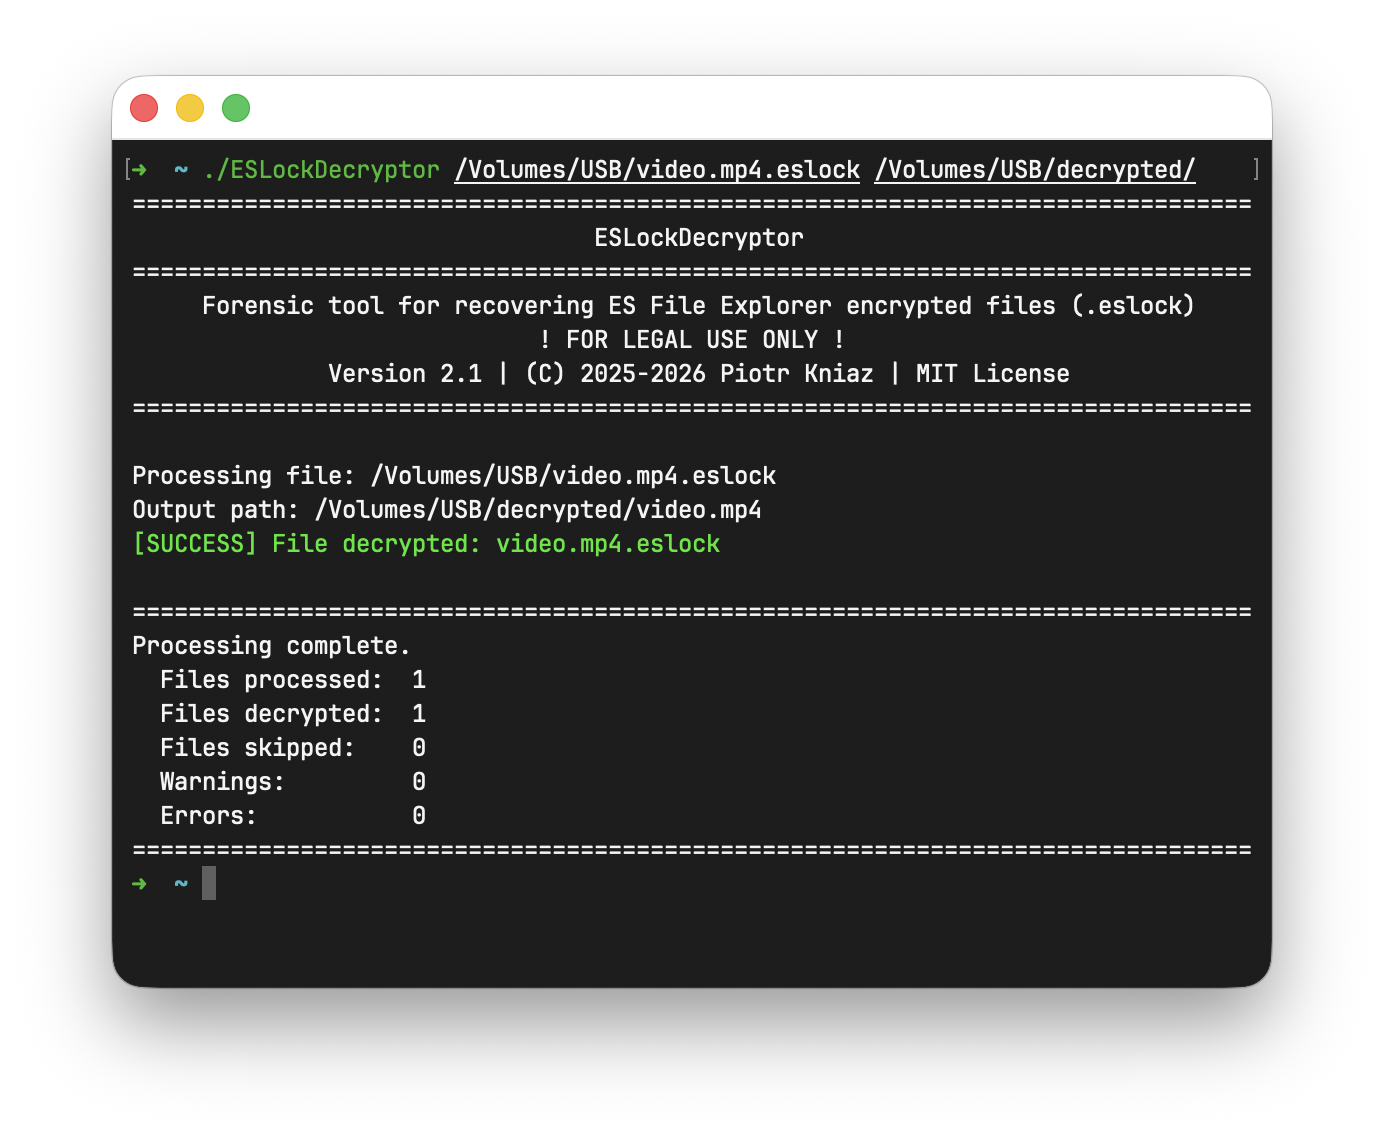 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
 r3n3r0/cve-2026-27280
In-depth analysis and proof-of-concept for CVE-2026-27280, an out-of-bounds write in Adobe DNG SDK's dng_render_task::ProcessArea, reachable via…
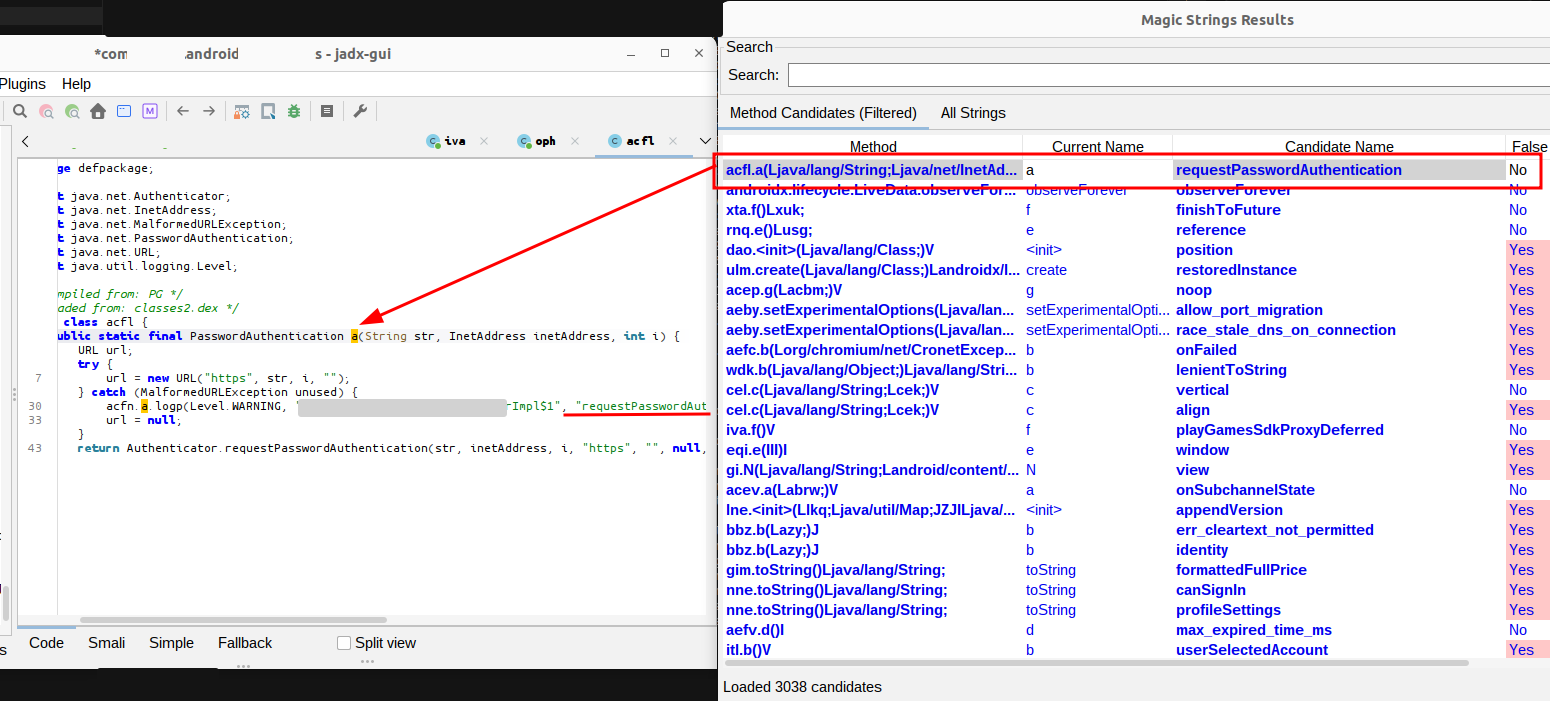 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.