
Magisk
 topjohnwu/magisk
Android customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
android-securitymobile-securityprivilege-escalation
topjohnwu/magiskAndroid customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 sslab-gatech/avpass
Tool for leaking and bypassing Android malware detection system
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 georgiaw/smartphone-pentest-framework
Repository for the Smartphone Pentest Framework (SPF)
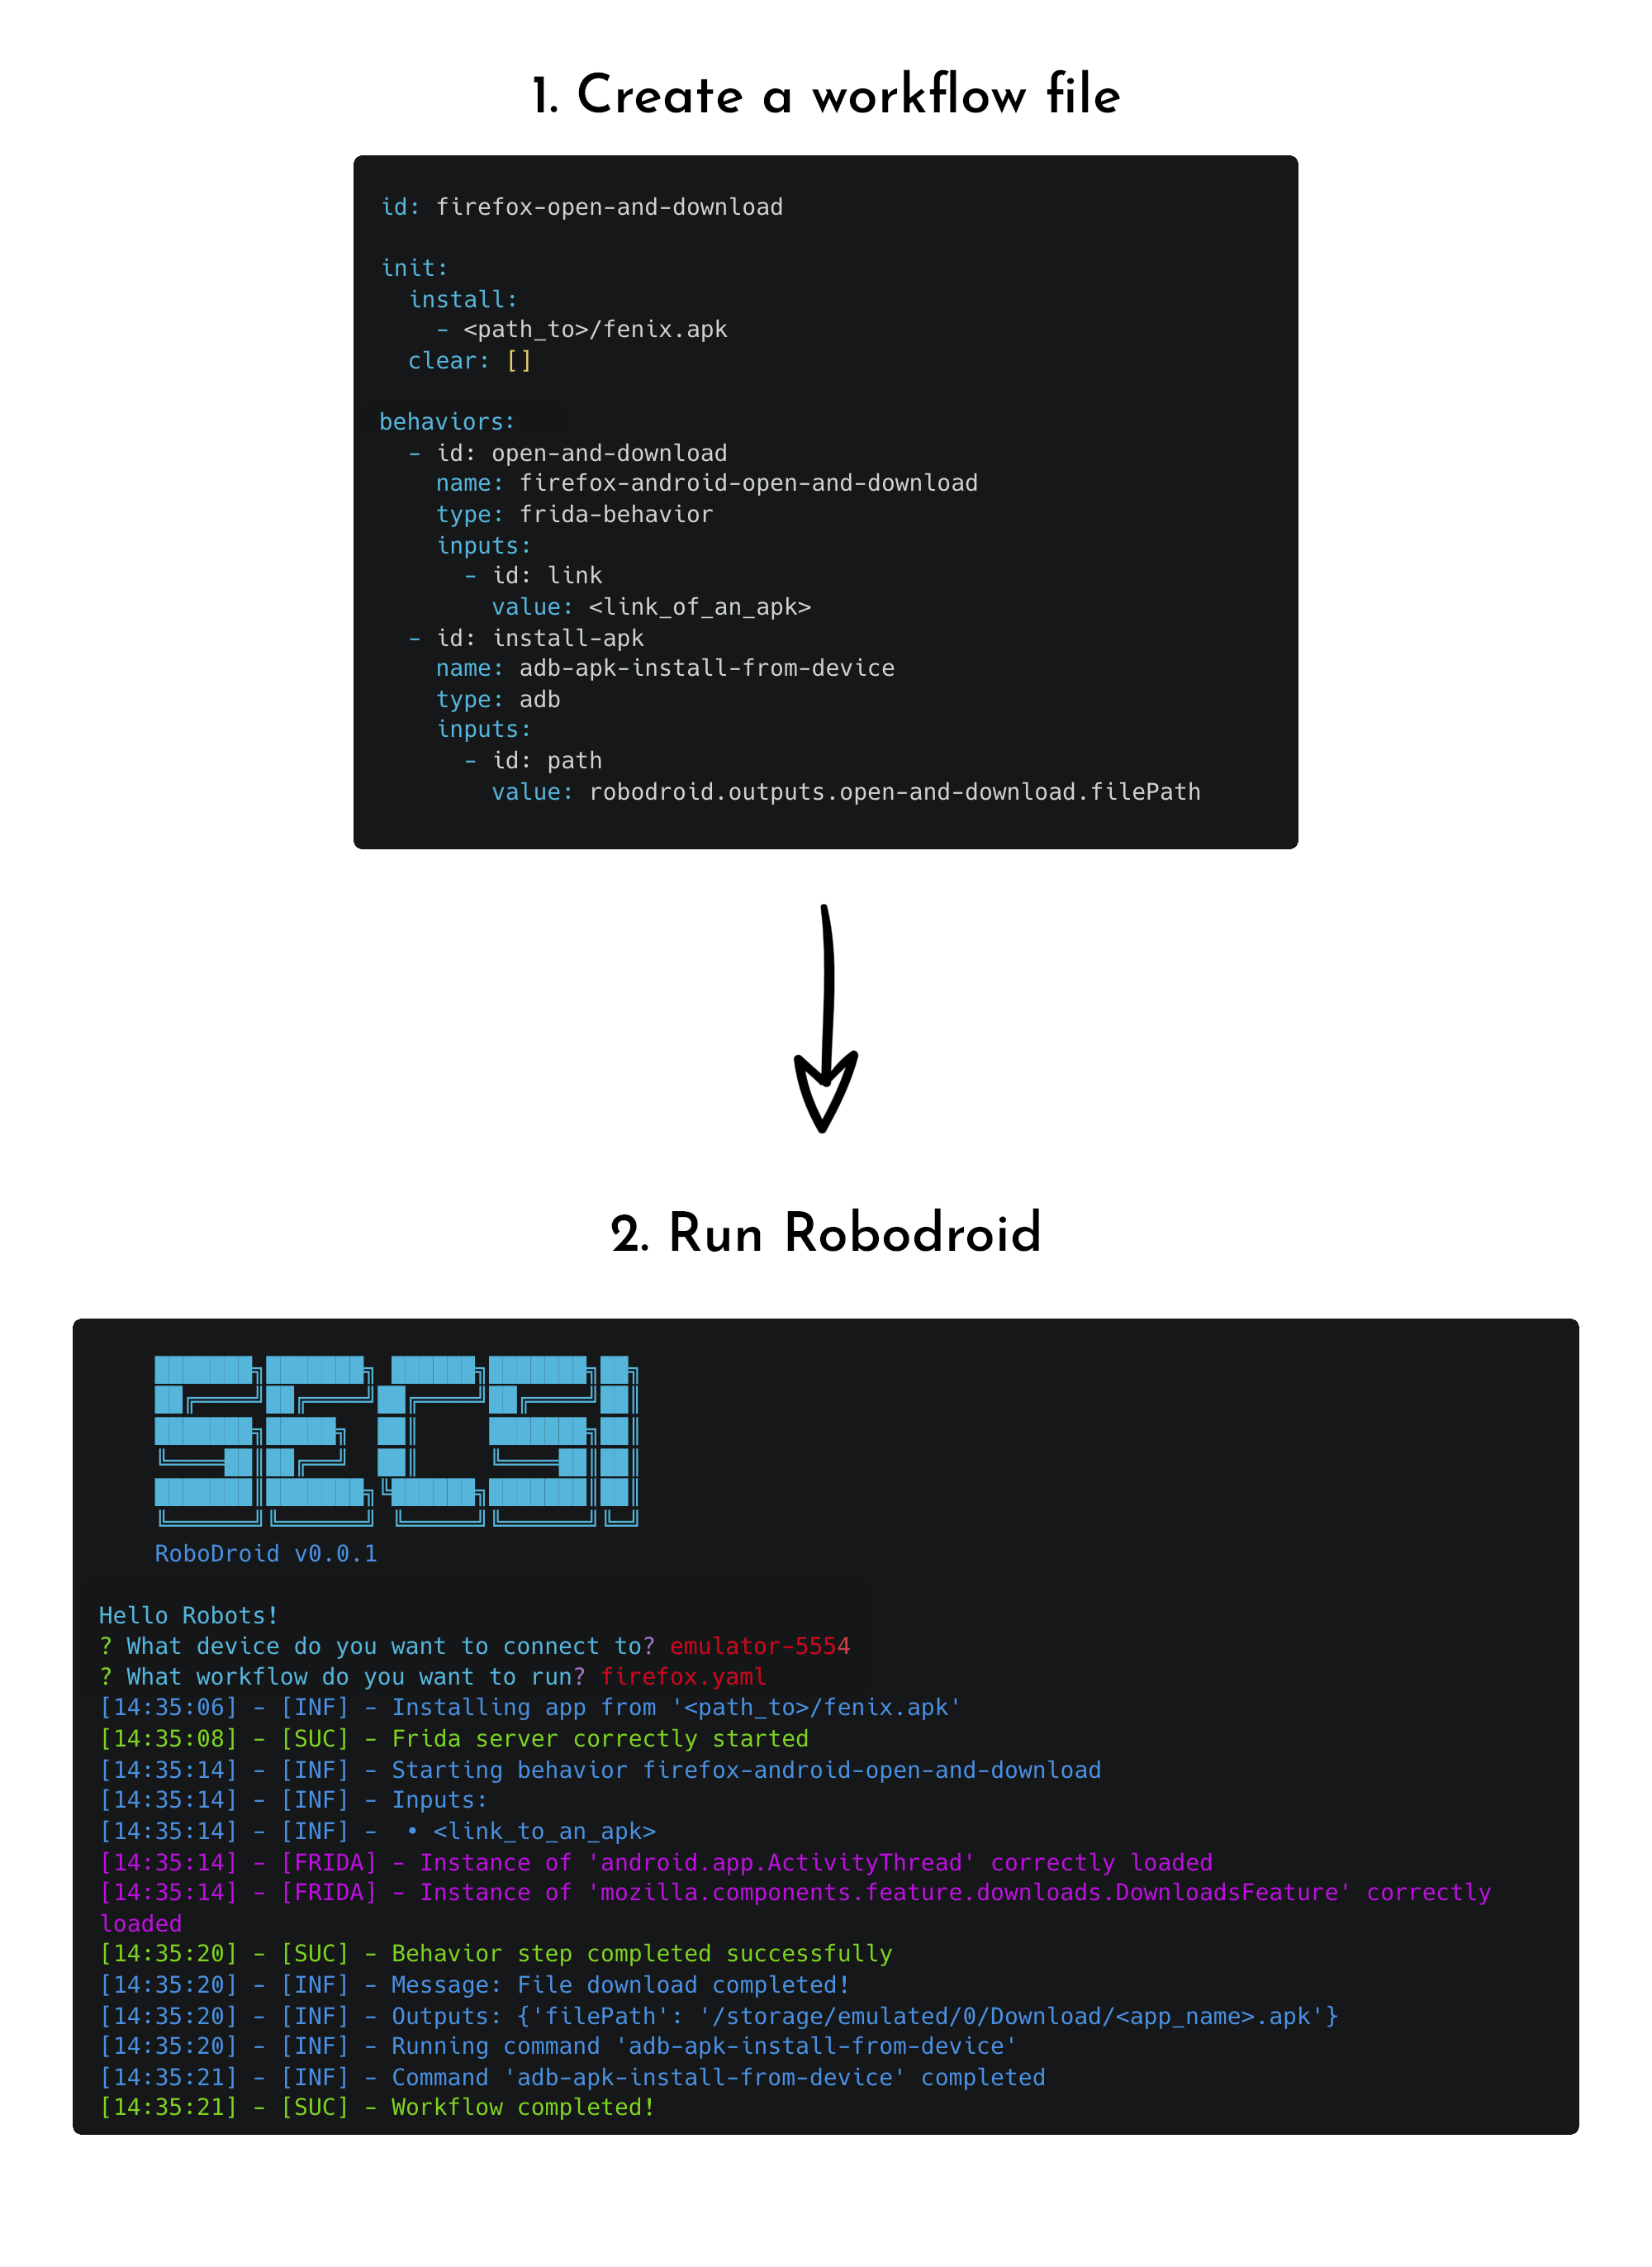 cybersecsi/robodroid
Manage Android machines with pre-defined behaviors for Cyber Range environments.
 idanr1986/cuckoo-droid
CuckooDroid - Automated Android Malware Analysis with Cuckoo Sandbox.
 hadesscs/artemis
Extracts and investigates infrastructure (IPs, domains) from APK files, with manifest parsing and WHOIS lookup for mobile application reconnaissance.
 bhathiya404/exploiting-stagefright-vulnerability-cve-2015-3864
Exploit implementation for Android Stagefright vulnerability CVE-2015-3864, enabling remote code execution and privilege escalation on Android 5.1.1…