

Moxy
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
ai-securityapi-security-testingdynamic-analysis-sandboxing+9
126
matank001/moxyMoxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 in3tinct/see-surf
Security tool to find potential vulnerable Server Side Request Forgery (SSRF) parameters.
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
 pannagkumaar/pentest-lab
Modern cyber range with 50 hands-on challenges across web, API, cloud, AI, and blue-team security tracks. Features guided attack chains, transparent…
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
 named1ess/cve-2026-30741
Proof-of-concept demonstrating remote code execution via request-side prompt injection in OpenClaw Agent Platform, exploiting lack of integrity…
 boreas37/cve-2026-73678-poc
CVE-2026-73678 — MindsDB Minds Platform unauthenticated RCE via scratchpad exec (CVSS 10.0). Verified end-to-end with real LLM
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
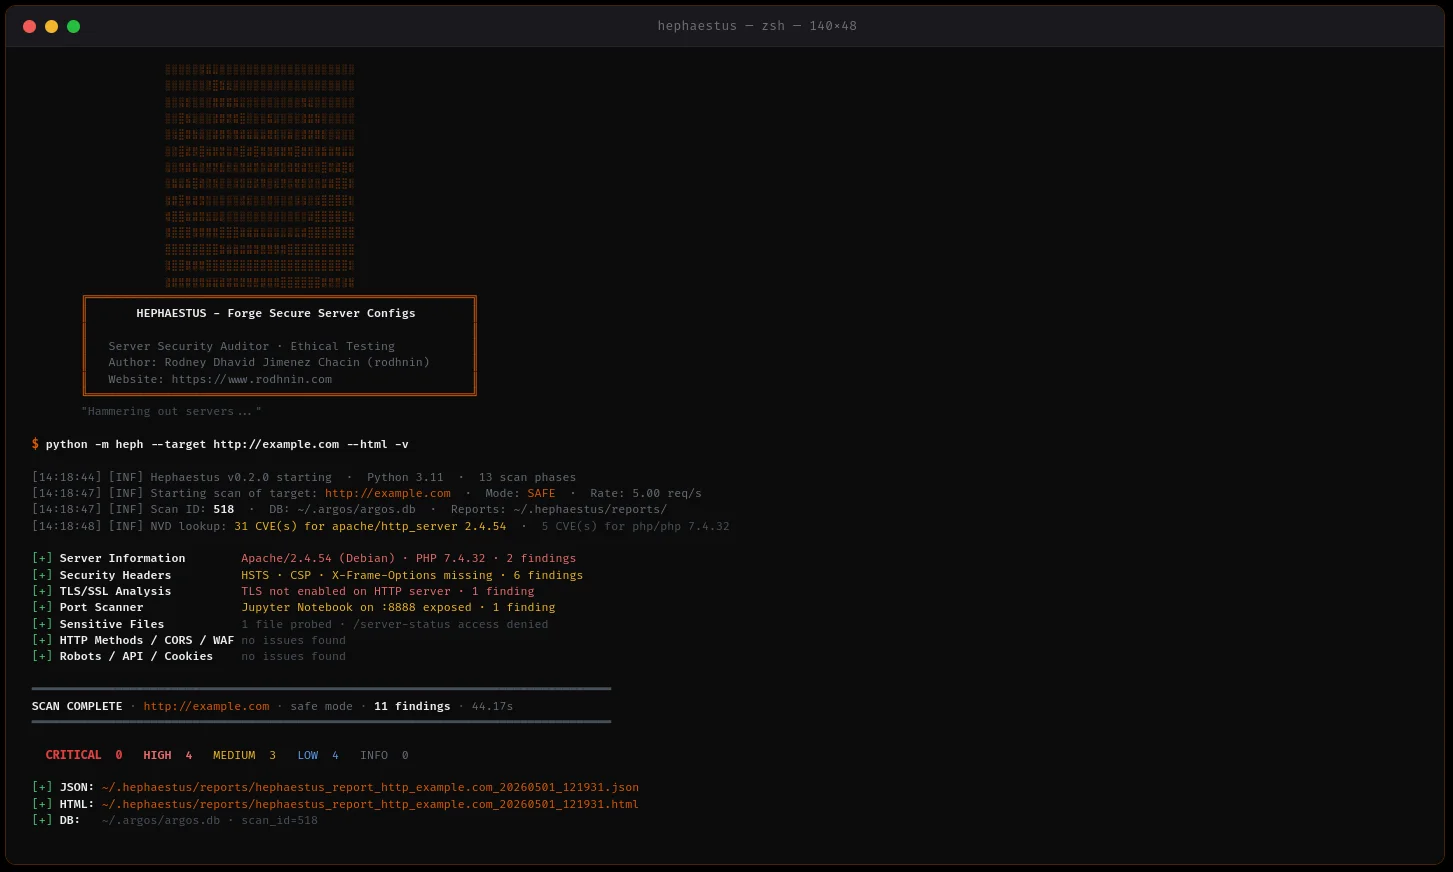 rodhnin/hephaestus-server-forger
server security auditor scanning Apache, Nginx, and IIS configurations with AI-powered hardening guides and professional reporting.
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 ny1024/clawguard
Modular security toolkit for autonomous agents providing static analysis, configuration auditing, runtime monitoring, and supply chain verification…
 sorami-consulting-au/ai-kubernetes-helm-chart-security
Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

 ayinedjimi-consultants/ldaprecon-ai
Active Directory LDAP Security Auditor with AI-Powered Analysis - By Ayi NEDJIMI https://ayinedjimi-consultants.fr
 cyberdudebivash/cyberdudebivash-servicenow-ai-agent-audit-script
This script audits ServiceNow AI Agents for vulnerabilities like CVE-2025-12420, governance gaps, and compliance risks. Powered by CYBERDUDEBIVASH –…