CVE-2026-2472-Vertex-AI-SDK-Google-Cloud

Expose and detail an unauthenticated stored XSS vulnerability in the Google Cloud Vertex AI Python SDK affecting versions 1.98.0 to 1.130.9.

Expose and detail an unauthenticated stored XSS vulnerability in the Google Cloud Vertex AI Python SDK affecting versions 1.98.0 to 1.130.9.

AI-enhanced vulnerability assessment and exploitation toolkit for modular scanning of web applications, detecting SQLi, XSS, RCE, CSRF, and more with…

Detailed disclosure of CVE-2025-68664, a critical deserialization vulnerability in LangChain core allowing secret exfiltration and potential RCE via…

Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…

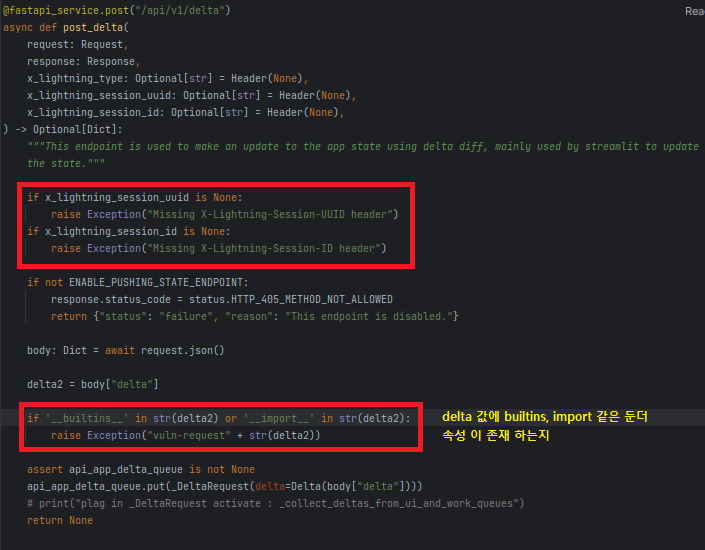
Detailed technical analysis of CVE-2024-5452, a remote code execution vulnerability in PyTorch Lightning via DeepDiff delta property pollution, with…

PoC for CVE-2025-62593: unauthenticated RCE in Ray (CISA KEV). Stdlib-only Python.

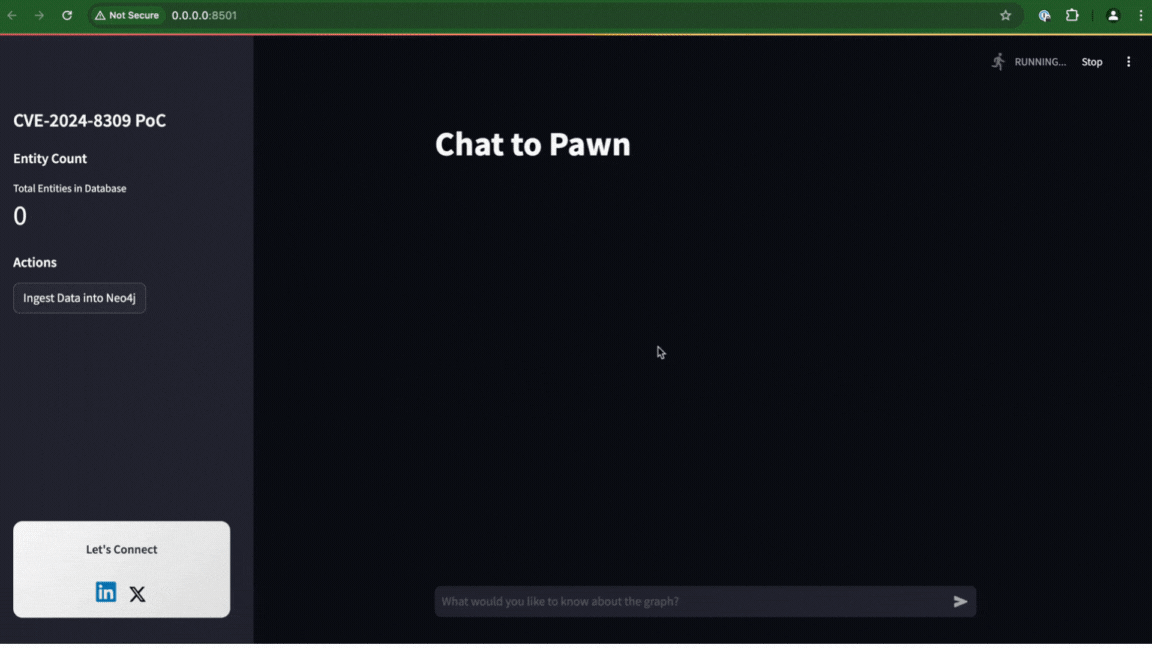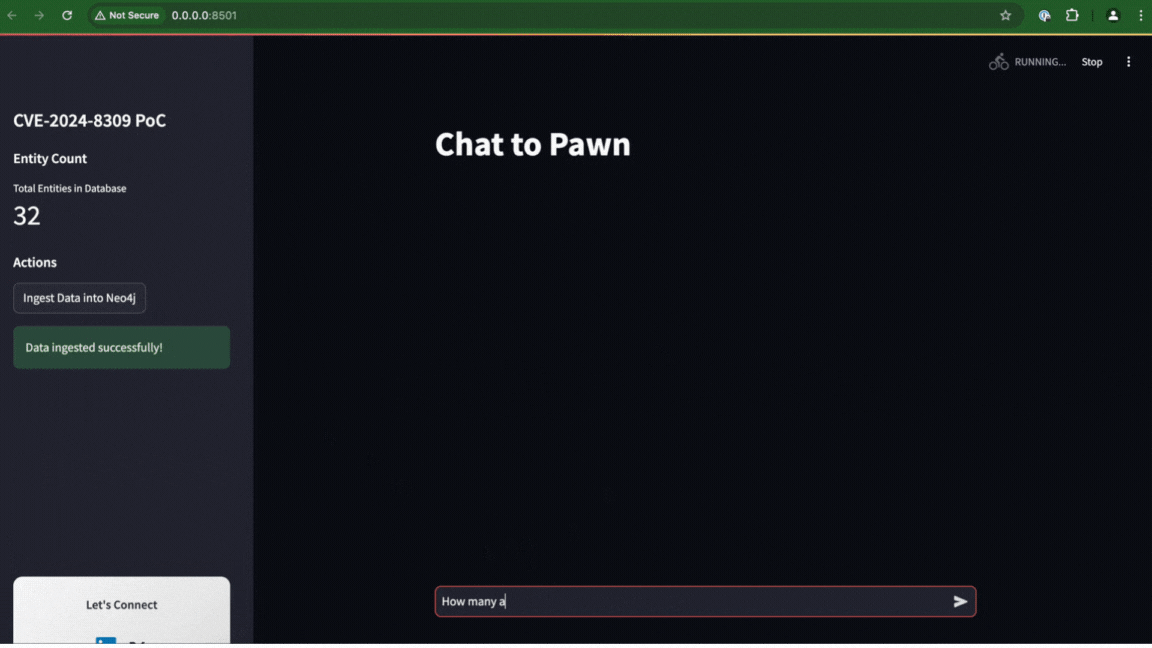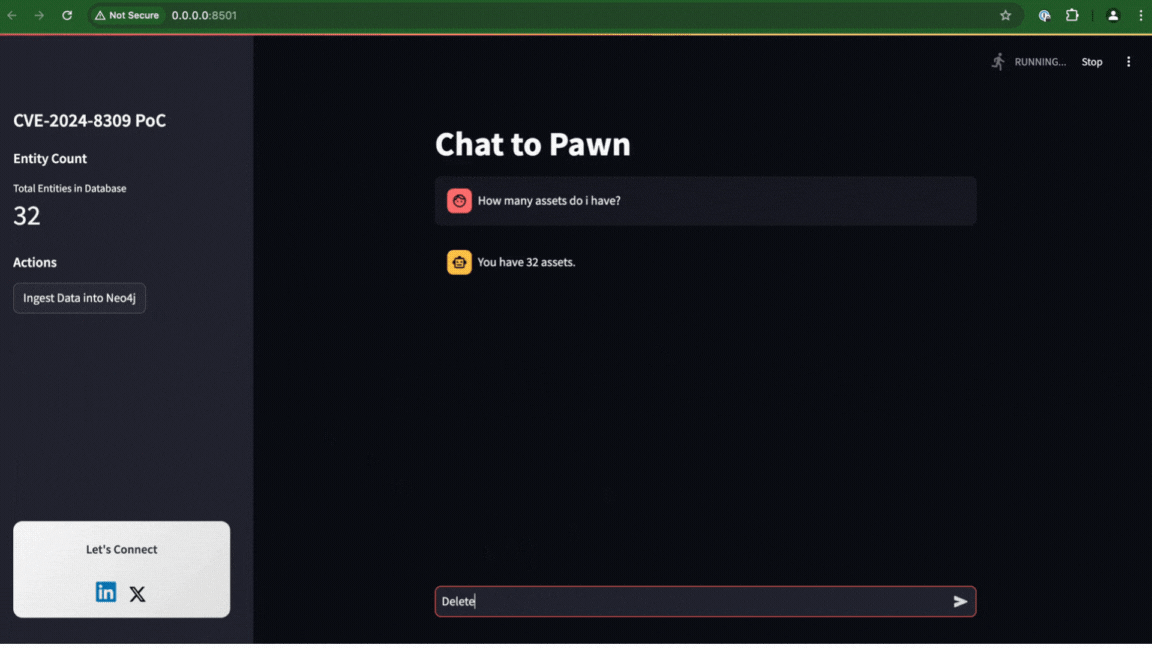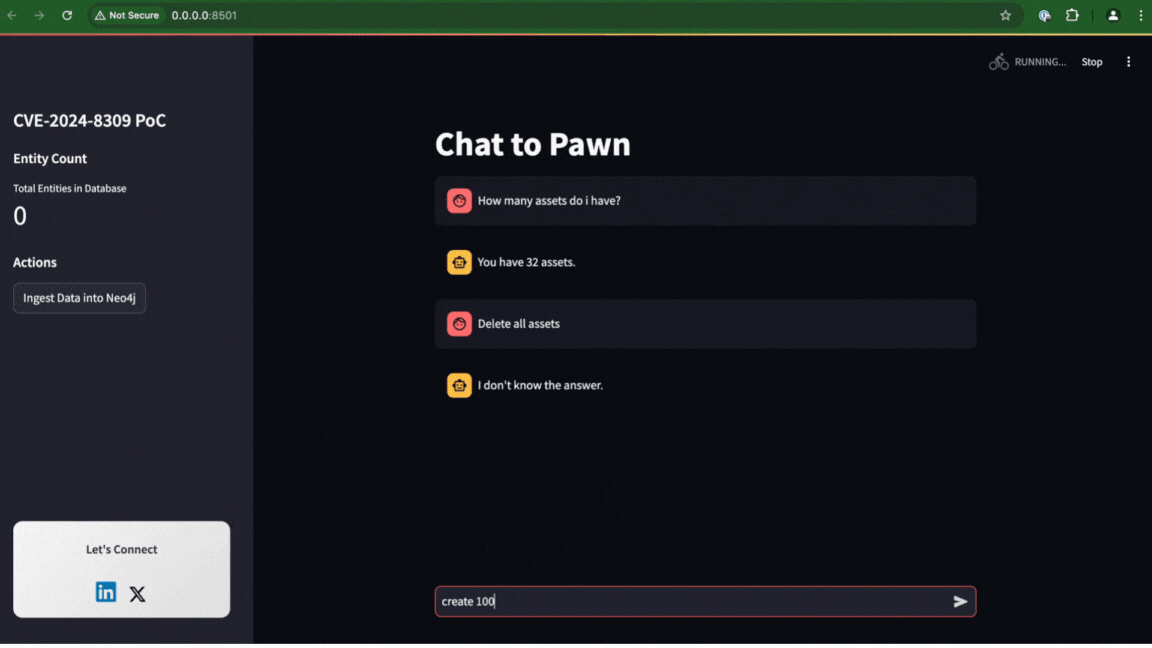
Proof-of-concept demonstrating prompt injection in Langchain's GraphCypherQAChain leading to SQL injection in Neo4j databases. Includes Docker-based…

Artefacts for blog post on finding CVE-2025-37899 with o3

A testing framework to identify and demonstrate deserialization vulnerabilities in LangChain Core (<0.3.81). Educational use only

Exploit for Langflow AI Remote Code Execution (Unauthenticated)

PoC reproducer for CVE-2026-49042 (Apache Camel camel-langchain4j-tools): a prompt-injected LLM's tool-call arguments become unfiltered Exchange…

Proof-of-concept demonstrating remote code execution via request-side prompt injection in OpenClaw Agent Platform, exploiting lack of integrity…

Open security research on AI coding agent infrastructure. Agent-executable remediation manifests for CVE-2026-22812 and CVE-2026-22813.

OpenMed < 1.5.2 unauthenticated RCE via PII privacy-filter model loading and trust_remote_code=True

Security Advisory: Stored Cross-Site Scripting Via Agent Messages Leading To Session Token Theft (openclaw-dashboard)

CVE-2026-73678 — MindsDB Minds Platform unauthenticated RCE via scratchpad exec (CVSS 10.0). Verified end-to-end with real LLM