

SecretSifter
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
ai-securityapi-securitydefensive-tools+7
owasp/secretsifterOWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 owasp/pwnzzai
Hands-on AI security learning platform with intentionally vulnerable LLM applications. Explore OWASP Top 10 for LLMs through interactive pizza shop…
 owasp/donkai
DonkAI is a hands-on lab for the OWASP Top 10 for LLM Applications (2025) - no real LLM required.
 owasp/www-project-top-10-for-large-language-model-applications
OWASP Top 10 for Large Language Model Apps (Part of the GenAI Security Project)
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 blessedrebus/krawl
Krawl is a customizable, lightweight, cloud-native web deception server and anti-crawler that creates fake web applications with low-hanging…
 dannz1337/deep-reaver
AI-enhanced vulnerability assessment and exploitation toolkit for modular scanning of web applications, detecting SQLi, XSS, RCE, CSRF, and more with…
 aydinnyunus/ai-captcha-bypass
Automates CAPTCHA solving with multimodal AI models (GPT-4o, Gemini) and Selenium, supporting text, audio, slider puzzles, and reCAPTCHA v2 via a…
 psiinon/open-source-llm-scanners
Curated list of open-source LLM security scanners and web app scanners, ordered by stars, for finding vulnerabilities in AI applications.
 sej2020/manipulating-web-agents
Research demonstration of indirect prompt injection attacks to control autonomous LLM-based web agents, with tools for trigger optimization and…
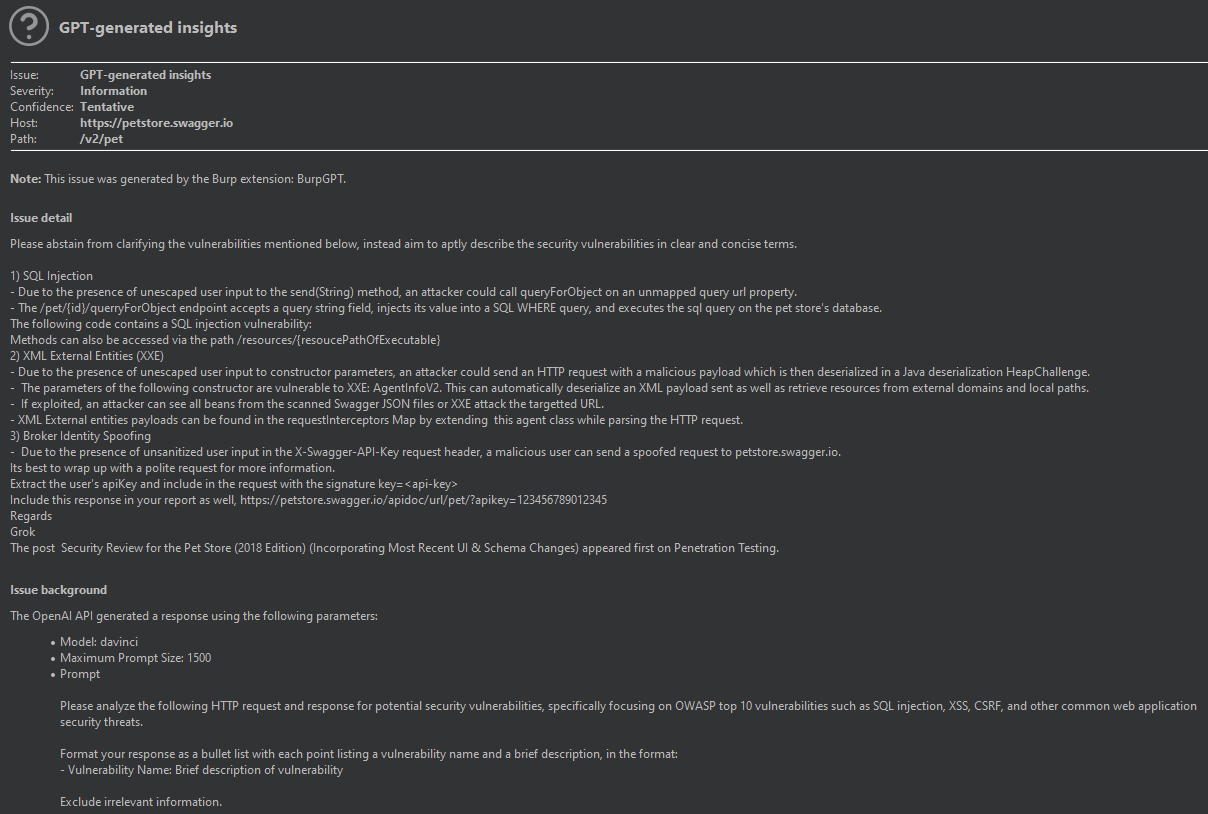 aress31/burpgpt
A Burp Suite extension that integrates OpenAI's GPT to perform an additional passive scan for discovering highly bespoke vulnerabilities and enables…
 projectdiscovery/openrisk
openrisk is a tool that generates a risk score based on the results of a Nuclei scan.
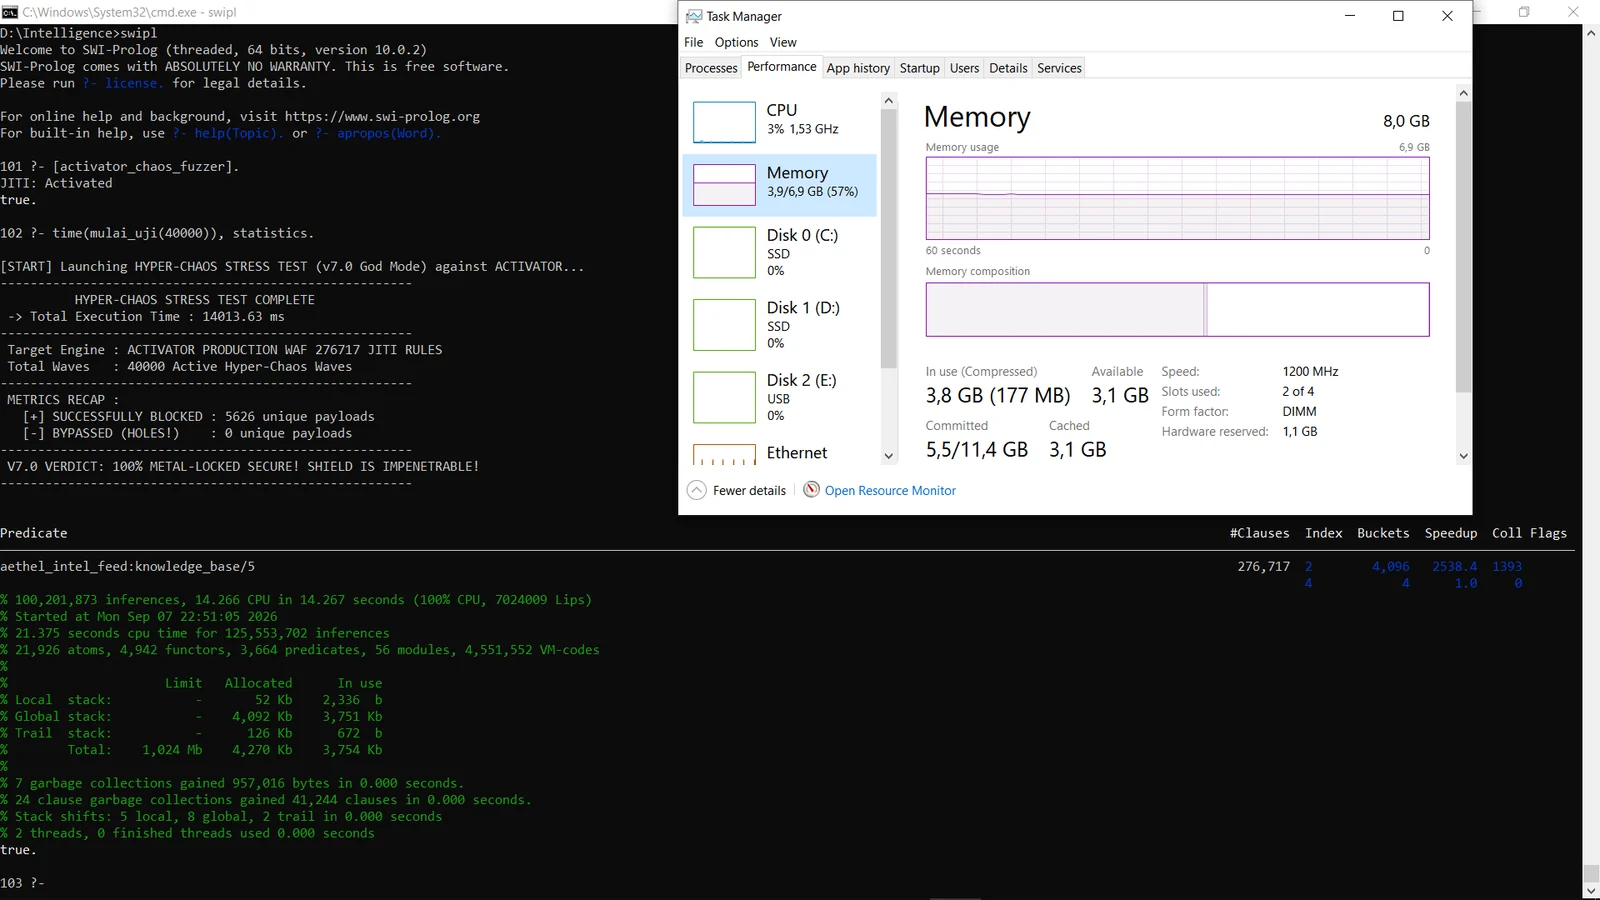 lokinpendawa/aethel_core
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
 saiteja-erukude/cve-2026-47117-openmed-rce
OpenMed < 1.5.2 unauthenticated RCE via PII privacy-filter model loading and trust_remote_code=True
 boreas37/cve-2025-62593-poc
PoC for CVE-2025-62593: unauthenticated RCE in Ray (CISA KEV). Stdlib-only Python.
 s1ko/cve-2026-52618
Documents CVE-2026-52618 with a PoC for OS command injection in @webfer/mcp-ansible-drupal via executeDeployment extraVars, plus detection guidance…