

tanuki
 mafifrizi/tanuki
Tactical Identity Operator for Linux & Hybrid Active Directory
ai-securityauthenticationdefensive-tools+6
mafifrizi/tanukiTactical Identity Operator for Linux & Hybrid Active Directory
 deso-pk/make-trust-irrelevant
Kernel-enforced authority and runtime security for Linux systems, autonomous software, and AI agents.
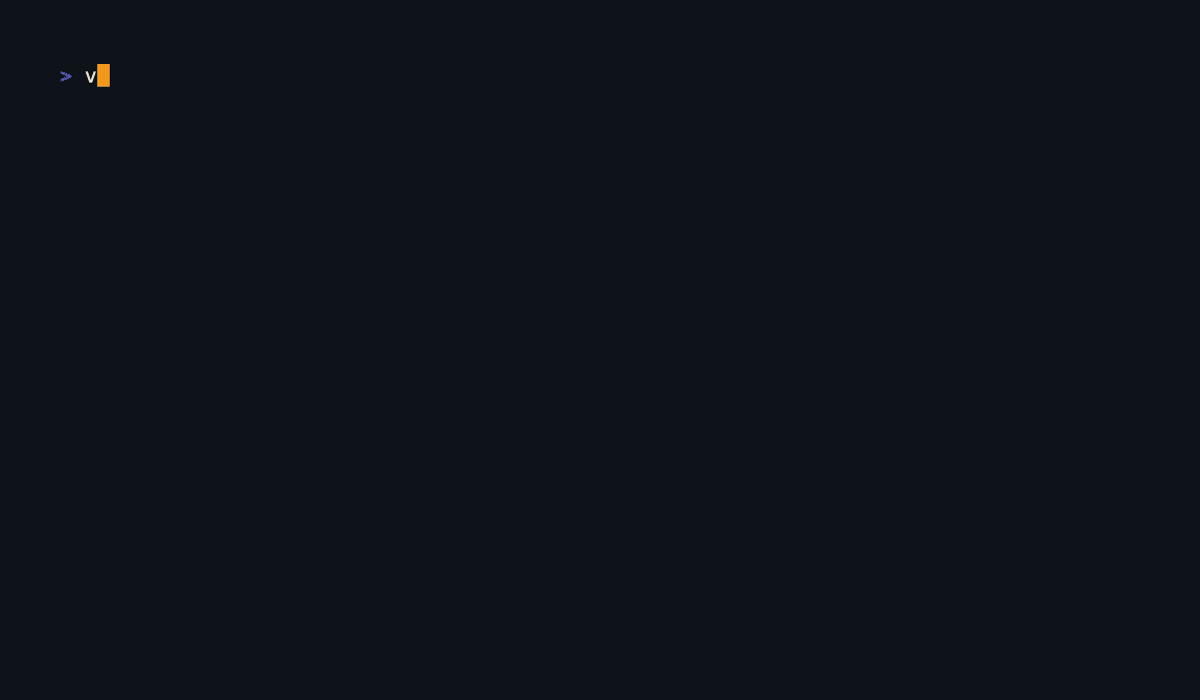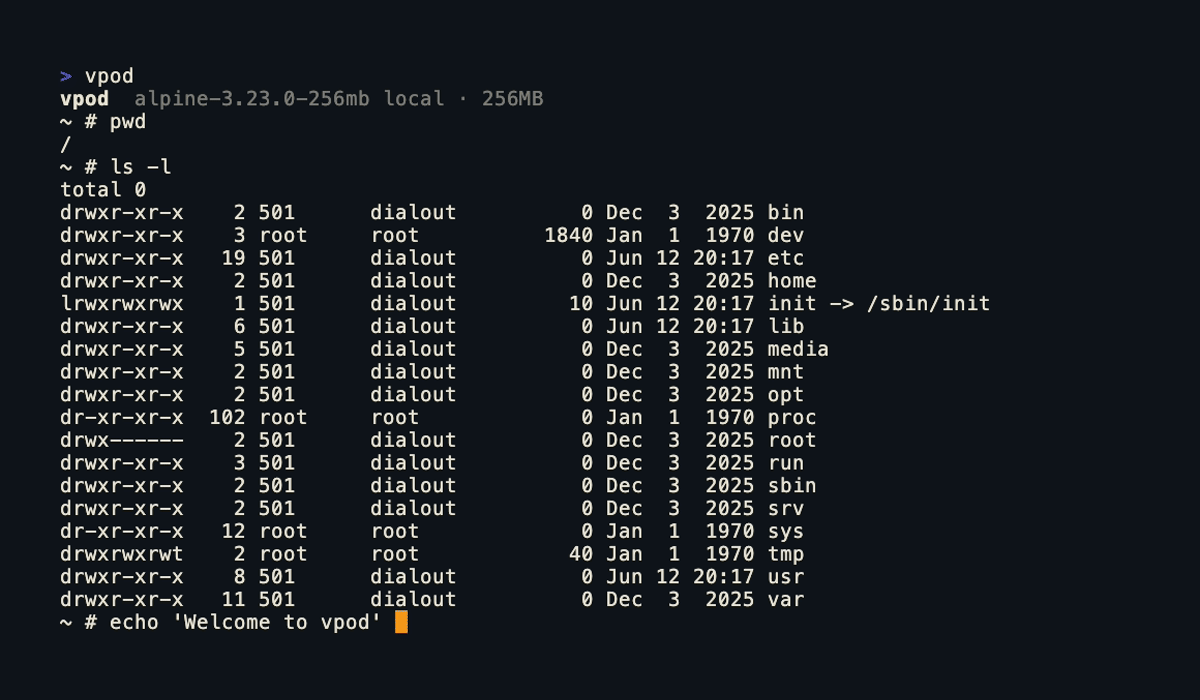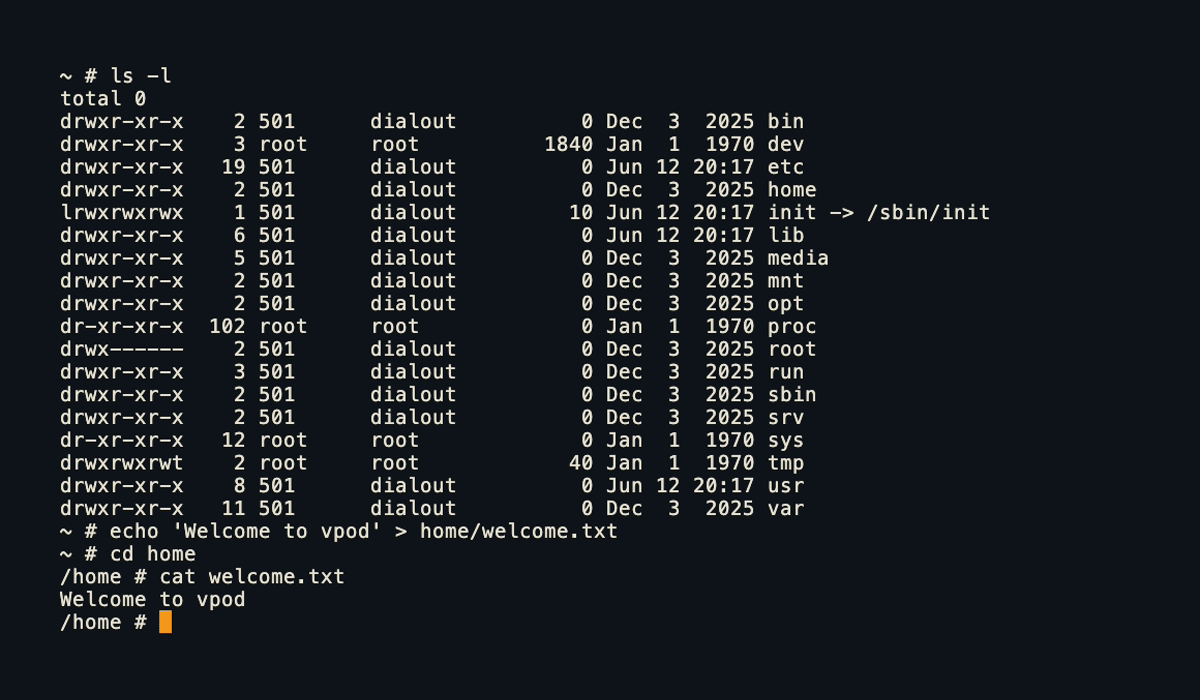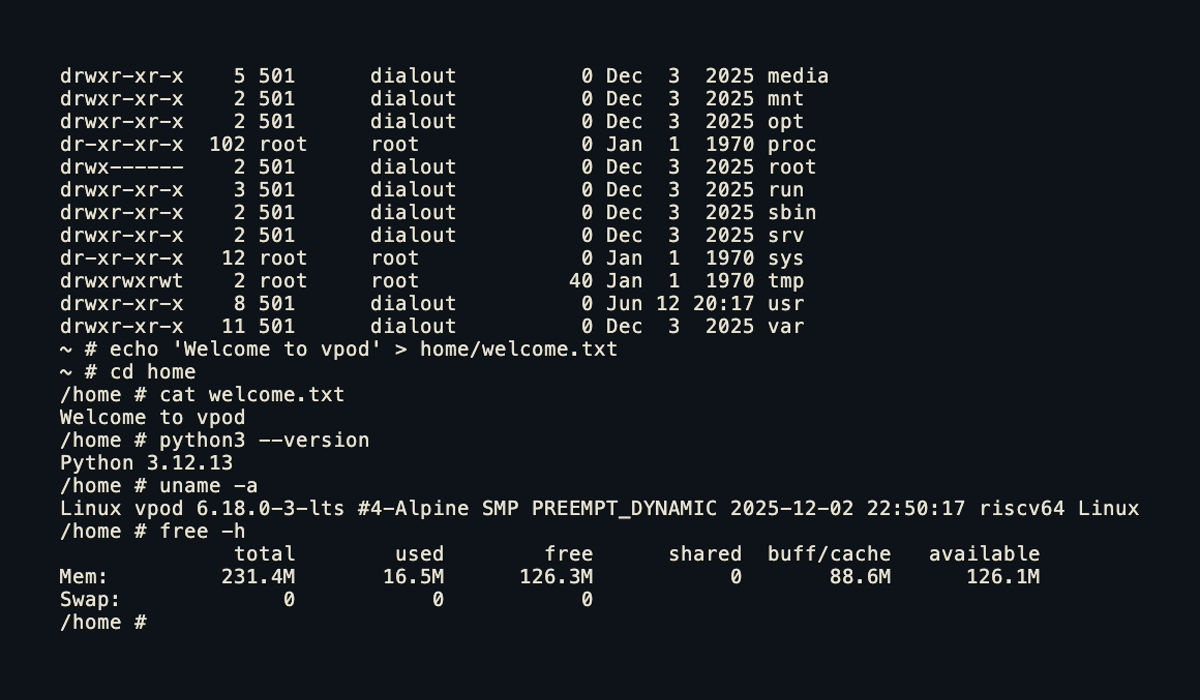 capsulerun/vpod
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 eiln/ane
Reverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…
 lglznl/klaios
KLAIOS is a hybrid security environment that merges Kali Linux’s offensive toolkit with hardened, VPN-bunker-style isolation—enhanced by modern AI…
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 ccss17/o3_finds_cve-2025-37899
Artefacts for blog post on finding CVE-2025-37899 with o3
 rodhnin/asterion-network-minotaur
Network and domain security auditor scanning Windows Active Directory, Linux systems, and network infrastructure with AI-powered hardening guides…
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
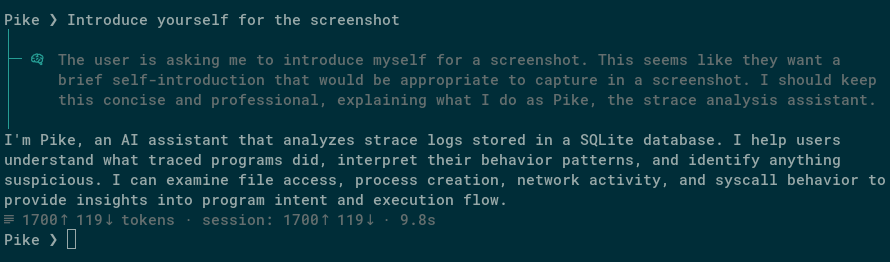 synacktiv/pike-agent
Experimental Linux strace LLM agent
 foxirain/linux-kernel-codex-harness-v2
Provenance-aware Linux kernel vulnerability research harness used in the investigation of CVE-2026-53075
 foxirain/linux-kernel-codex-harness
Evidence-driven Linux kernel vulnerability research harness used in the investigation of CVE-2026-31720
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
 linuztx/alter-zero
RAM efficient terminal agent harness for coding, cybersecurity, and automation.
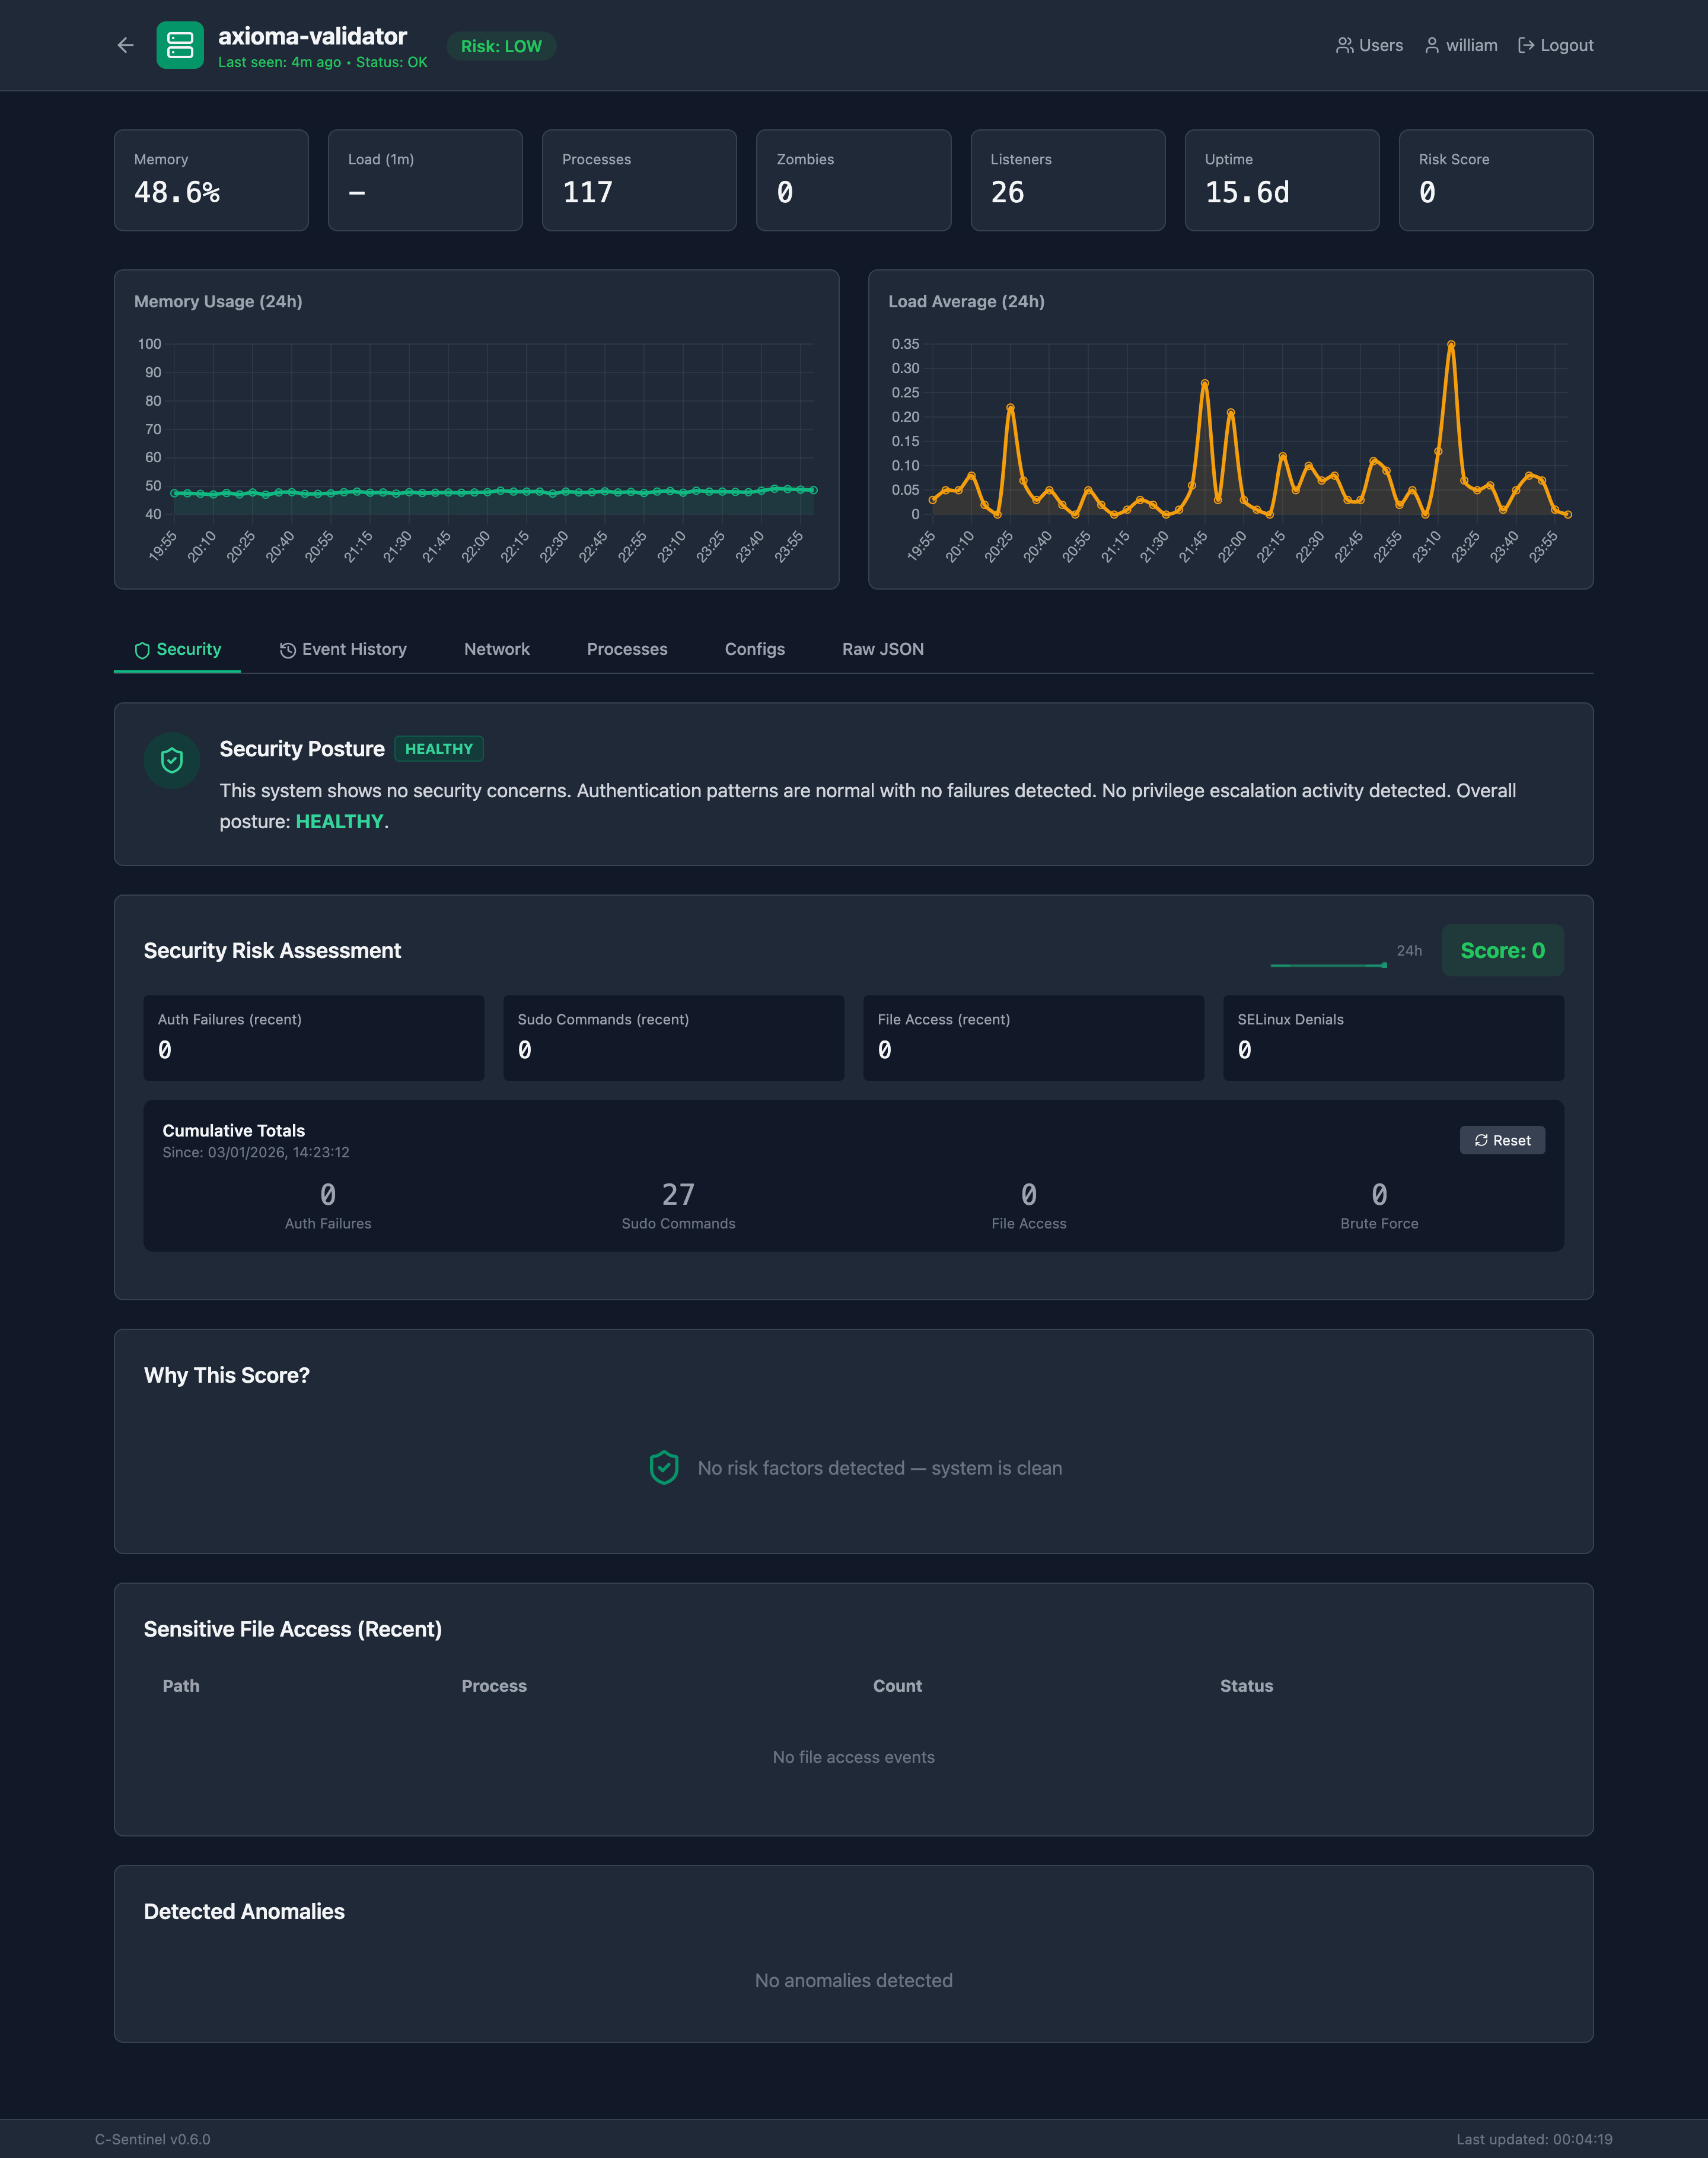 speytech/c-sentinel
Semantic Observability for UNIX Systems - A lightweight C-based system prober with AI-powered analysis