LLM-Jailbreak-via-Chain-of-Logic-Injection-CVE-2026-3098

Multi-stage prompt injection technique that bypasses LLM safety alignment via identity reassignment, refusal suppression, and output coercion,…

Multi-stage prompt injection technique that bypasses LLM safety alignment via identity reassignment, refusal suppression, and output coercion,…

Proof-of-concept demonstrating remote code execution via request-side prompt injection in OpenClaw Agent Platform, exploiting lack of integrity…

CVE-2026-73678 — MindsDB Minds Platform unauthenticated RCE via scratchpad exec (CVSS 10.0). Verified end-to-end with real LLM

Check if your AI agent setup is vulnerable to CVE-2026-33579

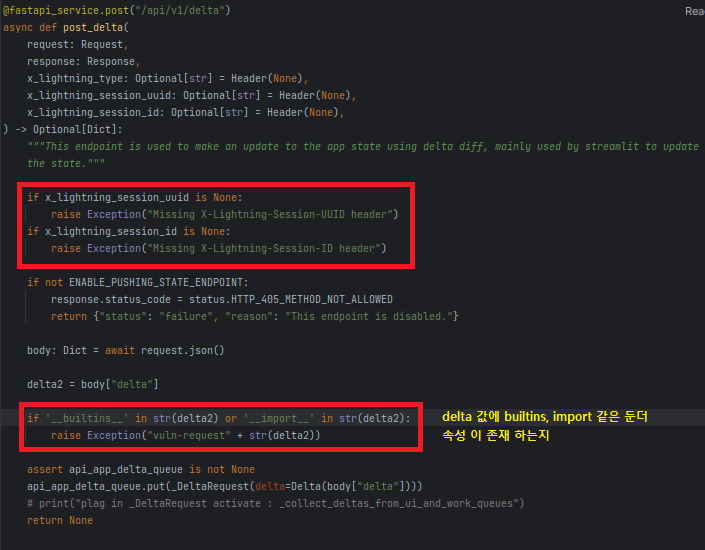
Detailed technical analysis of CVE-2024-5452, a remote code execution vulnerability in PyTorch Lightning via DeepDiff delta property pollution, with…

vllm-project vllm version 0.5.2.2 is vulnerable to Denial of Service attacks.

Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…

Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…

Public advisory landing page for CVE-2026-54519: missing ownership checks in ai-agent-automation memory APIs enabling cross-user memory read and…

AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…

A curated list of AI Security materials and resources for Pentesters, Bug Hunters, and Security Researchers.

Modular security toolkit for autonomous agents providing static analysis, configuration auditing, runtime monitoring, and supply chain verification…

Security patches for unpatched llama.cpp vulnerabilities (CVE-2026-43626 through CVE-2026-43632) — Cyera Research

Working implementation: cryptographically verified short-lived identities for AI decision authentication — CVE-2025-59536 (Patent Pending US…

Free security-baseline rule for Claude Code, Codex, and Cursor: treats MCP tool descriptions as untrusted input (OWASP MCP Top 10 MCP03,…

AngularJS 1.x -> Angular 18 migration guidance for GitHub Copilot. Source-of-truth repo for…

Open security research on AI coding agent infrastructure. Agent-executable remediation manifests for CVE-2026-22812 and CVE-2026-22813.

An automated, high-precision zero-shot evaluation pipeline for OpenAI's CLIP model on CIFAR-10. Features 88.80% accuracy, Safetensors security…