

vuln-bank
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
ai-securityapi-securitycode-analysis+5
961
commando-x/vuln-bankIntentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 pericena/ciclopeclic
Security awareness training tool for authorized phishing simulations and internal IT audits
 oscar-collado/comfyui-cve-2026-68771-poc
Security research lab — Unauthenticated RCE via insecure deserialization in ComfyUI v0.23.0 (CVSS 9.8). Isolated Docker environment, technical…
 megafart1/cve-2026-2472-vertex-ai-sdk-google-cloud
Expose and detail an unauthenticated stored XSS vulnerability in the Google Cloud Vertex AI Python SDK affecting versions 1.98.0 to 1.130.9.
 saiteja-erukude/cve-2026-47117-openmed-rce
OpenMed < 1.5.2 unauthenticated RCE via PII privacy-filter model loading and trust_remote_code=True
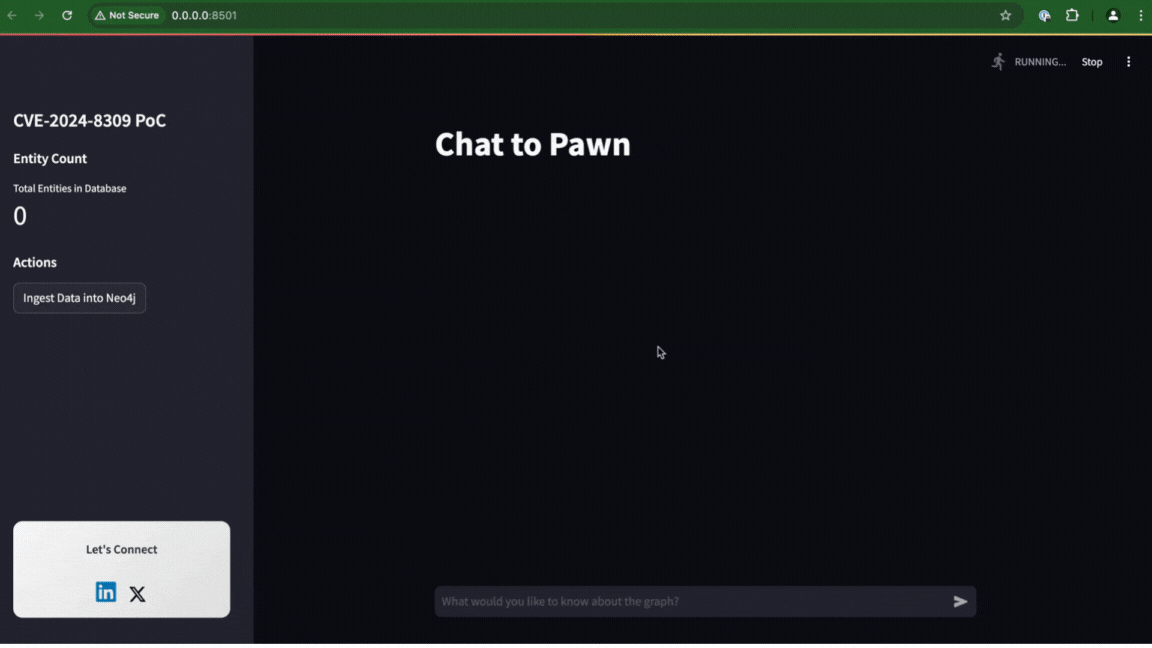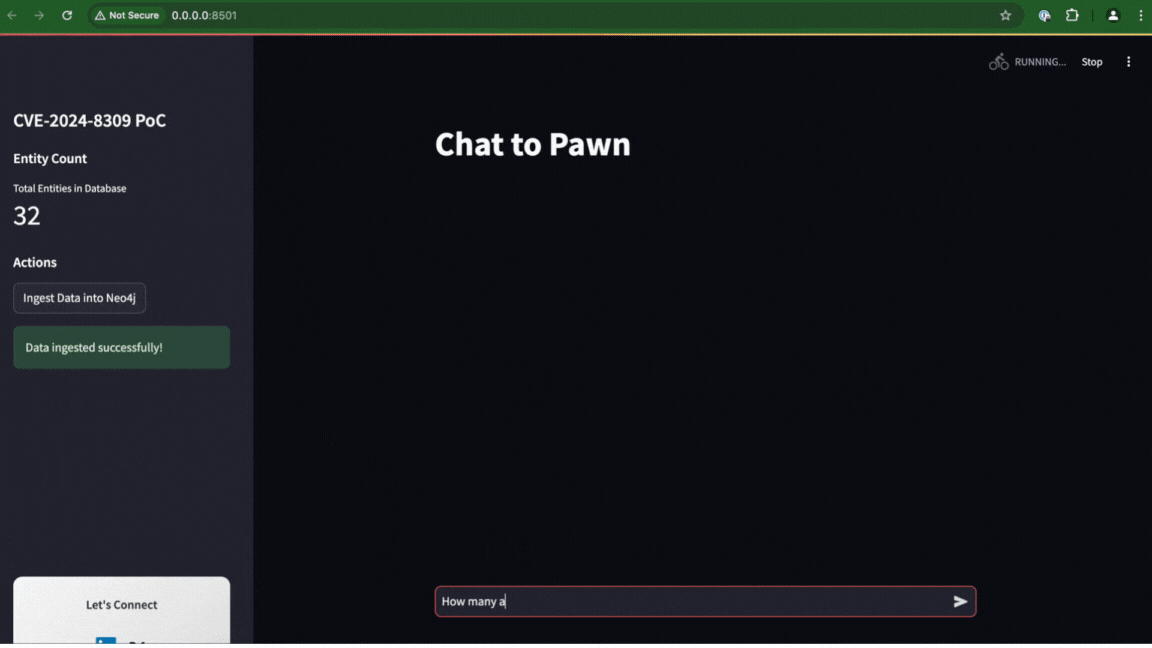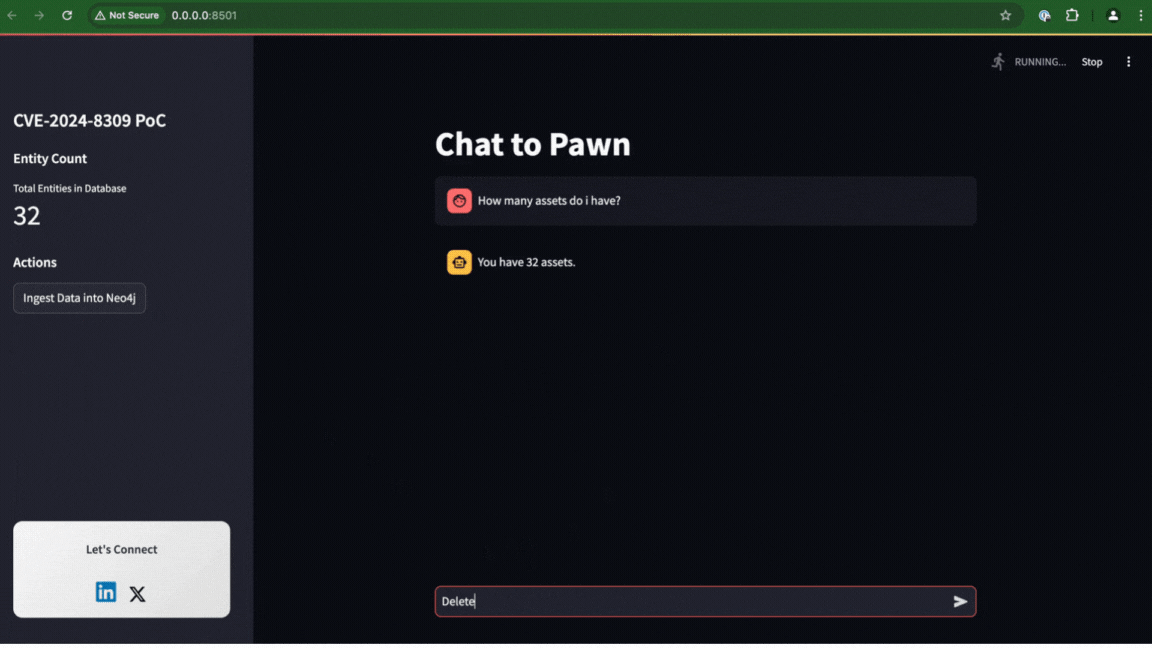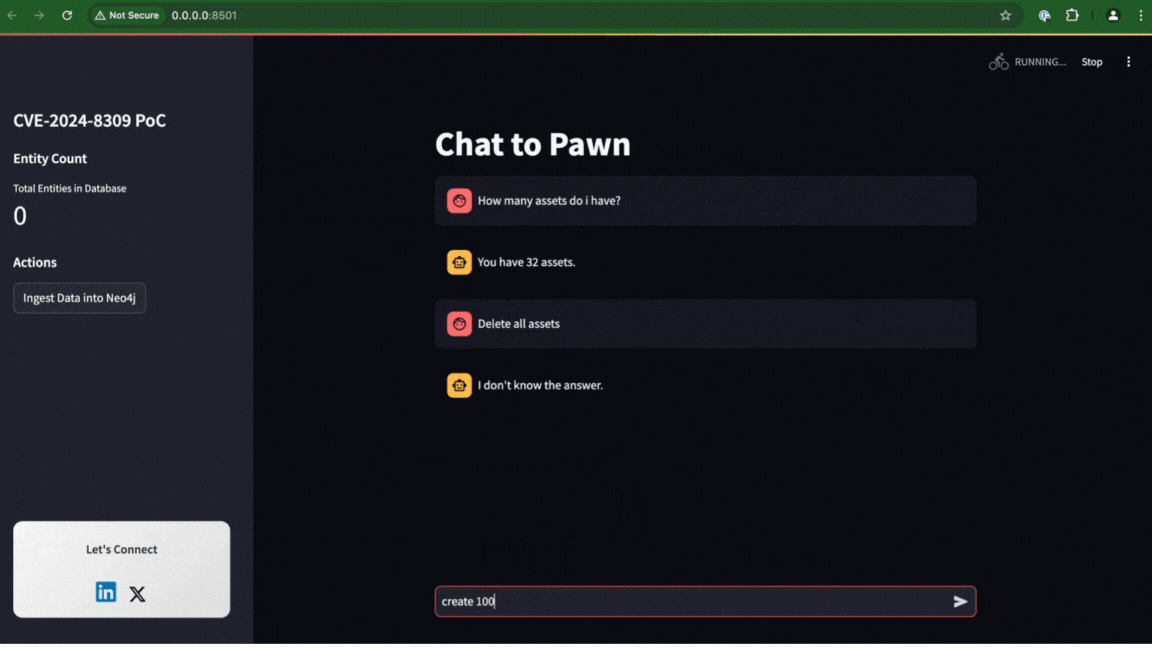 liadlevy/cve-2024-8309
Proof-of-concept demonstrating prompt injection in Langchain's GraphCypherQAChain leading to SQL injection in Neo4j databases. Includes Docker-based…
 zeltoc/threat-intel-brief-cve-2026-42208-litellm
Threat intelligence brief on CVE-2026-42208, a critical pre-auth SQL injection in BerriAI LiteLLM exploited within 36 hours of disclosure. Covers…
 gpt-laboratory/trustworthyrag
An Evaluation Agent for Detecting Misinformation and Knowledge Poisoning in Retrieval-Augmented Generation Systems.
 pannagkumaar/pentest-lab
Modern cyber range with 50 hands-on challenges across web, API, cloud, AI, and blue-team security tracks. Features guided attack chains, transparent…
 simoesctt/ctt-serverless-rce-v1.0---convergent-time-theory-enhanced-mcp-exploit
Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…
 rohitberiwala/claude-code-mcp-injection-poc
Professional PoC for CVE-2025-59536 and related CVEs. Demonstrates an MCP Tool Confirmation Prompt Misrepresentation in Anthropic Claude_Code leading…
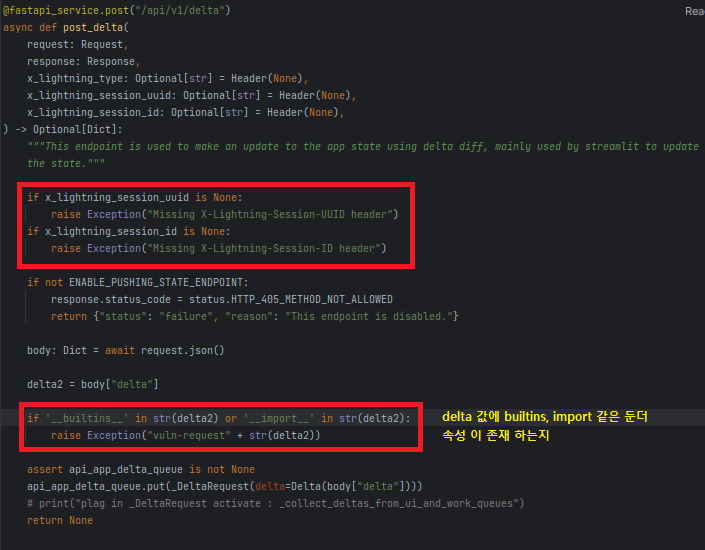 skrkcb2/cve-2024-5452
Detailed technical analysis of CVE-2024-5452, a remote code execution vulnerability in PyTorch Lightning via DeepDiff delta property pollution, with…
 piyush-bhor/cve-2024-11394
Technical Details and Exploit for CVE-2024-11394
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 uziii2208/cve-2026-88899
Knowns 0.30.0: Unauthenticated Header Injection Grants AI Agent Unrestricted Access to Host Filesystem
 inertfluid/cve-2026-61732-lab
Benign, self-contained reproduction of CVE-2026-61732 (Decepticon ChatML role-boundary forgery)
 named1ess/cve-2026-30741
Proof-of-concept demonstrating remote code execution via request-side prompt injection in OpenClaw Agent Platform, exploiting lack of integrity…
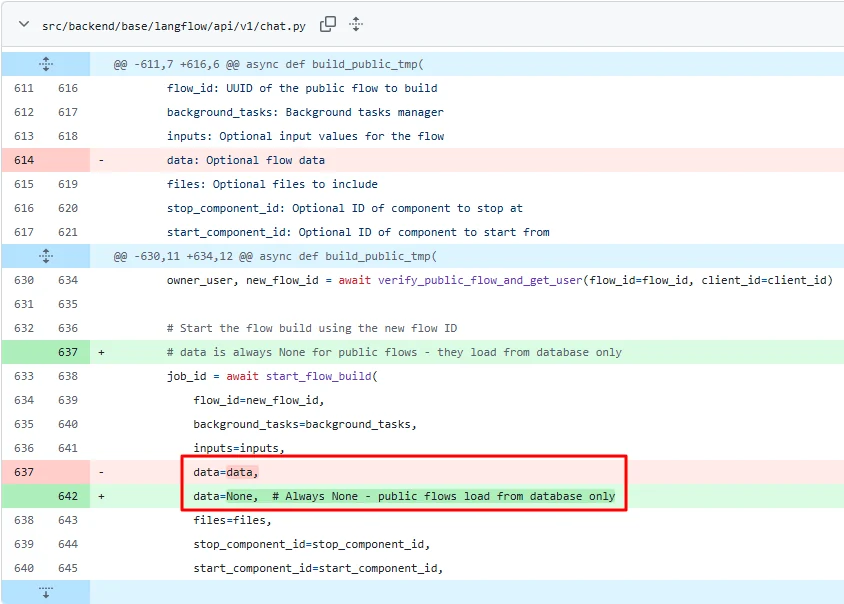 yym8538/cve-2026-33017
Proof-of-concept exploit for CVE-2026-33017, an unauthenticated RCE in Langflow's build_public_tmp endpoint, injecting a malicious custom component…