cybersecurity-projects

This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…

This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…

AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.

The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…

Claude Skill that audits your projects for RLS misconfigurations, exposed keys, auth bypasses, and storage vulnerabilities. 27 anti-patterns sourced…

Open-source AI security platform providing perimeter defense for LLMs and AI agents through swarm analysis, policy enforcement, adversarial testing,…

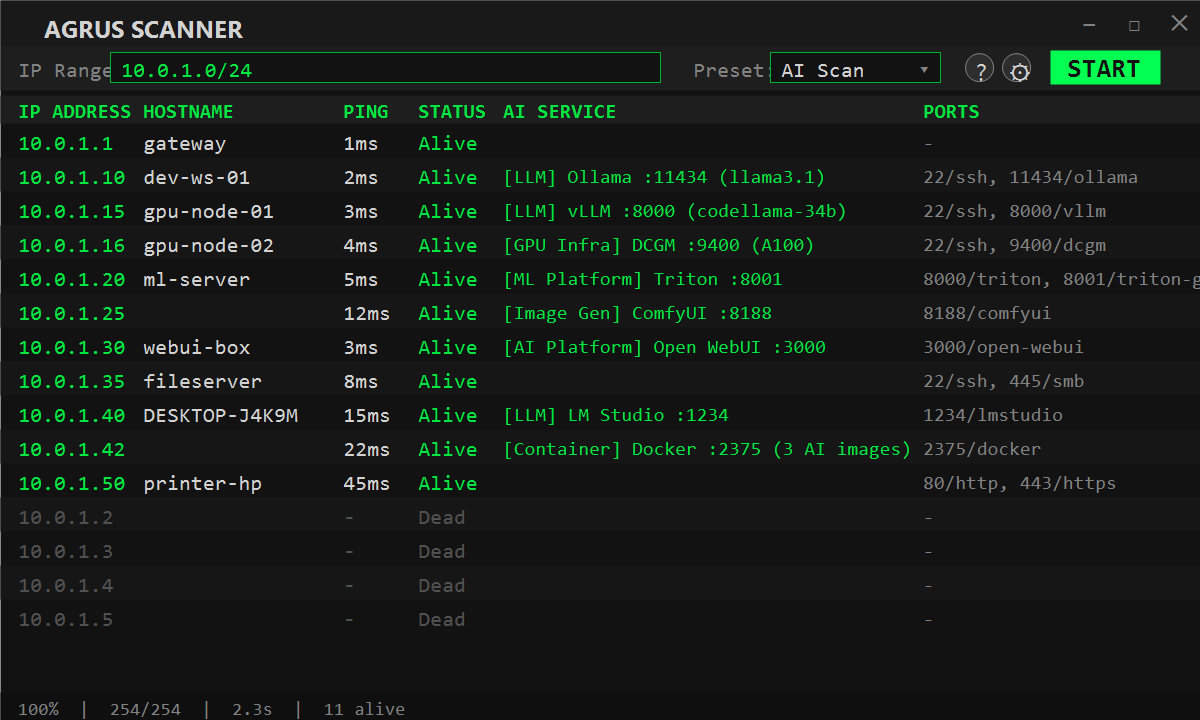
Windows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…

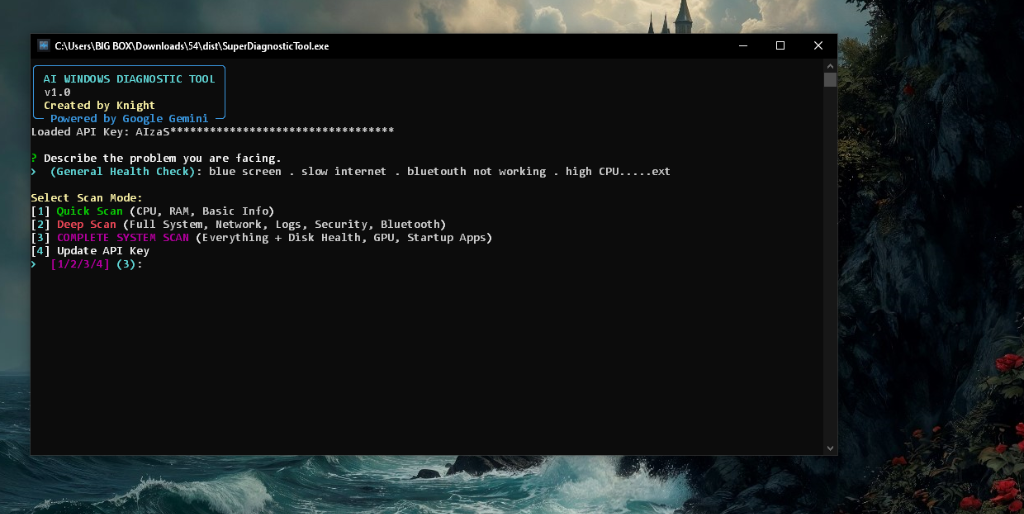
AI-powered Windows diagnostic & auto-repair tool using Google Gemini. Detect crashes, optimize performance, scan for malware, and generate PowerShell…

Enterprise AI agent security toolkit providing pre-flight auditing, configuration hardening, runtime threat detection, and active defense against…

Sigma detection rules for AI agent security monitoring

MCP is being adopted rapidly. Security guidance is lagging behind. This checklist gives security engineers, platform teams, and technical leaders a…

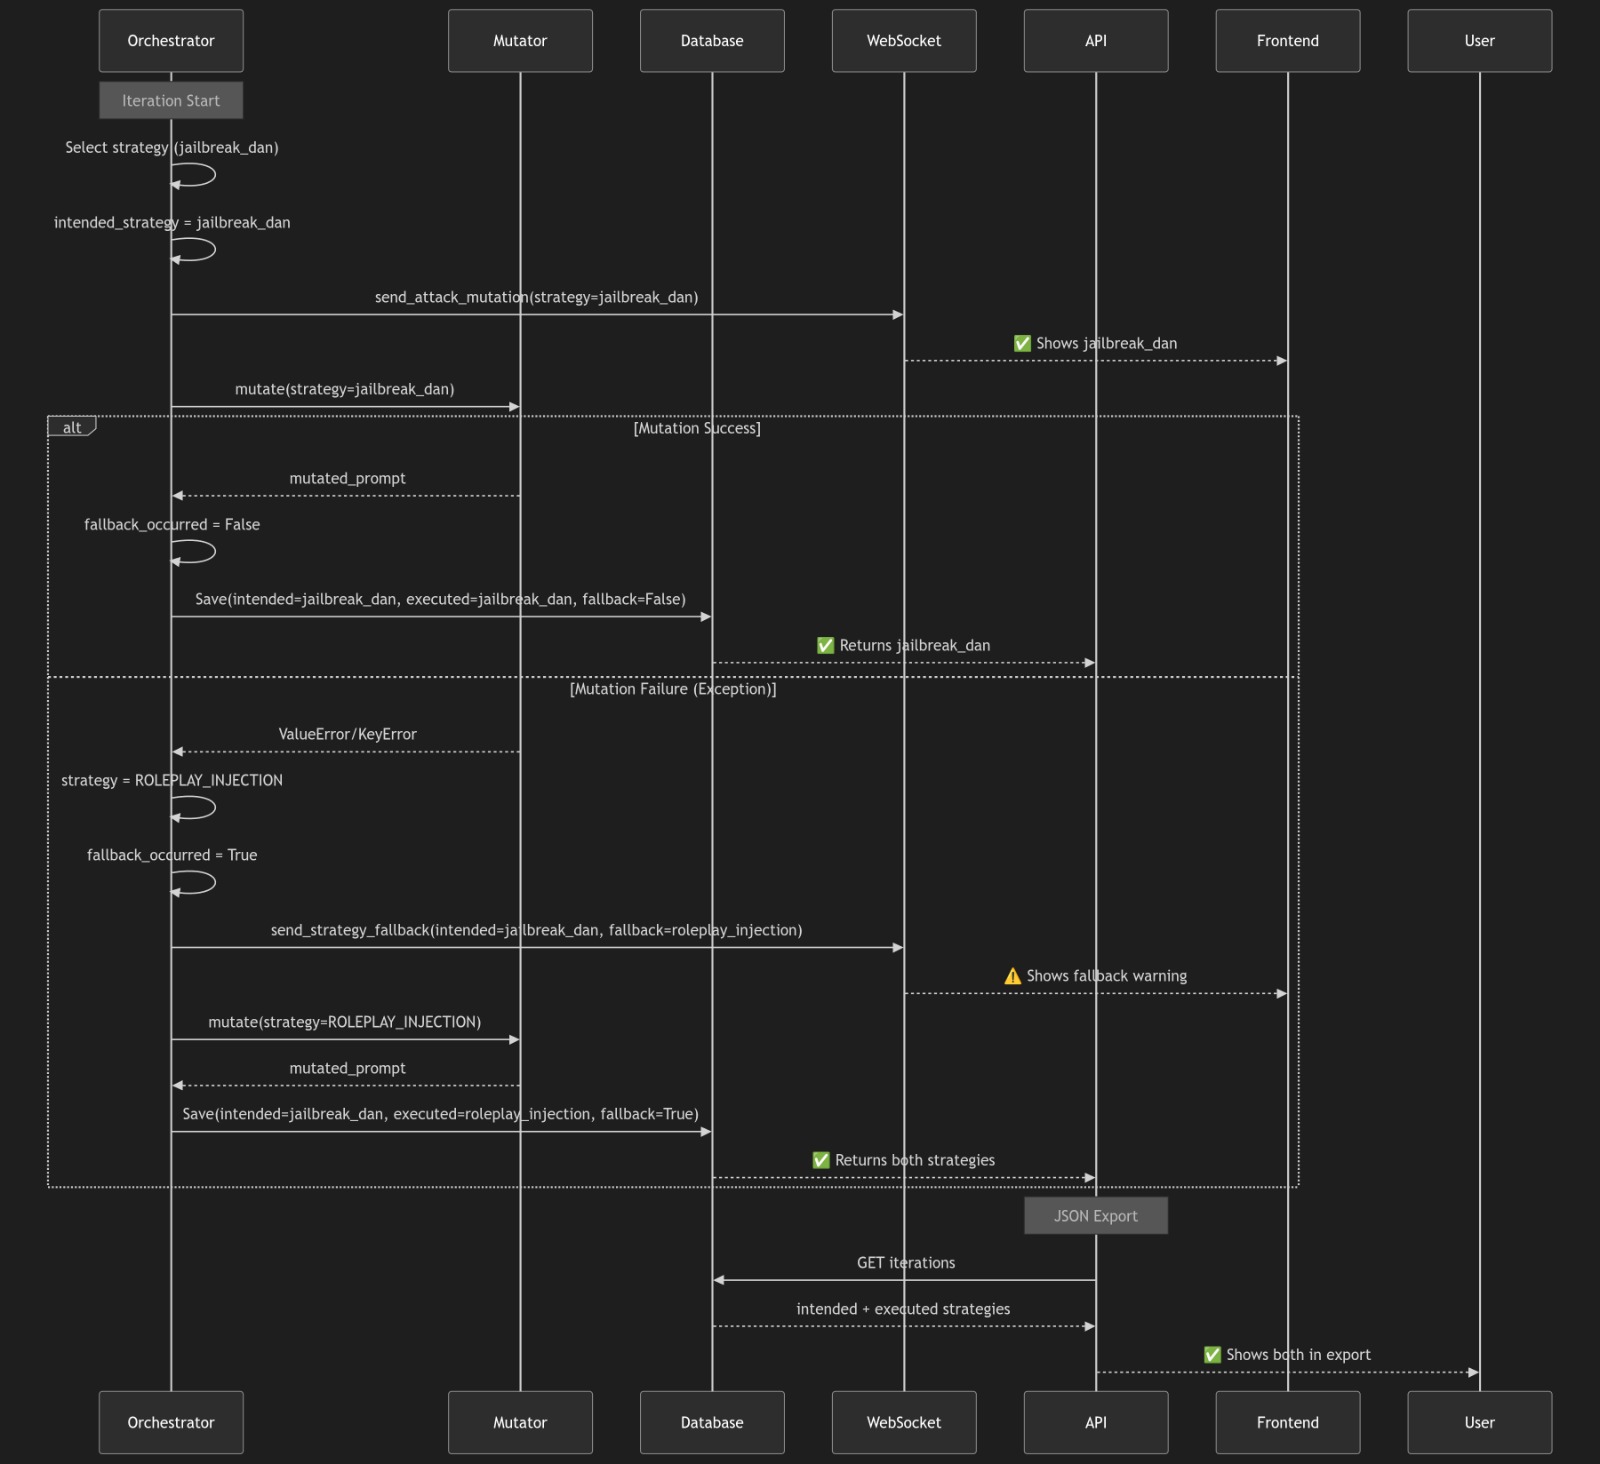
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation

Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…

Causal context attribution and rule-based monitor LLM defense against indirect prompt injection in LLM agents, achieving state-of-art performance on…

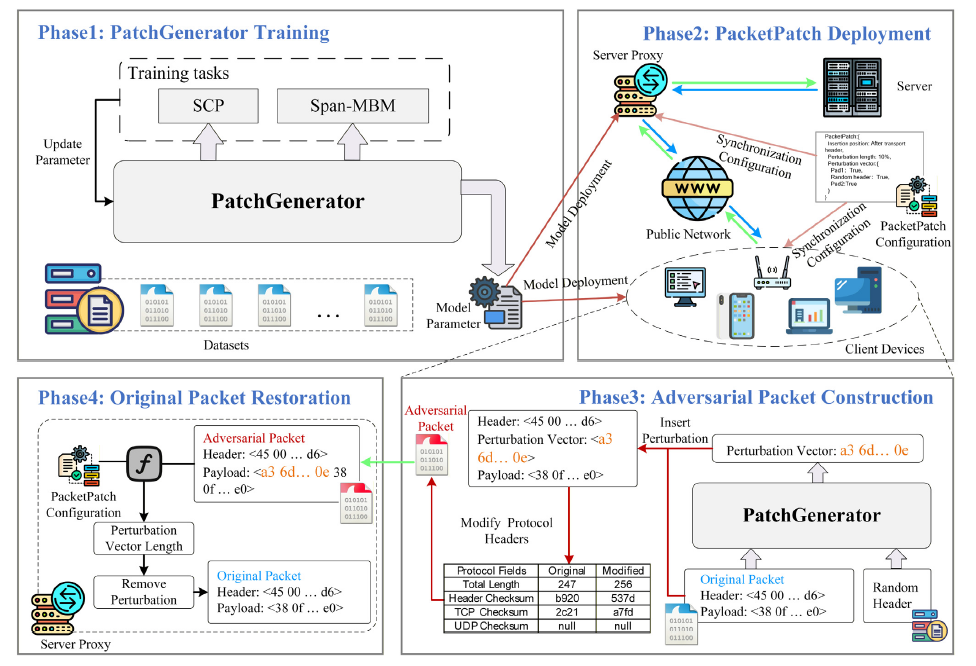
Practical black-box adversarial packet generation against encrypted traffic classification with minimal overhead and full packet recoverability.

Unified dashboard to monitor, govern, and audit AI agents in real-time. Enforce budgets, detect policy violations, and export compliance reports for…

Zero-trust sandbox for AI agents with kernel-level filesystem jail, transparent network proxy, and YAML-based policy engine to intercept and control…

Read-only WordPress security scanner for HestiaCP servers. Detects wp2shell compromise indicators (CVE-2026-63030 / CVE-2026-60137) across all hosted…

A practical framework identifying and prioritizing the top security risks in AI datacenter infrastructure, covering hardware, networking, management…