

secure-agent-playbook
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
ai-securityapi-securitycloud-security+9
1792 days ago
owasp/secure-agent-playbookOWASP Secure Agent Playbook Project
 owasp/pwnzzai
Hands-on AI security learning platform with intentionally vulnerable LLM applications. Explore OWASP Top 10 for LLMs through interactive pizza shop…
 owasp/owasp-aibom
OWASP project defining an AI Bill of Materials (AIBOM) standard to document AI/ML components, dependencies, and supply chain risks for AI security…
 owasp/donkai
DonkAI is a hands-on lab for the OWASP Top 10 for LLM Applications (2025) - no real LLM required.
 owasp/sbom-vex-taint-analysis
Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
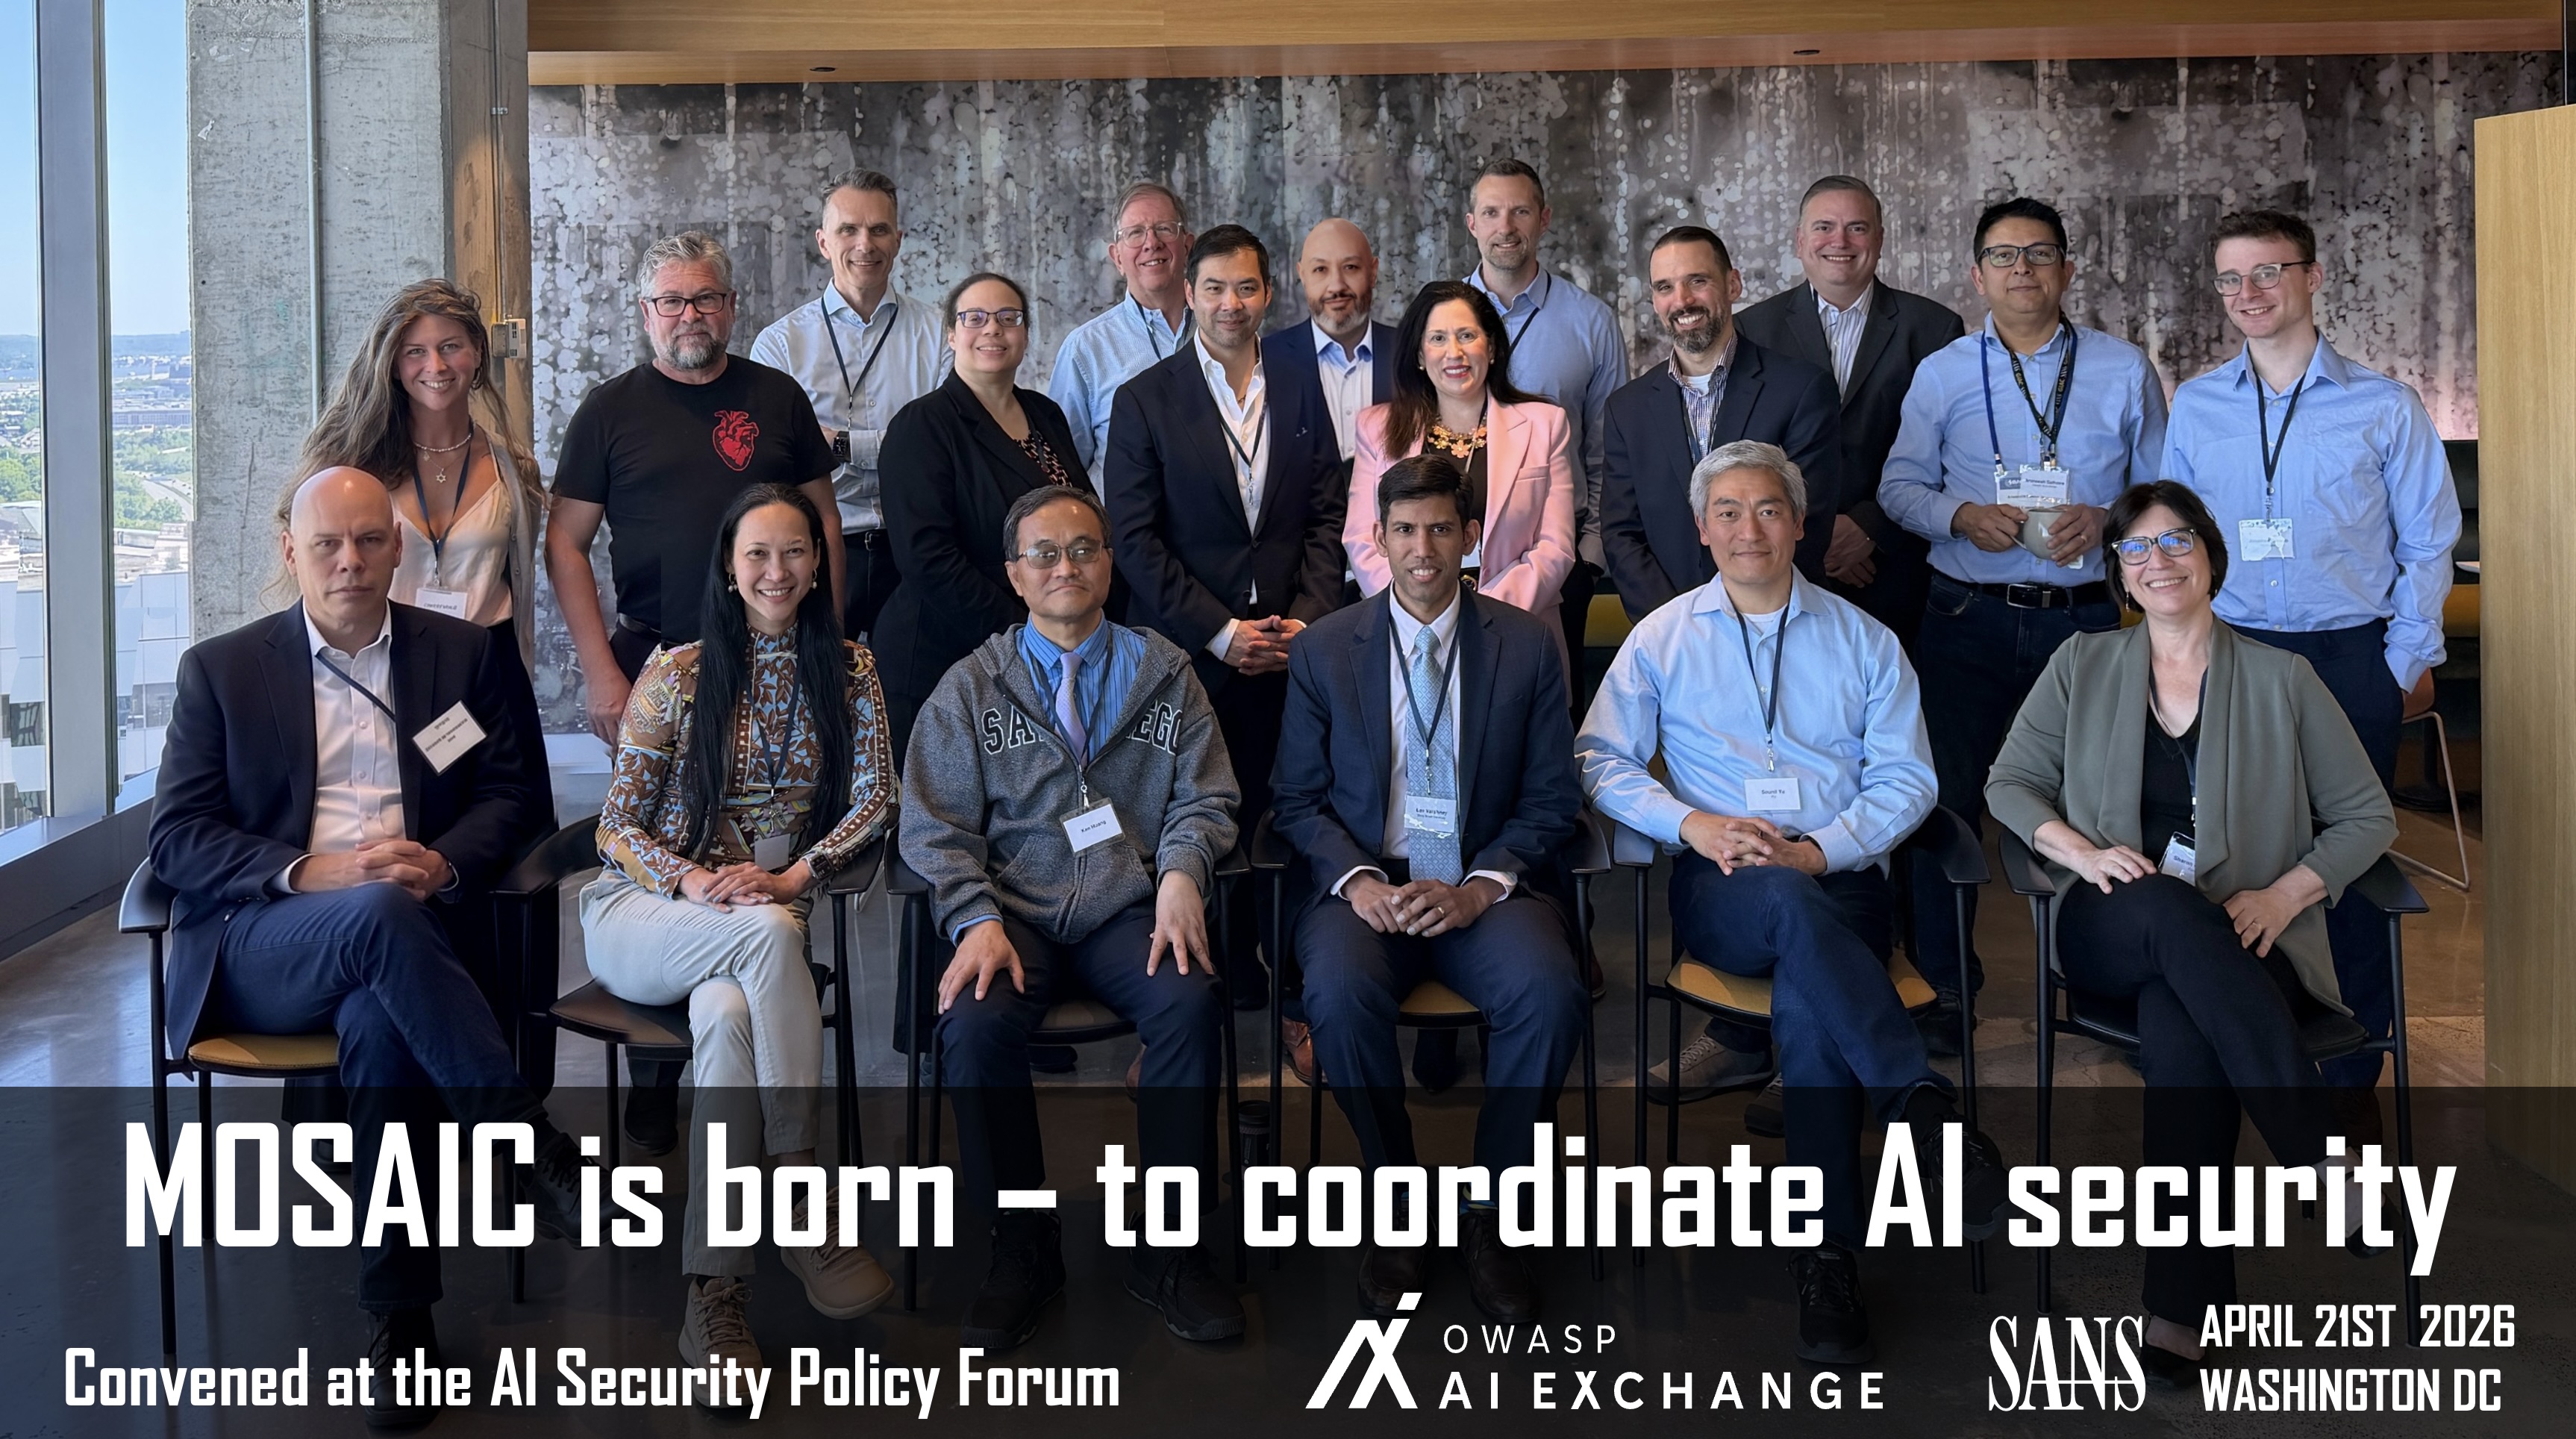 owasp/mosaic
Coordination structure for AI security standards and guidelines, reducing fragmentation and providing clear guidance for securing AI systems across…
 owasp/owasp-model-card-security-standard
Open standard for documenting security-relevant metadata of AI models, including training data provenance, PII risk, known vulnerabilities, and…
 owasp/secureml
SecureML - Securing and Watermarking AL models
 owasp/agent-skills-security-standard
Security standard for agent skills, providing guidelines and best practices to secure AI-driven autonomous agents in cloud and API environments.
 owasp/damn-vulnerable-ml-model
Intentionally vulnerable machine learning model for hands-on security training. Explore common ML vulnerabilities, adversarial attacks, and defensive…
 nexaiceo/nexus-os
The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 ransomleak/training-security-awareness
Open-source interactive security awareness training library with 130+ SCORM exercises covering phishing, vishing, BEC, MFA fatigue, and OWASP AI/LLM…
 josh-blythe/bordair-multimodal
Open-source cross-modal and multimodal prompt injection test suite. 250,000+ attack payloads across text, image, document, and audio modalities.…
 bytepro-ai/bitcoder-v2-research
Research repository documenting LLM generalization ceilings in code security vulnerability detection, with cross-evaluation across synthetic and…
 geeksikhsecurity/ai-tool-poisoning-guard
Free security-baseline rule for Claude Code, Codex, and Cursor: treats MCP tool descriptions as untrusted input (OWASP MCP Top 10 MCP03,…