Guardrails
 nvidia-nemo/guardrails
Programmable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask…
ai-securityanomaly-detectiondefensive-tools+3
7.4k
nvidia-nemo/guardrailsProgrammable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask…
 sseshachala/conductai
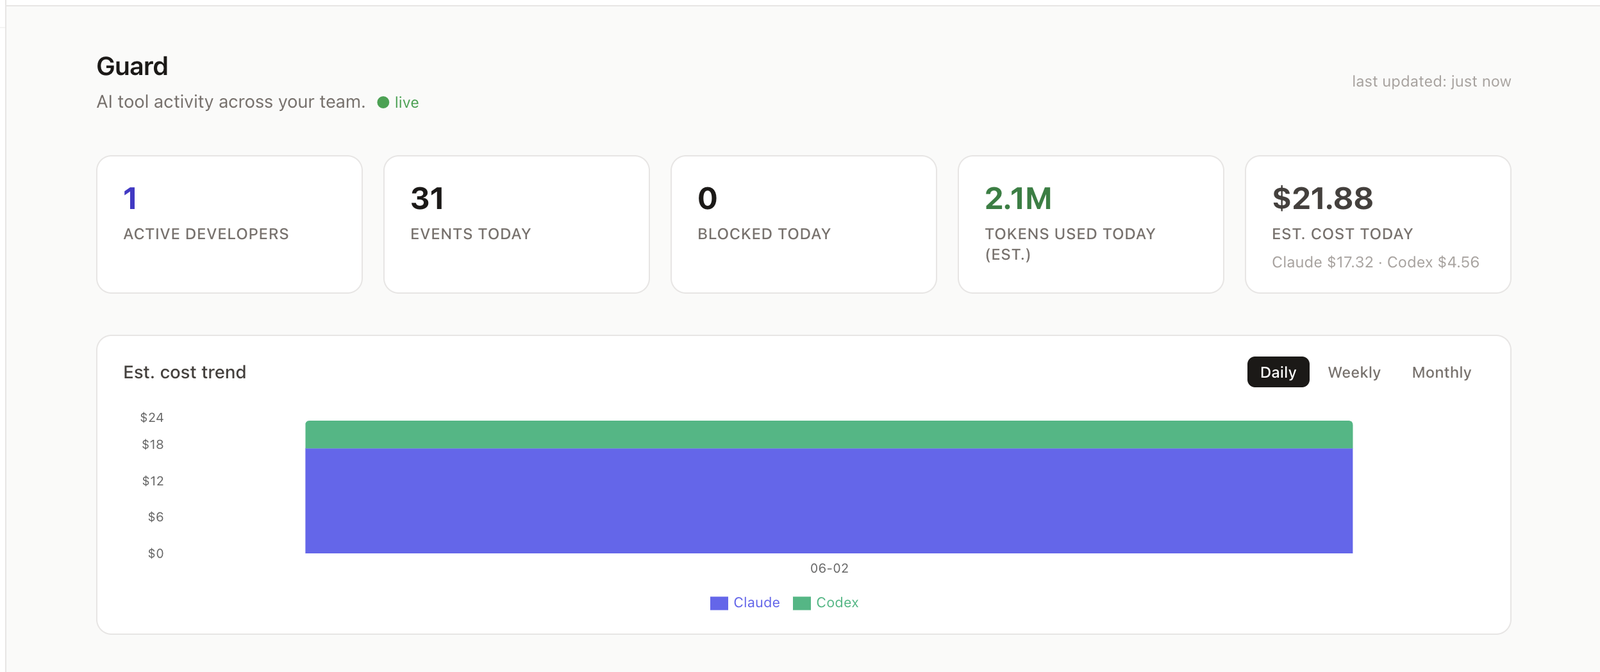
Runtime governance for AI agents. Allow, warn, or block every model and tool call before it commits. Hash-chained audit for every decision.…
 wattocyber/lm-fingerprint
Fingerprint OpenAI-compatible LLMs from tokenizer and behavior signals.
 wattocyber/agentic-dm-gateway
Security control plane for LLM agents: allowlists, owner kill switch, PIN sessions, rate limits, prompt-injection detection, and output scrubbing to…
 mohamed--abdel-maksoud/pisiguard
Browser extension that detects PII and sensitive data in AI chats, masks it with placeholders before sending, and restores originals in replies—all…
 ryehr/hitms_steganography
Embed multiple secret messages in LLM chat token choices using arithmetic/Discop steganographic coders, with bit-exact decoding and steganalysis…
 securelayer7/promptpurify
Prompt-injection guardrail for LLM applications. Compact model that outperforms larger open-source guards. No regex, no signatures. Demo:…
 ashishsecdev/mobsf_ai
AI powered security analysis extension for Mobile Security Framework MobSF
 lycis/cawdog
CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…
 trinib/zorg-jailbreak-prompt-text
Bypass restricted and censored content on AI chat prompts 😈