

repeat-strike
 hackvertor/repeat-strike
Burp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…
ai-securityapi-security-testinginformation-gathering+6
41
hackvertor/repeat-strikeBurp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…
 hackvertor/shadow-repeater
Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…
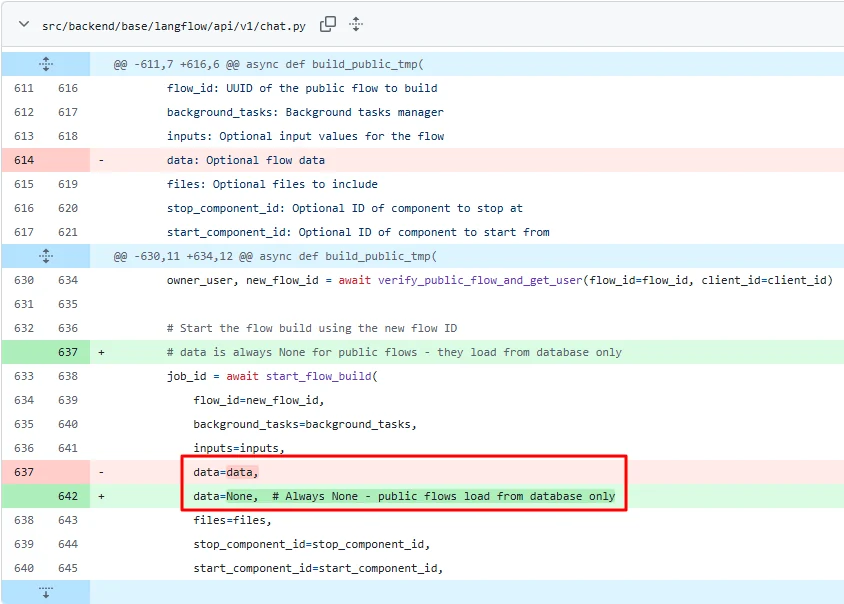 yym8538/cve-2026-33017
Proof-of-concept exploit for CVE-2026-33017, an unauthenticated RCE in Langflow's build_public_tmp endpoint, injecting a malicious custom component…
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
 gmh5225/ida-claude-code-plugins
Plugins integrating Claude Code with IDA Pro to assist reverse engineering and binary analysis workflows through AI-driven disassembly and code…
 portswigger/http-terminator
AI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…
 inertfluid/cve-2026-61732-lab
Benign, self-contained reproduction of CVE-2026-61732 (Decepticon ChatML role-boundary forgery)
 bardlaudian/cve-2024-37054
Proof-of-concept that poisons MLflow registered models via the REST API, embedding a malicious pickle to trigger RCE when the model is loaded.
 oscar-collado/comfyui-cve-2026-68771-poc
Security research lab — Unauthenticated RCE via insecure deserialization in ComfyUI v0.23.0 (CVSS 9.8). Isolated Docker environment, technical…
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 uziii2208/cve-2026-88899
Knowns 0.30.0: Unauthenticated Header Injection Grants AI Agent Unrestricted Access to Host Filesystem
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
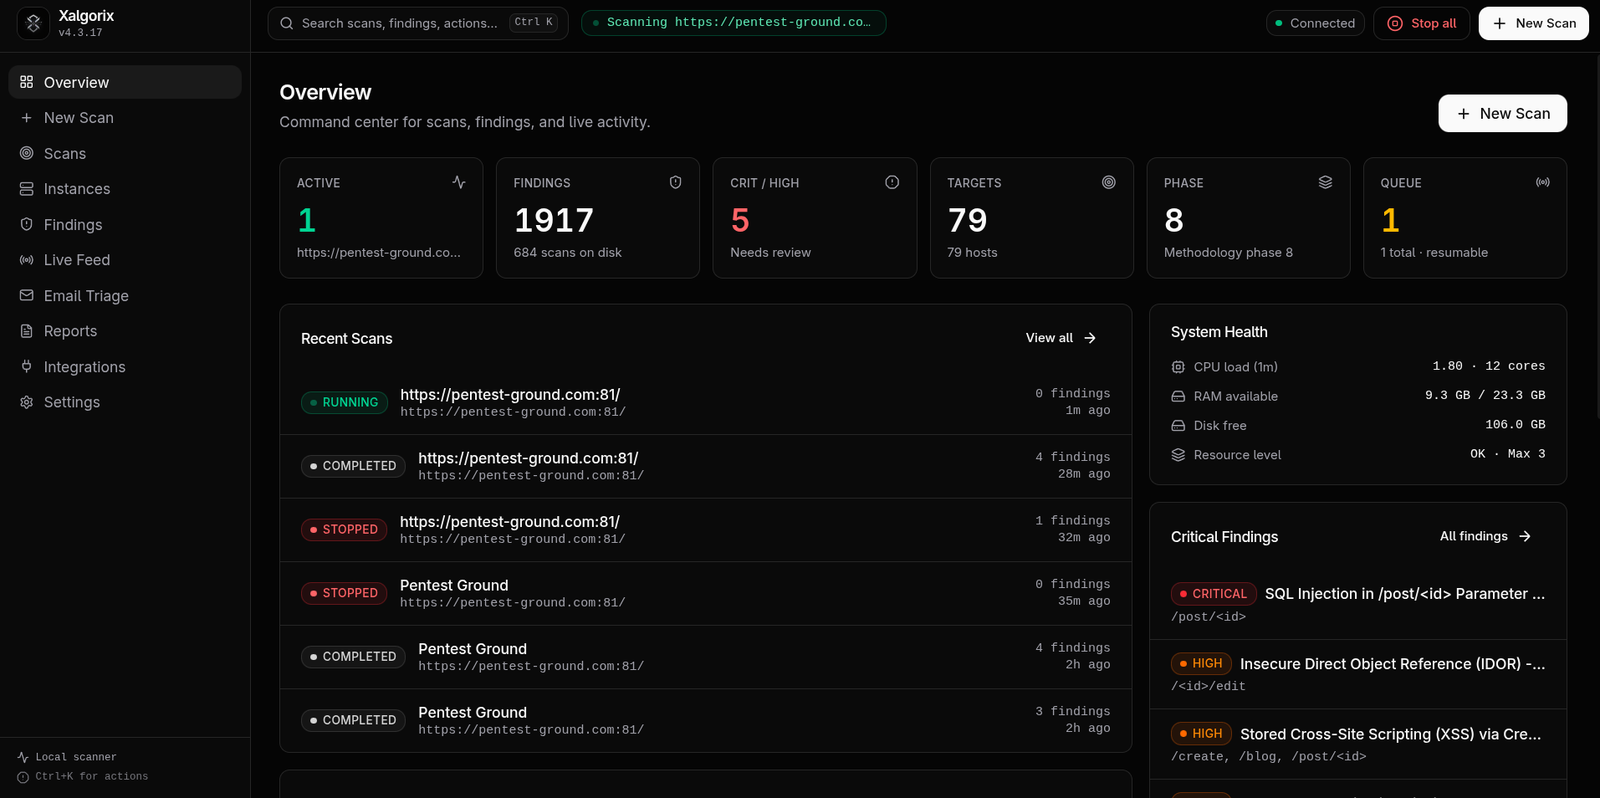 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 freire007-byte/sentric-core
Autonomous AI agent with its own crypto identity — hunts CVEs, builds exploit labs, validates vulnerabilities (first public PoC of CVE-2026-86283),…
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
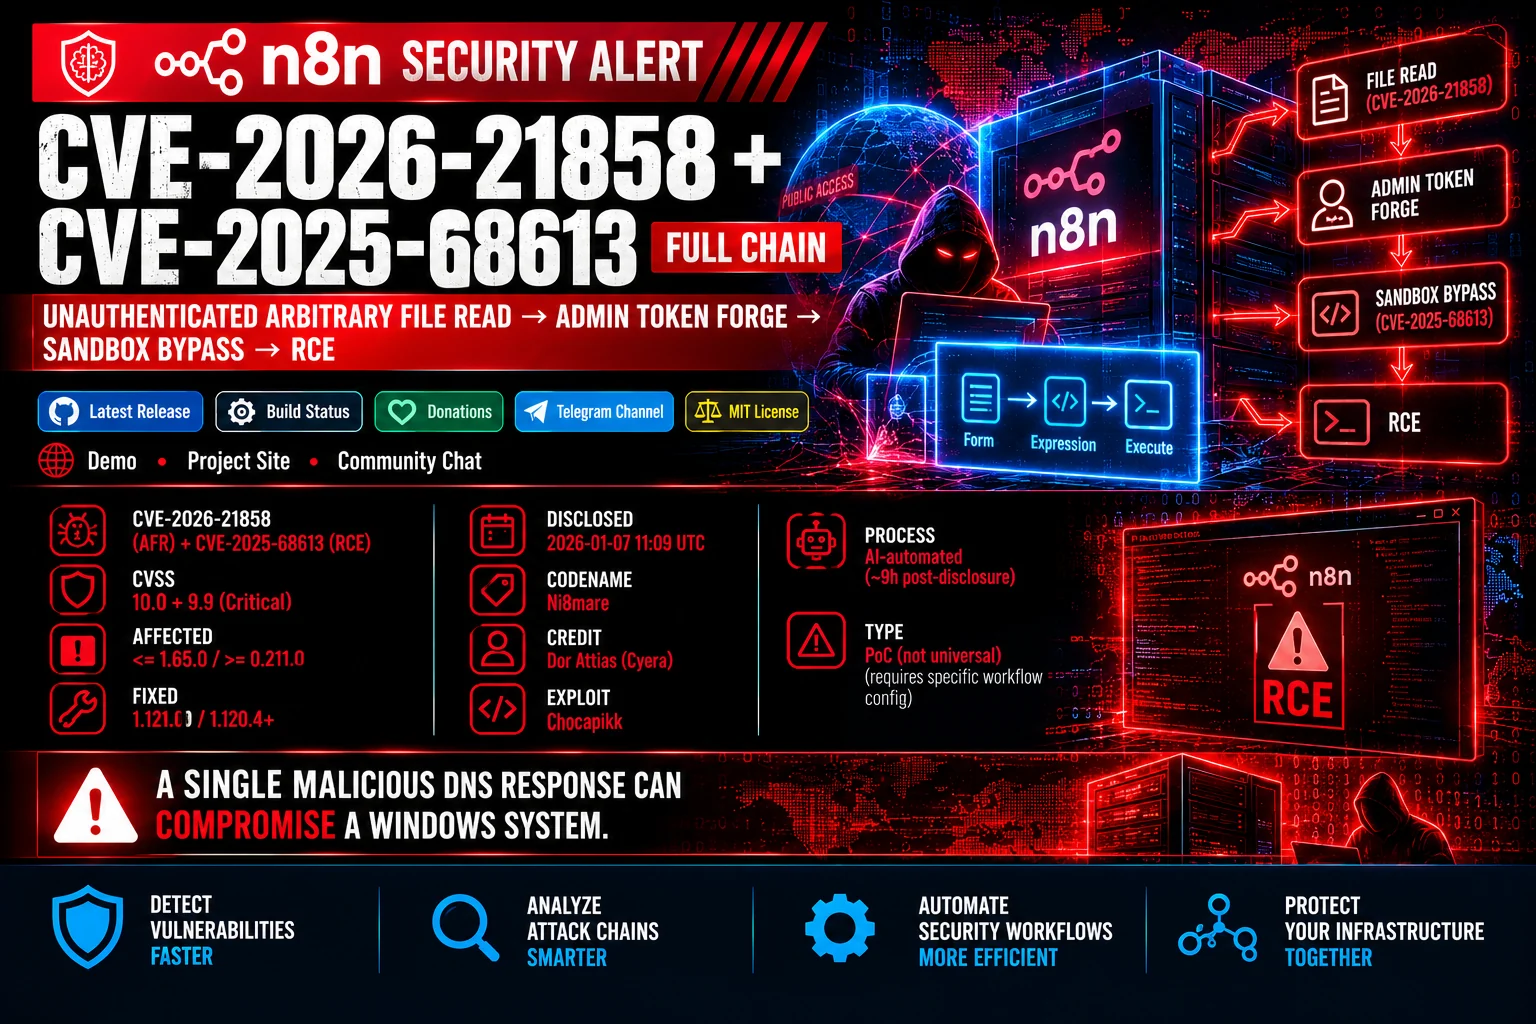 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…