

secprbench
 secprbench/secprbench
Benchmark of 265 real vulnerability-introducing code changes across nine C, C++, and Rust projects, with paired review tasks, Docker sandbox, judge,…
ai-securitycode-analysiscurated-resources+6
secprbench/secprbenchBenchmark of 265 real vulnerability-introducing code changes across nine C, C++, and Rust projects, with paired review tasks, Docker sandbox, judge,…
 lzh0082-cloud/code-detection
Replication package studying how LLM vulnerability auditors defer to static-analysis evidence, with a tree-sitter C/C++ front end, controlled…
 trailofbits/brotli-checker
Claude Code and Codex skill for finding potentially vulnerable Brotli copies and guiding updates for CVE-2026-111497.
 asngs/agenttriage-open-source
Cross-agent tracing and security-diagnosis system for tool-using LLM agents: normalizes trace events, builds provenance graphs, extracts…
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 ag3ntsc4rn/autorun-audit
Find code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…
 happytotoro116/ghidra-llm-pipeline
Deterministic PyGhidra extraction, triage, and local LLM compiler-backend pipeline for C reimplementation.
 gmh5225/malicious-code-detection-bugu
AI-based malicious code detection and obfuscation system with microservices for detection, packing, and code confusion, plus user and admin services.
 gach0ng/agentstalker
End-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 moontea0416/webmirage
Adversarial image attacks on vision-language web agents, from visual grounding to browser execution
 githubsecuritylab/seclab-taskflow-agent
MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 morluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
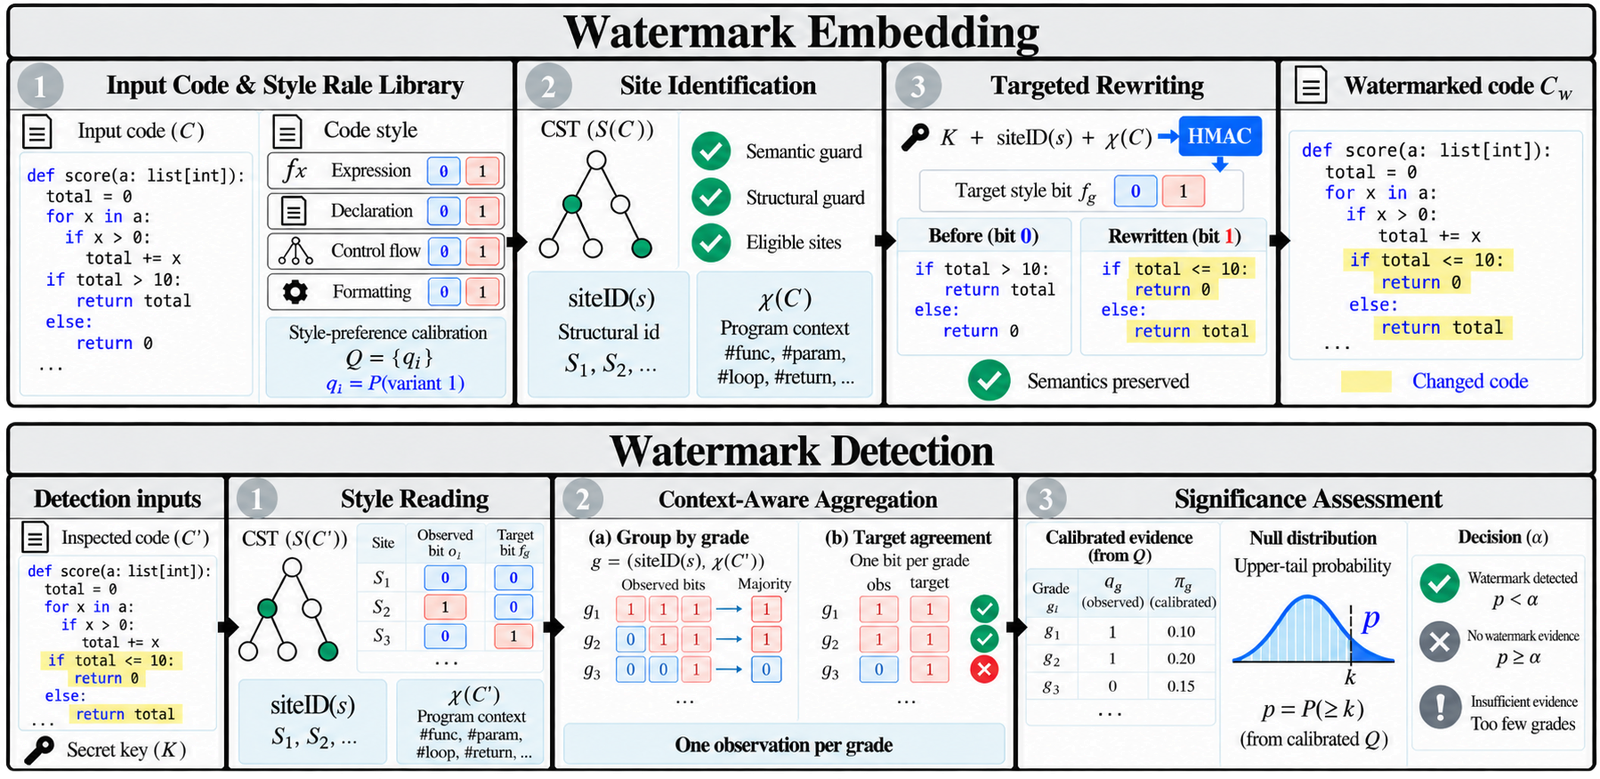 suhanmen/sew
Embeds and detects keyed, style-based watermarks in LLM-generated Python, Java, and C++ code via CST rewriting, preserving functional correctness and…
 linuztx/alter-zero
RAM efficient terminal agent harness for coding, cybersecurity, and automation.
 joshuaprovoste/deserializer
AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…