
Agent-Reach
 panniantong/agent-reach
Give your AI agent eyes to see the entire internet. Read & search Twitter, Reddit, YouTube, GitHub, Bilibili, XiaoHongShu — one CLI, zero API fees.
ai-securitycrawlergeneral-purpose-utilities+5
82.4k
panniantong/agent-reachGive your AI agent eyes to see the entire internet. Read & search Twitter, Reddit, YouTube, GitHub, Bilibili, XiaoHongShu — one CLI, zero API fees.
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 sushant-me/agentic-workflow-injection
Reproducible vulnerable and fixed GitHub Actions fixtures for agentic workflow injection (CVE-2026-44246), with measured detector coverage and…
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 off-by-1-labs/flawed
Fix-Like Artifacts With Embedded Defects
 adarsh14734/aegis-releases
Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
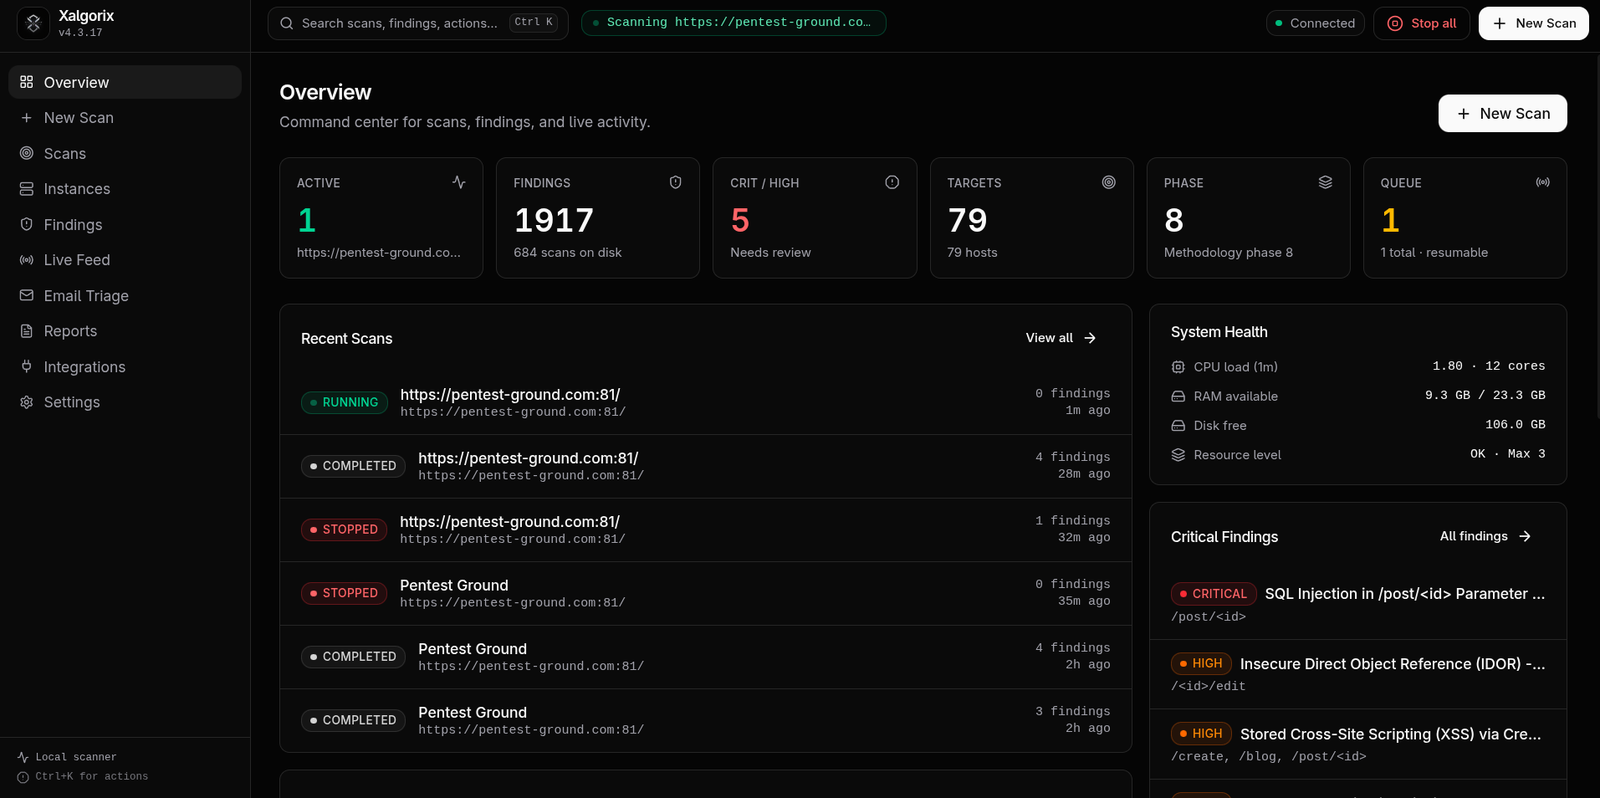 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 runewardd/runeward
Governed execution cells for AI agents.
 freire007-byte/sentric-core
Autonomous AI agent with its own crypto identity — hunts CVEs, builds exploit labs, validates vulnerabilities (first public PoC of CVE-2026-86283),…
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 abhishek2512mishra/claude-code-security-audit
Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.
 badchars/darknet-mcp-server
66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…
 owasp/owasp-aibom
OWASP project defining an AI Bill of Materials (AIBOM) standard to document AI/ML components, dependencies, and supply chain risks for AI security…