

cdxgen
 cdxgen/cdxgen
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…
ai-securitycloud-securityconfiguration-auditing+6
1.1k
cdxgen/cdxgenCreates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…
 tencentcloud/cubesandbox
Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.
 tridents10/vader-pro-vdr
AI-assisted Vulnerability Detection & Remediation platform featuring a Go endpoint agent, centralized dashboard, and vulnerability intelligence…
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 tuskira/ai-agent-gateway
Open-source gateway that secures, governs, and observes AI agents' MCP tool calls and LLM traffic, with API-key authentication and an admin console…
 owasp/owasp-top-10-neocloud-and-ai-data-center-security-risks
OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 sorami-consulting-au/ai-kubernetes-helm-chart-security
Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 adarsh14734/aegis-releases
Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
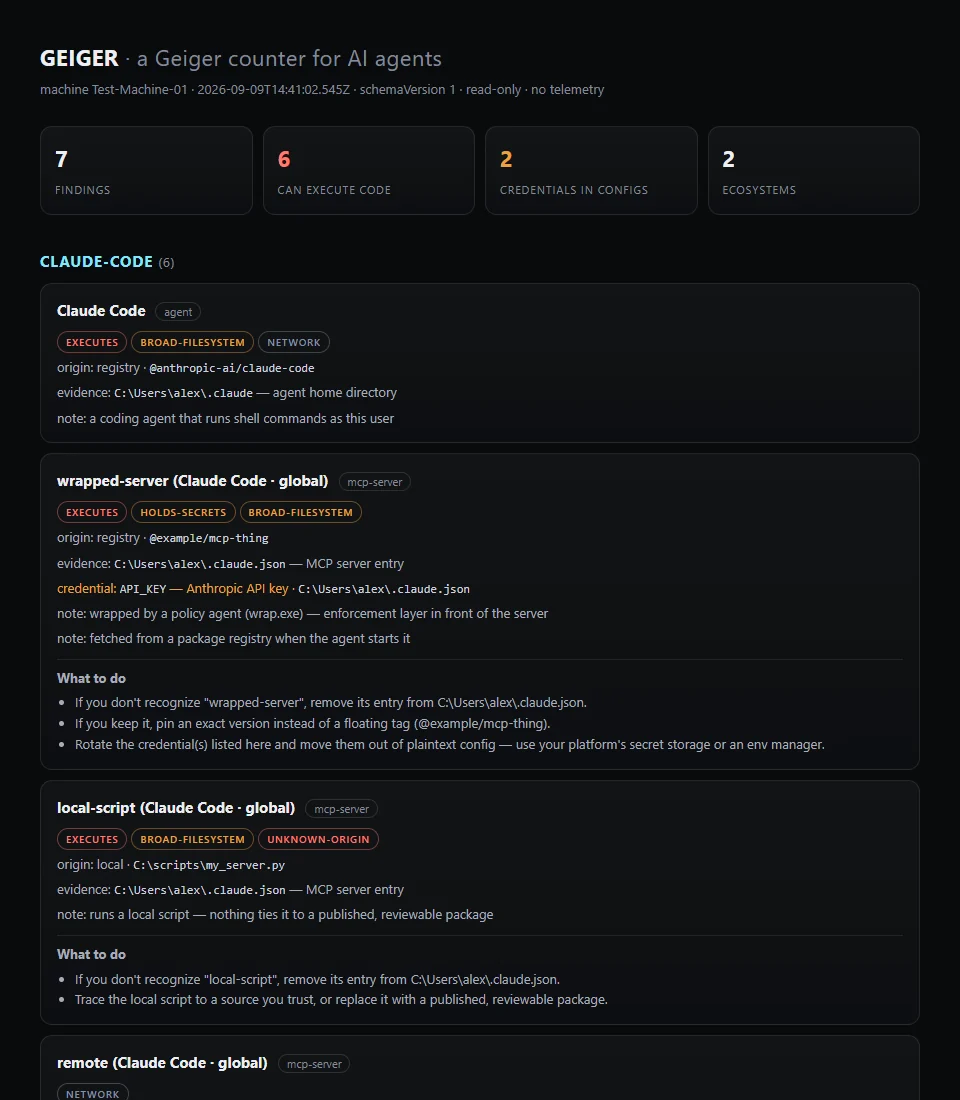 atomburstofficial/geiger
Read-only CLI that inventories AI agents, MCP servers, plugins, and extensions on a machine, reporting their capabilities and exposure with…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 pigeonlabshq/pigeon
Enforce least-privilege delegation for AI agents with signed, scoped credentials. Grant sub-agents narrow capabilities and resources, verify actions…
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 db-ol/cuaharm
Benchmark for evaluating safety risks of computer-using agents, with 104 realistic misuse scenarios across seven malicious categories, supporting…
 sseshachala/conductai
Runtime governance for AI agents. Allow, warn, or block every model and tool call before it commits. Hash-chained audit for every decision.…