

CyberStrike
 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
ai-securitycloud-securityeducation+9
2.9k
cyberstrikeus/cyberstrikeAutonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
 named1ess/cve-2026-30741
Proof-of-concept demonstrating remote code execution via request-side prompt injection in OpenClaw Agent Platform, exploiting lack of integrity…
 appsecco/vulnerable-mcp-servers-lab
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.
 wantasticapp/wantasticcore
AIO Cloud Managment Server
 clearlotus-git/cve-2024-37054-poc
Proof-of-concept and research repository for CVE-2024-37054, an unsafe deserialization flaw in MLflow PyFunc model loading that can lead to remote…
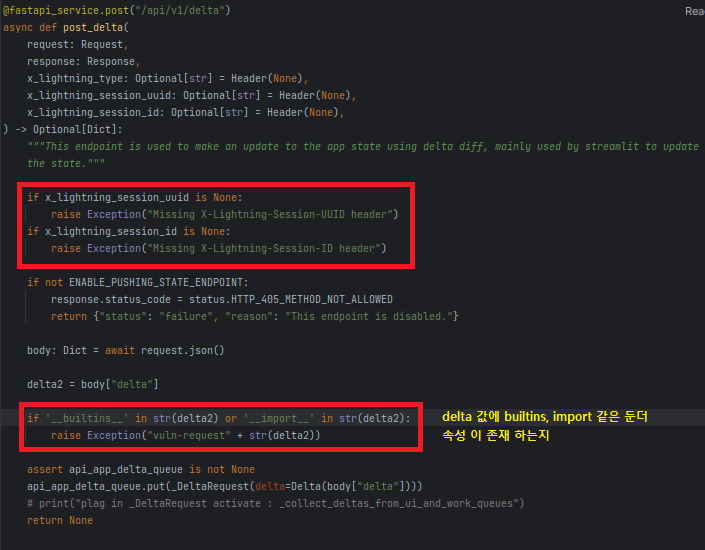 skrkcb2/cve-2024-5452
Detailed technical analysis of CVE-2024-5452, a remote code execution vulnerability in PyTorch Lightning via DeepDiff delta property pollution, with…
 ccss17/o3_finds_cve-2025-37899
Artefacts for blog post on finding CVE-2025-37899 with o3
 boreas37/cve-2025-62593-poc
PoC for CVE-2025-62593: unauthenticated RCE in Ray (CISA KEV). Stdlib-only Python.
 shinthink/cve-2026-27966
Pre-auth RCE scanner for Langflow < 1.8.0 — Route Injection + Vertex Injection → Code Execution (CVSS 9.8)
 george0papasotiriou/cve-2026-1337-ai-coding-assistant-prompt-injection-to-sandbox-escape
A prompt injection in a code‑review bot that executes AI‑generated fixes in a sandbox. The sandbox uses a blacklist to prevent dangerous commands,…
 0xgh057r3c0n/cve-2025-3248
Exploit for Langflow AI Remote Code Execution (Unauthenticated)
 inertfluid/sk-cve-2026-26030-lab
Ethical, network-isolated Docker lab reproducing CVE-2026-26030 — Semantic Kernel in-memory vector store filter eval() RCE (patched in 1.39.4)