

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
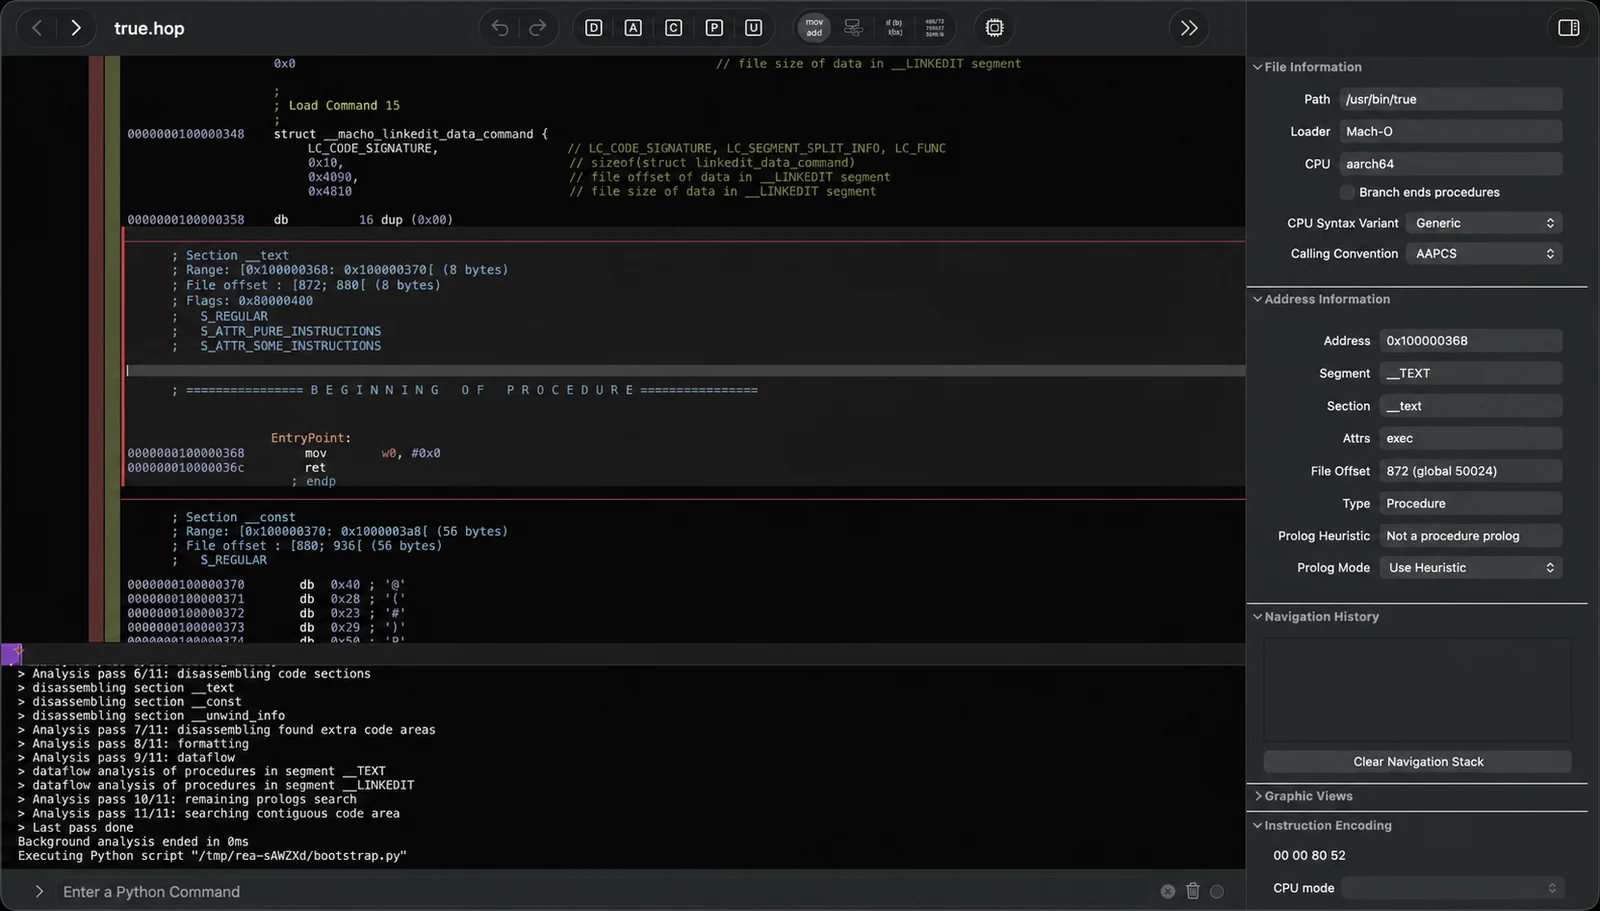 morluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
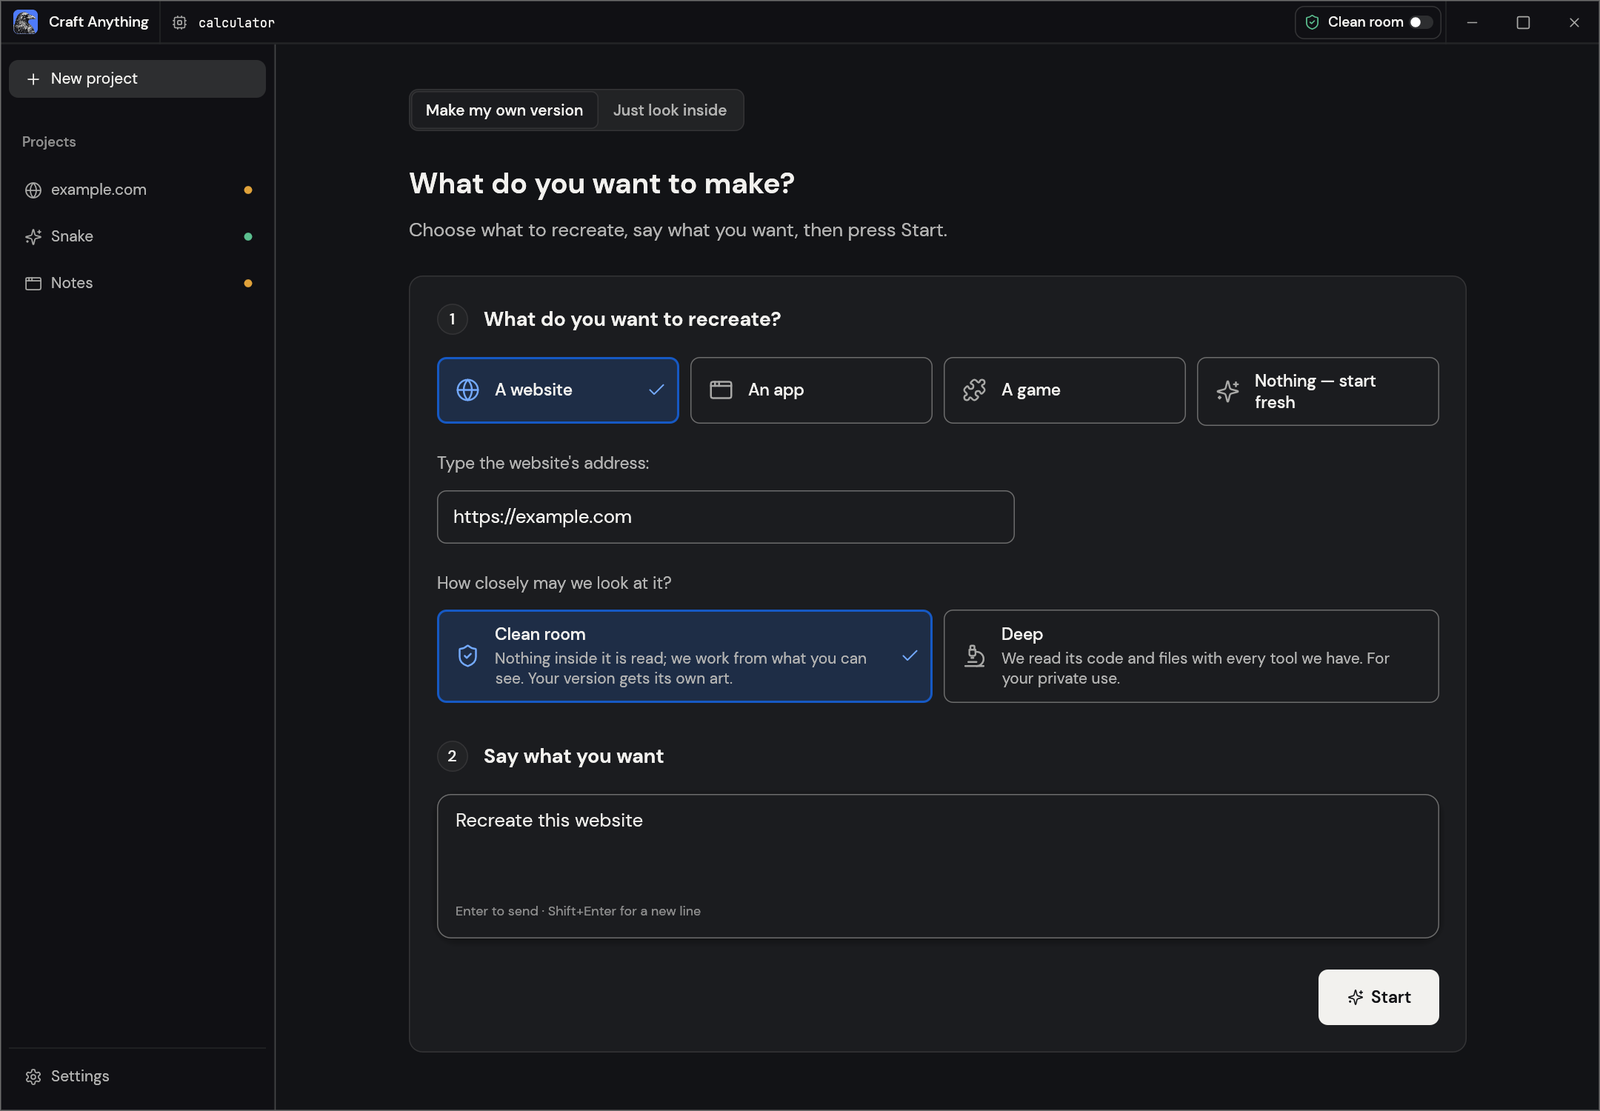 storytold/craft-anything
Pure-Rust reverse-engineering engine with 314 CLI/MCP inspection tools (disassembly, decompilation, strings, call graphs) that studies any app, site…
 angr/angr
A powerful and user-friendly binary analysis platform!
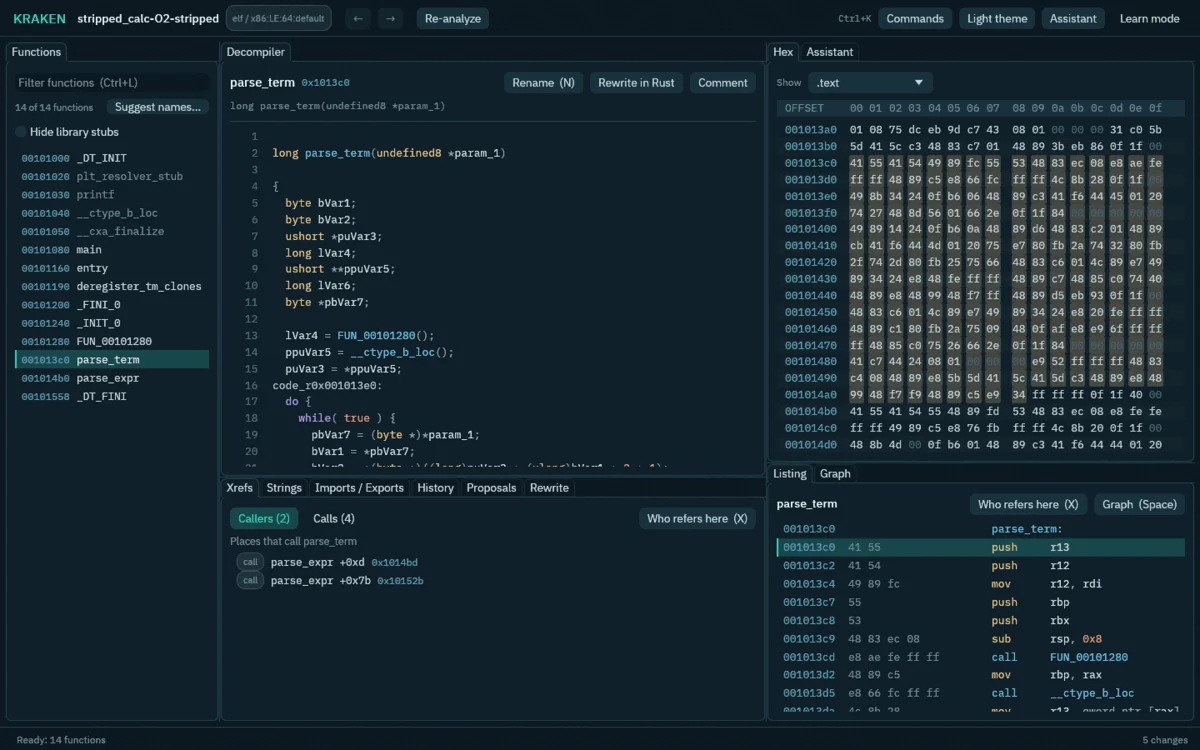 adam-atlassoftware/kraken
Reverse-engineering workbench built on Ghidra's decompiler with a native Java-free engine, AI-assisted function analysis, byte patching, sandboxed…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 zhuyansen/awesome-ai-reverse-engineering
Open-source AI reverse engineering tools for coding agents: Ghidra MCP, IDA Pro MCP, jadx, Frida, skills and REA. 122 repos, each read and…
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 githubsecuritylab/seclab-taskflow-agent
MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…