

UAC-bypass
 winscripting/uac-bypass
PowerShell proof-of-concept that bypasses Windows User Account Control (UAC) to elevate privileges, intended for authorized penetration testing and…
adversarial-attackexploitationpenetration-testing+3
242
winscripting/uac-bypassPowerShell proof-of-concept that bypasses Windows User Account Control (UAC) to elevate privileges, intended for authorized penetration testing and…
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
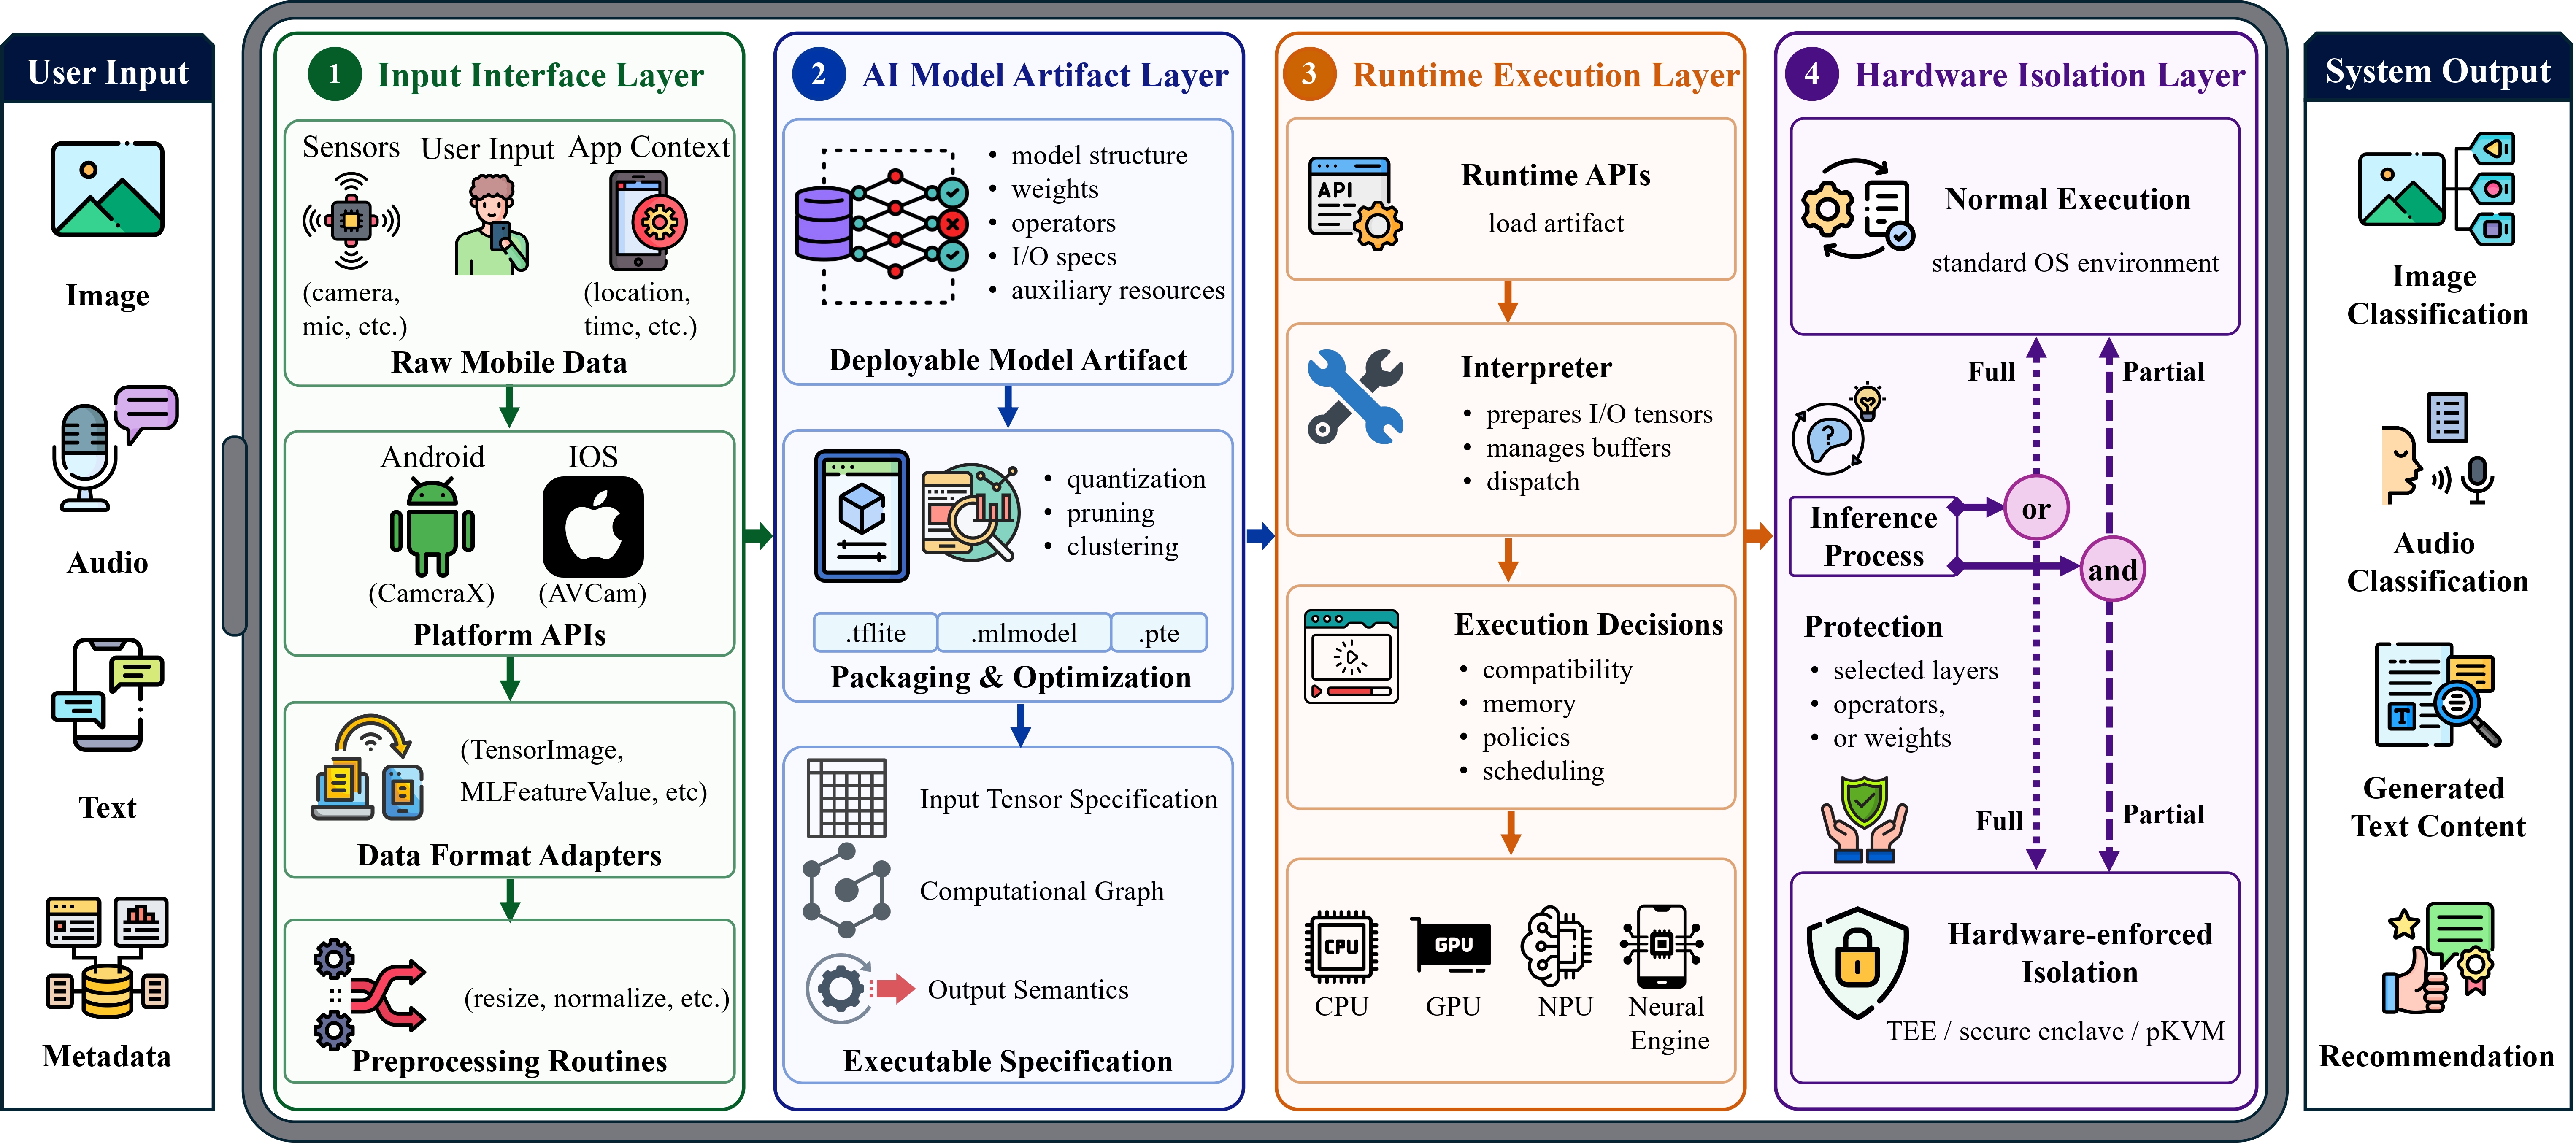 jinxhy/awesome-moai-security
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…
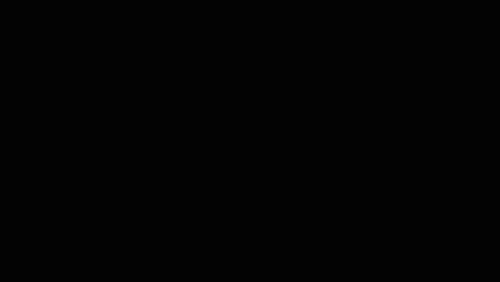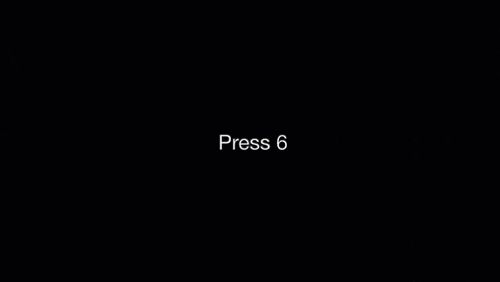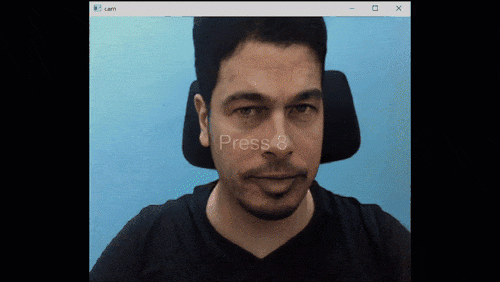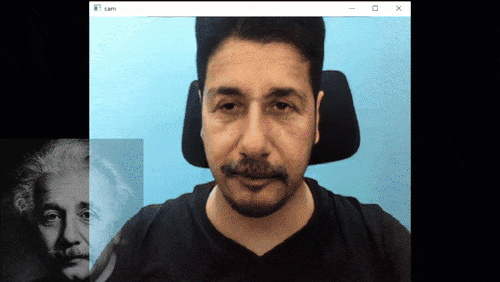 sensity-ai/dot
Real-time deepfake toolkit for penetration testing of identity verification and video conferencing systems. Supports face swap, image animation, and…
 alteredsecurity/disable-tamperprotection
A POC to disable TamperProtection and other Defender / MDE components
 sleepthegod/windows
Windows And Ways To Break It
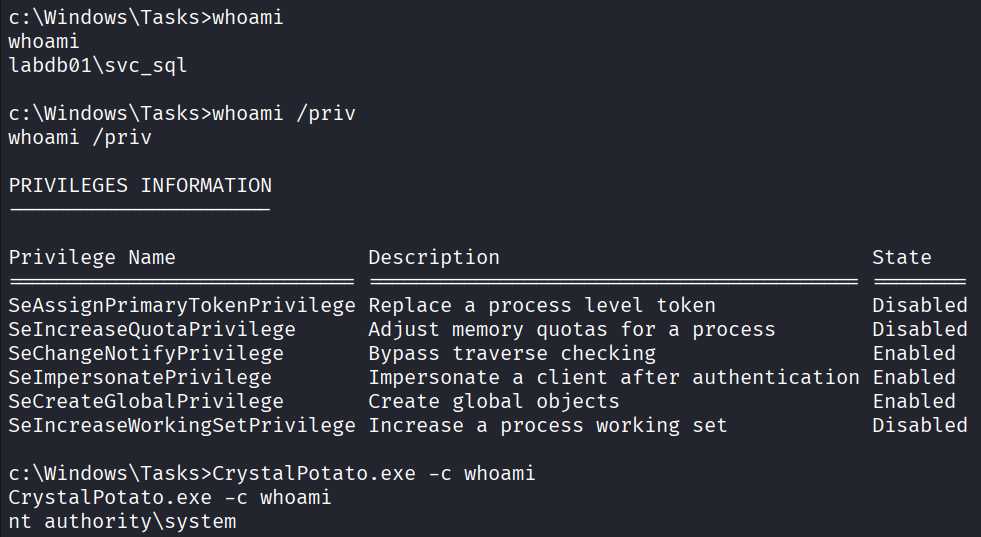 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 wh04m1001/diagtrackeop
Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.
 saadahla/pspersist
Dropping a powershell script at %HOMEPATH%\Documents\WindowsPowershell\ , that contains the implant's path , and whenever powershell process is…
 adpunisher/ownershipstealer
Command-line utility for Windows that enables SeTakeOwnershipPrivilege and modifies file ownership to the current user, granting access to otherwise…
 redcanaryco/atomictestharnesses
Public Repo for Atomic Test Harness
 gtworek/psbits
Simple (relatively) things allowing you to dig a bit deeper than usual.
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
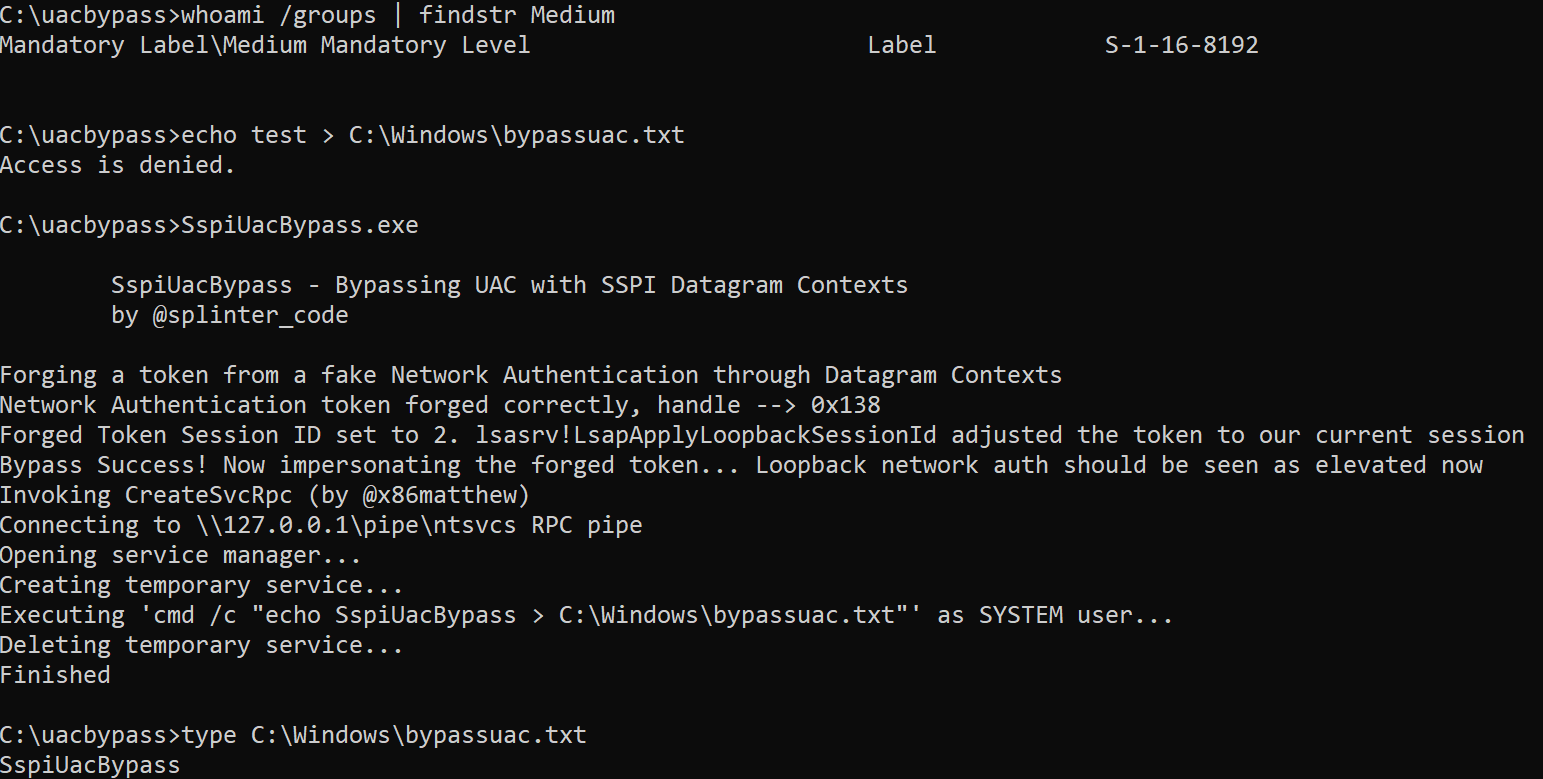 antoniococo/sspiuacbypass
Bypassing UAC with SSPI Datagram Contexts
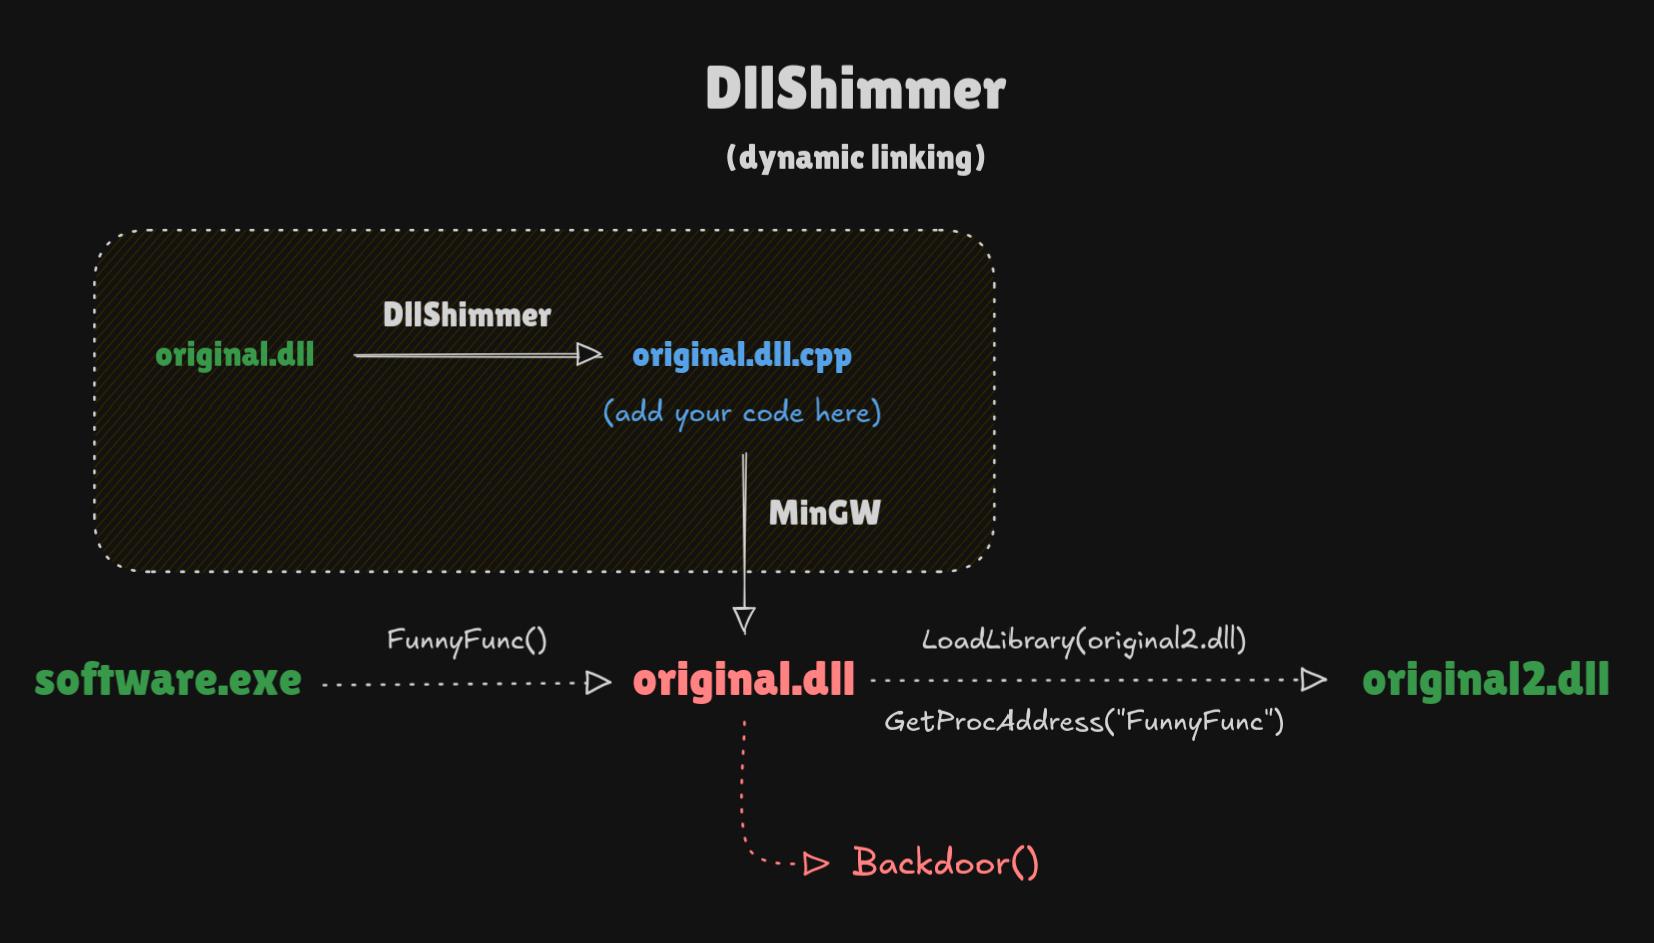 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 beichendream/printnotifypotato
PrintNotifyPotato
 deepinstinct/nofilter
Abuses Windows Filtering Platform to launch a console as NT AUTHORITY\SYSTEM or impersonate another logged-on user for privilege escalation during…