Anti-Virus-Evading-Payloads

During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…

During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…

C++ self-Injecting dropper based on various EDR evasion techniques.

A new simple and powerfull packer for malware

Application-scoped Windows network brownouts in native C and BOF form

Test your prompts, agents, and RAGs. Red teaming/pentesting/vulnerability scanning for AI. Compare performance of GPT, Claude, Gemini, DeepSeek, and…

Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.

HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…

Hands-on AI security lab platform with 50+ scenarios across prompt injection, agentic system exploitation, model manipulation, and MCP trust boundary…

A collection of awesome resources related AI security

PoC simulation of a critical CCSDS telecommand replay vulnerability in satellite command systems, demonstrating missing sequence-number validation…

PoC for Windows privilege escalation and code injection using OfficeClickToRun RPC and undocumented shim manipulation to inject DLLs into SYSTEM…

A POC to disable TamperProtection and other Defender / MDE components

Reproduces CVE-2026-21019 by manipulating node clock to force early Kubernetes CronJob execution; includes vulnerable YAML manifest and Python…

A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…

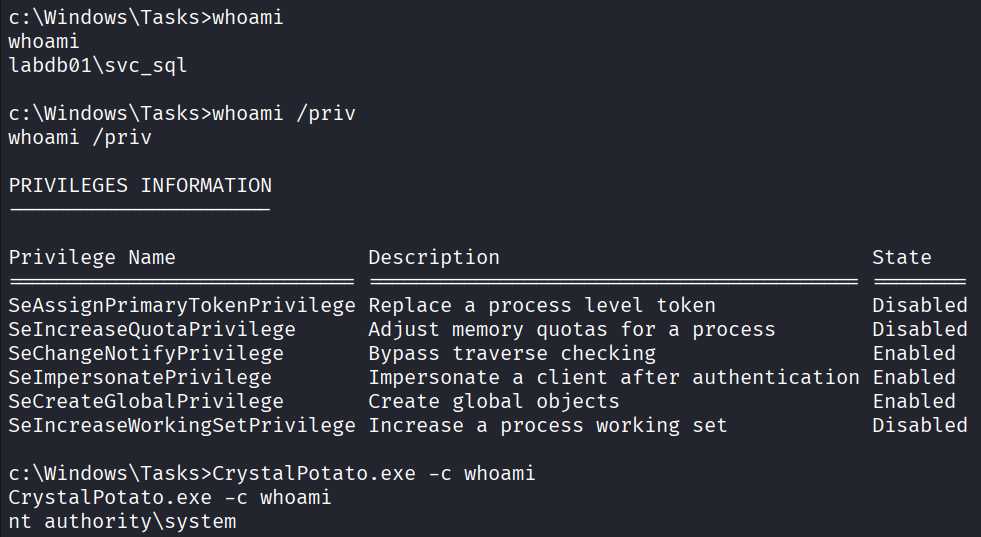
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…

Simple (relatively) things allowing you to dig a bit deeper than usual.

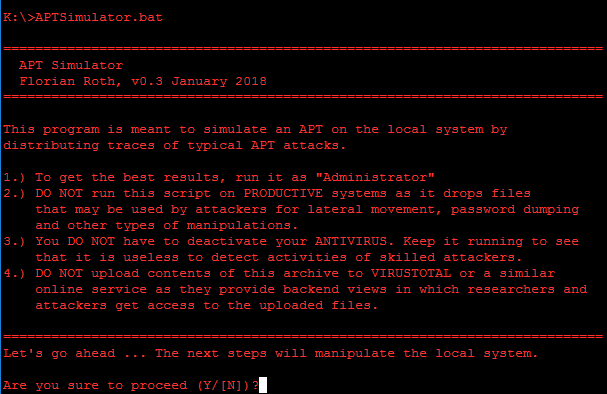
A toolset to make a system look as if it was the victim of an APT attack

A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.