
DutchOven
 loosehose/dutchoven
Application-scoped Windows network brownouts in native C and BOF form
adversarial-attackchaos-engineeringnetwork-security+2
232 months ago
loosehose/dutchovenApplication-scoped Windows network brownouts in native C and BOF form
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 wh04m1001/diagtrackeop
Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 owasp/ai-vulnerabilities-playground
Hands-on AI security lab platform with 50+ scenarios across prompt injection, agentic system exploitation, model manipulation, and MCP trust boundary…
 redcanaryco/chain-reactor
Generate Linux executables that simulate adversary behaviors and techniques for testing detection and response coverage. Consumes JSON for easy…
 togg53192-cmd/jailbreaks
Curated collection of LLM jailbreak prompts and bypass techniques, documenting adversarial inputs that circumvent AI model safety guardrails.
 george0papasotiriou/cve-2026-23010-ccsds-telecommand-replay-without-sequence-number
PoC simulation of a critical CCSDS telecommand replay vulnerability in satellite command systems, demonstrating missing sequence-number validation…
 deepinstinct/shimme
PoC for Windows privilege escalation and code injection using OfficeClickToRun RPC and undocumented shim manipulation to inject DLLs into SYSTEM…
 alteredsecurity/disable-tamperprotection
A POC to disable TamperProtection and other Defender / MDE components
 george0papasotiriou/cve-2026-21019-kubernetes-cronjob-suspended-execution-via-time-manipulation
Reproduces CVE-2026-21019 by manipulating node clock to force early Kubernetes CronJob execution; includes vulnerable YAML manifest and Python…
 toxy4ny/delirium-ai-safety-benchmark
A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…
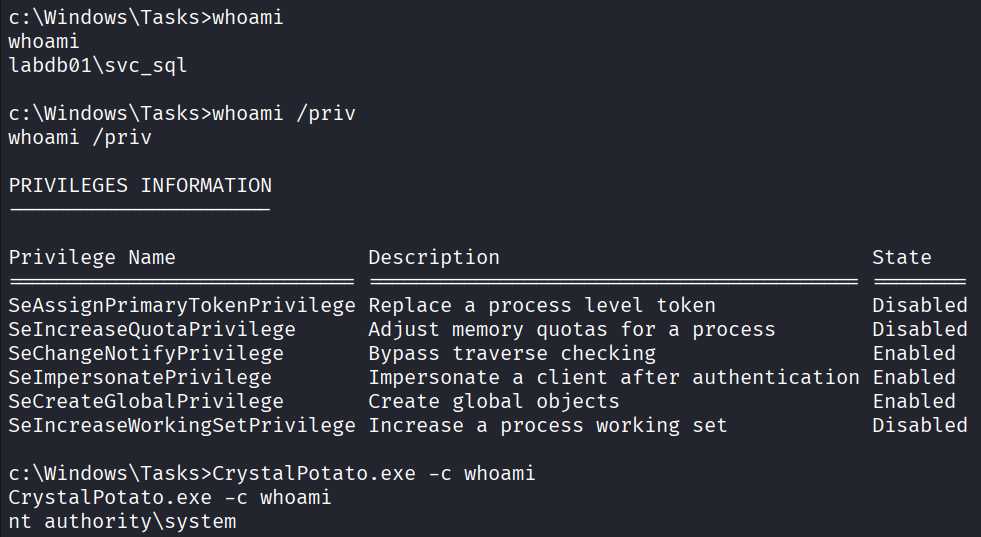 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 suels-group/beyond_asr
Research code for measuring jailbreak attack success rates (ASR and stepwise ASR) against LLMs, with implementations of attacks such as GCG and…
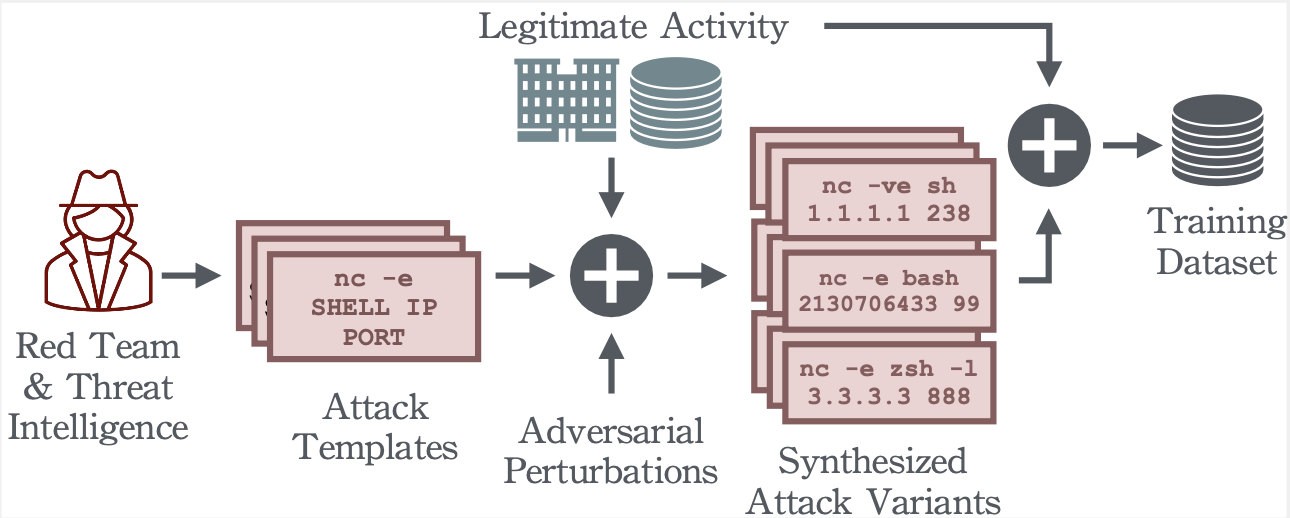 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 trusted-ai/adversarial-robustness-toolbox
Python library for adversarial machine learning security, enabling red and blue teams to run evasion, poisoning, extraction, and inference attacks…
 funnywolf/viper
Adversary simulation and Red teaming platform with AI
 endgameinc/rta
Scripted framework for simulating over 50 MITRE ATT&CK techniques to test blue team detection capabilities. Includes Python scripts and a compiled…