
brawl-public-game-001
 mitre/brawl-public-game-001
Data from a BRAWL Automated Adversary Emulation Exercise
adversarial-attackcloud-securitydigital-forensics+7
215
mitre/brawl-public-game-001Data from a BRAWL Automated Adversary Emulation Exercise
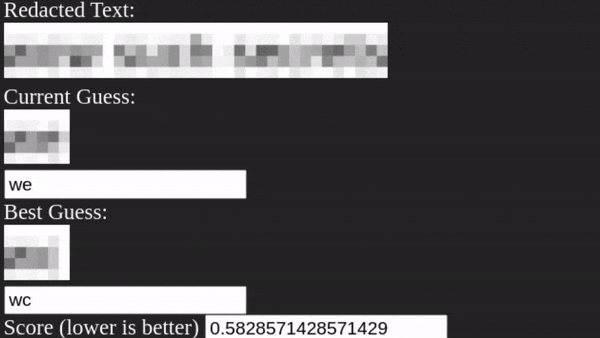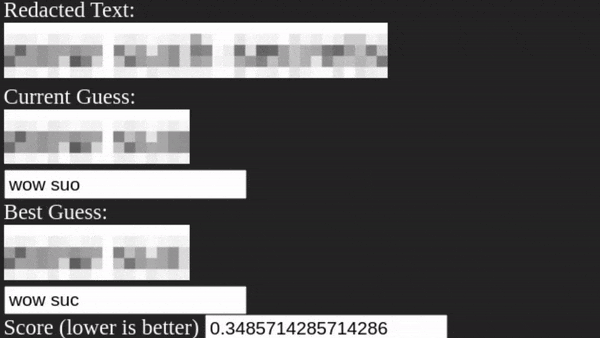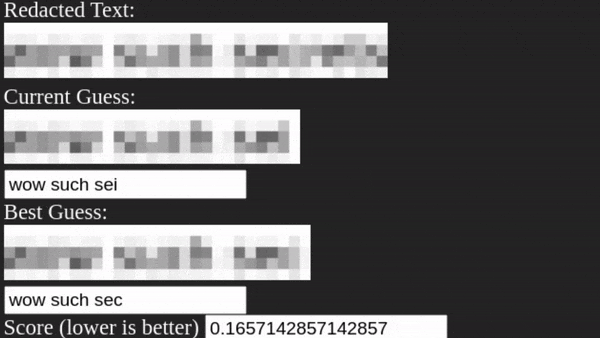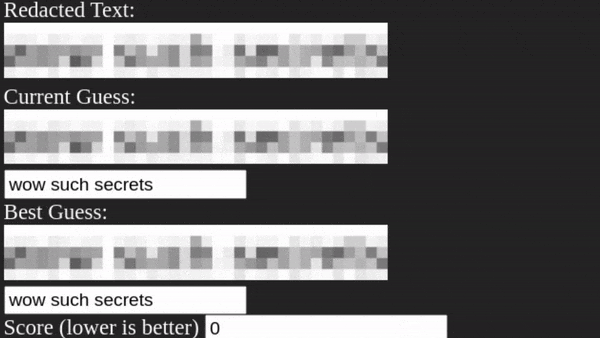 bishopfox/unredacter
Never ever ever use pixelation as a redaction technique
 mthcht/purpleteam
Purpleteam scripts simulation & Detection - trigger events for SOC detections
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…