

linux_injector
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
adversarial-attackpayload-developmentpenetration-testing+3
296
namazso/linux_injectorA simple ptrace-less shared library injector for x64 Linux
 redcanaryco/atomictestharnesses
Public Repo for Atomic Test Harness
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 winscripting/uac-bypass
PowerShell proof-of-concept that bypasses Windows User Account Control (UAC) to elevate privileges, intended for authorized penetration testing and…
 gtworek/psbits
Simple (relatively) things allowing you to dig a bit deeper than usual.
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
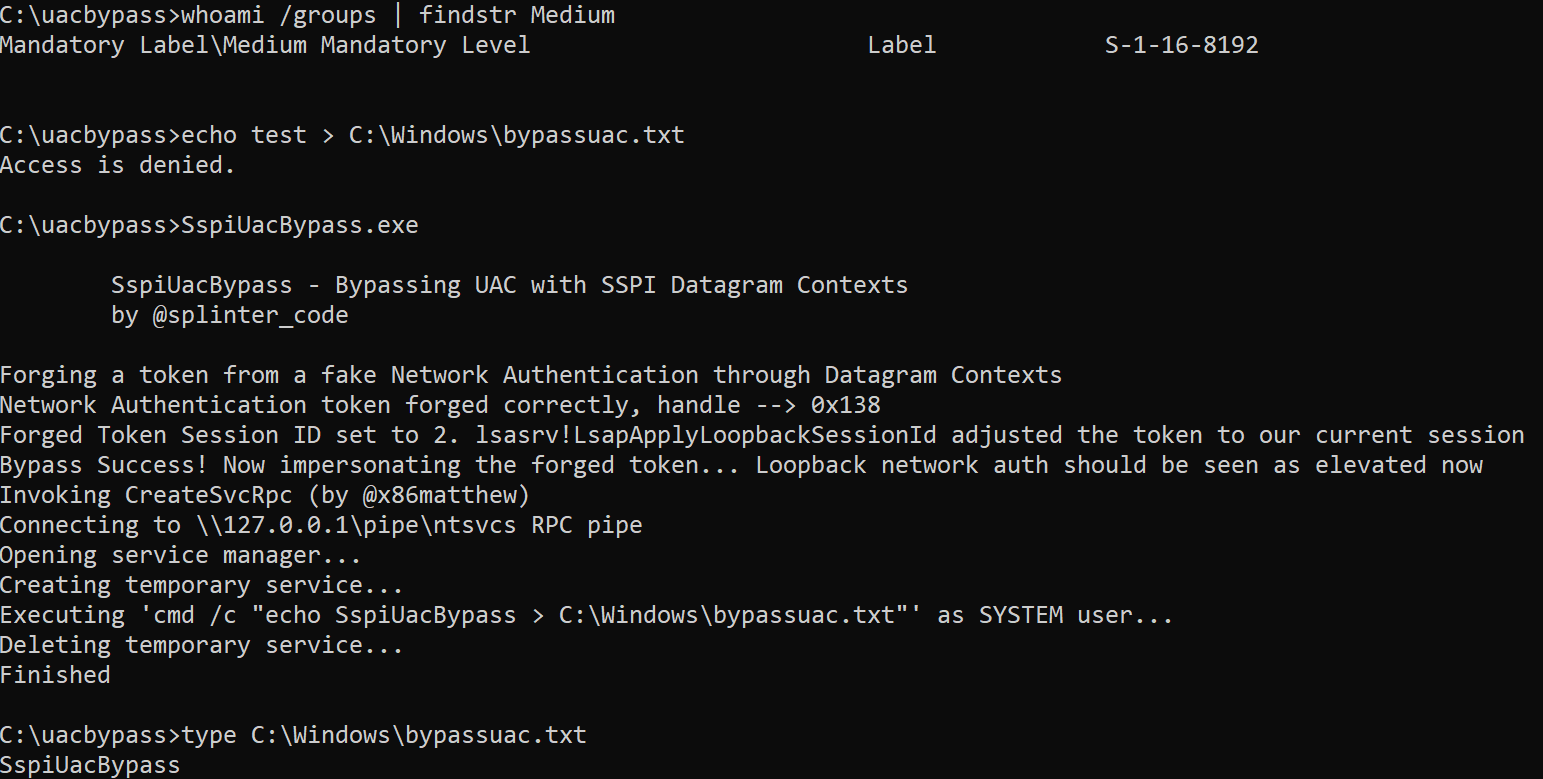 antoniococo/sspiuacbypass
Bypassing UAC with SSPI Datagram Contexts
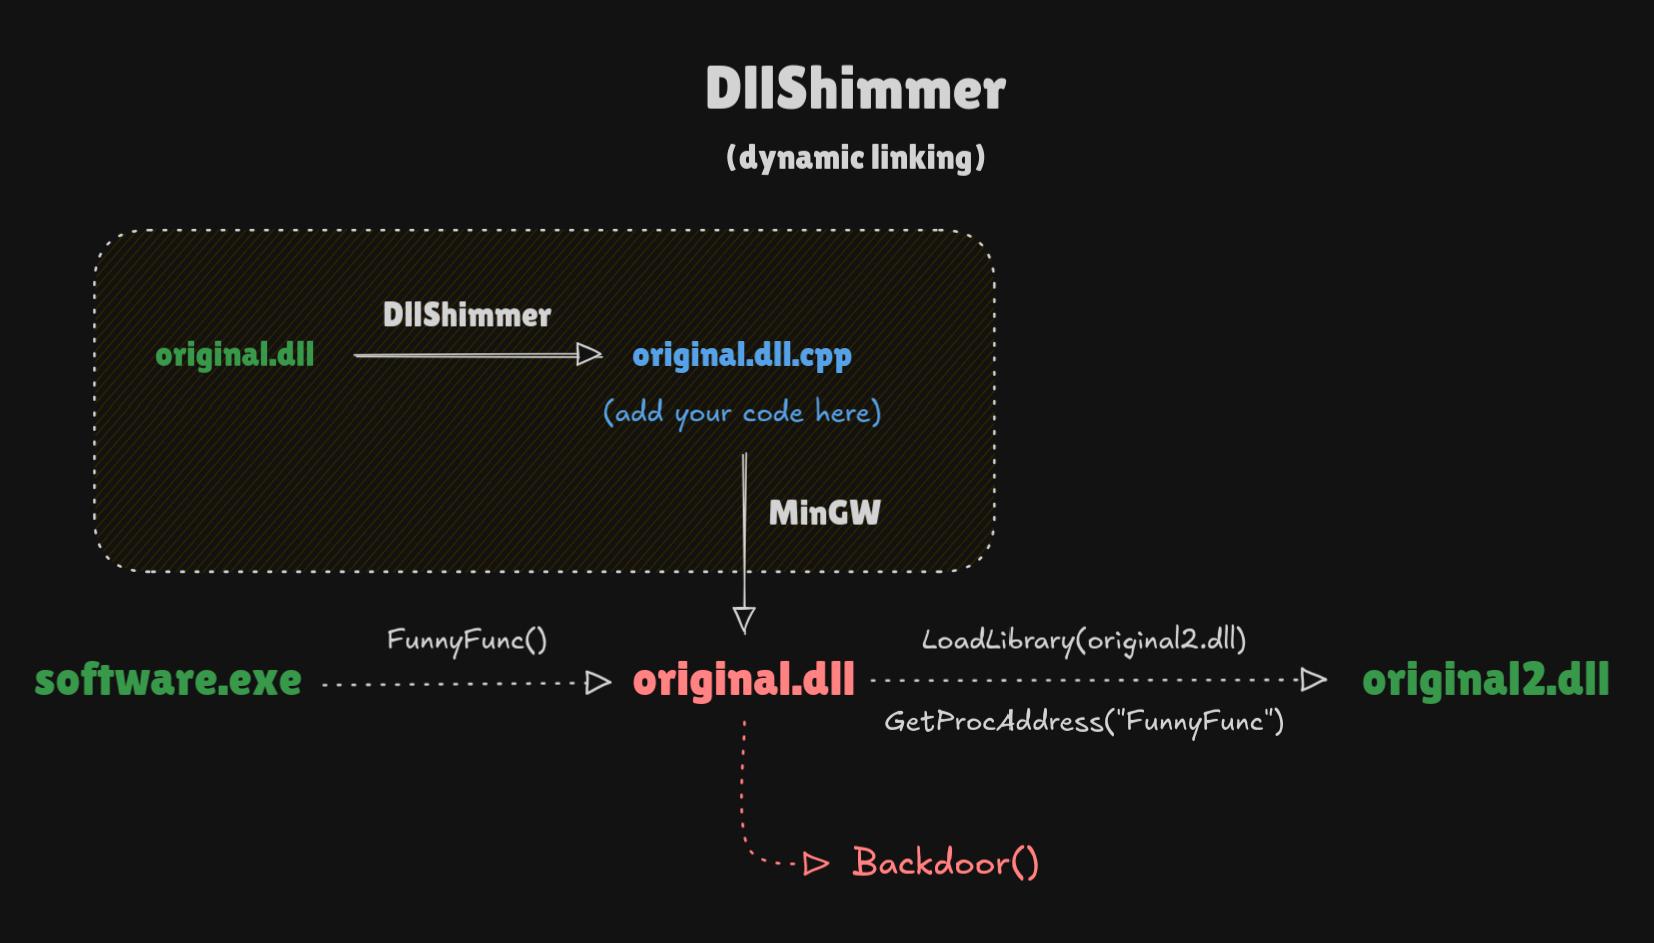 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
 beichendream/printnotifypotato
PrintNotifyPotato
 deepinstinct/nofilter
Abuses Windows Filtering Platform to launch a console as NT AUTHORITY\SYSTEM or impersonate another logged-on user for privilege escalation during…
 alteredsecurity/disable-tamperprotection
A POC to disable TamperProtection and other Defender / MDE components
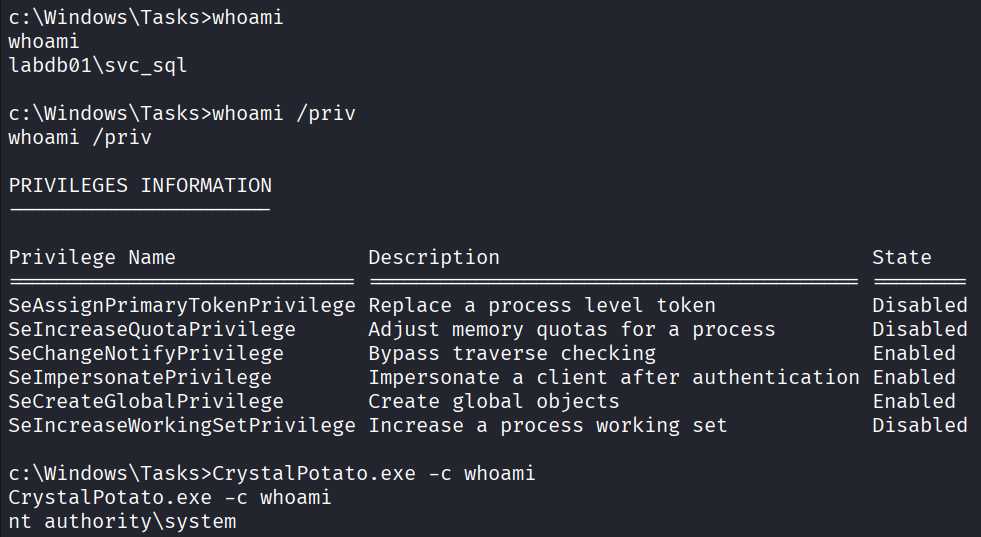 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 sleepthegod/windows
Windows And Ways To Break It
 vozzie/uacscript
Windows 7 UAC Bypass Vulnerability in the Windows Script Host
 kudaes/bin-finder
Detect EDR's exceptions by inspecting processes' loaded modules
 wh04m1001/diagtrackeop
Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.
 saadahla/pspersist
Dropping a powershell script at %HOMEPATH%\Documents\WindowsPowershell\ , that contains the implant's path , and whenever powershell process is…