
RingReaper
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
adversarial-attackcommand-and-controldata-exfiltration+5
385
matheuzsecurity/ringreaperLinux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 redcanaryco/chain-reactor
Generate Linux executables that simulate adversary behaviors and techniques for testing detection and response coverage. Consumes JSON for easy…
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…
 mthcht/purpleteam
Purpleteam scripts simulation & Detection - trigger events for SOC detections
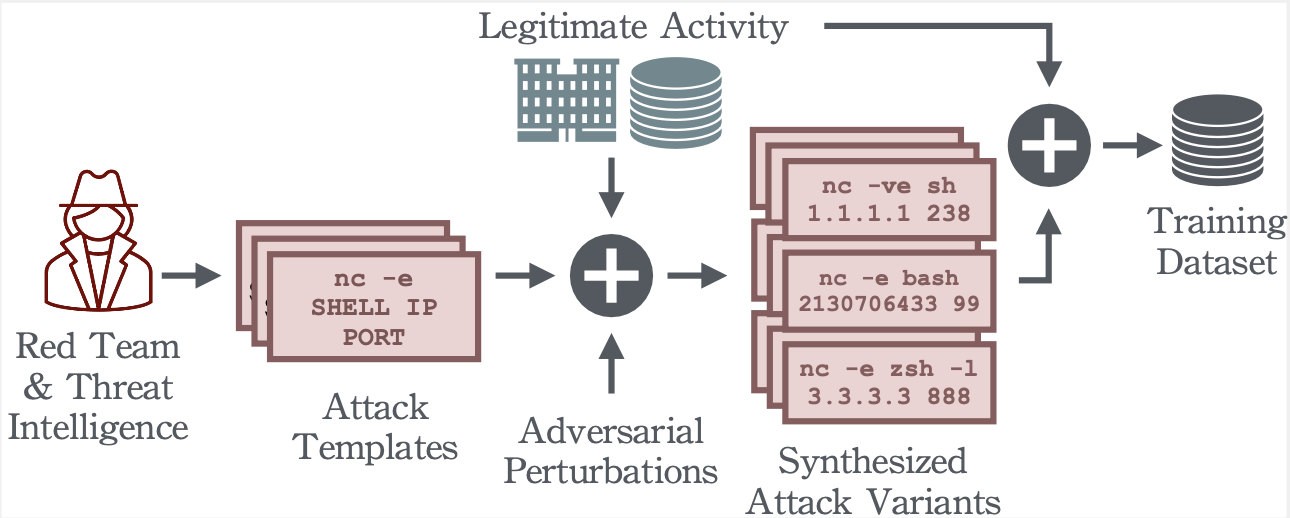 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 bishopfox/sliver
Adversary Emulation Framework
 trusted-ai/adversarial-robustness-toolbox
Python library for adversarial machine learning security, enabling red and blue teams to run evasion, poisoning, extraction, and inference attacks…
 funnywolf/viper
Adversary simulation and Red teaming platform with AI
 endgameinc/rta
Scripted framework for simulating over 50 MITRE ATT&CK techniques to test blue team detection capabilities. Includes Python scripts and a compiled…
 barre/privaxy
Privaxy is the next generation tracker and advertisement blocker. It blocks ads and trackers by MITMing HTTP(s) traffic. Also check out my new…
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 doctoreww/evilfonttool
A font-based deception tool for red teaming, security research, and whatever else.
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
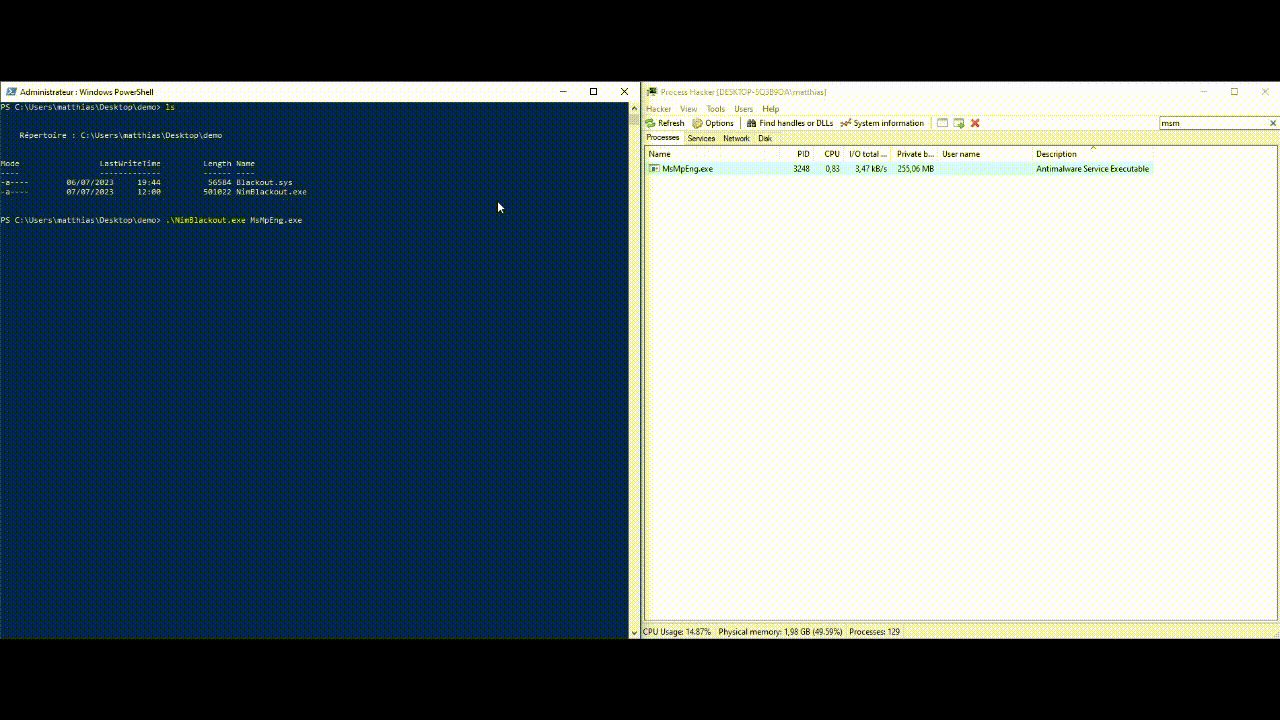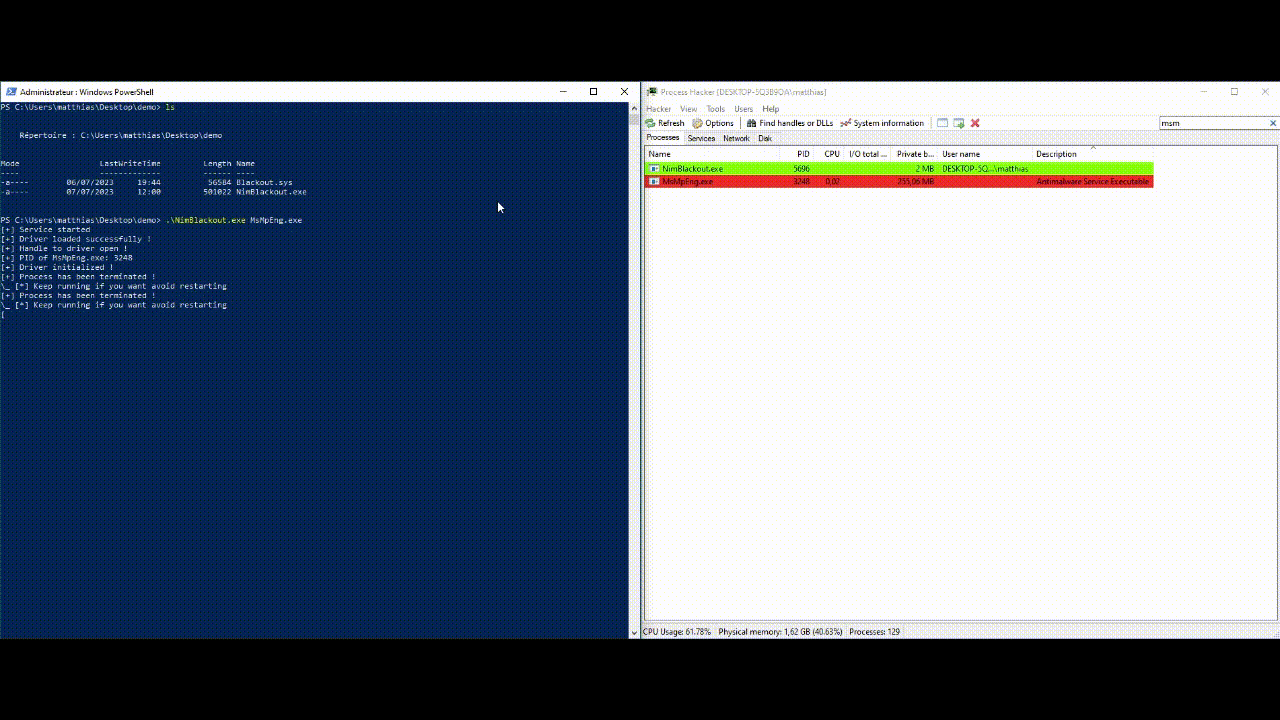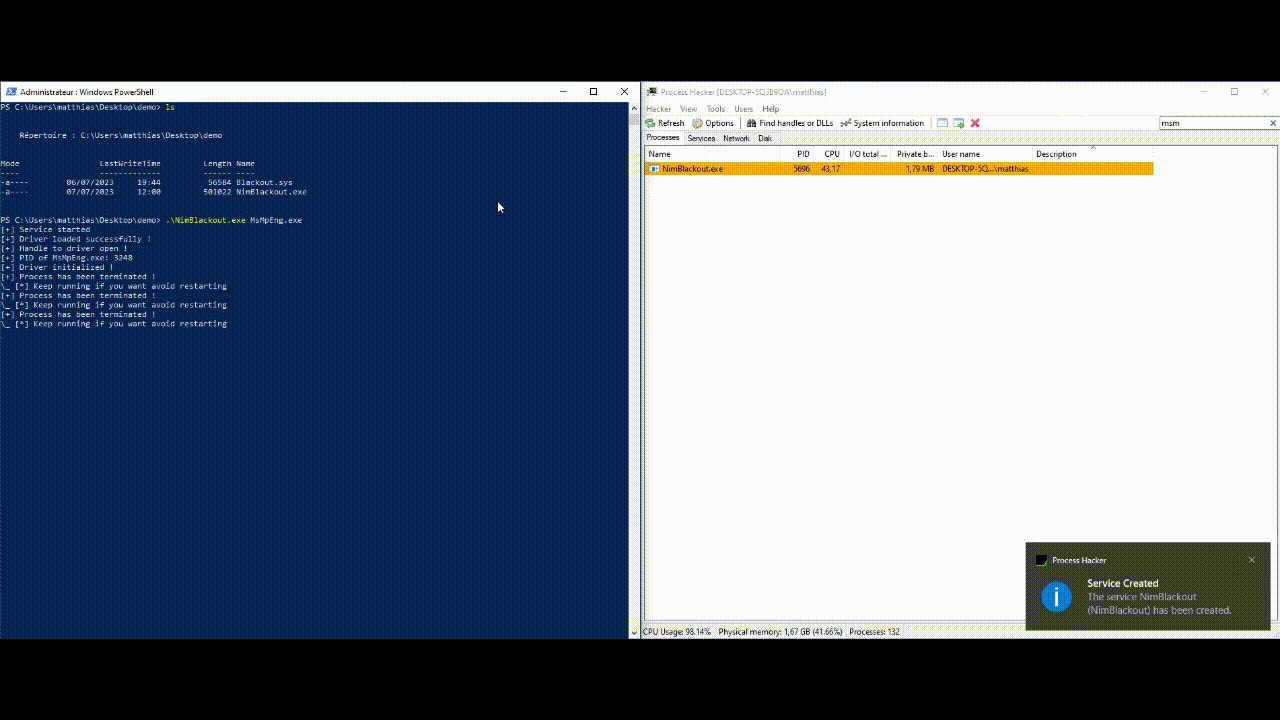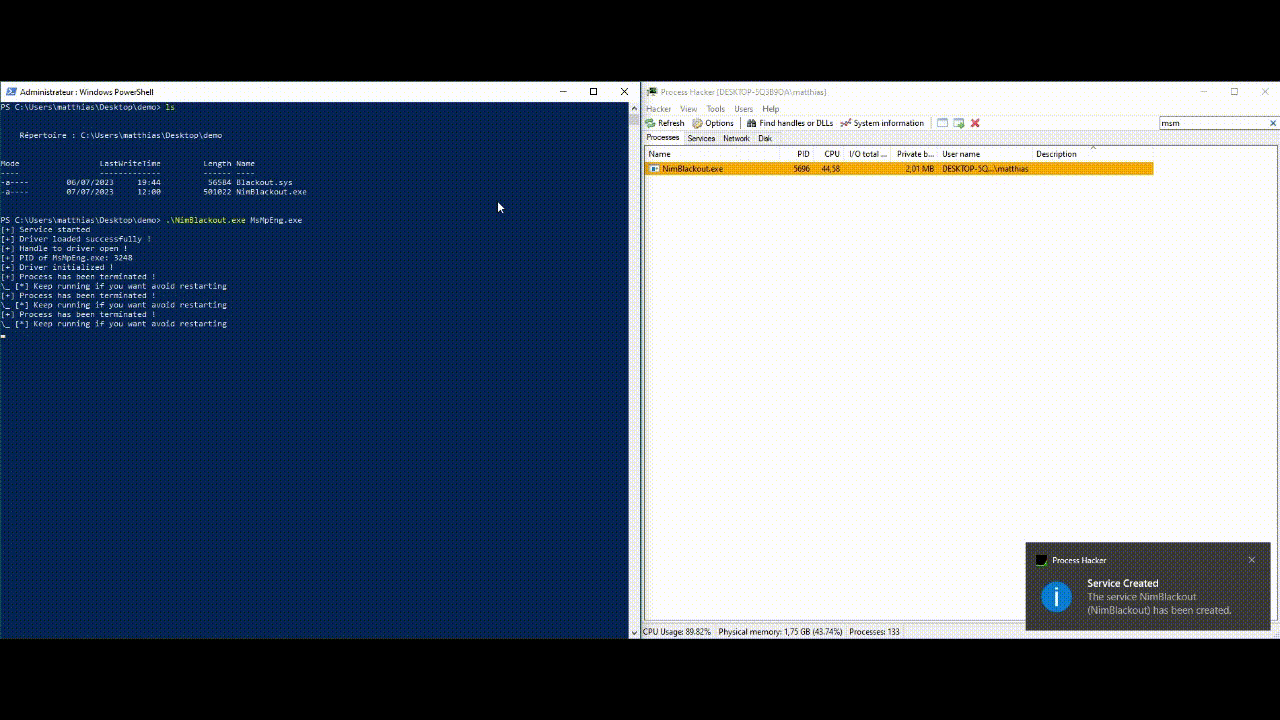 helixo32/nimblackout
Kill AV/EDR leveraging BYOVD attack
 redcanaryco/atomictestharnesses
Public Repo for Atomic Test Harness
 jwillyamz/ezemu
See adversary, do adversary: Simple execution of commands for defensive tuning/research (now with more ELF on the shelf)