Windows-SignedBinary

Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…

Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…

Python library for adversarial machine learning security, enabling red and blue teams to run evasion, poisoning, extraction, and inference attacks…

An adversarial example library for constructing attacks, building defenses, and benchmarking both

:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud

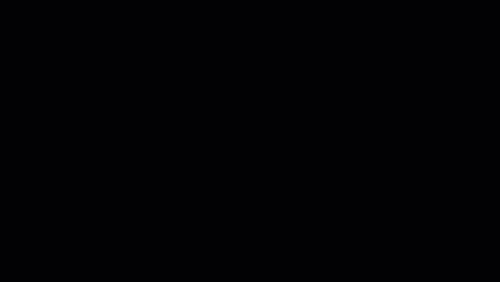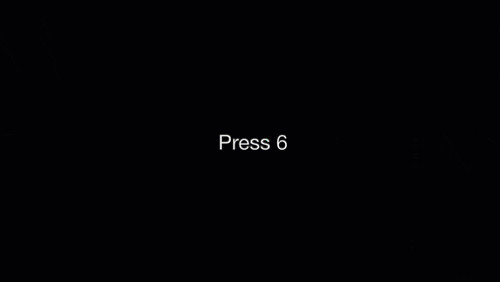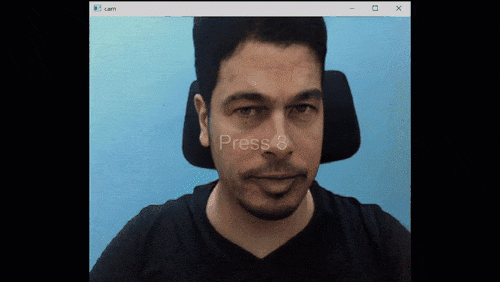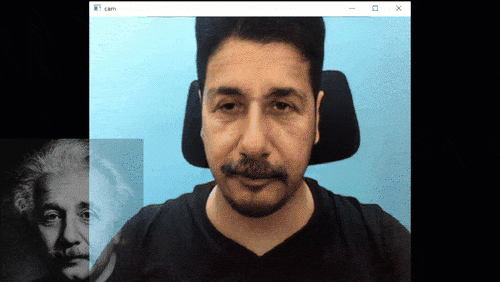
Real-time deepfake toolkit for penetration testing of identity verification and video conferencing systems. Supports face swap, image animation, and…

PoCs and tools for investigation of Windows process execution techniques

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

image scaling attacks for multi-modal prompt injection

A security scanner for your LLM agentic workflows

Metasploit for machine learning.

A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…

Train, evaluate, and explore neural networks with built-in adversarial robustness tools, including PGD attacks, adversarial training, and robust…

RedCloudOS is a Cloud Adversary Simulation Operating System for Red Teams to assess the Cloud Security of Leading Cloud Service Providers (CSPs)

HookChain: A new perspective for Bypassing EDR Solutions

Evasion kit for Cobalt Strike

A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…

A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…

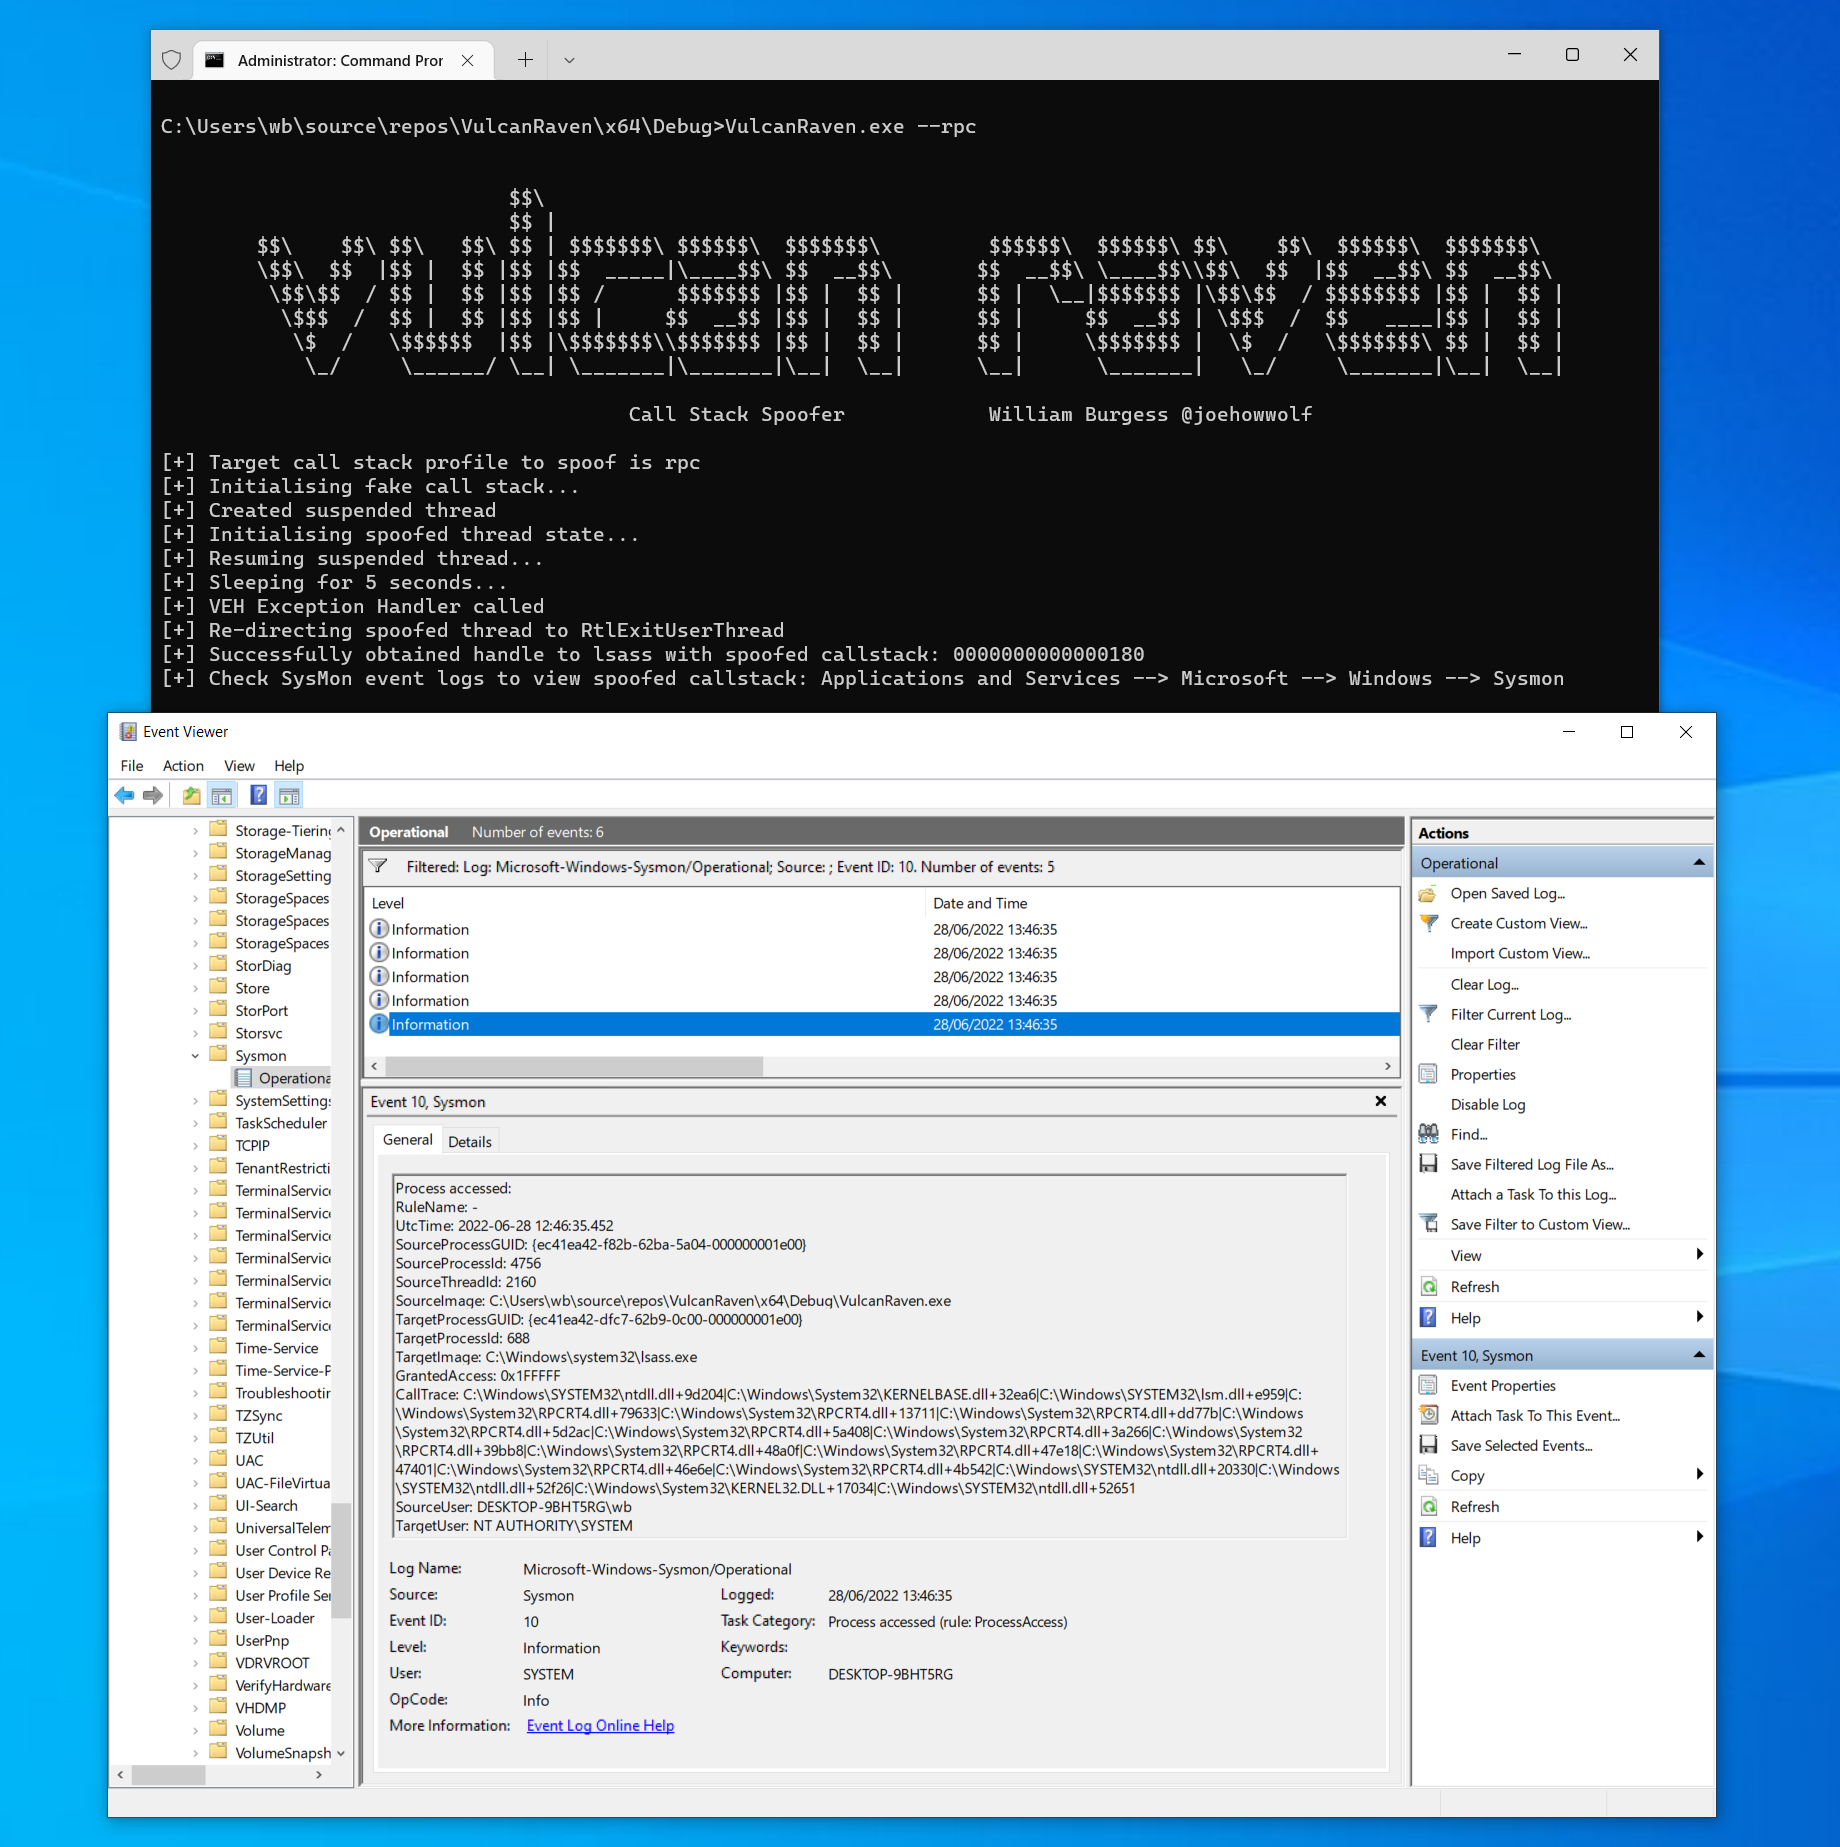
A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)