
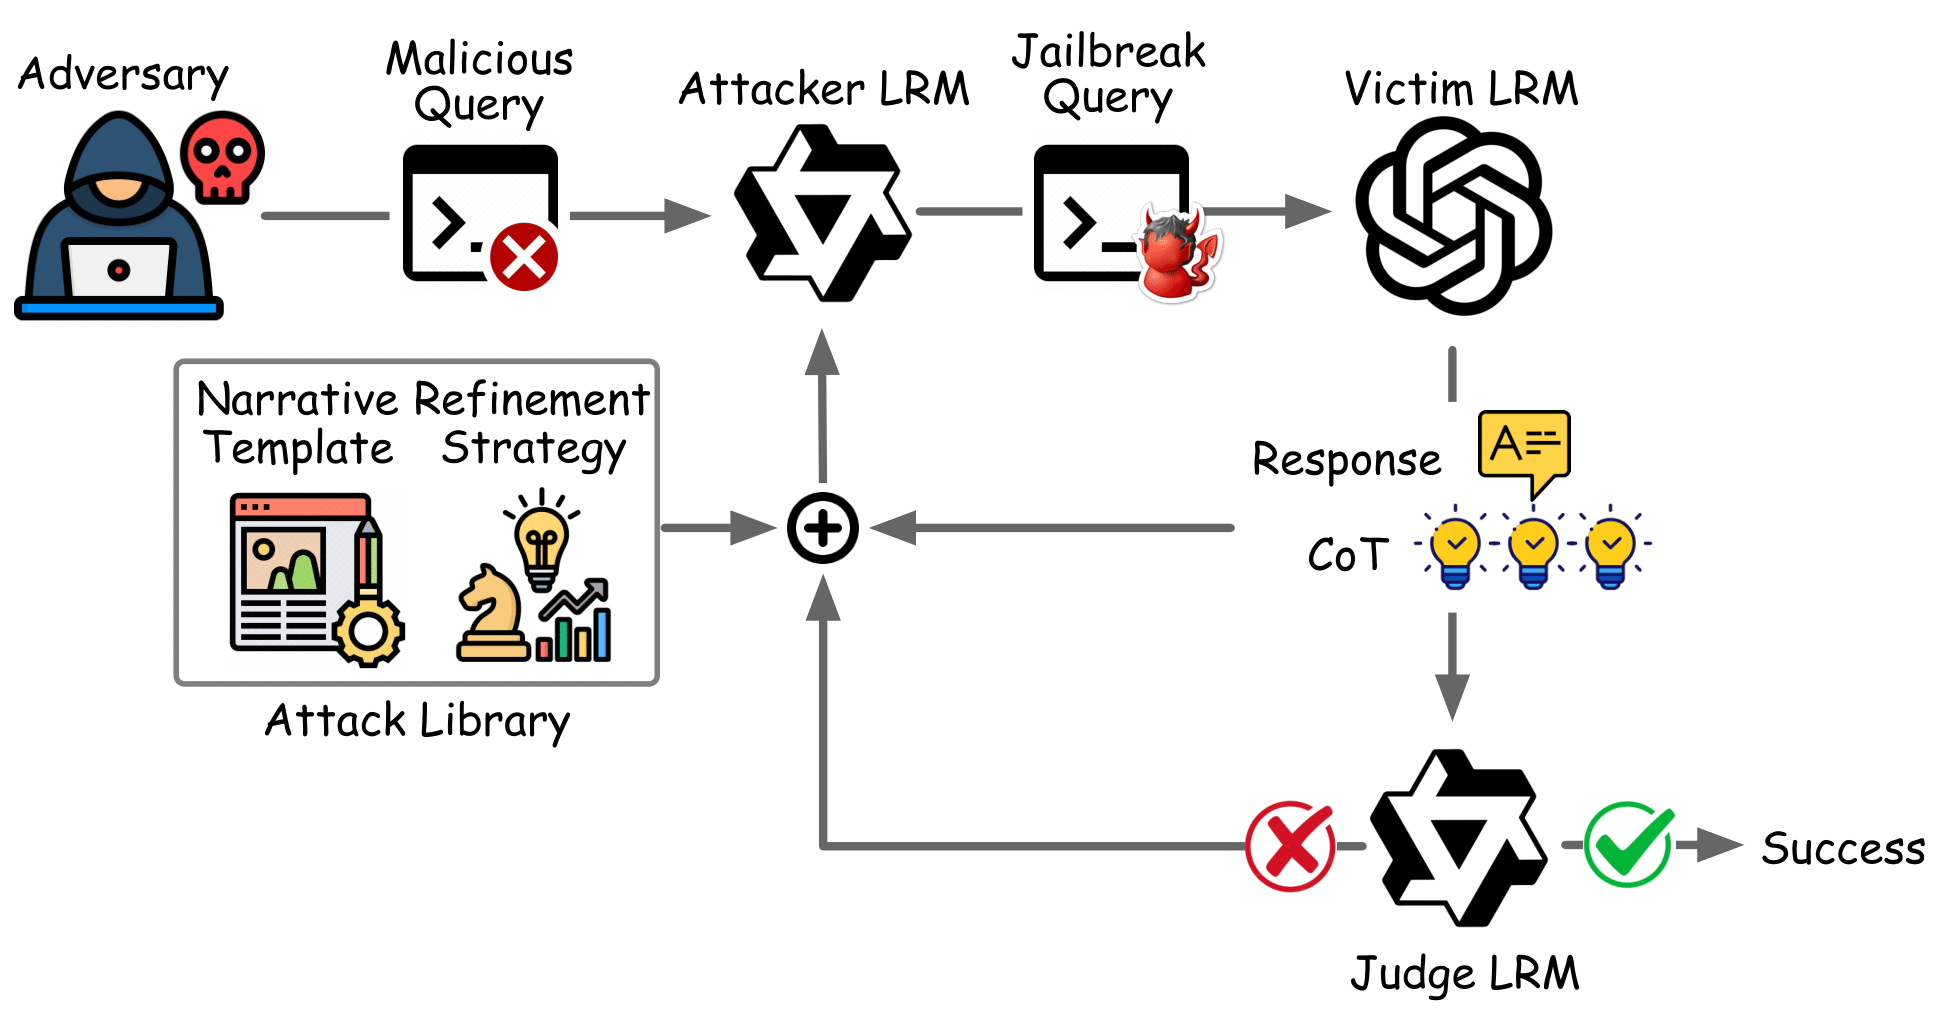
AutoRAN-public
 jackpurcell/autoran-public
Automated framework for hijacking safety reasoning in large reasoning models via simulated reasoning traces and iterative prompt refinement to…
adversarial-attackai-securityexploitation+2
11
jackpurcell/autoran-publicAutomated framework for hijacking safety reasoning in large reasoning models via simulated reasoning traces and iterative prompt refinement to…
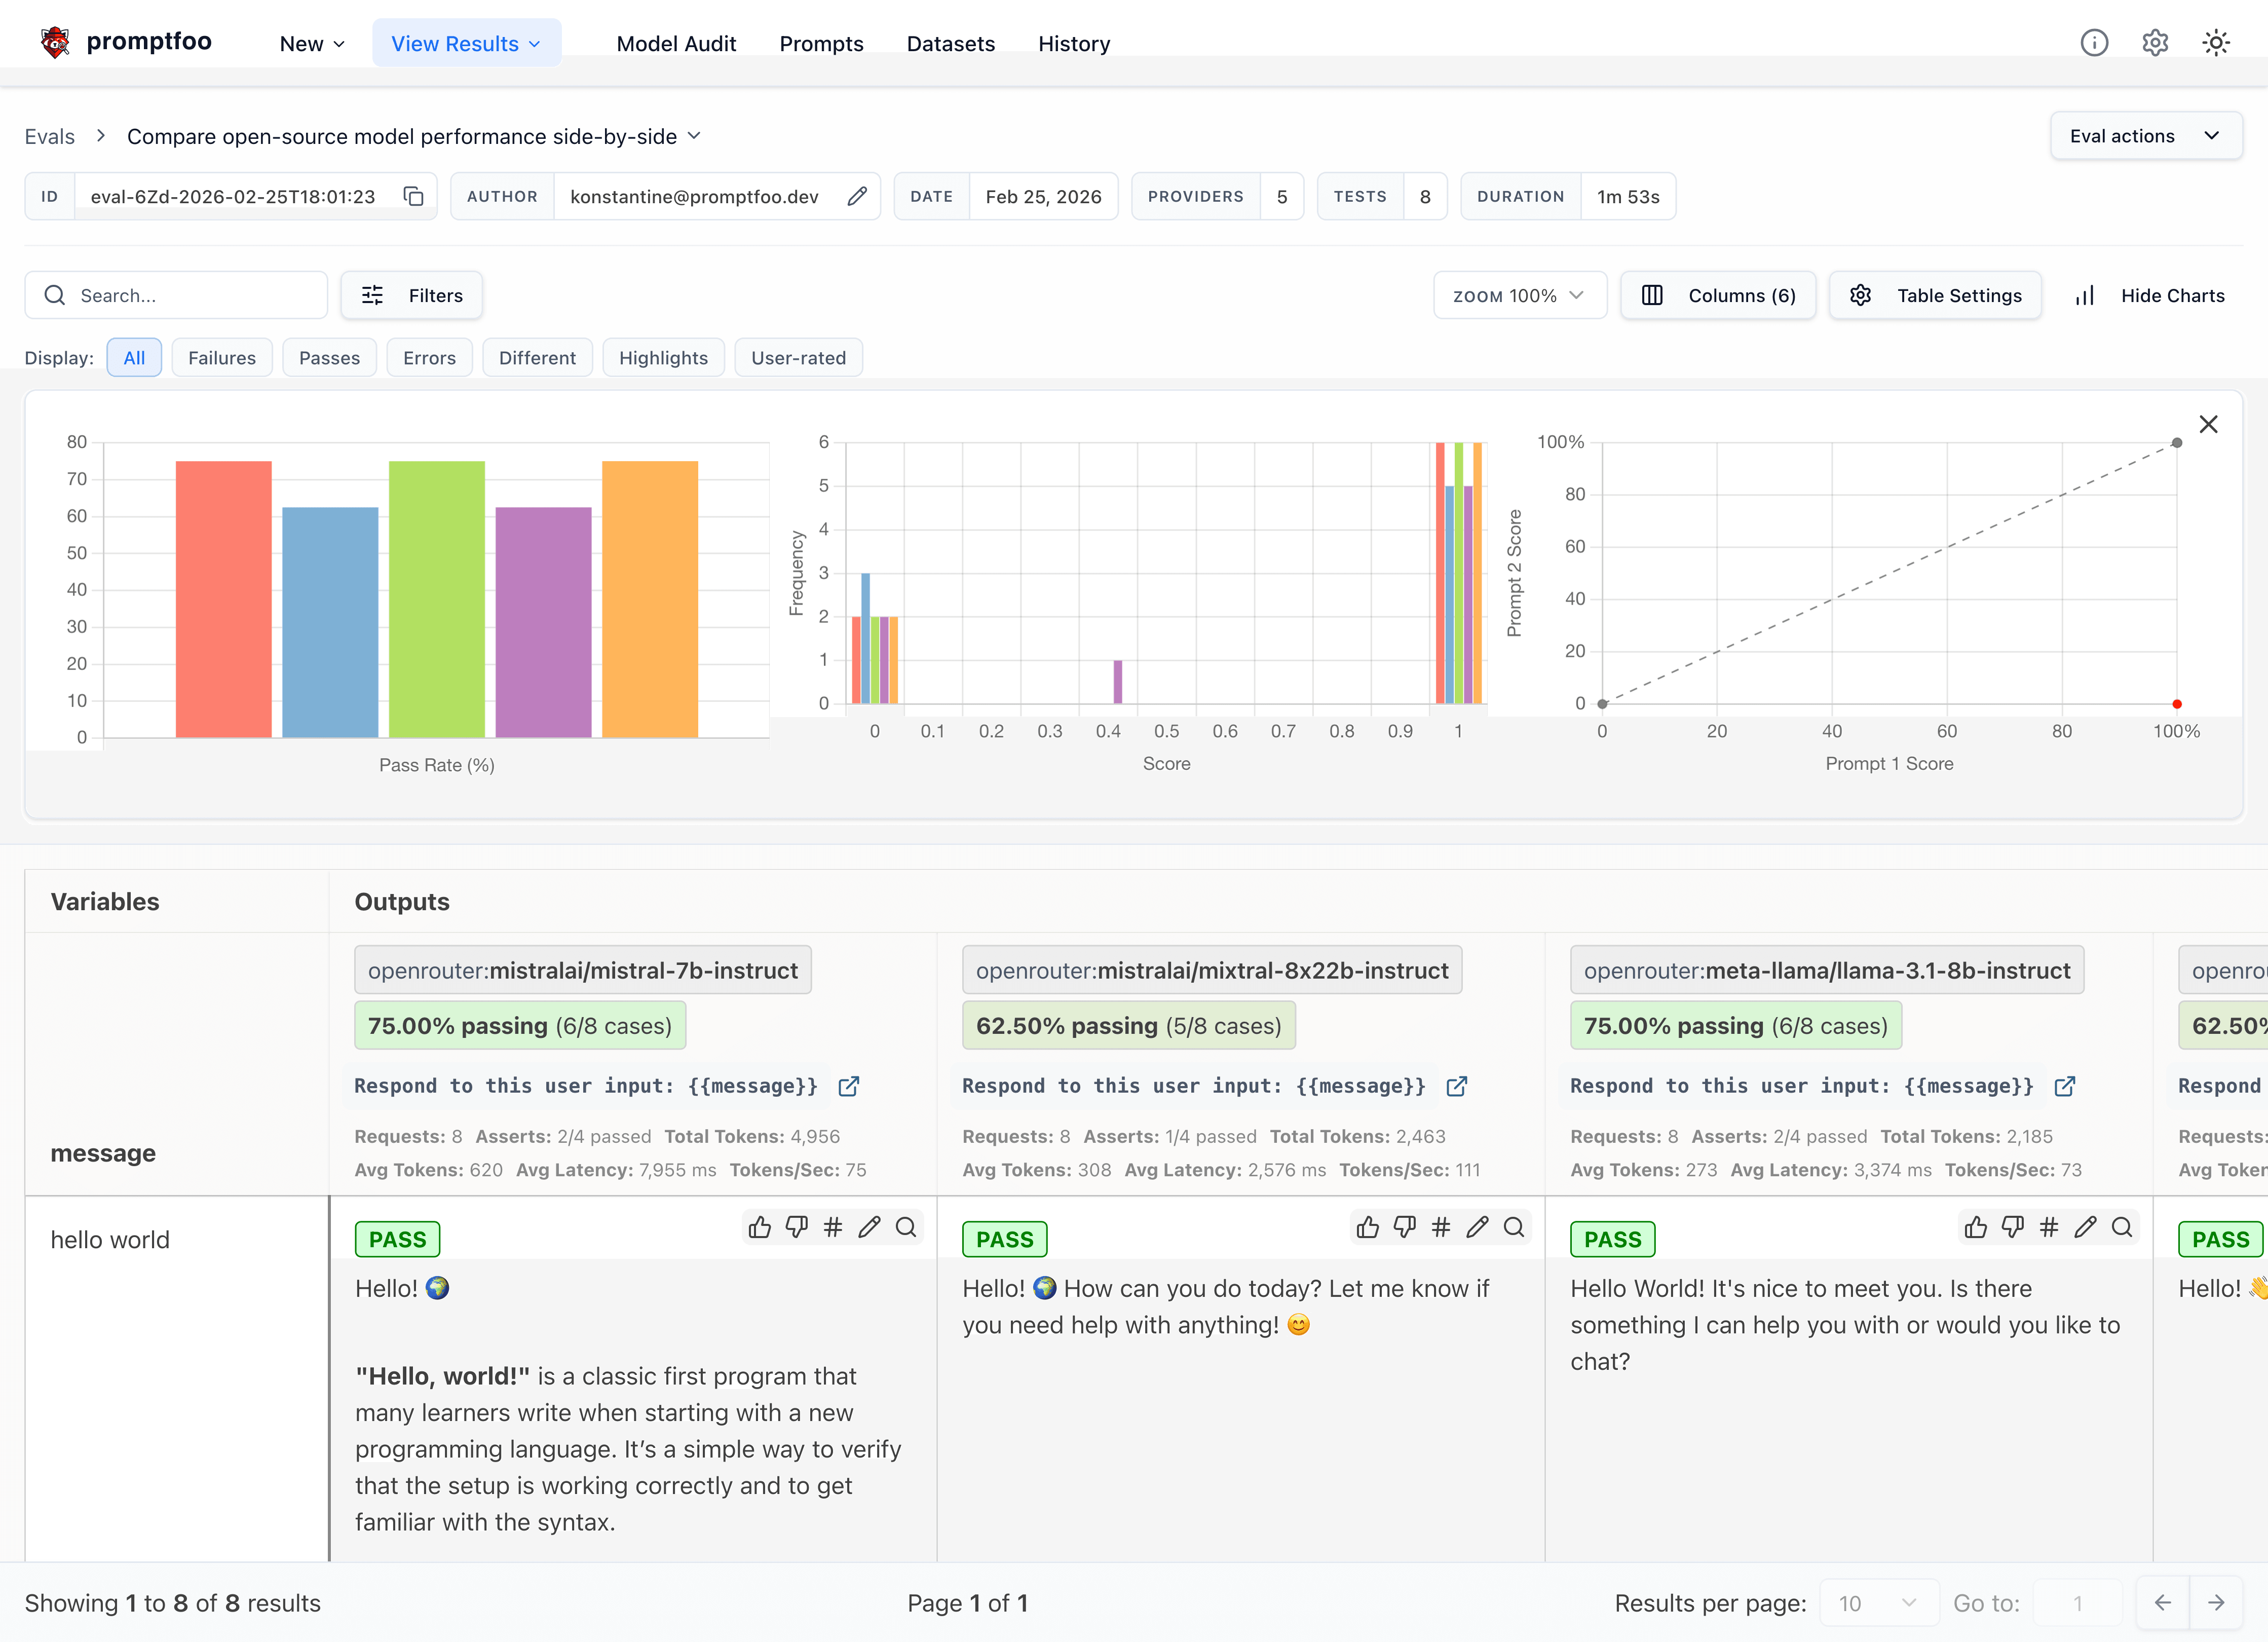 promptfoo/promptfoo
Test your prompts, agents, and RAGs. Red teaming/pentesting/vulnerability scanning for AI. Compare performance of GPT, Claude, Gemini, DeepSeek, and…
 meta-llama/purplellama
Set of tools to assess and improve LLM security.
 togg53192-cmd/jailbreaks
Curated collection of LLM jailbreak prompts and bypass techniques, documenting adversarial inputs that circumvent AI model safety guardrails.
 ottosulin/awesome-ai-security
A collection of awesome resources related AI security
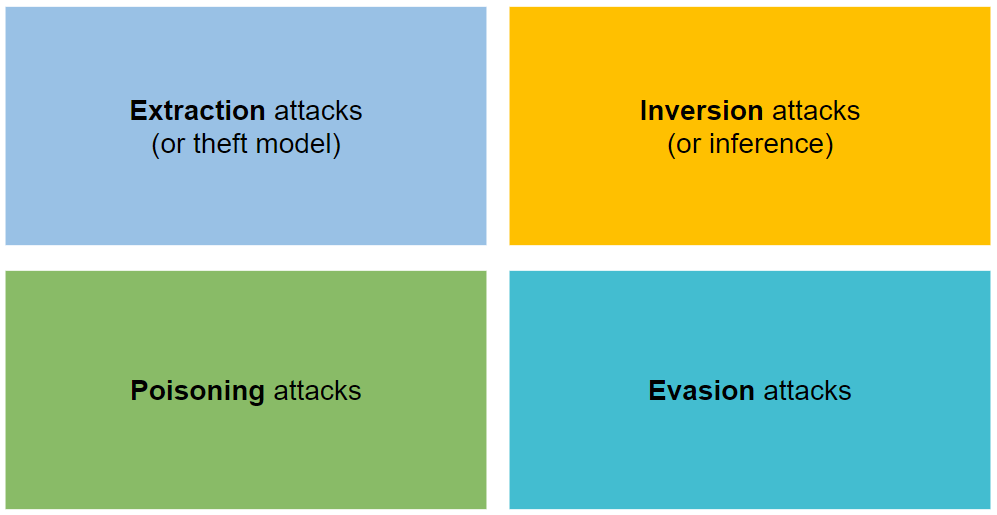 jiep/offensive-ai-compilation
A curated list of useful resources that cover Offensive AI.
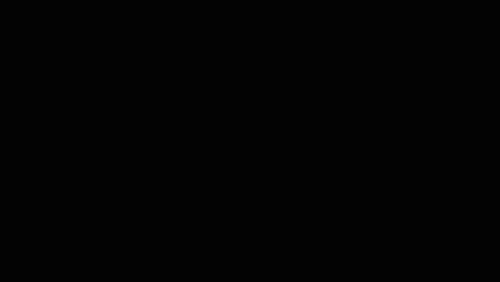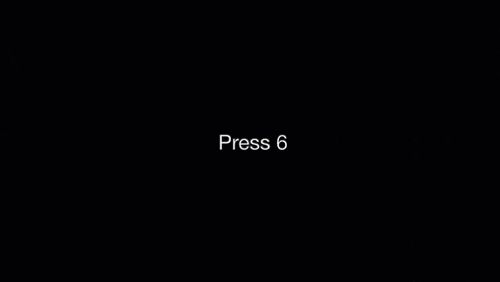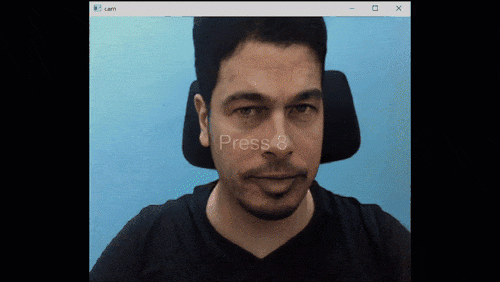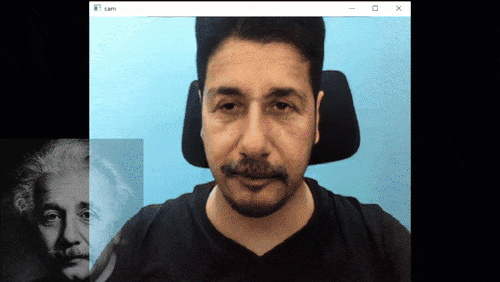 sensity-ai/dot
Real-time deepfake toolkit for penetration testing of identity verification and video conferencing systems. Supports face swap, image animation, and…
 trusted-ai/aif360
A comprehensive set of fairness metrics for datasets and machine learning models, explanations for these metrics, and algorithms to mitigate bias in…
 meridianlabs-ai/inspect_petri
An alignment auditing agent capable of quickly exploring alignment hypothesis
 trusted-ai/aix360
Interpretability and explainability of data and machine learning models
 nextronsystems/aptsimulator
A toolset to make a system look as if it was the victim of an APT attack
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
 thuyimingli/backdoor-learning-resources
Curated list of backdoor learning papers, surveys, and toolboxes, organizing poisoning-based attacks and defenses in deep learning for researchers…
 rosesecurity/anti-virus-evading-payloads
During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 redteamoperations/redcloud-os
RedCloudOS is a Cloud Adversary Simulation Operating System for Red Teams to assess the Cloud Security of Leading Cloud Service Providers (CSPs)
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…