
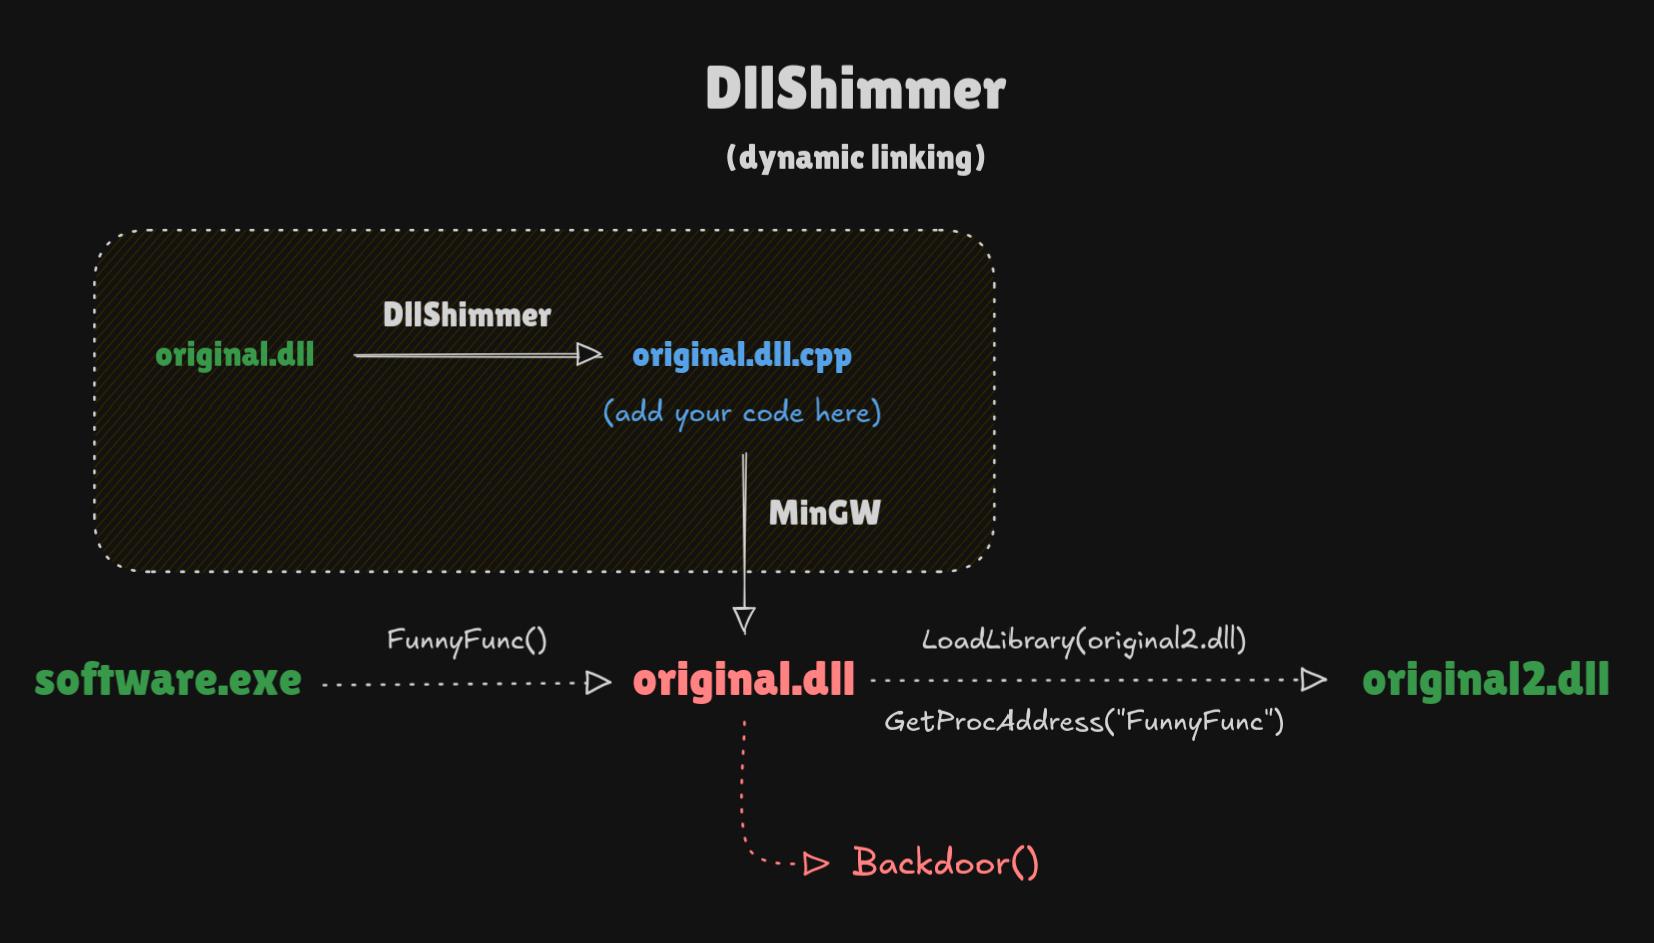
DllShimmer
 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
adversarial-attackpayload-developmentpenetration-testing+2
7631 year ago
print3m/dllshimmerWeaponize DLL hijacking easily. Backdoor any function in any DLL.
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 thiagopeixoto/winsos-poc
A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.
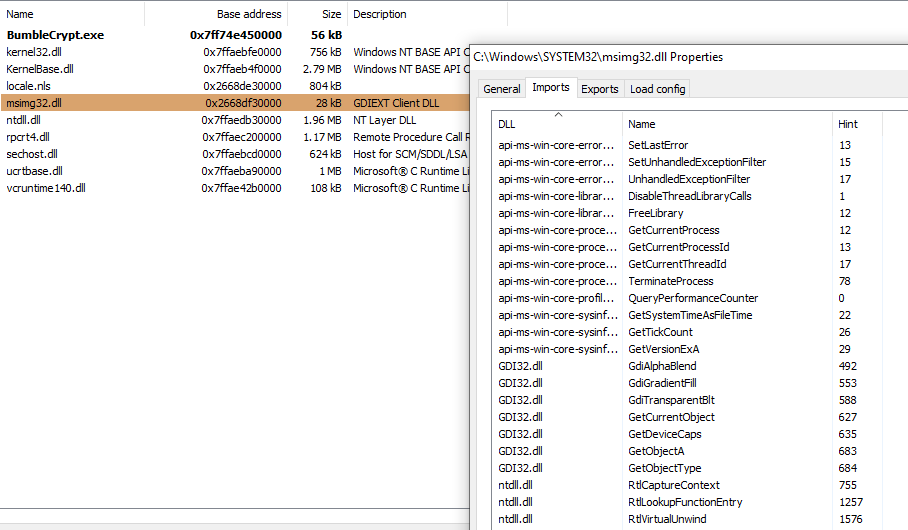 knight0x07/bumblecrypt
A Bumblebee-inspired Crypter
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
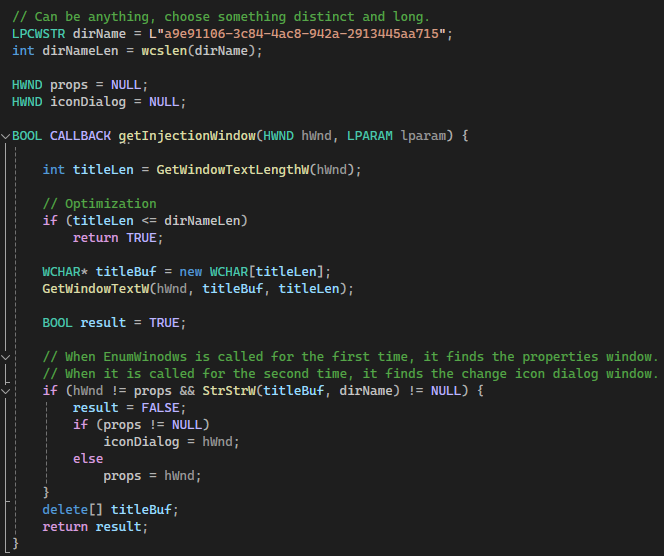 d419h/iconjector
Inject DLLs into the explorer process using icons
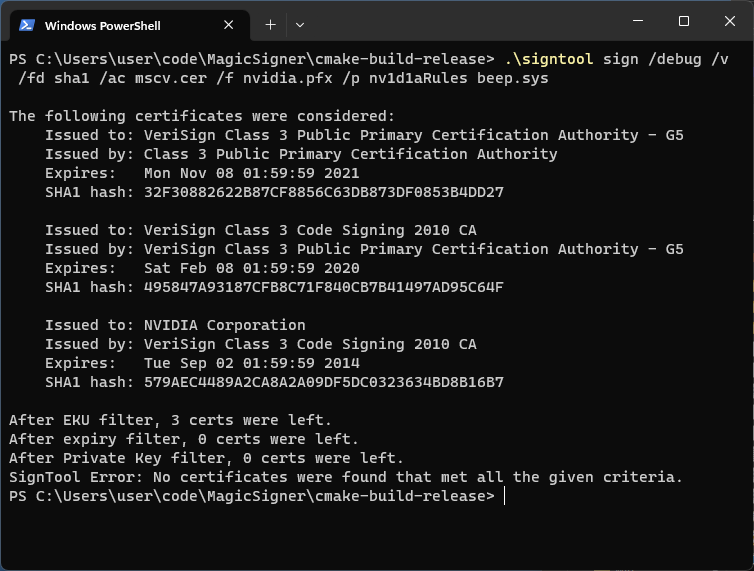 namazso/magicsigner
Signtool for expired certificates
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post