

badsuccessor
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
adversarial-attackexploitationinformation-gathering+7
122
cybrly/badsuccessorExploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
 george0papasotiriou/cve-2026-22003-redis-lua-sandbox-escape-via-debug.sethook-
Proof-of-concept exploit for CVE-2026-22003 demonstrating Redis Lua sandbox escape via debug.sethook to execute arbitrary system commands.
 davidrxchester/cve-2026-5817
Docker Container-to-Host Remote Code Execution POC via vllm-metal trust_remote_code=True
 imabee101/cve-2023-44487
PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…
 marcgoam/cve-2026-54121-certighost
CVE-2026-54121 (Certighost) AD CS DC-impersonation PoC. Patched SAN handling + MAQ-safe account reuse.
 lxxexxbxx/cve-2026-44578
Proof-of-concept exploit for CVE-2026-44578 that reproduces the vulnerable condition, enabling security researchers to validate affected systems and…
 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 gmh5225/awesome-ai-security
A curated list of AI Security materials and resources for Pentesters, Bug Hunters, and Security Researchers.
 adityabhatt3010/cve-2025-54794-hijacking-claude-ai-with-a-prompt-injection-the-jailbreak-that-talked-back
A high-severity prompt injection flaw in Claude AI proves that even the smartest language models can be turned into weapons — all with a few lines of…
 hackspeak/cve-2026-64638
XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE PoC mirror — WordSec, MIT; for authorized security testing
 george0papasotiriou/cve-2026-21010-voip-sip-digest-authentication-replay
Python PoC for CVE-2026-21010 that replays captured SIP digest Authorization headers to bypass nonce uniqueness/expiration and make unauthorized VoIP…
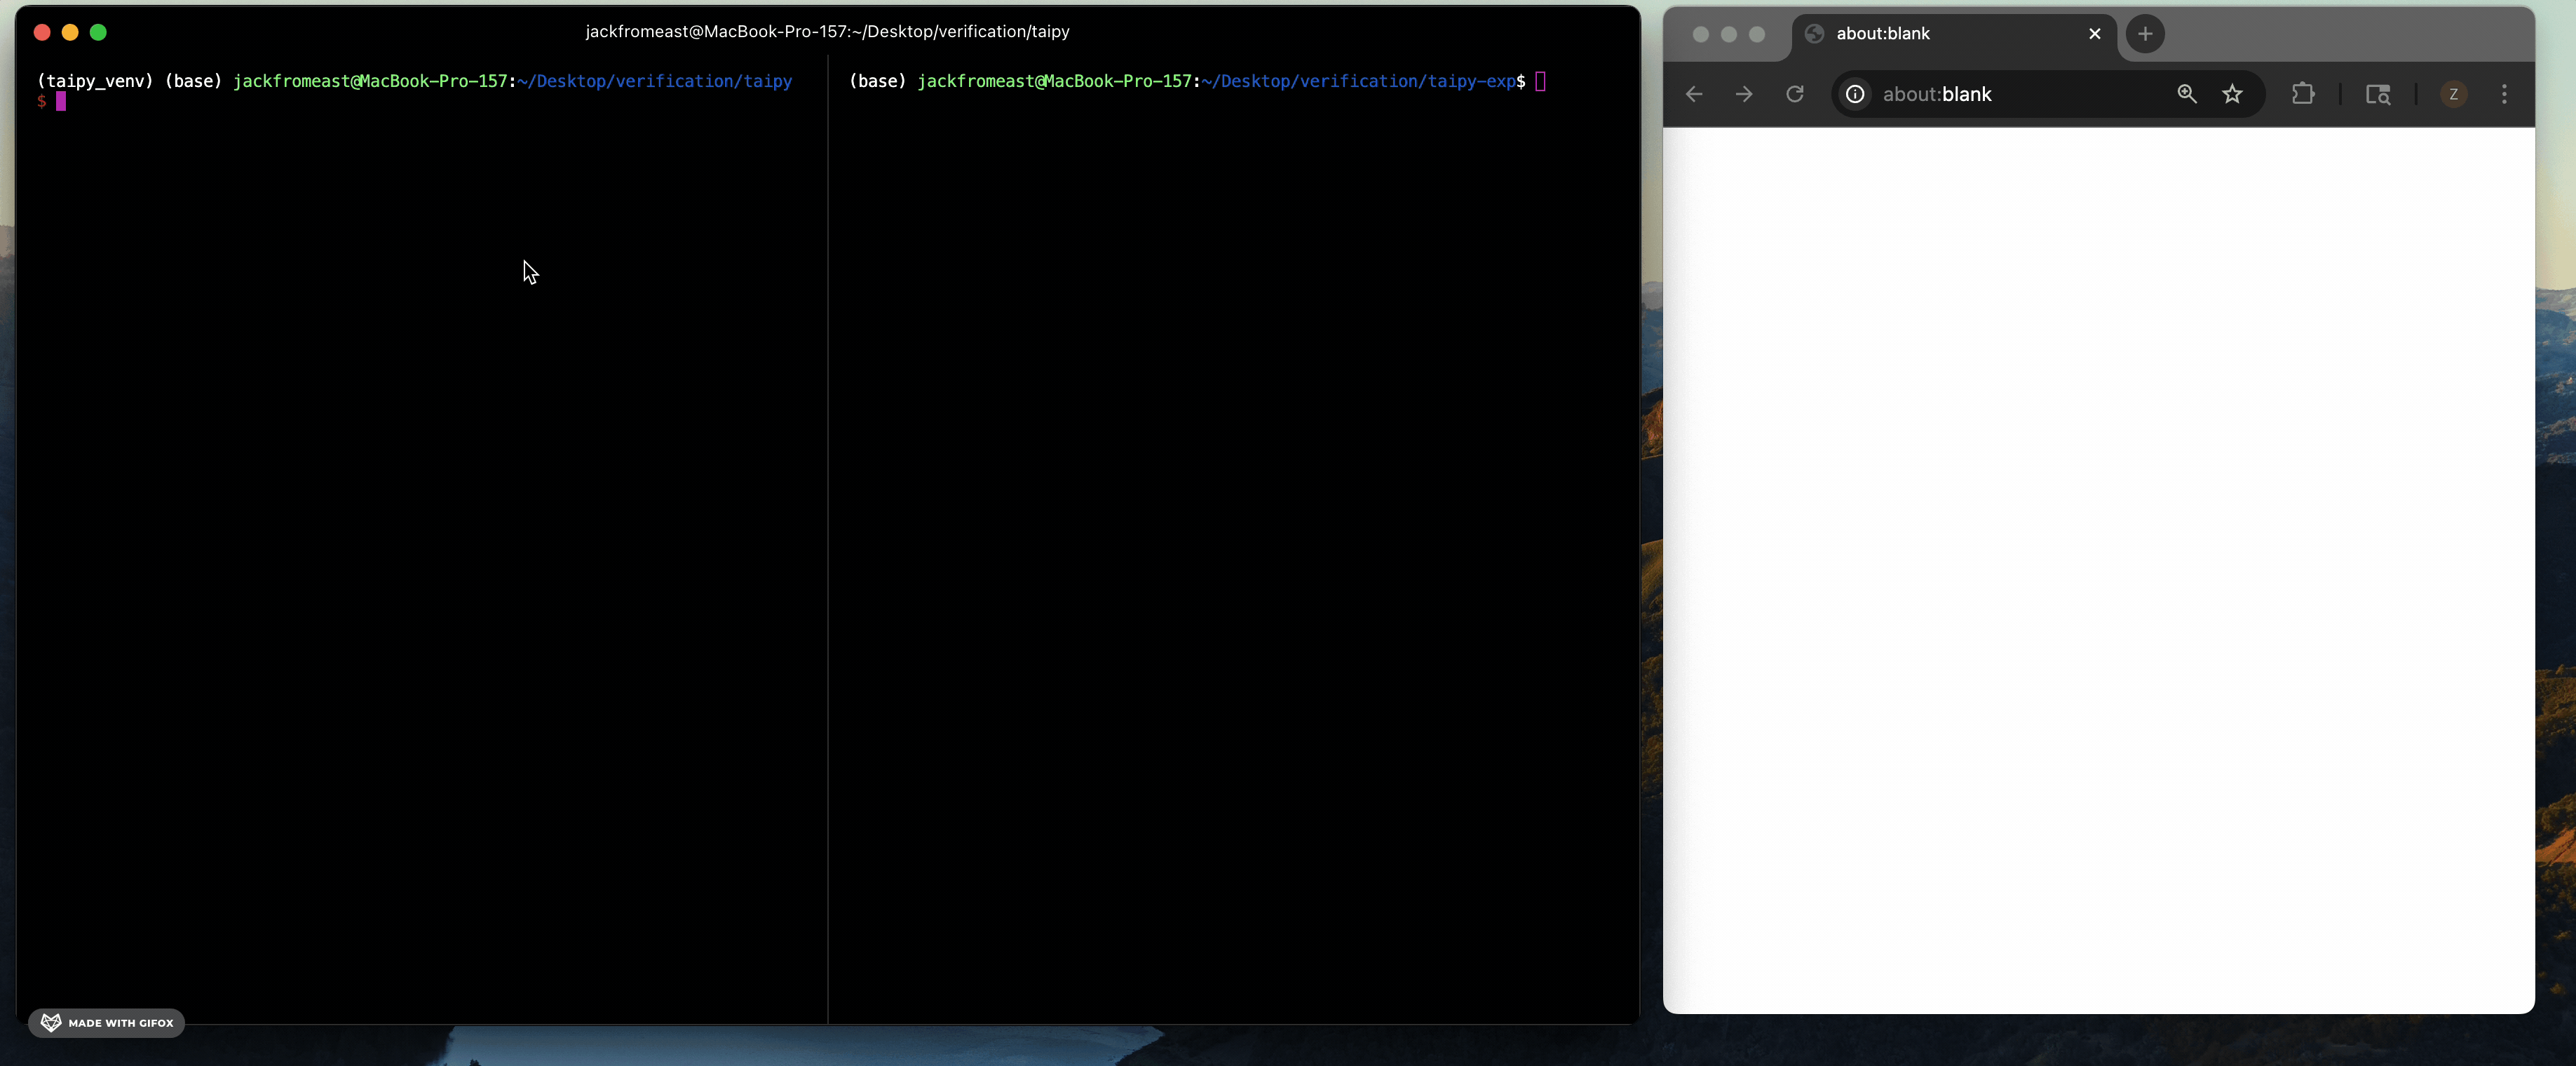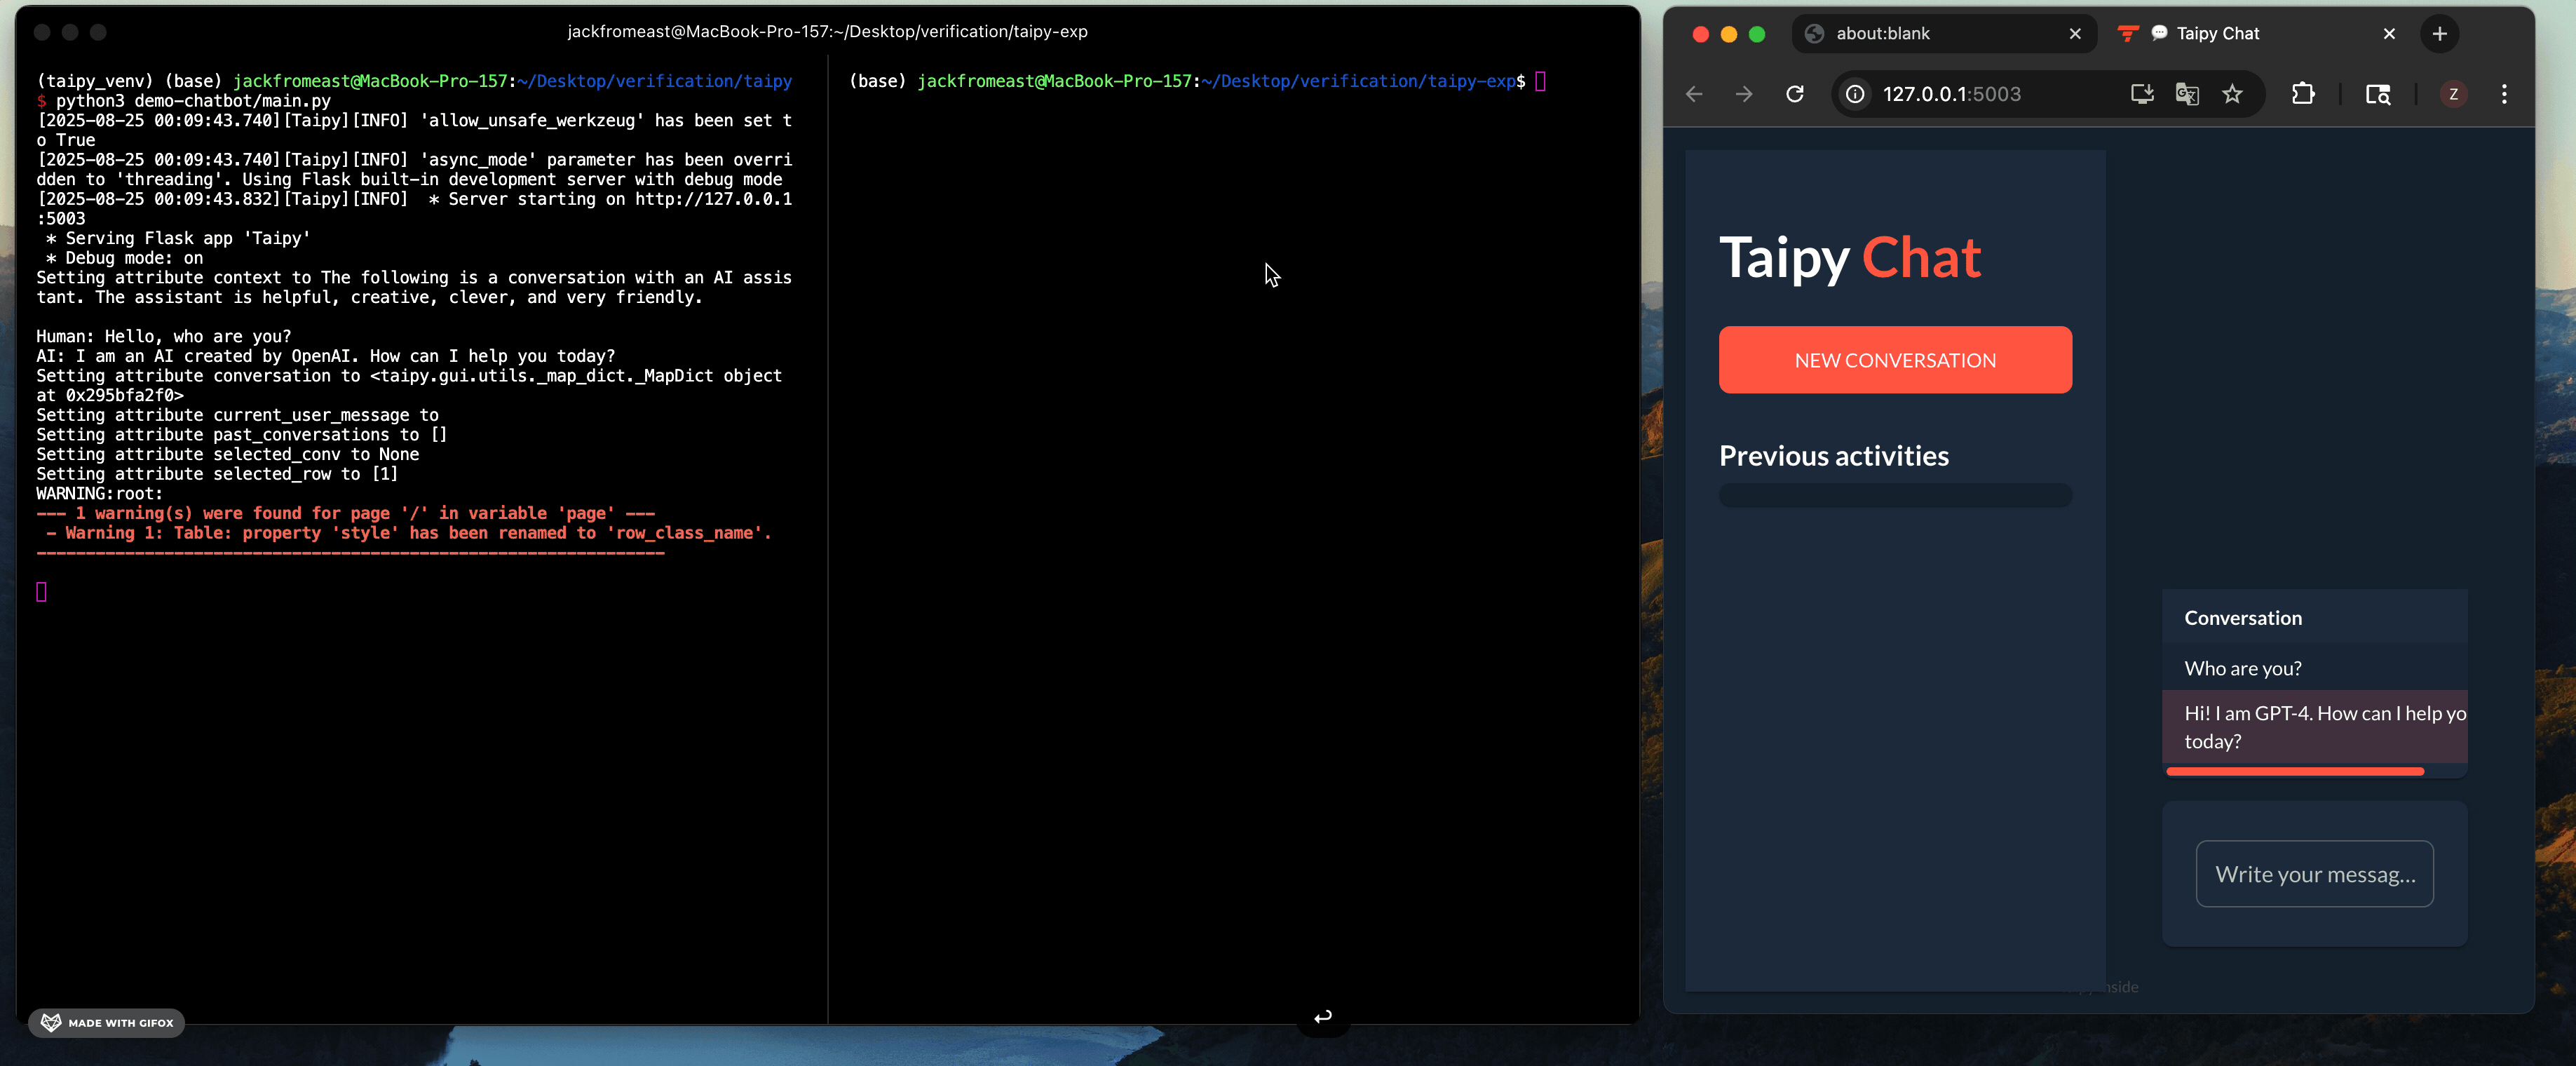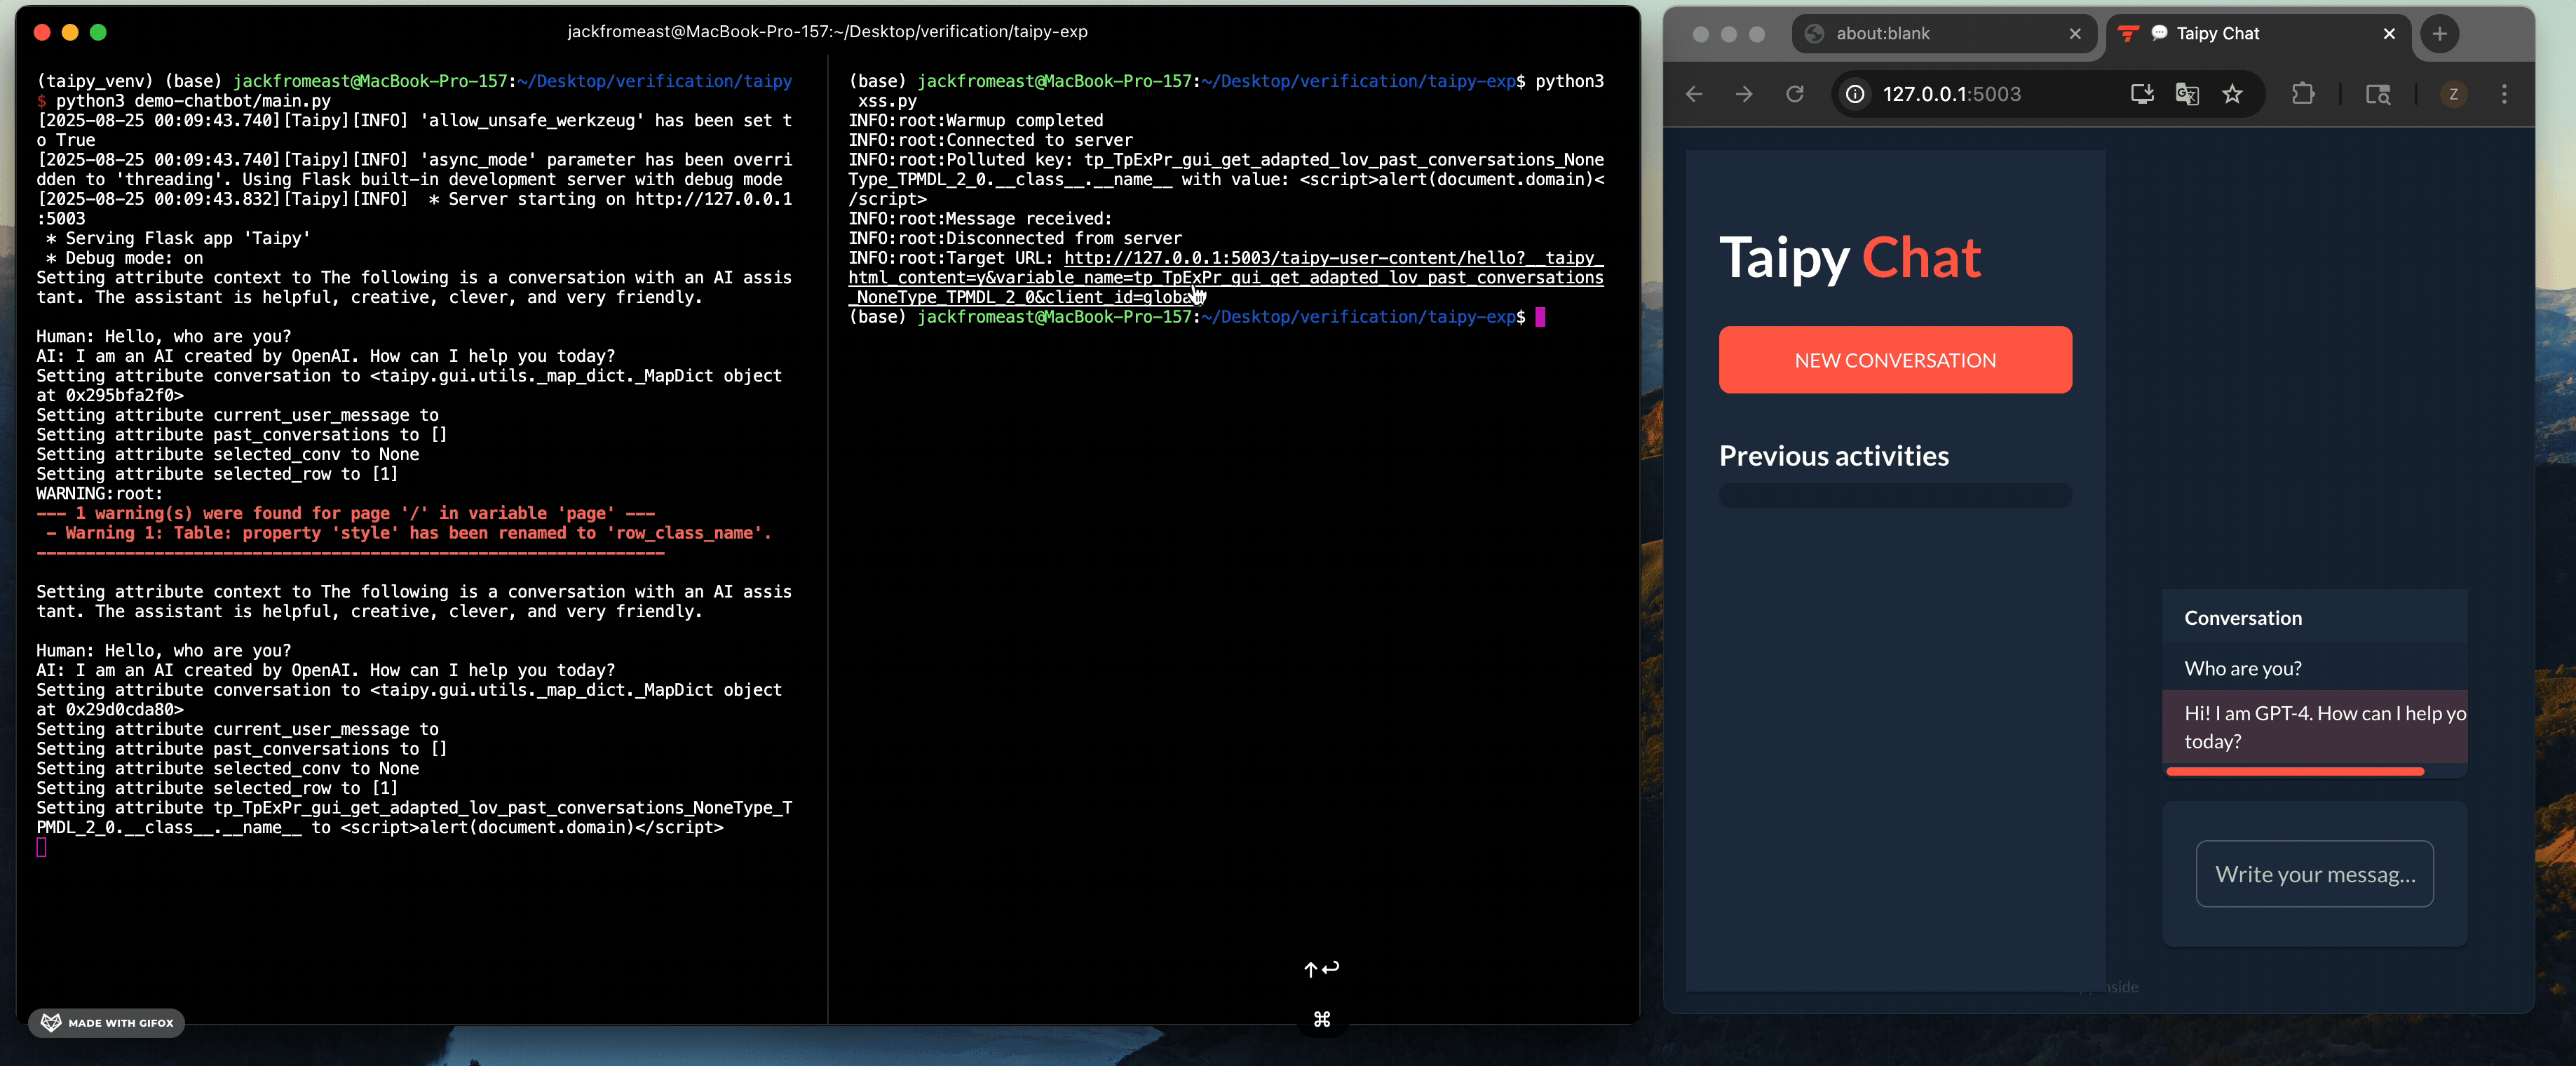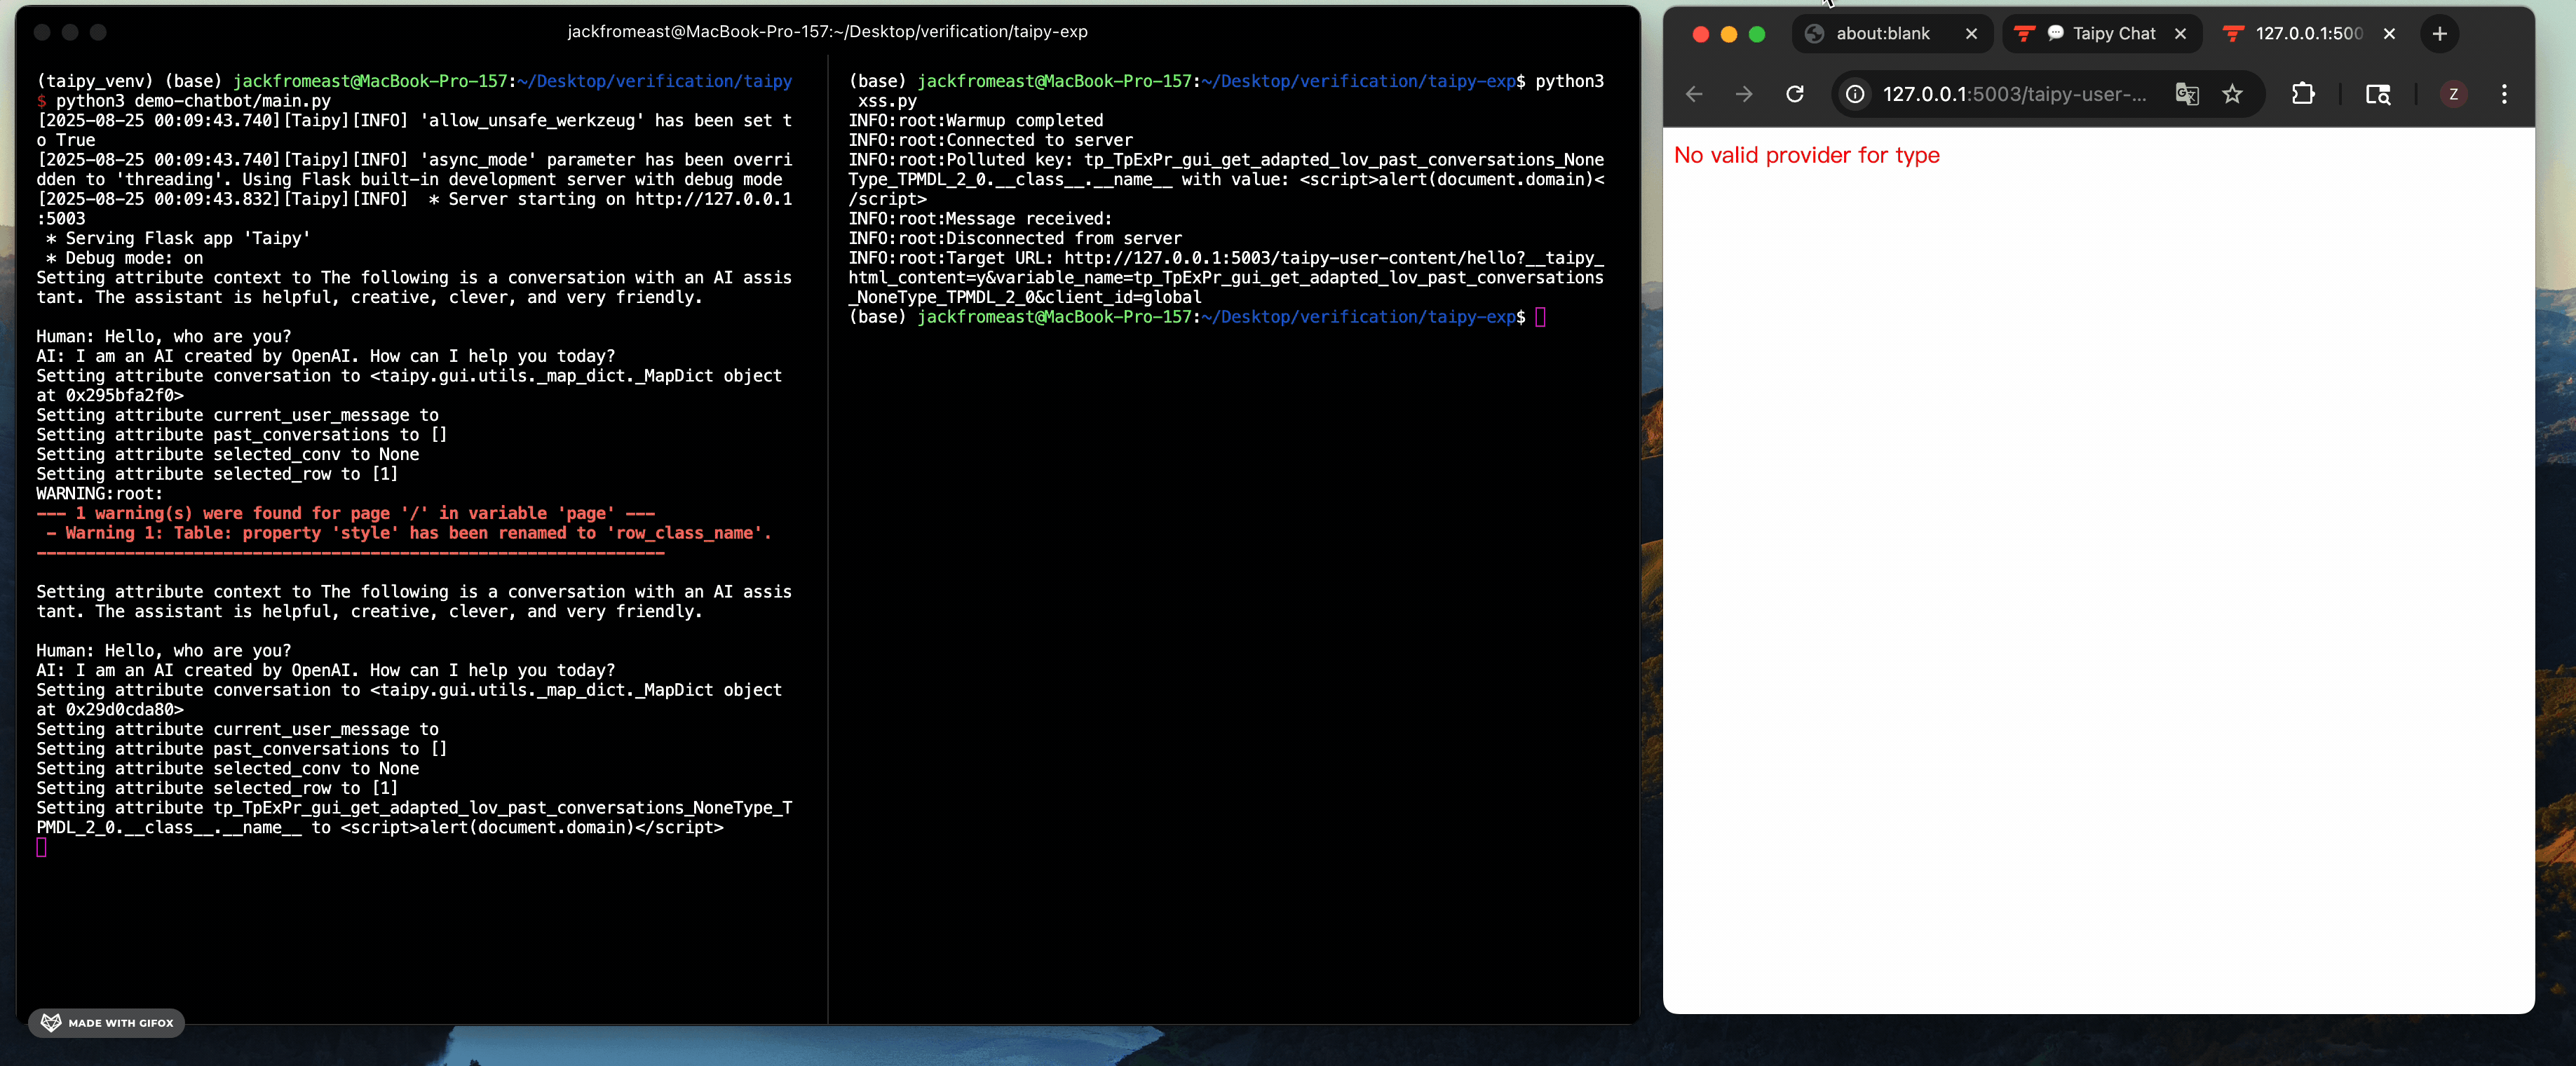 jackfromeast/cve-2025-30374
Exploit PoCs for CVE-2025-30374, a Taipy class pollution bug, demonstrating RCE, reflected XSS, DoS, and OpenAI credential leakage with Docker-based…
 ezramansor/cve-2025-32432-poc
A simple PoC on the Remote Code Execution (RCE) Vulnerability of CraftCMS designated as CVE-2025-32432 written in Go