APTs-Adversary-Simulation

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…

Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.

Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…

Proof-of-concept exploit for CVE-2026-21003 demonstrating JWT authentication bypass by omitting the kid header and using the 'none' algorithm to…

Threadless Process Injection using remote function hooking.

An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents

A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…

Dynamically invoke arbitrary unmanaged code from managed code without PInvoke.

C# obfuscator that bypass windows defender

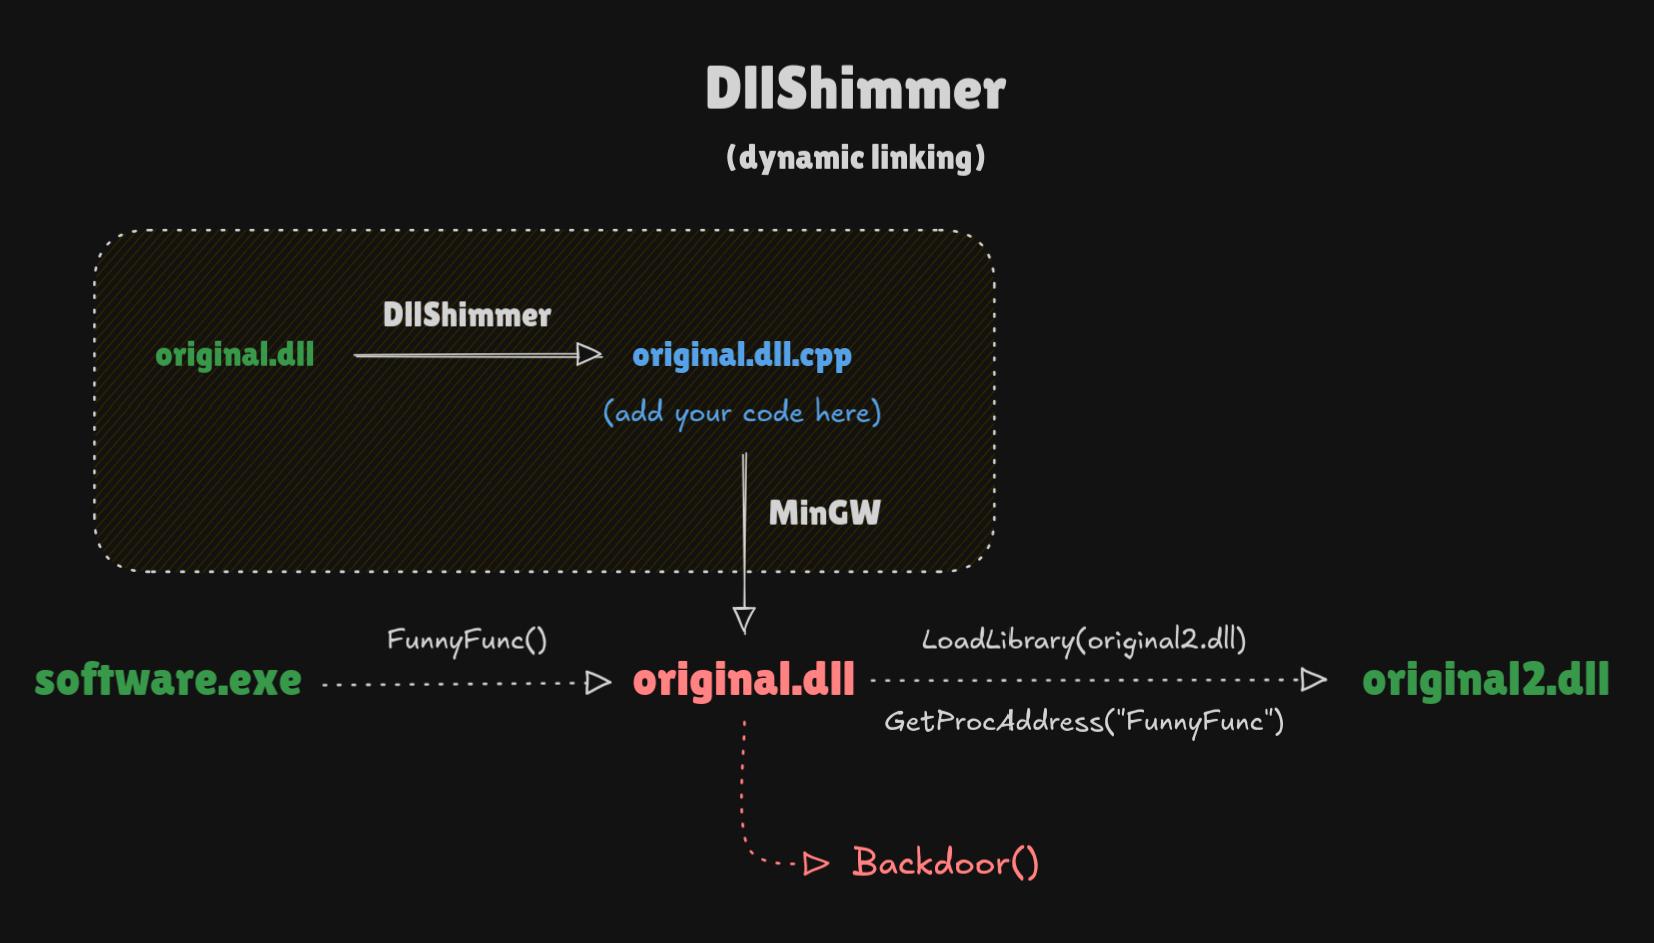
Weaponize DLL hijacking easily. Backdoor any function in any DLL.

Inject DLLs into the explorer process using icons

macOS Initial Access Payload Generator

A delicious, but malicious SSL-VPN server 🌮

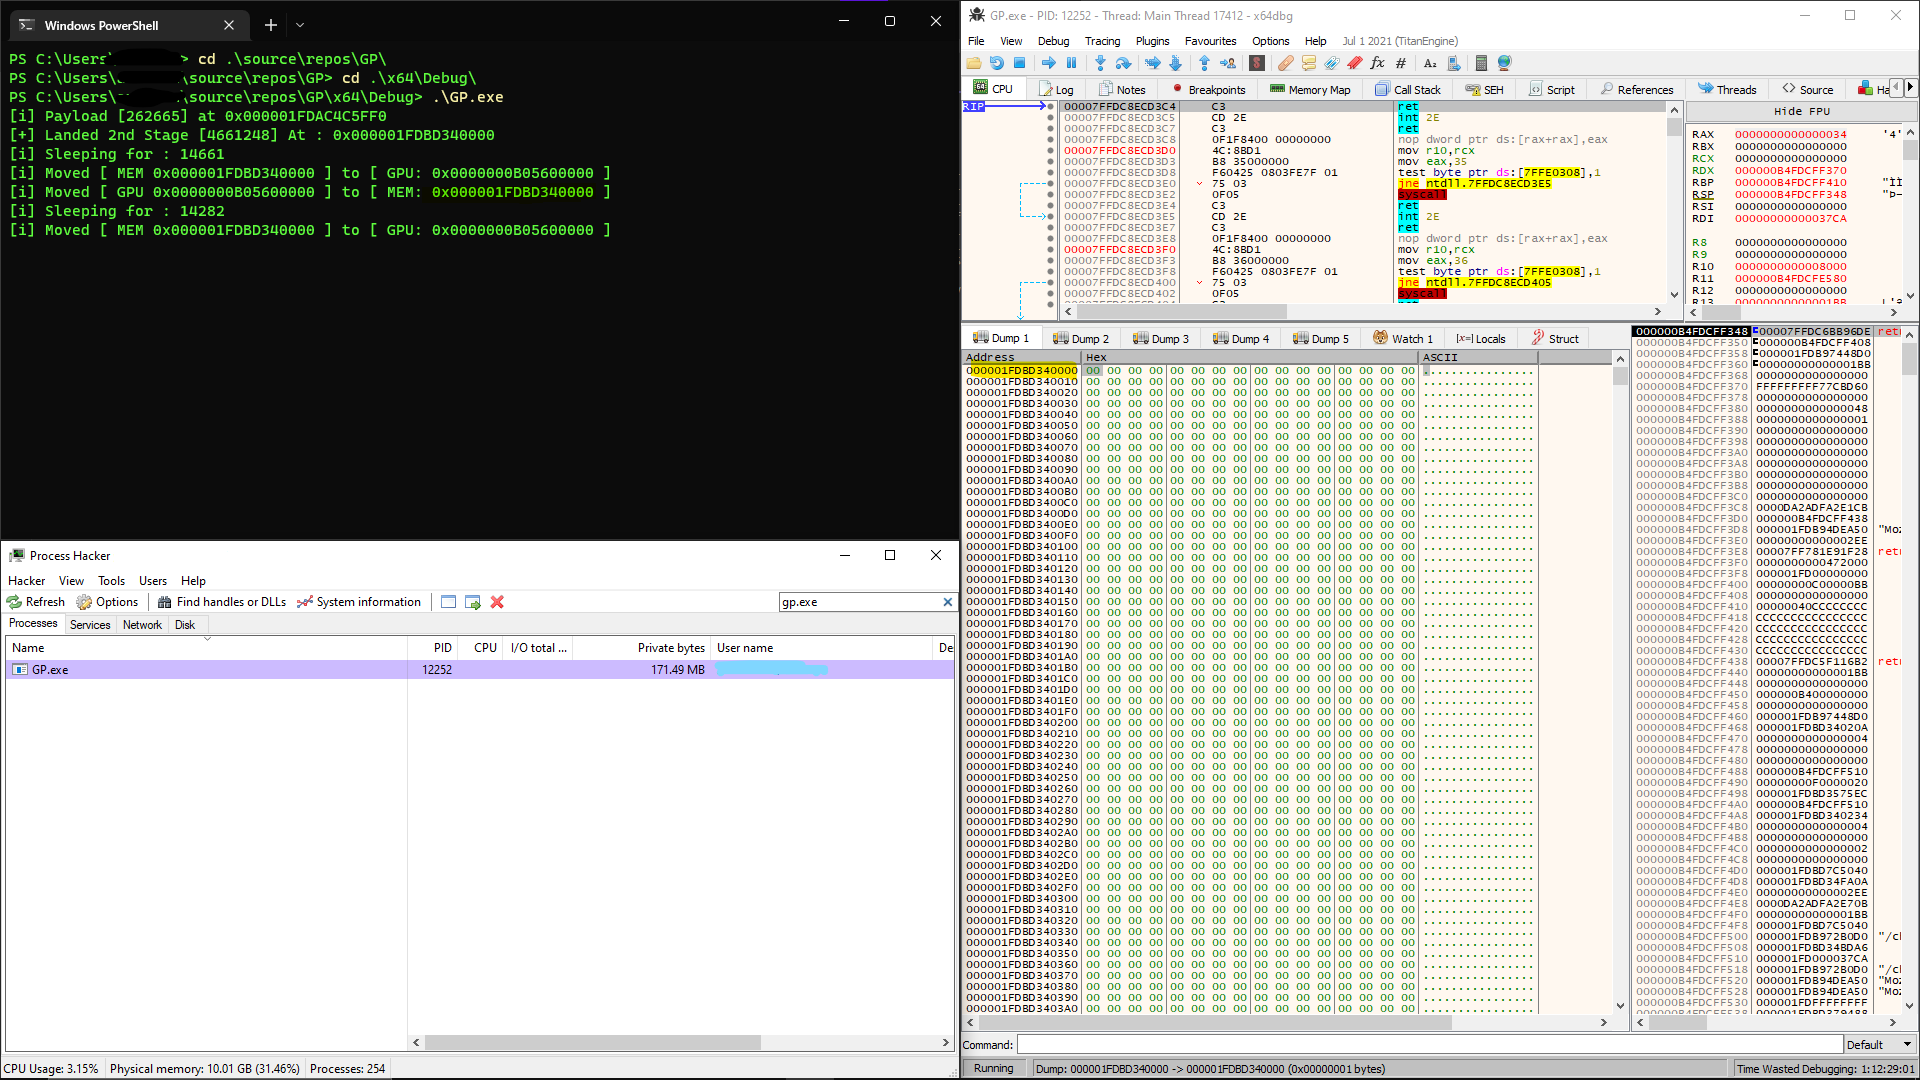
Hides reflective payloads in GPU memory via CUDA APIs, wiping host memory during sleep and using a VEH handler to restore executable memory, evading…

Encypting the Heap while sleeping by hooking and modifying Sleep with our own sleep that encrypts the heap

A simple ptrace-less shared library injector for x64 Linux

PE obfuscator with Evasion in mind

Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC